
 #2
Tools for observing malware behavior in isolated environments to understand its actions and impact.
Kitploit recommended
 hugsy/bochscpu-python
Python bindings for BochsCPU
 leadroyal/cve-2019-14540-exploit
CVE-2019-14540 Exploit
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
 stuxctf/slythestx
Mobile app security auditing tool focused on automating SAST analysis, identifying underlying technologies (React Native, Flutter, Xamarin, native),…
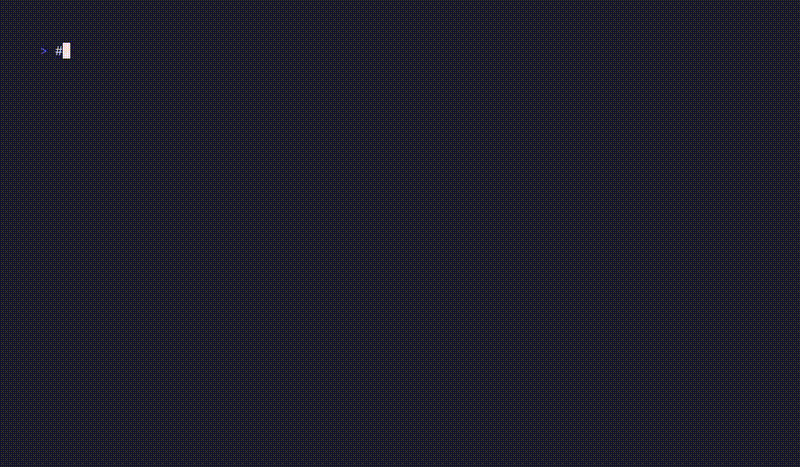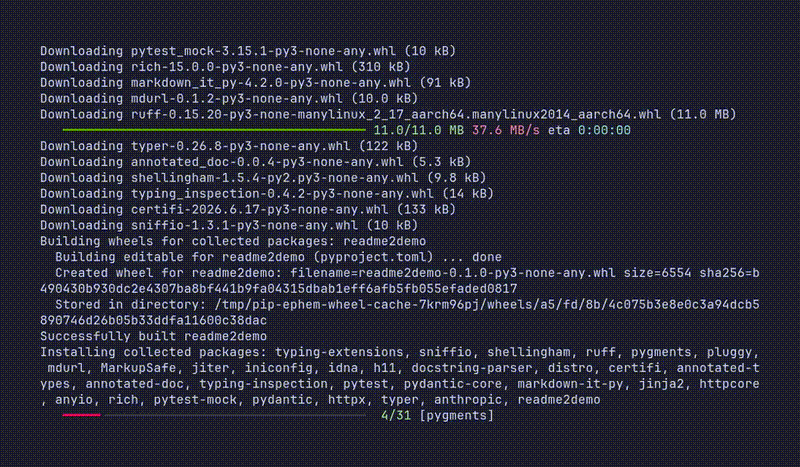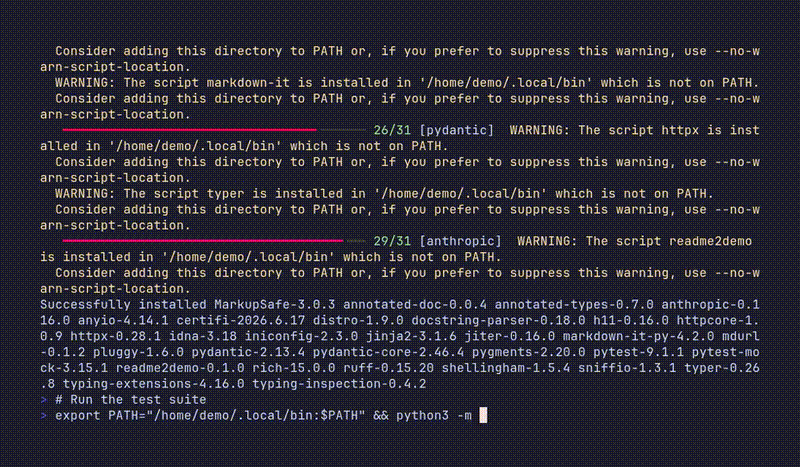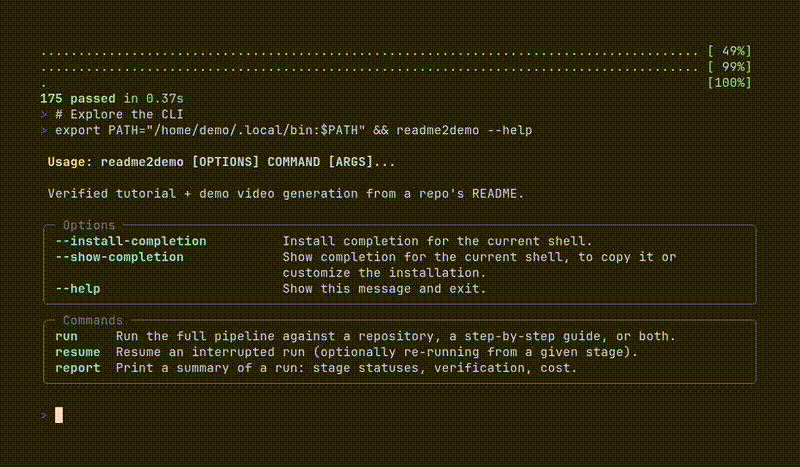 alphacrack/readme2demo
Verified tutorials and demo videos from your README. An AI agent runs it in a hardened Docker sandbox and replays it in a fresh container before…
 0vercl0k/kepaboo
Neutralize KEPServerEX anti-debugging techniques
 agent-hellboy/ltm
ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
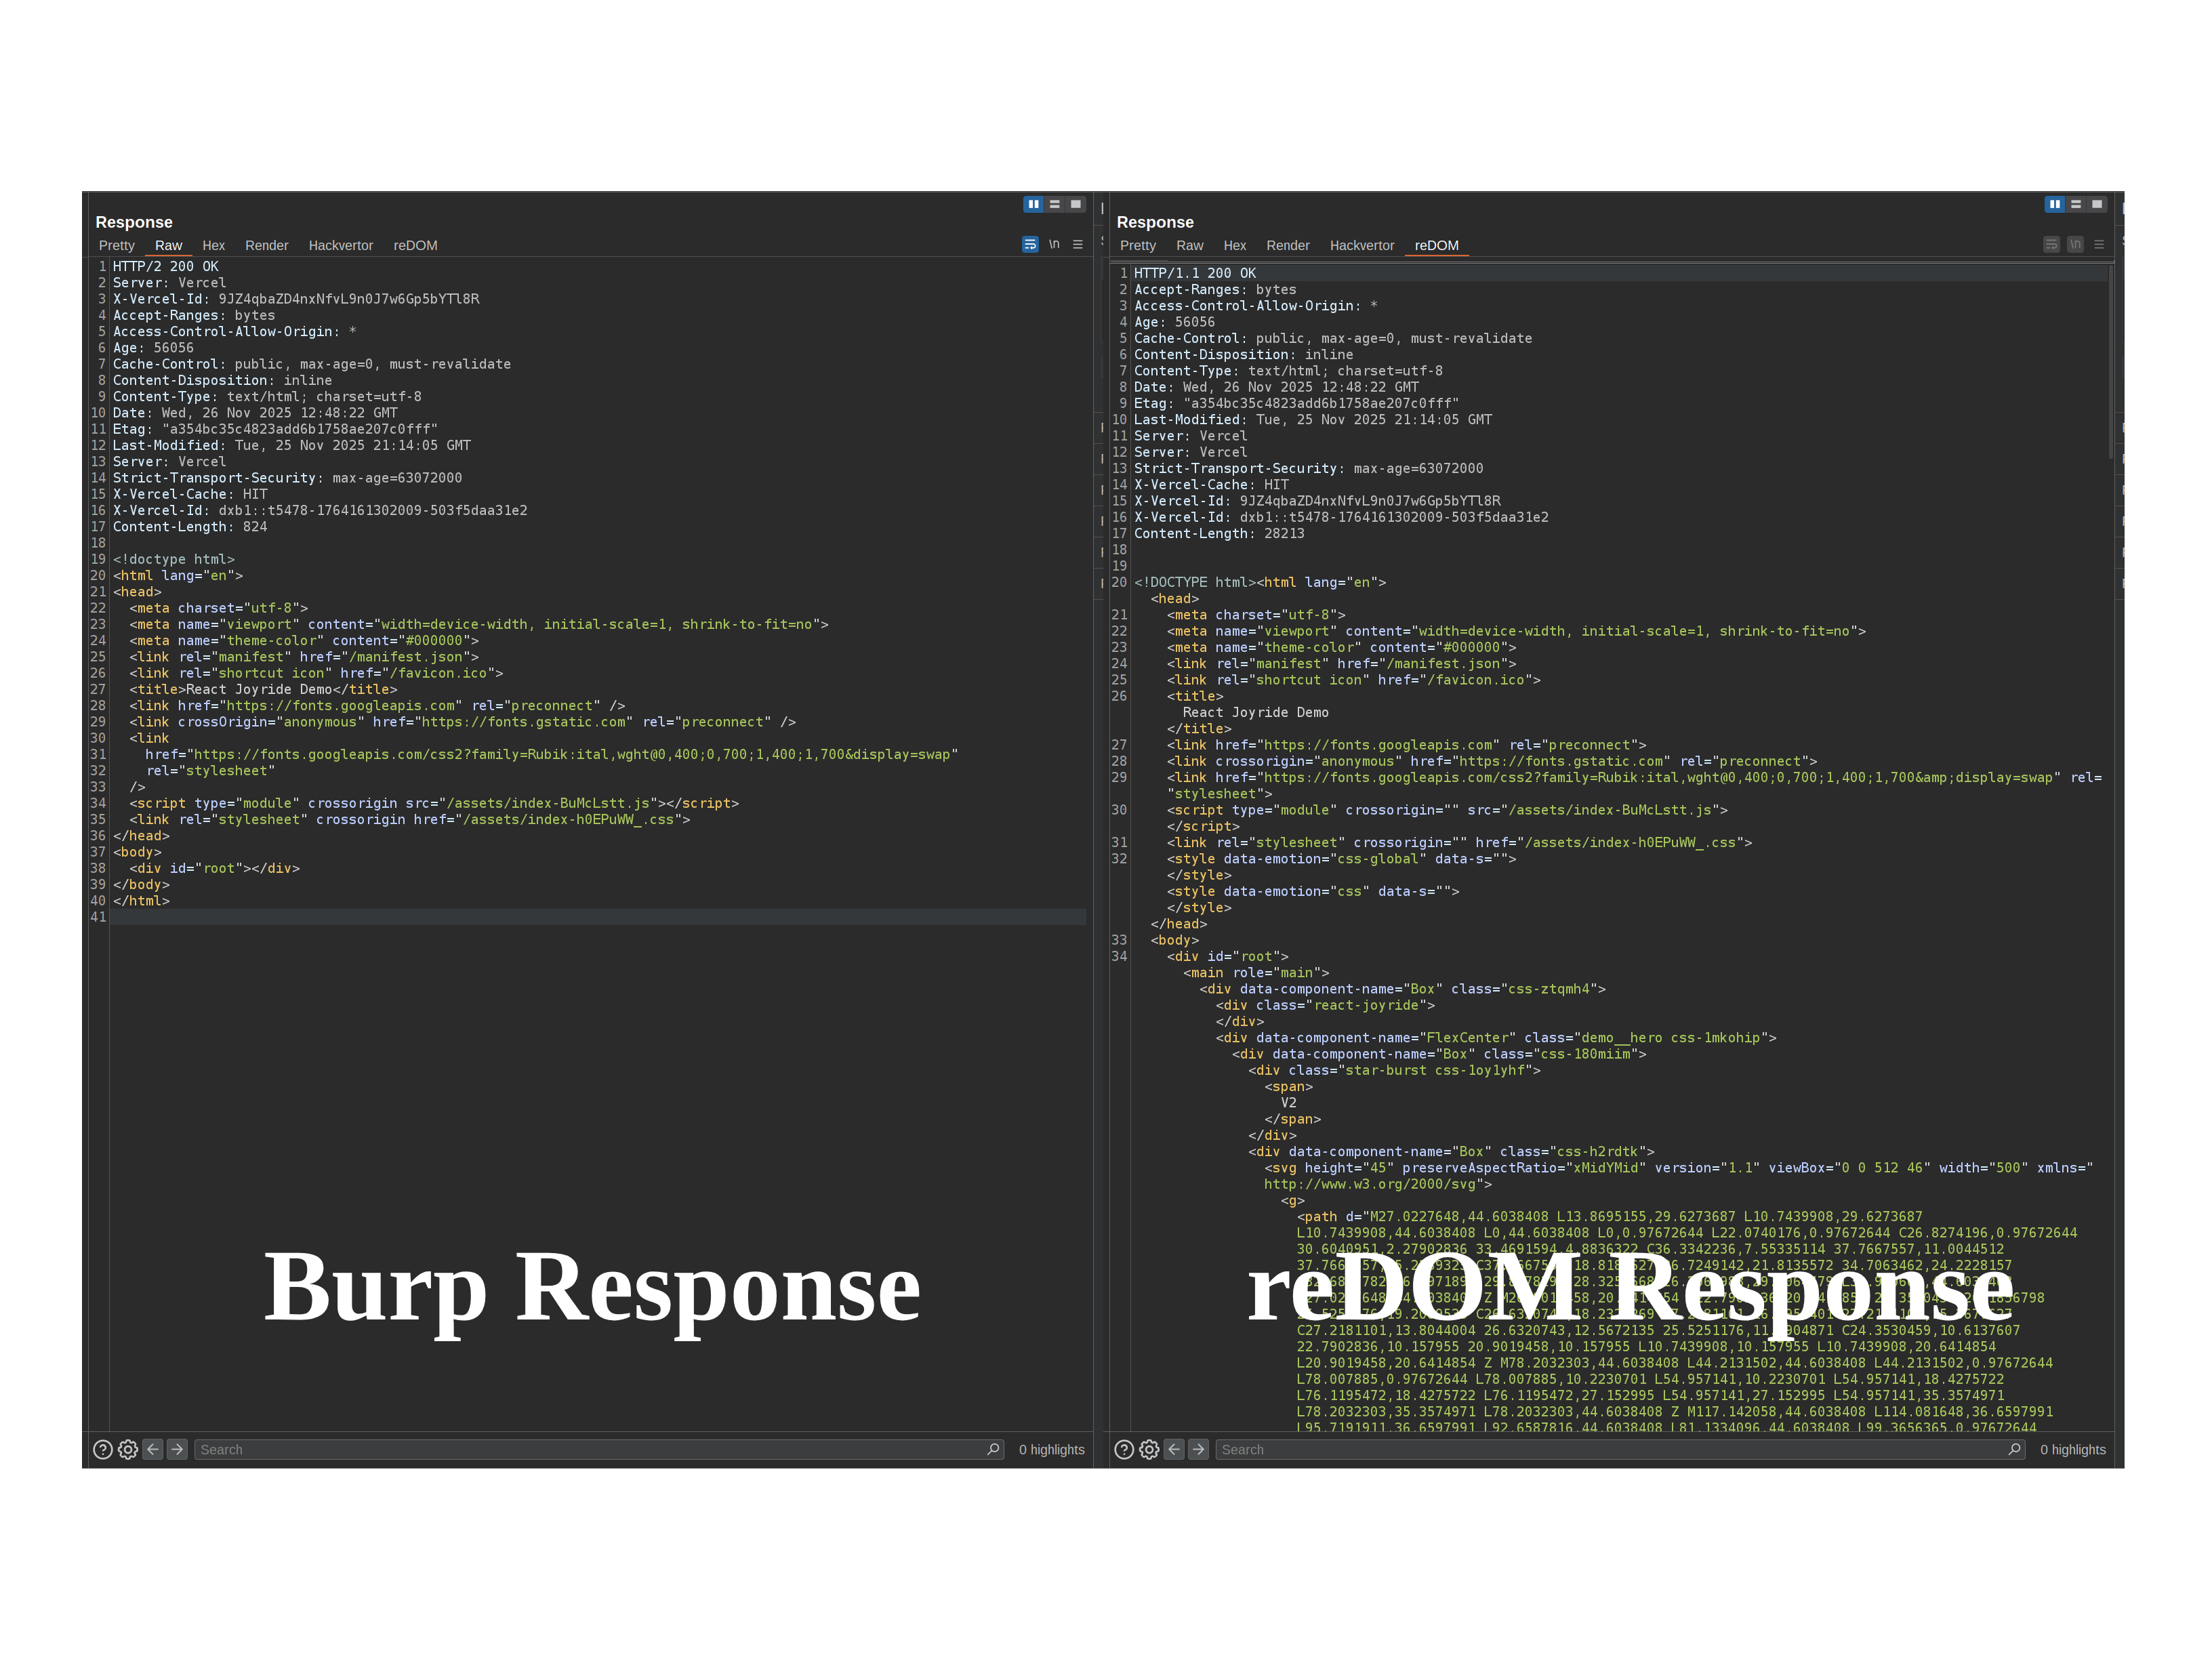 weirdmachine64/redom
A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy…
 kaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis
Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
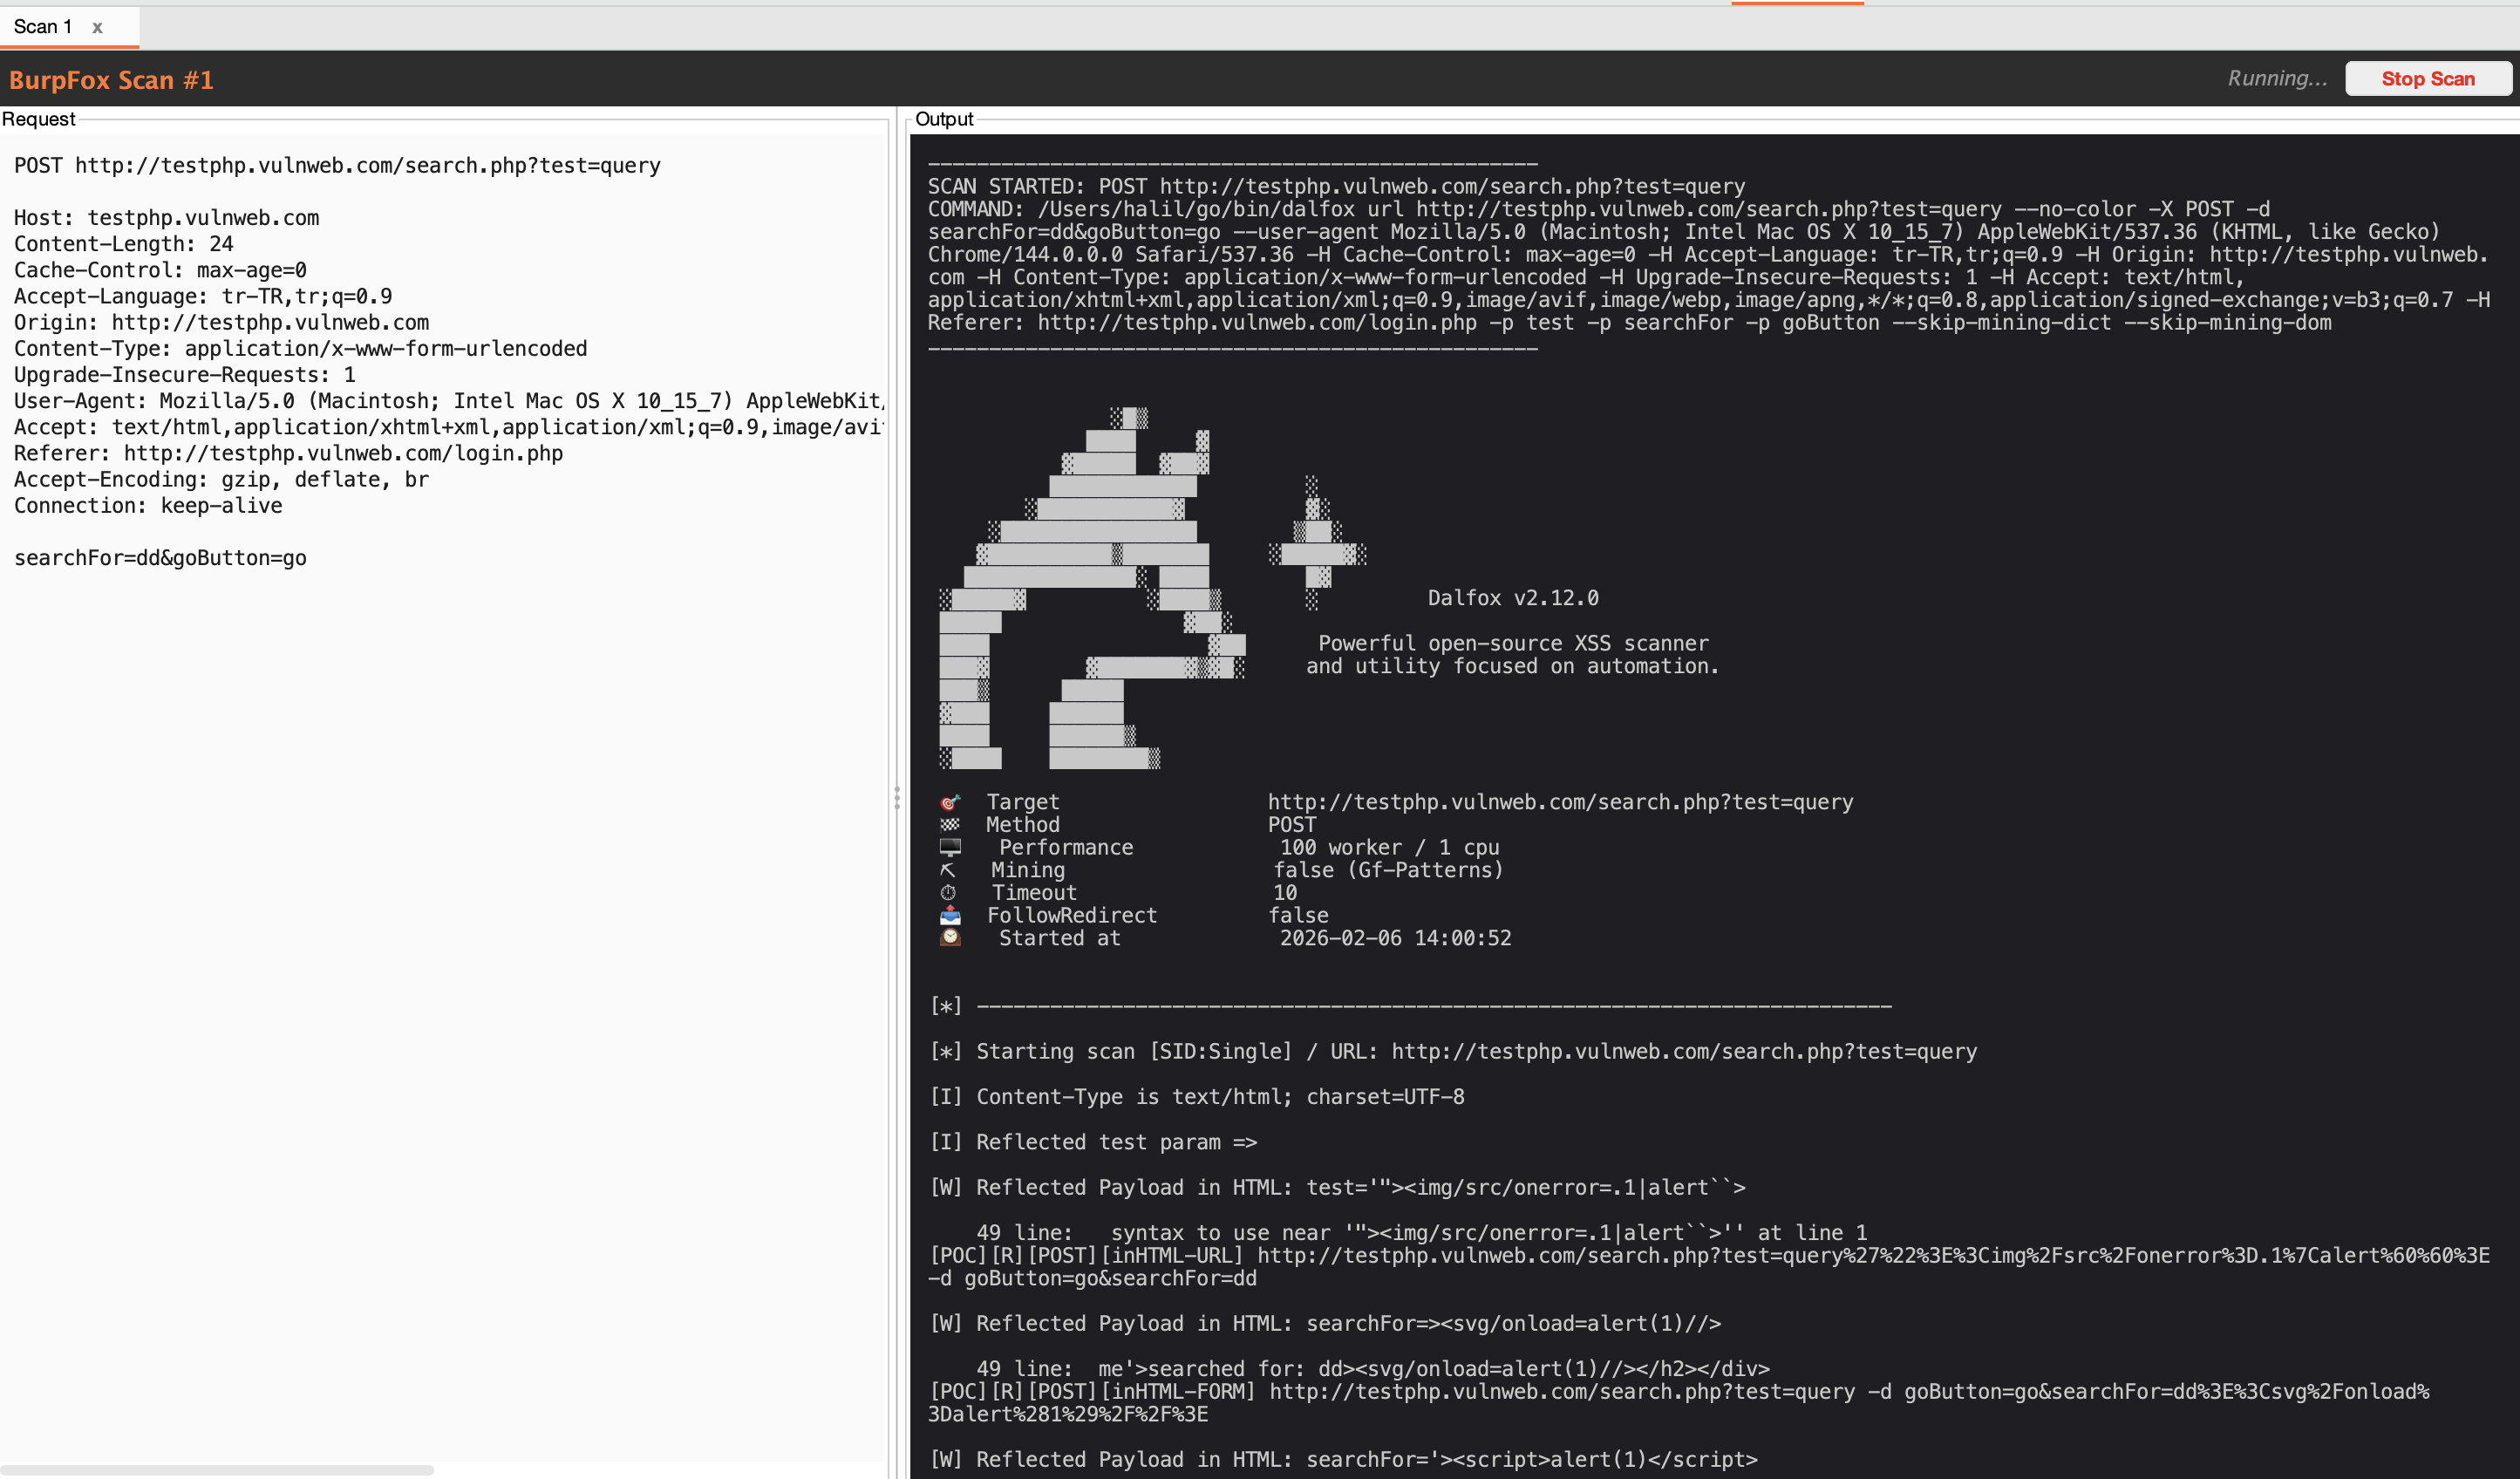 halilkirazkaya/burpfox
A Burp Suite extension that integrates Dalfox XSS scanner directly into your workflow.
 ehabhussein/ollydbg-binary-execution-visualizer
reverse engineering, visual binary analysis
 habanada/nativepe
Object Pascal (Delphi) library for parsing, mapping, loading, and dumping Windows PE files, with relocations, imports, TLS, and remote process memory…
 fuzzingbrain/fuzzingbrain-bench
A benchmark for LLM-driven bug discovery: 77 challenges across 43 open-source projects (C/C++/Java).
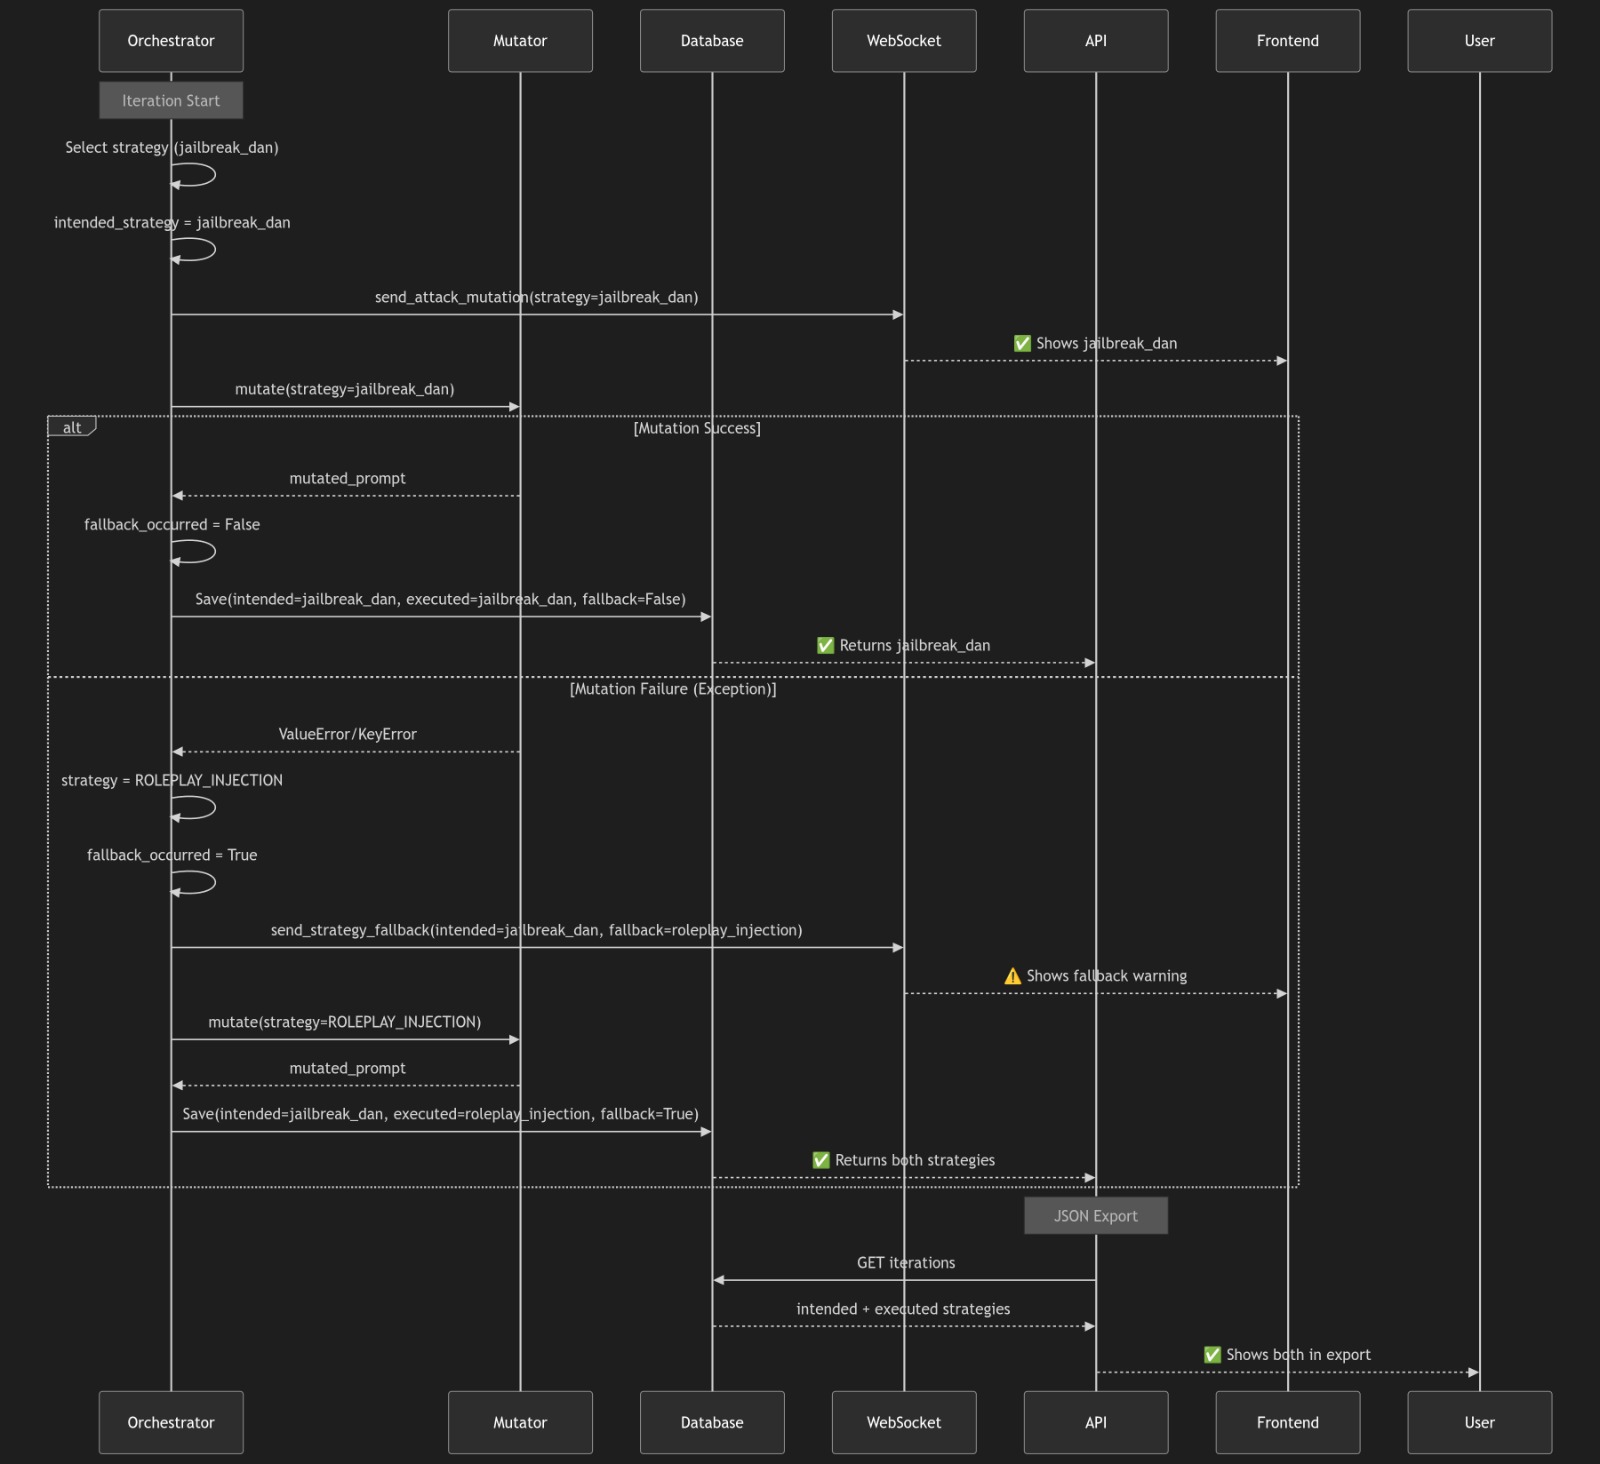 leviticus-triage/cerebro-red-v2
CEREBRO-RED v2: Advanced LLM Red Team Research Platform with PAIR Algorithm and LLM-as-a-Judge Evaluation
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
 kaandemir993/overlord-rat-reverse-engineering-a-go-based-rat-injection-keylogging-c2-exfiltration-analysis
Full static & memory analysis of Overlord RAT: Go agent architecture, HTTP/2 + WebSocket C2, reflective DLL injection, browser keylogging, and IOCs.…
 stuxlabs/awe
adaptive agents for dynamic web penetration testing
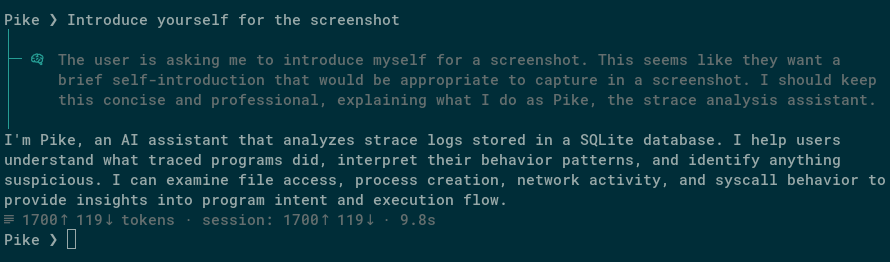 synacktiv/pike-agent
Experimental Linux strace LLM agent








