
 #2
Tools for observing malware behavior in isolated environments to understand its actions and impact.
Kitploit recommended
 sysnets/atfuzzer
Grammar-guided evolutionary fuzzer for dynamic analysis of AT command interfaces on Android smartphones via Bluetooth and USB, uncovering DoS,…
 demonslay335/cryptotester
A utility for playing with cryptography, geared towards ransomware analysis.
 nccgroup/lazydroid
bash script to facilitate some aspects of an Android application assessment
 nmantani/fileinsight-plugins
FileInsight-plugins: decoding toolbox of McAfee FileInsight hex editor for malware analysis
 xoreaxeaxeax/schrodingers-toctou
Detect compiler-invented memory loads that turn secure C into TOCTOU vulnerabilities. Includes automated source audits, Unicorn-based binary…
 hahwul/mzap
⚡️ Multiple target ZAP Scanning
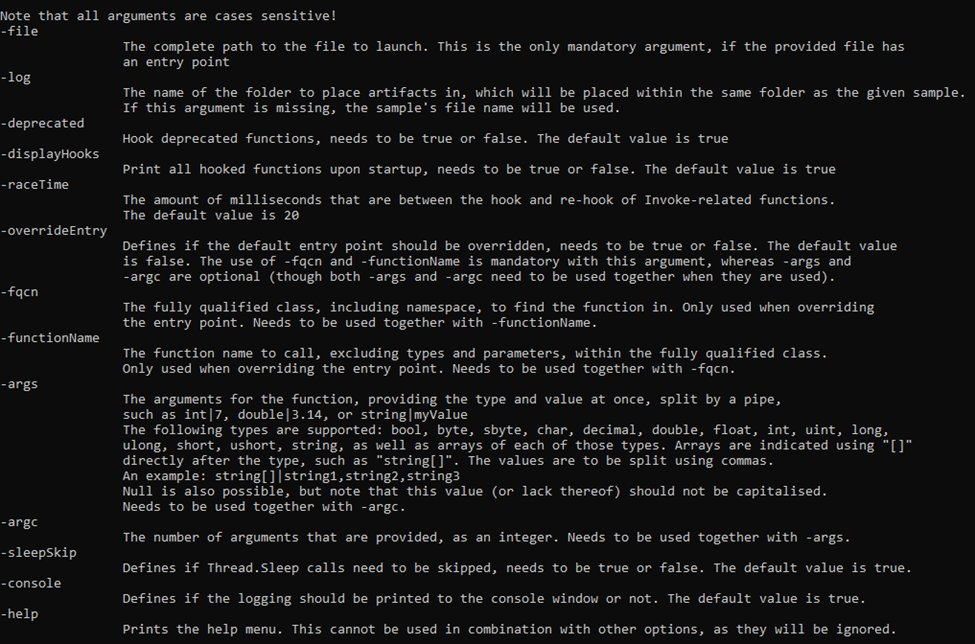 advanced-threat-research/dotdumper
An automatic unpacker and logger for DotNet Framework targeting files
 cybermaggedon/cyberprobe
Capturing, analysing and responding to cyber attacks
 ngwg/ceasta
Disassembler, decompiler and x64dbg-style debugger for PE/ELF binaries with IDA-style listing, function graphs, Lua plugins, CLI, and a built-in MCP…
 facebook/mcpguard-dynamic
Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)
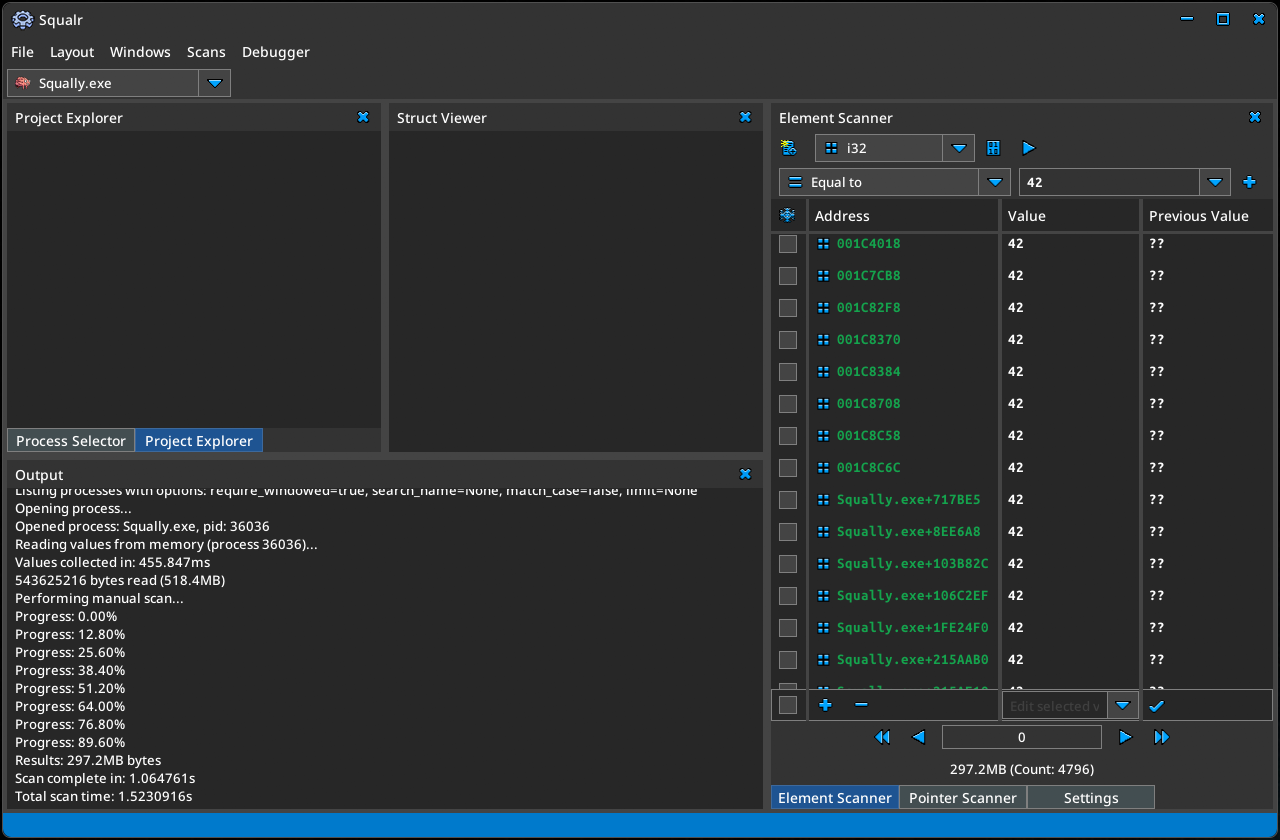 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.
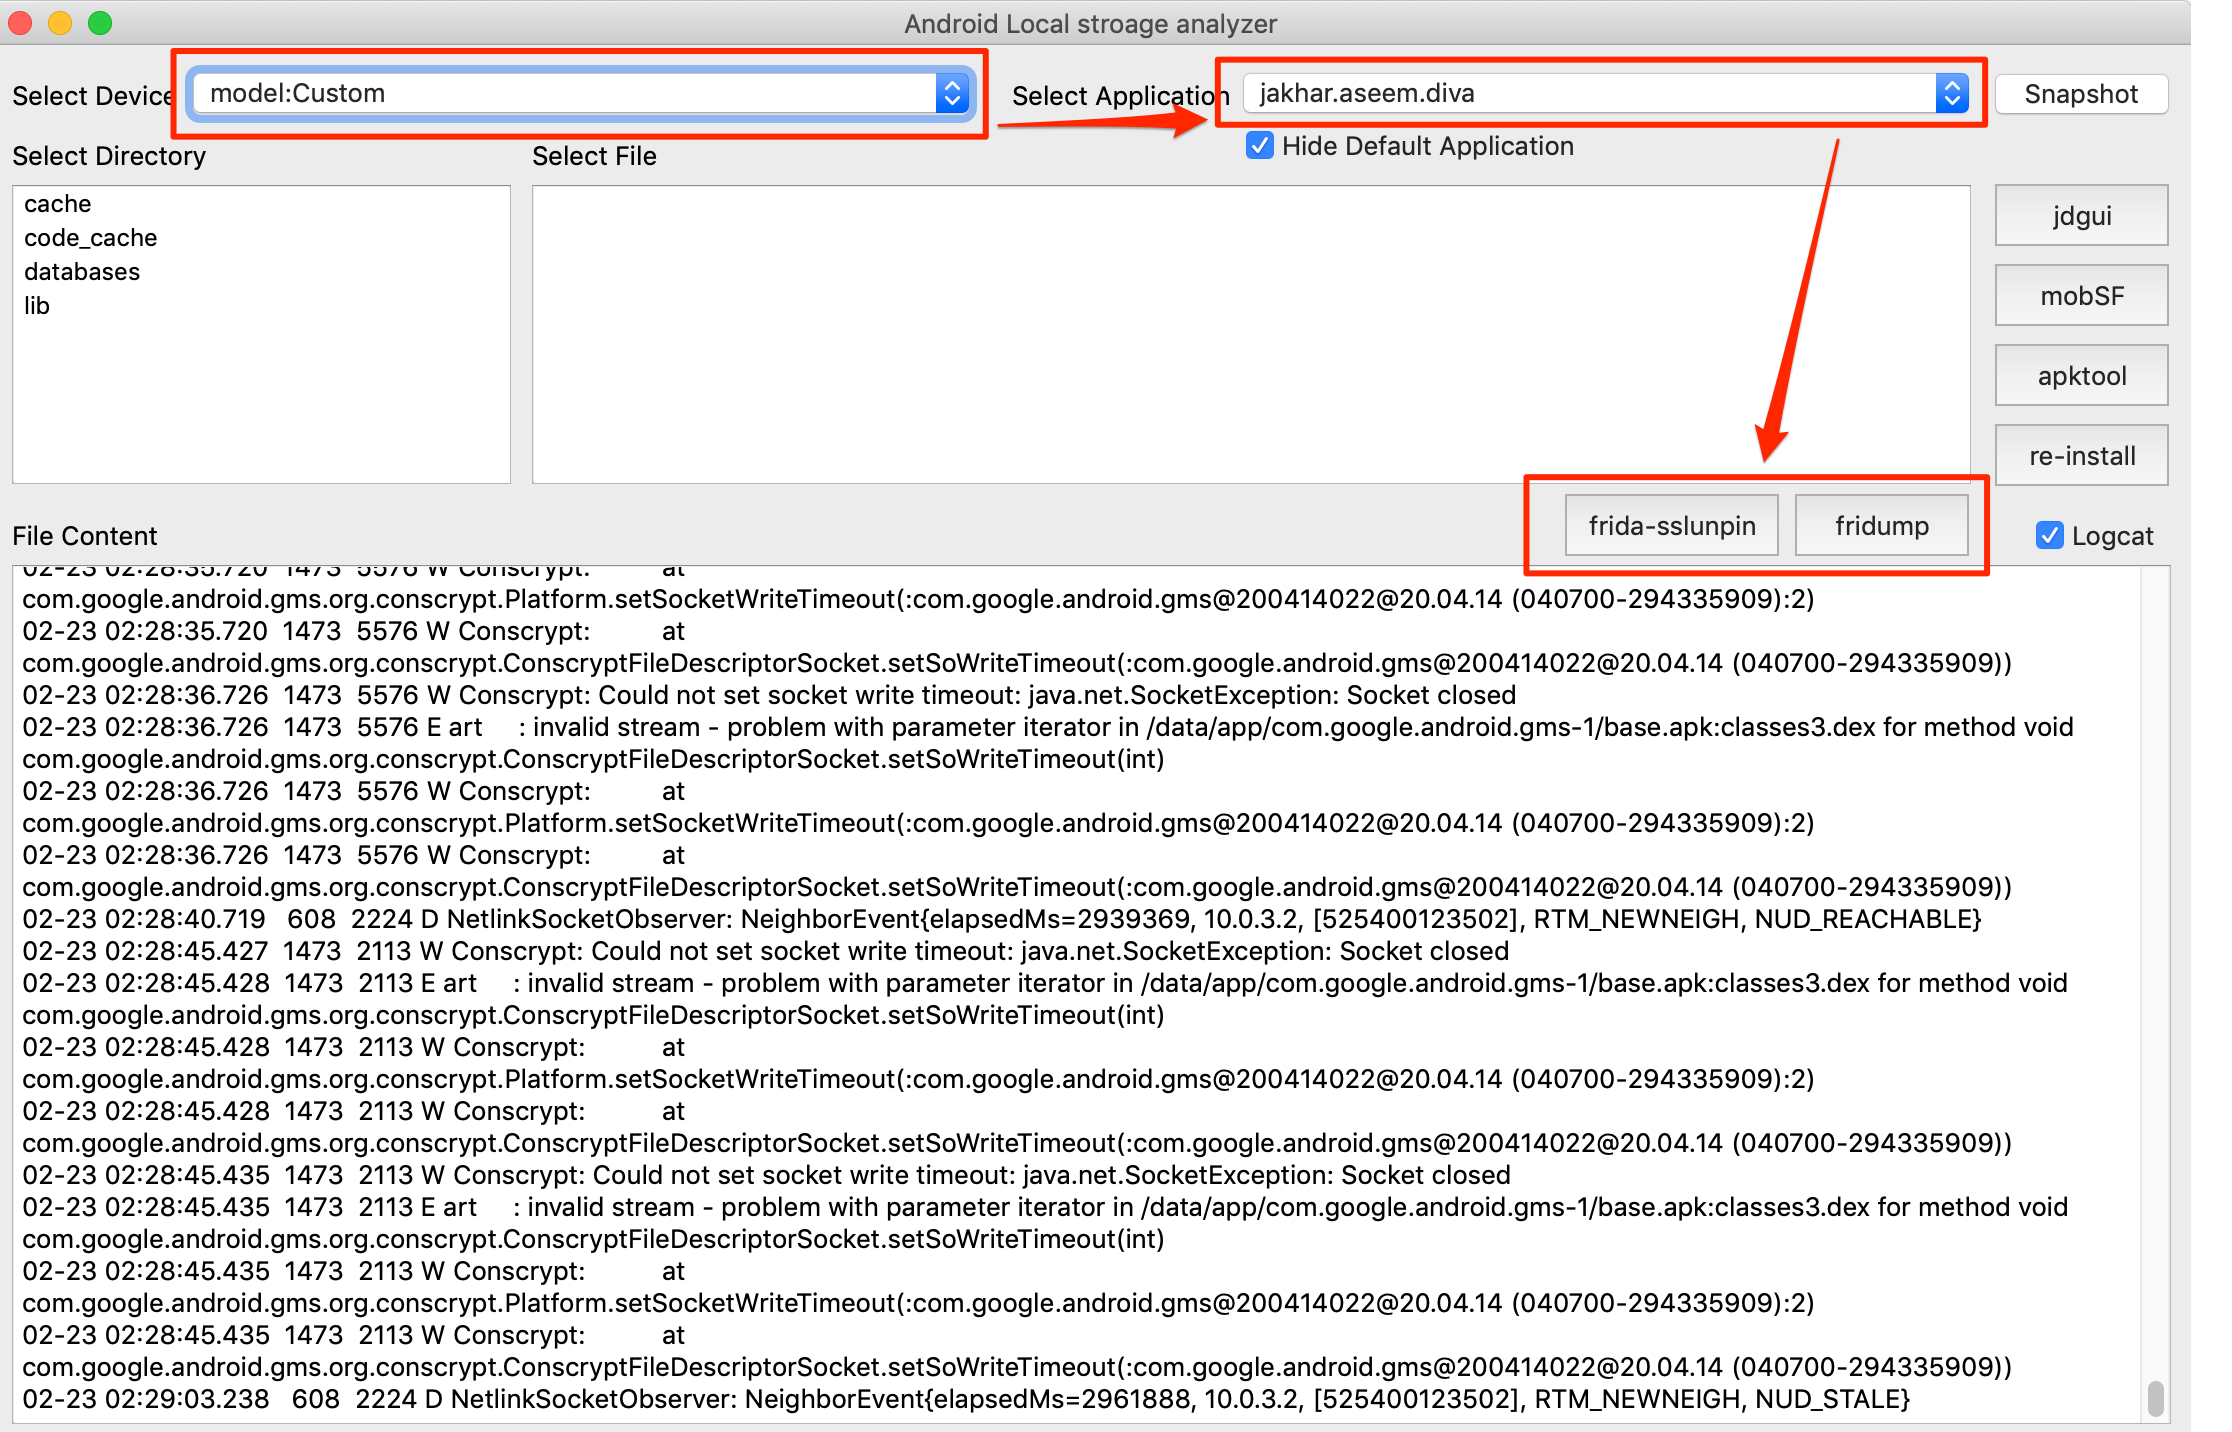 notsosecure/android_application_analyzer
The tool is used to analyze the content of the android application in local storage.
 ricccrd/dd
JIT-based userspace Linux kernel that runs containers natively on Apple Silicon macOS without a VM. Drop-in Docker Engine API replacement with…
 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 icicle-emu/icicle
Emulation-based fuzzer for MSP430 firmware that finds and analyzes memory-corruption bugs with detailed crash reports and reproducible inputs.
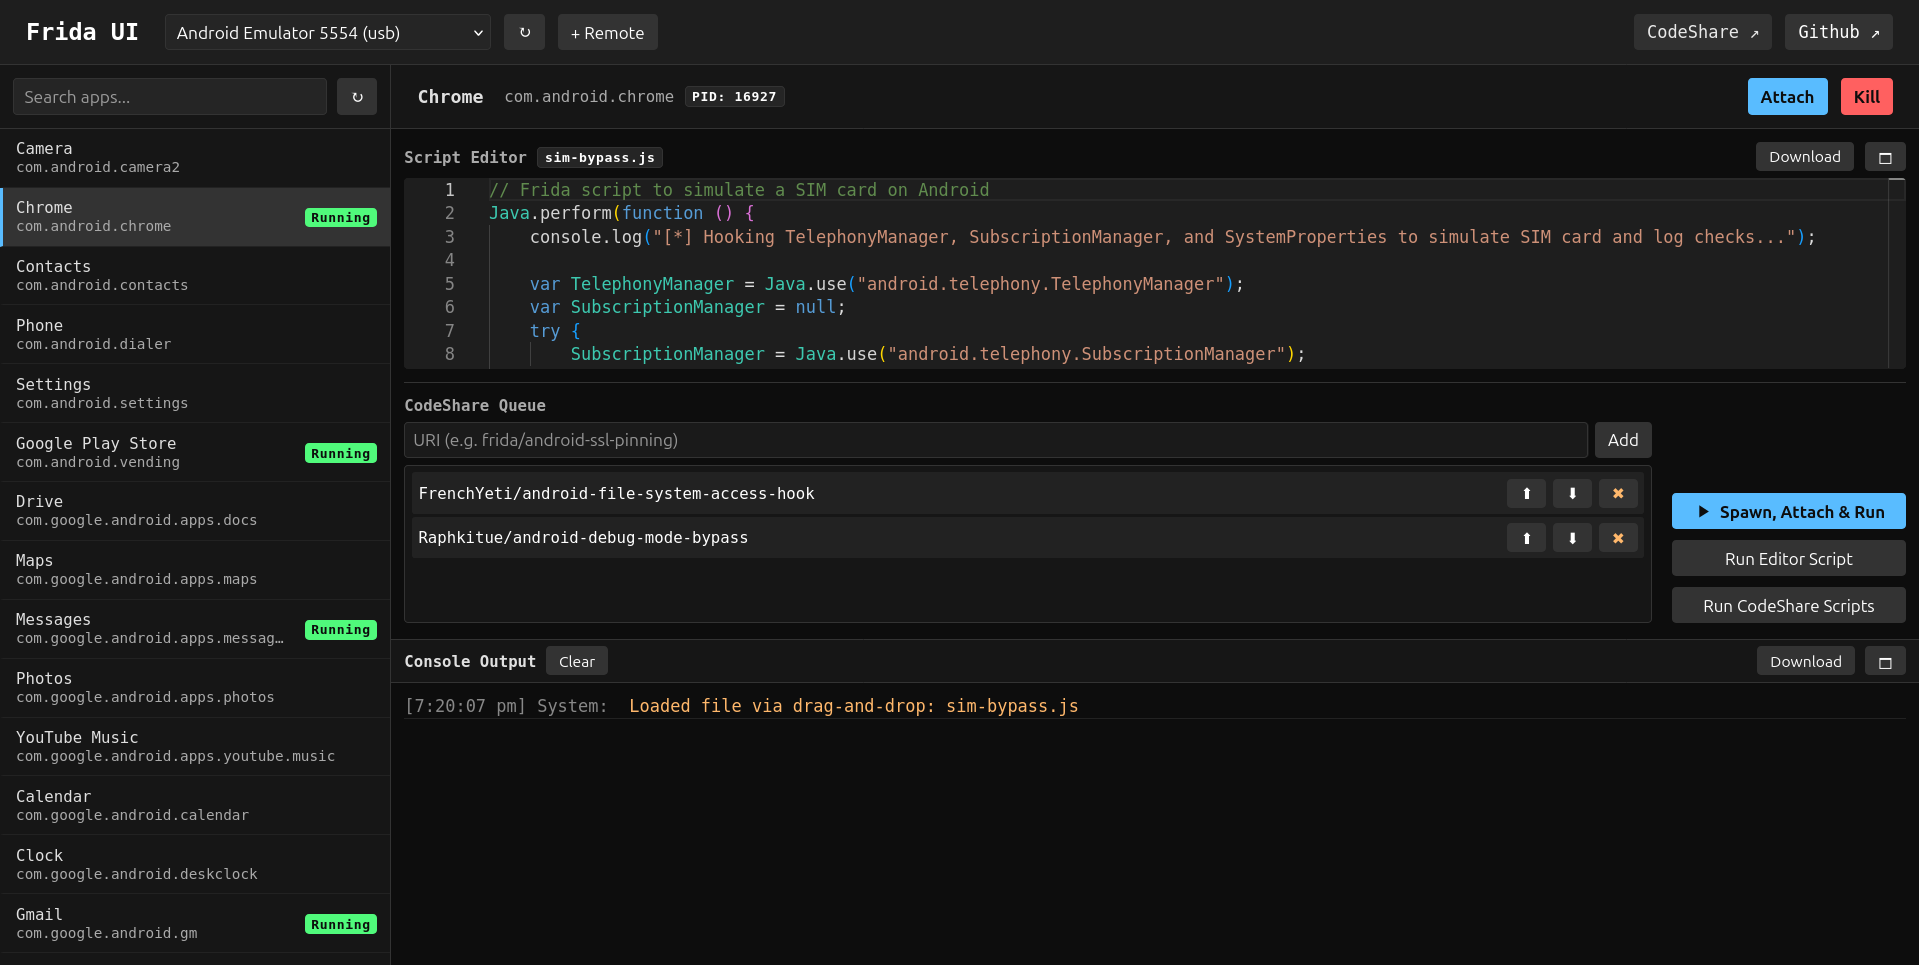 adityatelange/frida-ui
Interact with Frida devices, processes, and scripts directly from your browser.
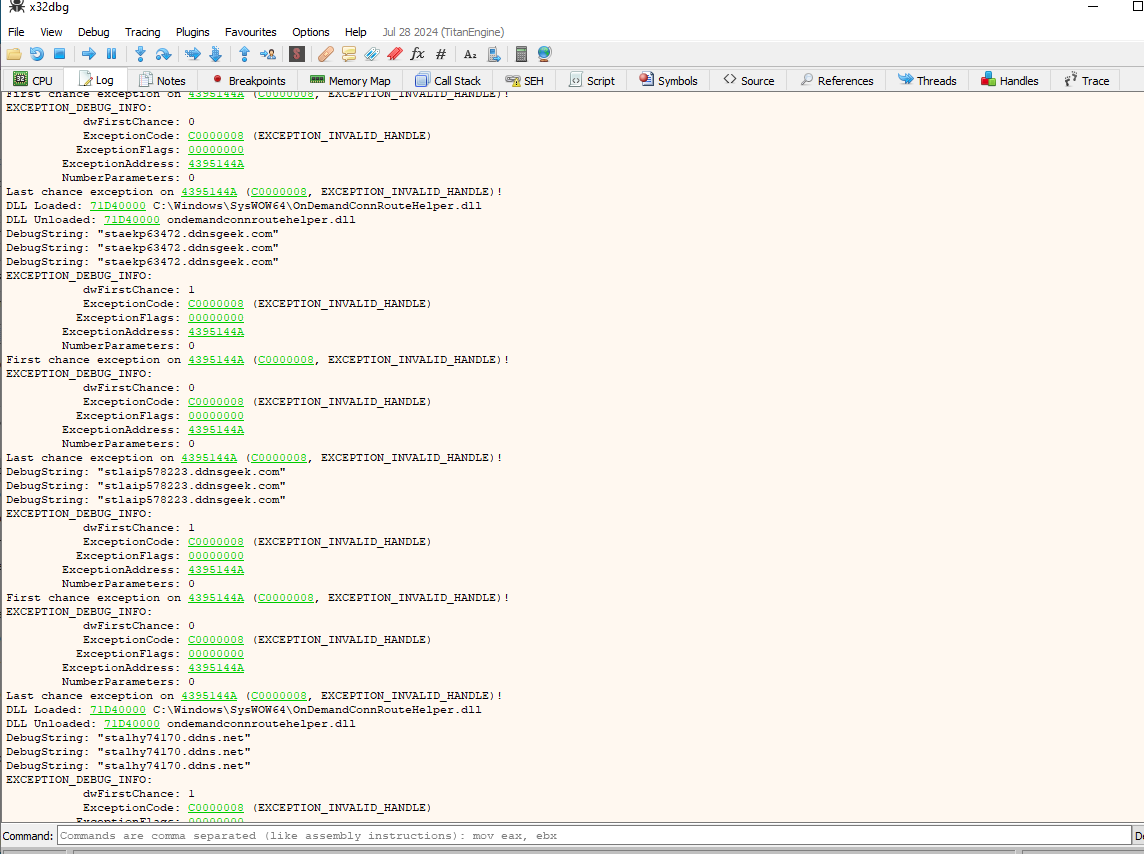 zeromemoryex/c2-hunter
Real-time C2 traffic extractor for malware analysts. Hooks Win32 connection APIs to intercept and analyze command-and-control communication,…








