
 #2
Tools for observing malware behavior in isolated environments to understand its actions and impact.
Kitploit recommended
 malwaretech/appcontainersandbox
An example sandbox using AppContainer (Windows 8+)
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 epfl-vlsc/memoro
Memoro: A Detailed Heap Profiler
 livecvebench/cve-factory
CVE-Factory
 secforce/droidground
A flexible playground for Android CTF challenges.
 deputation/instrumentation_callbacks
A proof of concept demonstrating instrumentation callbacks on Windows 10 21h1 with a TLS variable to ensure all syscalls are caught.
 sfaci/masc
A Web Malware Scanner
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 security-prince/resources-for-application-security
Some good resources for getting started with application security
 leandrofroes/gftrace
A command line Windows API tracing tool for Golang binaries.
 rasetsuu/vmp-devirt
Trace-assisted VMProtect devirtualization research platform: version front-ends feed a shared Remill/LLVM backend to lift handlers, recover dataflow,…
 nanashili/rea-rust
Rust port of REA, a local-only reverse-engineering tool with CLI/MCP workflows and a native Ghidra worker
 idiom/pftriage
Python tool and library to help analyze files during malware triage and analysis.
 radareorg/r2web
Access radare2 from anywhere, anytime.
 rog3rsm1th/frelatage
Coverage-based fuzzer for python applications
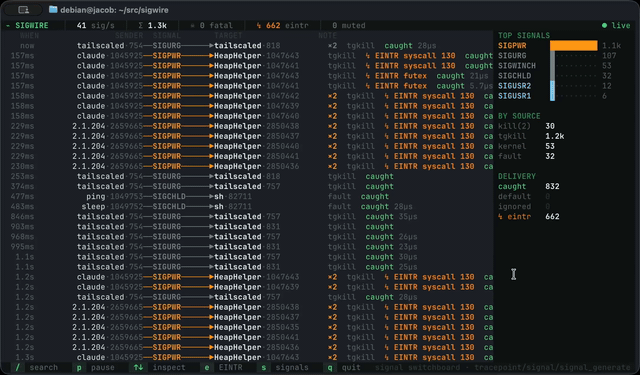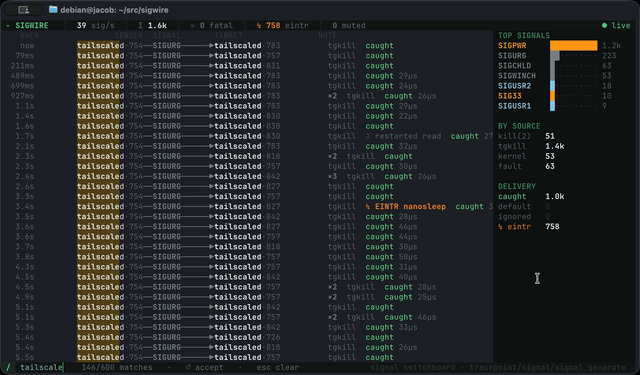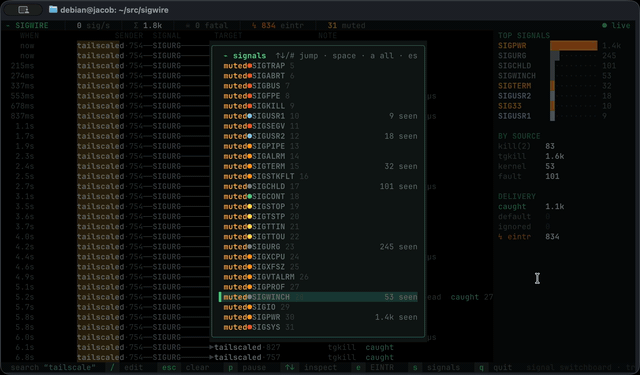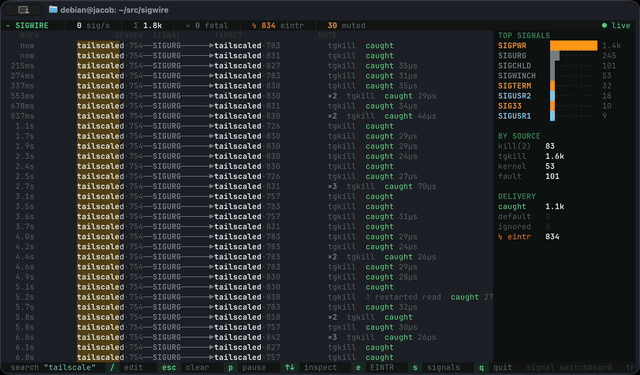 yeet-src/sigwire
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
 hamz-a/frida-android-libbinder
PoC Frida script to view Android libbinder traffic
 0x742/noia
Web-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…








