#2
Tools for observing malware behavior in isolated environments to understand its actions and impact.
Kitploit recommended

 shivammittal2403/cve-2026-80428-ctf
Containerized educational CTF lab emulating CVE-2026-80428 (CWE-502 deserialization) for safe, isolated student and researcher practice.
 off-by-1-labs/flawed
Fix-Like Artifacts With Embedded Defects
 lkimuk/reark
An intelligent reverse engineering analysis tool designed for multiple target platforms, currently supporting HarmonyOS (HAP/APP/ABC) and Android…
 gavmor/x86-cpp-reversing-skill
Claude Code skill for reverse-engineering 32-bit little-endian x86 C++ binaries (vtables, RTTI, inheritance recovery)
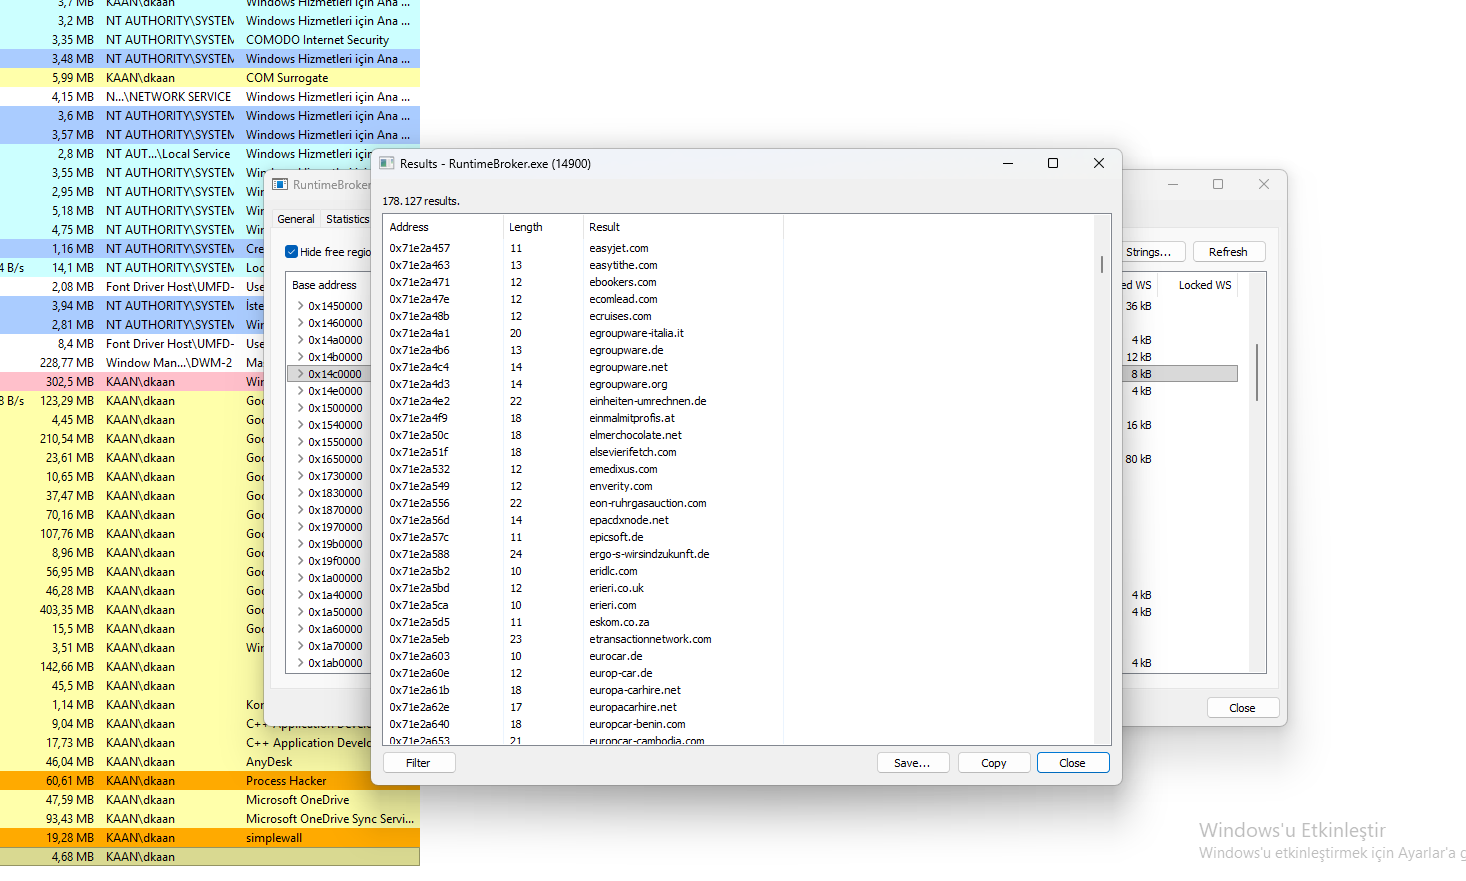 kaandemir993/stealc-stealer-runtimebroker-hollowing-c2-extraction-payload-extraction-analysis
Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 gmh5225/driver-kaldereta
Unsigned Kernel Mode Driver that does memory modifications
 gmh5225/driver-pidqserializationwrite-example
How to use PiDqSerializationWrite. Introduces how to safely read and write from mapped driver
 nathan-luevano/silica
Exhaustive differential validation of all 4.3B AArch64 instruction encodings.
 abhinavagarwal07/gdcm-security-poc
Private end-to-end sanitizer reproduction package for six GDCM findings
 hunt-benito/the-callback-that-outlived-the-page-cve-2026-78997-uc-browser-android-universal-xss
PoC for CVE-2026-78997, a Universal XSS in UC Browser for Android. Includes a crafted URL builder, a callback-dispatch oracle, and Frida hooks to…
 doctormord/philips-pm-5139-5138a-5136-firmware-project
Firmware reverse engineering of the Philips PM5139 / PM5138A / PM5136 function generators: 8051 emulators used as measuring instruments, 35 sections…
 orbitcurve/firmware-reverse-engineering
Agent skills for firmware extraction, static analysis, Ghidra reverse engineering, emulation, and security reporting, packaged for Claude Code and…
 microsoft/mxc
Policy-driven, layered isolation and containment
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
 withsecurelabs/python-exe-unpacker
A helper script for unpacking and decompiling EXEs compiled from python code.
 withsecurelabs/amsidetection
Proof-of-concept tool for detecting AMSI (Antimalware Scan Interface) bypasses and malicious in-memory script activity on Windows endpoints.