
 #1
Security integration in CI/CD pipelines, shift-left, and DevOps security automation tools.
Kitploit recommended

 semgrep/semgrep-rules
Static analysis rule pack for detecting security vulnerabilities, dangerous code patterns, and configuration issues across many languages; integrates…
 cerbos/cerbos
Authorization engine for context-aware access control with YAML policies, RBAC/ABAC support, check/plan APIs, and GitOps-friendly deployment.
 google/osv.dev
Open source vulnerability DB and triage service.
 99designs/aws-vault
A vault for securely storing and accessing AWS credentials in development environments
 deepfence/threatmapper
Open Source Cloud Native Application Protection Platform (CNAPP)
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 yandex/gixy
Nginx configuration static analyzer
 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…
 onecli/onecli
Open-source sandboxed agent harness for teams. Giving every employee a secured personal agent.
 zerobootdev/zeroboot
Sub-millisecond VM sandboxes for AI agents via copy-on-write forking
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
 fairwindsops/polaris
Validation of best practices in your Kubernetes clusters
 open-policy-agent/conftest
Write tests against structured configuration data using the Open Policy Agent Rego query language
 microsoft/whatthehack
A collection of challenge based hack-a-thons including student guide, coach guide, lecture presentations, sample/instructional code and templates. …
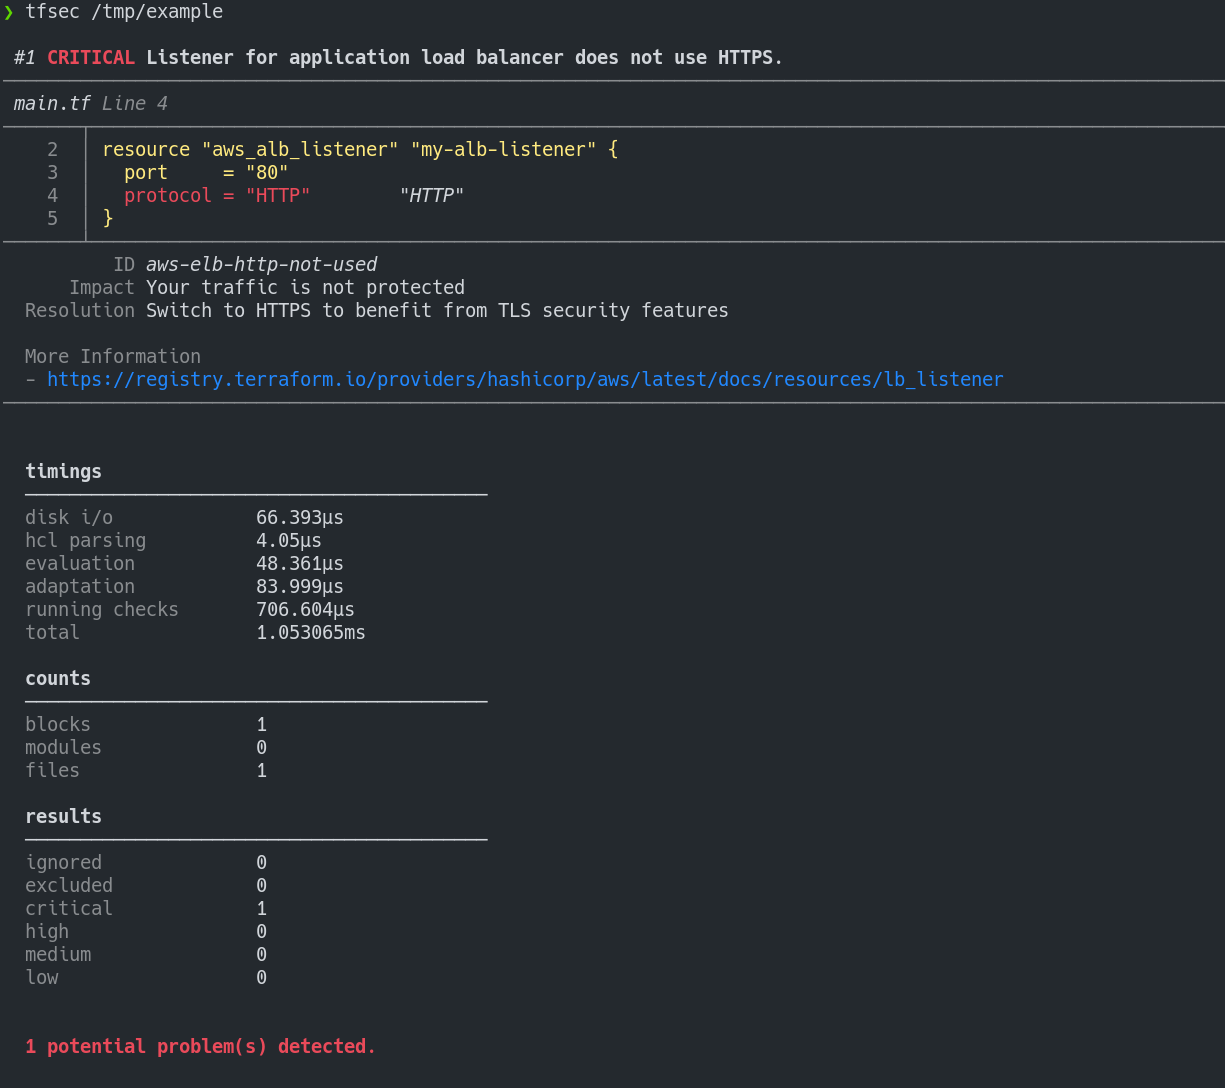 aquasecurity/tfsec
Tfsec is now part of Trivy
 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 flipkart-incubator/astra
Automated Security Testing For REST API's
 nilsteampassnet/teampass
Collaborative Passwords Manager








