
 zerobootdev/zeroboot
Sub-millisecond VM sandboxes for AI agents via copy-on-write forking

Sub-millisecond VM sandboxes for AI agents via copy-on-write forking


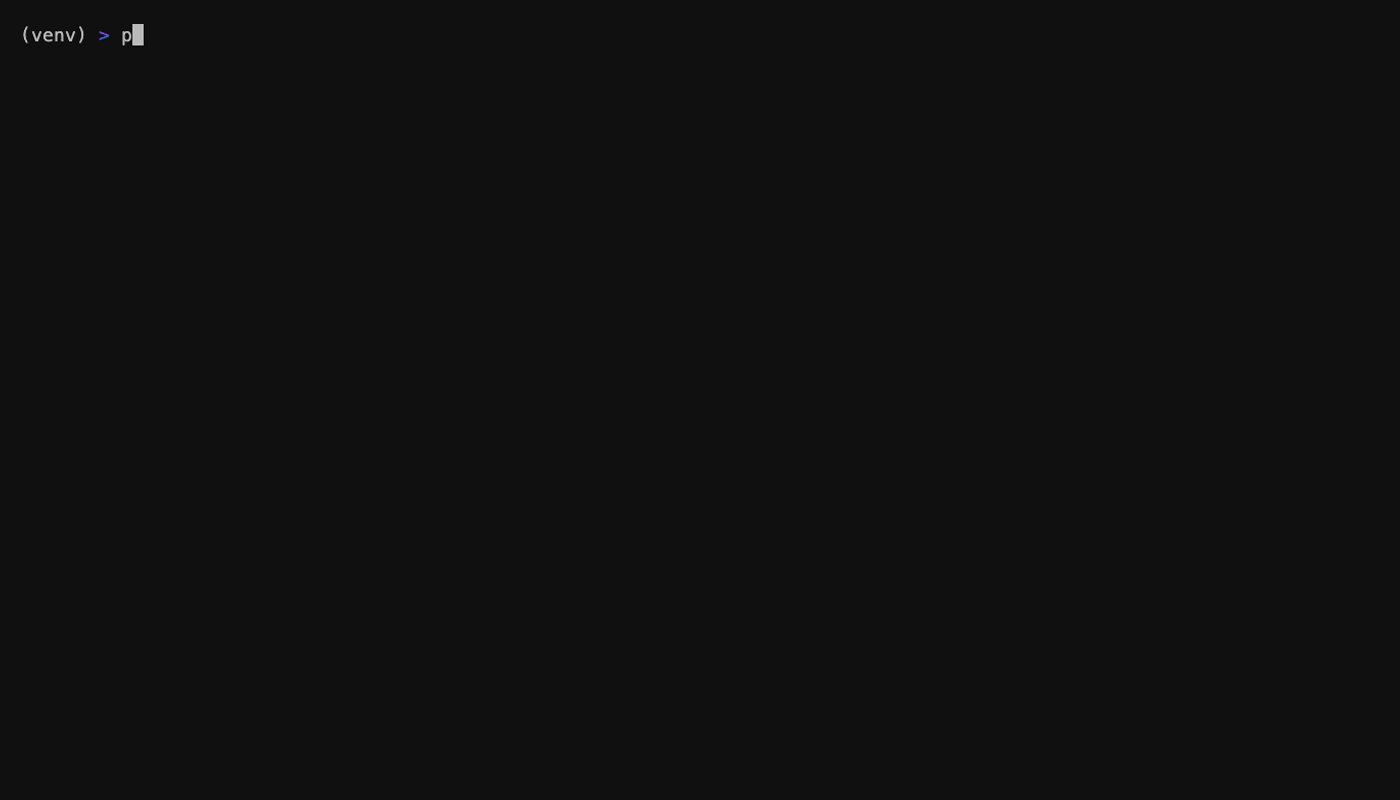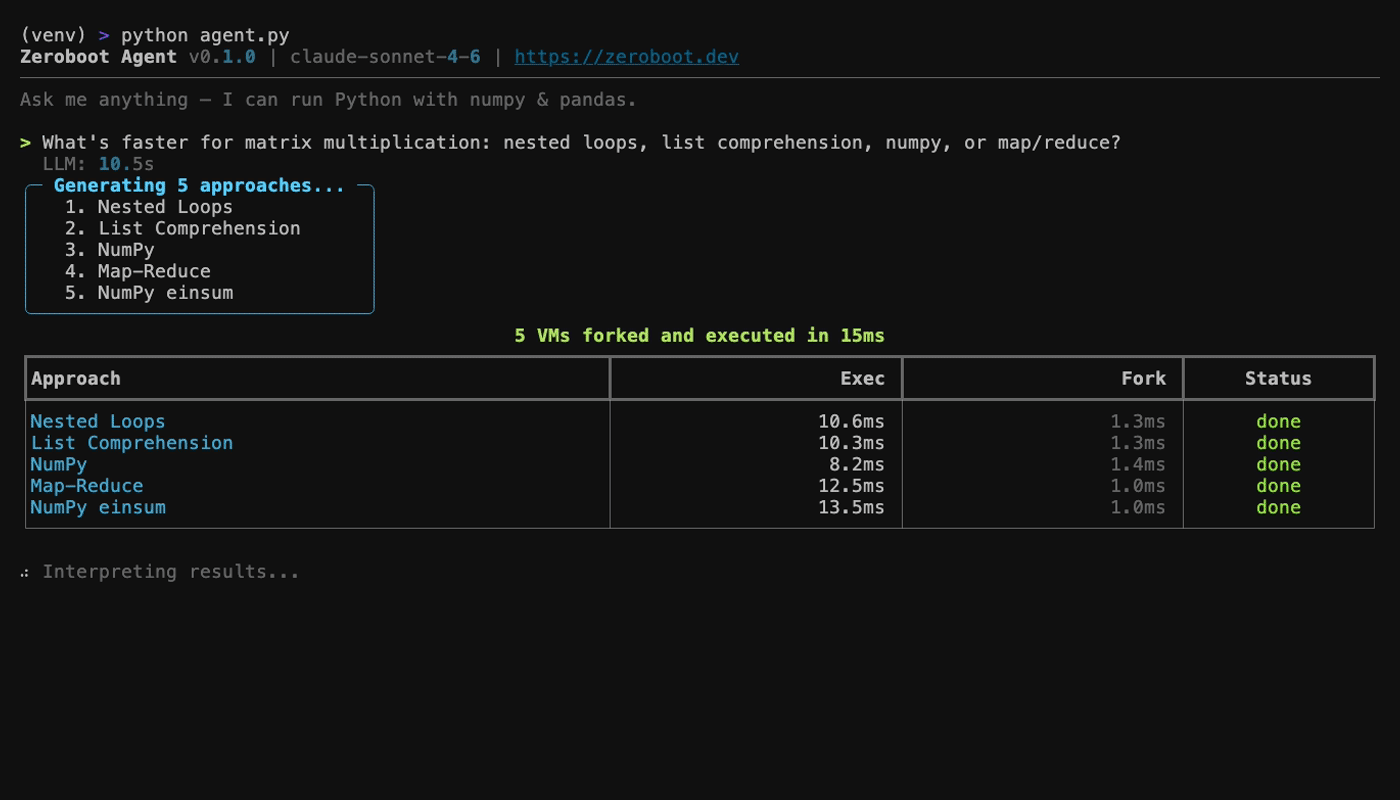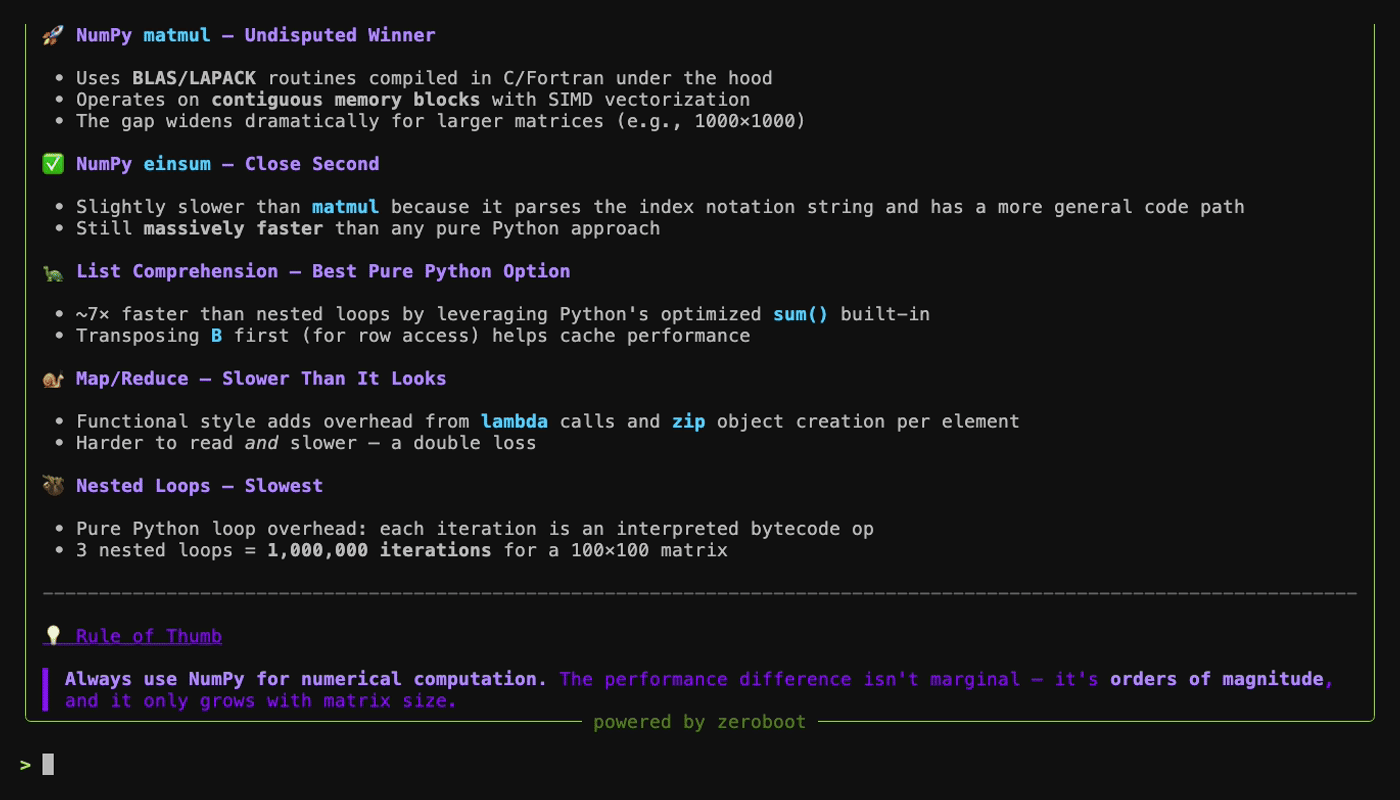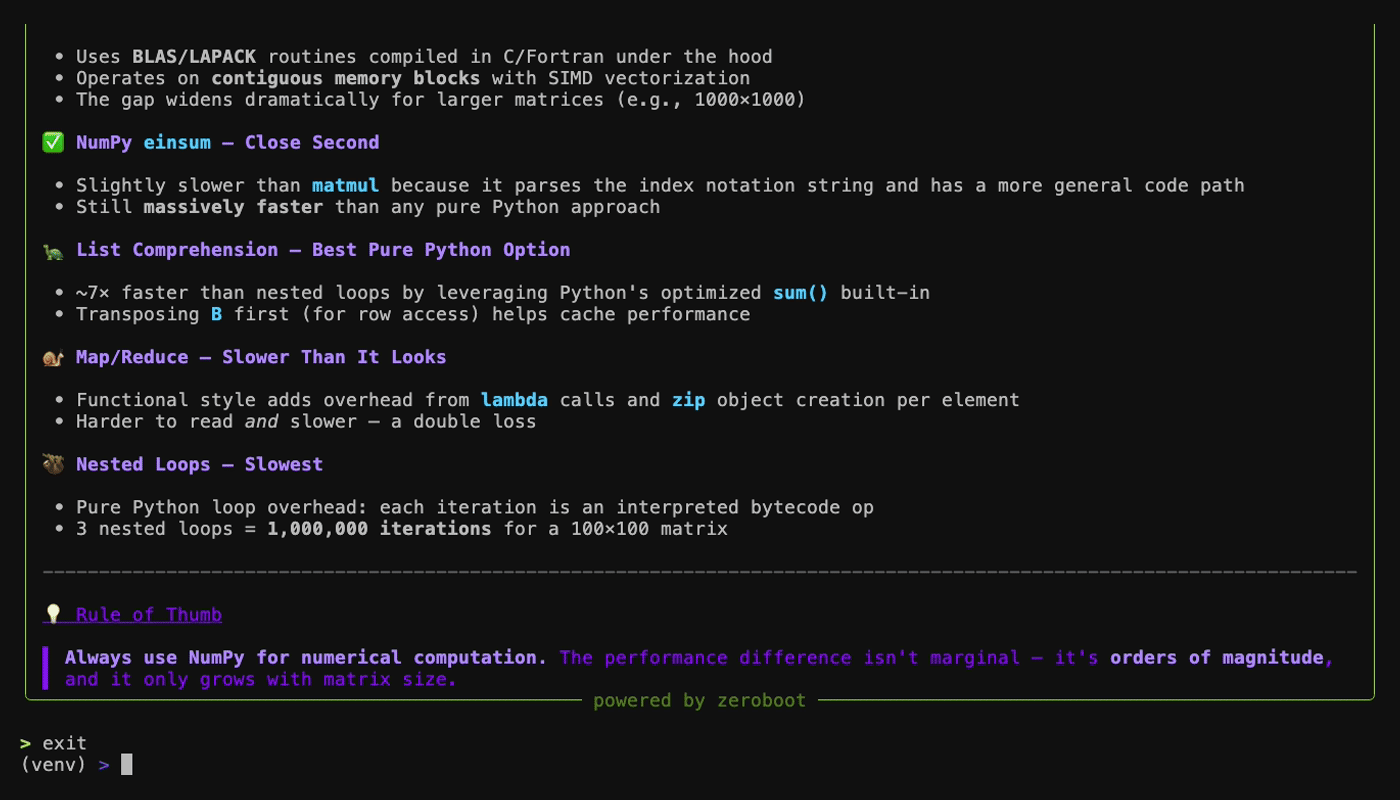
curl -X POST https://api.zeroboot.dev/v1/exec \
  -H 'Content-Type: application/json' \
  -H 'Authorization: Bearer zb_demo_hn2026' \
  -d '{"code":"import numpy as np; print(np.random.rand(3))"}'
| Metric | Zeroboot | E2B | microsandbox | Daytona |
|---|---|---|---|---|
| Spawn latency p50 | 0.79ms | ~150ms | ~200ms | ~27ms |
| Spawn latency p99 | 1.74ms | ~300ms | ~400ms | ~90ms |
| Memory per sandbox | ~265KB | ~128MB | ~50MB | ~50MB |
| Fork + exec (Python) | ~8ms | - | - | - |
| 1000 concurrent forks | 815ms | - | - | - |
Each sandbox is a real KVM virtual machine with hardware-enforced memory isolation.
  Firecracker snapshot ──► mmap(MAP_PRIVATE) ──► KVM VM + restored CPU state
                              (copy-on-write)         (~0.8ms)
Python — sdk/python
from zeroboot import Sandbox
sb = Sandbox("zb_live_your_key")
result = sb.run("print(1 + 1)")
TypeScript — sdk/node
import { Sandbox } from "@zeroboot/sdk";
const result = await new Sandbox("zb_live_your_key").run("console.log(1+1)");
Zeroboot was created in March 2026 and is maintained by Adam Miribyan (@adammiribyan). Project site: zeroboot.dev.
If you use zeroboot in research, please cite it; see CITATION.cff or use the "Cite this repository" button.
If your paper or project uses zeroboot, open an issue or pull request to add it here.
Working prototype. The fork primitive, benchmarks, and API are real, but not production-hardened yet. Open an issue if you're interested.
Zeroboot is open source. Self-host it on any Linux box with KVM, or use the managed API:
curl -X POST https://api.zeroboot.dev/v1/exec \
  -H 'Content-Type: application/json' \
  -H 'Authorization: Bearer zb_demo_hn2026' \
  -d '{"code":"import numpy as np; print(np.random.rand(3))"}'
Building the managed service for teams that don't want to run their own infra. Sign up for early access: https://tally.so/r/aQGkpb
