
 #1
Security integration in CI/CD pipelines, shift-left, and DevOps security automation tools.
Kitploit recommended
 mahradbt/copyfail-mitigation
Ansible playbooks to audit and mitigate CVE-2026-31431 ("Copy Fail"), a local privilege escalation vulnerability in the Linux kernel's `algif_aead`…
 pvharmo2/gha-lab-232af4821f
Security-research lab reproducing CVE-2021-4281 (GHSA-3796-3f93-cfvx): shell command injection via PR head-branch name in…
 abhishek2512mishra/claude-code-security-audit
Security scanner auditing Claude Code environments for CVE-2026-21852 pre-trust execution, hook hijacking, and eBPF lockdown.
 george0papasotiriou/cve-2026-11120-command-injection-via-git-url-in-ci-cd-pipeline
Demonstrates command injection via unsanitized Git URLs in CI/CD pipelines, including a vulnerable build script and exploit example for a critical…
 devstuff/harden-docker-seccomp
Docker mitigation for CVE-2026-31431 ('Copy Fail'). Includes Kubernetes templates as well.
 philippeabraxas-jpg/responsible-alliance-protocol
Safety cannot be a prompt instruction. TBP provides an external execution-layer boundary for autonomous agents, enforcing hard F/I/W invariants via…
 pmontesd/log4j-cve-2021-44228
Very simple Ansible playbook that scan filesystem for JAR files vulnerable to Log4Shell
 pvharmo2/gha-lab-00d54c717d
Security-research lab: CVE-2026-47172 (workflow_run pwn request in deploy.yaml) — flattened snapshot of duck-organization/questbot at 1903b2f
 bakos-sandor-nx/teamcity-cve-2026-63077-remediation
JetBrains TeamCity On-Premises CVE-2026-63077 Emergency Hardening & Patch Runbook Package
 pvharmo2/gha-lab-5bce203f66
Security-research lab: reproduction of CVE-2026-41249 (GHSA-q58j-g3f4-h26h) — pull_request_target pwn request in .github/workflows/static.yml,…
 appsec-forge/appsec-forge
Structured security knowledge base with production-inspired cases: vulnerability analysis, exploit explanation, remediation, and DevSecOps for…
 paveg/rails-activestorage-vips-audit
Agent skill that audits a Rails codebase for CVE-2026-66066 (KindaRails2Shell) — Active Storage + libvips arbitrary file read / RCE, checking Rails…
 roxanne_ardary/aurea
Aurea is an open-source, AI-powered platform that secures infrastructure-as-code (IaC) across Terraform, Kubernetes, Docker, and Ansible. It…
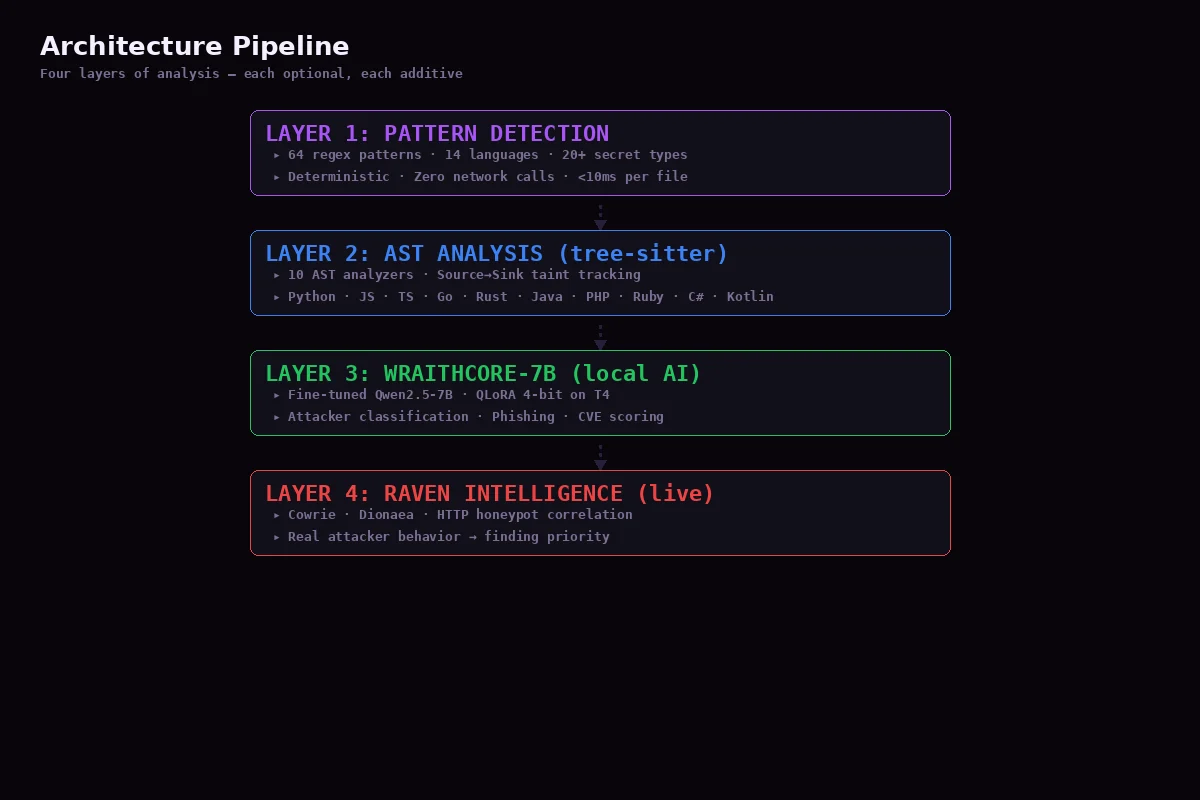 niffyhunt/codeguard-copilot
AI-powered security co-pilot that catches vulnerabilities as you code. Real-time security scanning, educational explanations, and auto fixes for…
 rh-rahulshetty/log4shell-cve-2021-44228
Deliberately vulnerable Java/Maven fixture for testing Log4Shell (CVE-2021-44228) detection, code-impact classification, and remediation guidance in…
 pvharmo2/gha-lab-ba8e0c4217
Authorized security-research lab: reproduction of CVE-2024-42370 / GHSA-4hq2-rpgc-r8r7 (env injection in docs-preview.yml) — snapshot of…
 pvharmo2/gha-lab-ca4fa82ac5
Security-research lab: reproduction of CVE-2026-29075 (GHSA-3j55-5q6x-2h48) in mesa/mesa benchmarks.yml pull_request_target workflow — single-commit…
 gduma-phdata/patch-cve-2026-09881
Patch: Template injection RCE (Atlassian Confluence)








