
 #1
Security integration in CI/CD pipelines, shift-left, and DevOps security automation tools.
Kitploit recommended

 aquasecurity/vex-repo-spec
VEX Repository Specification
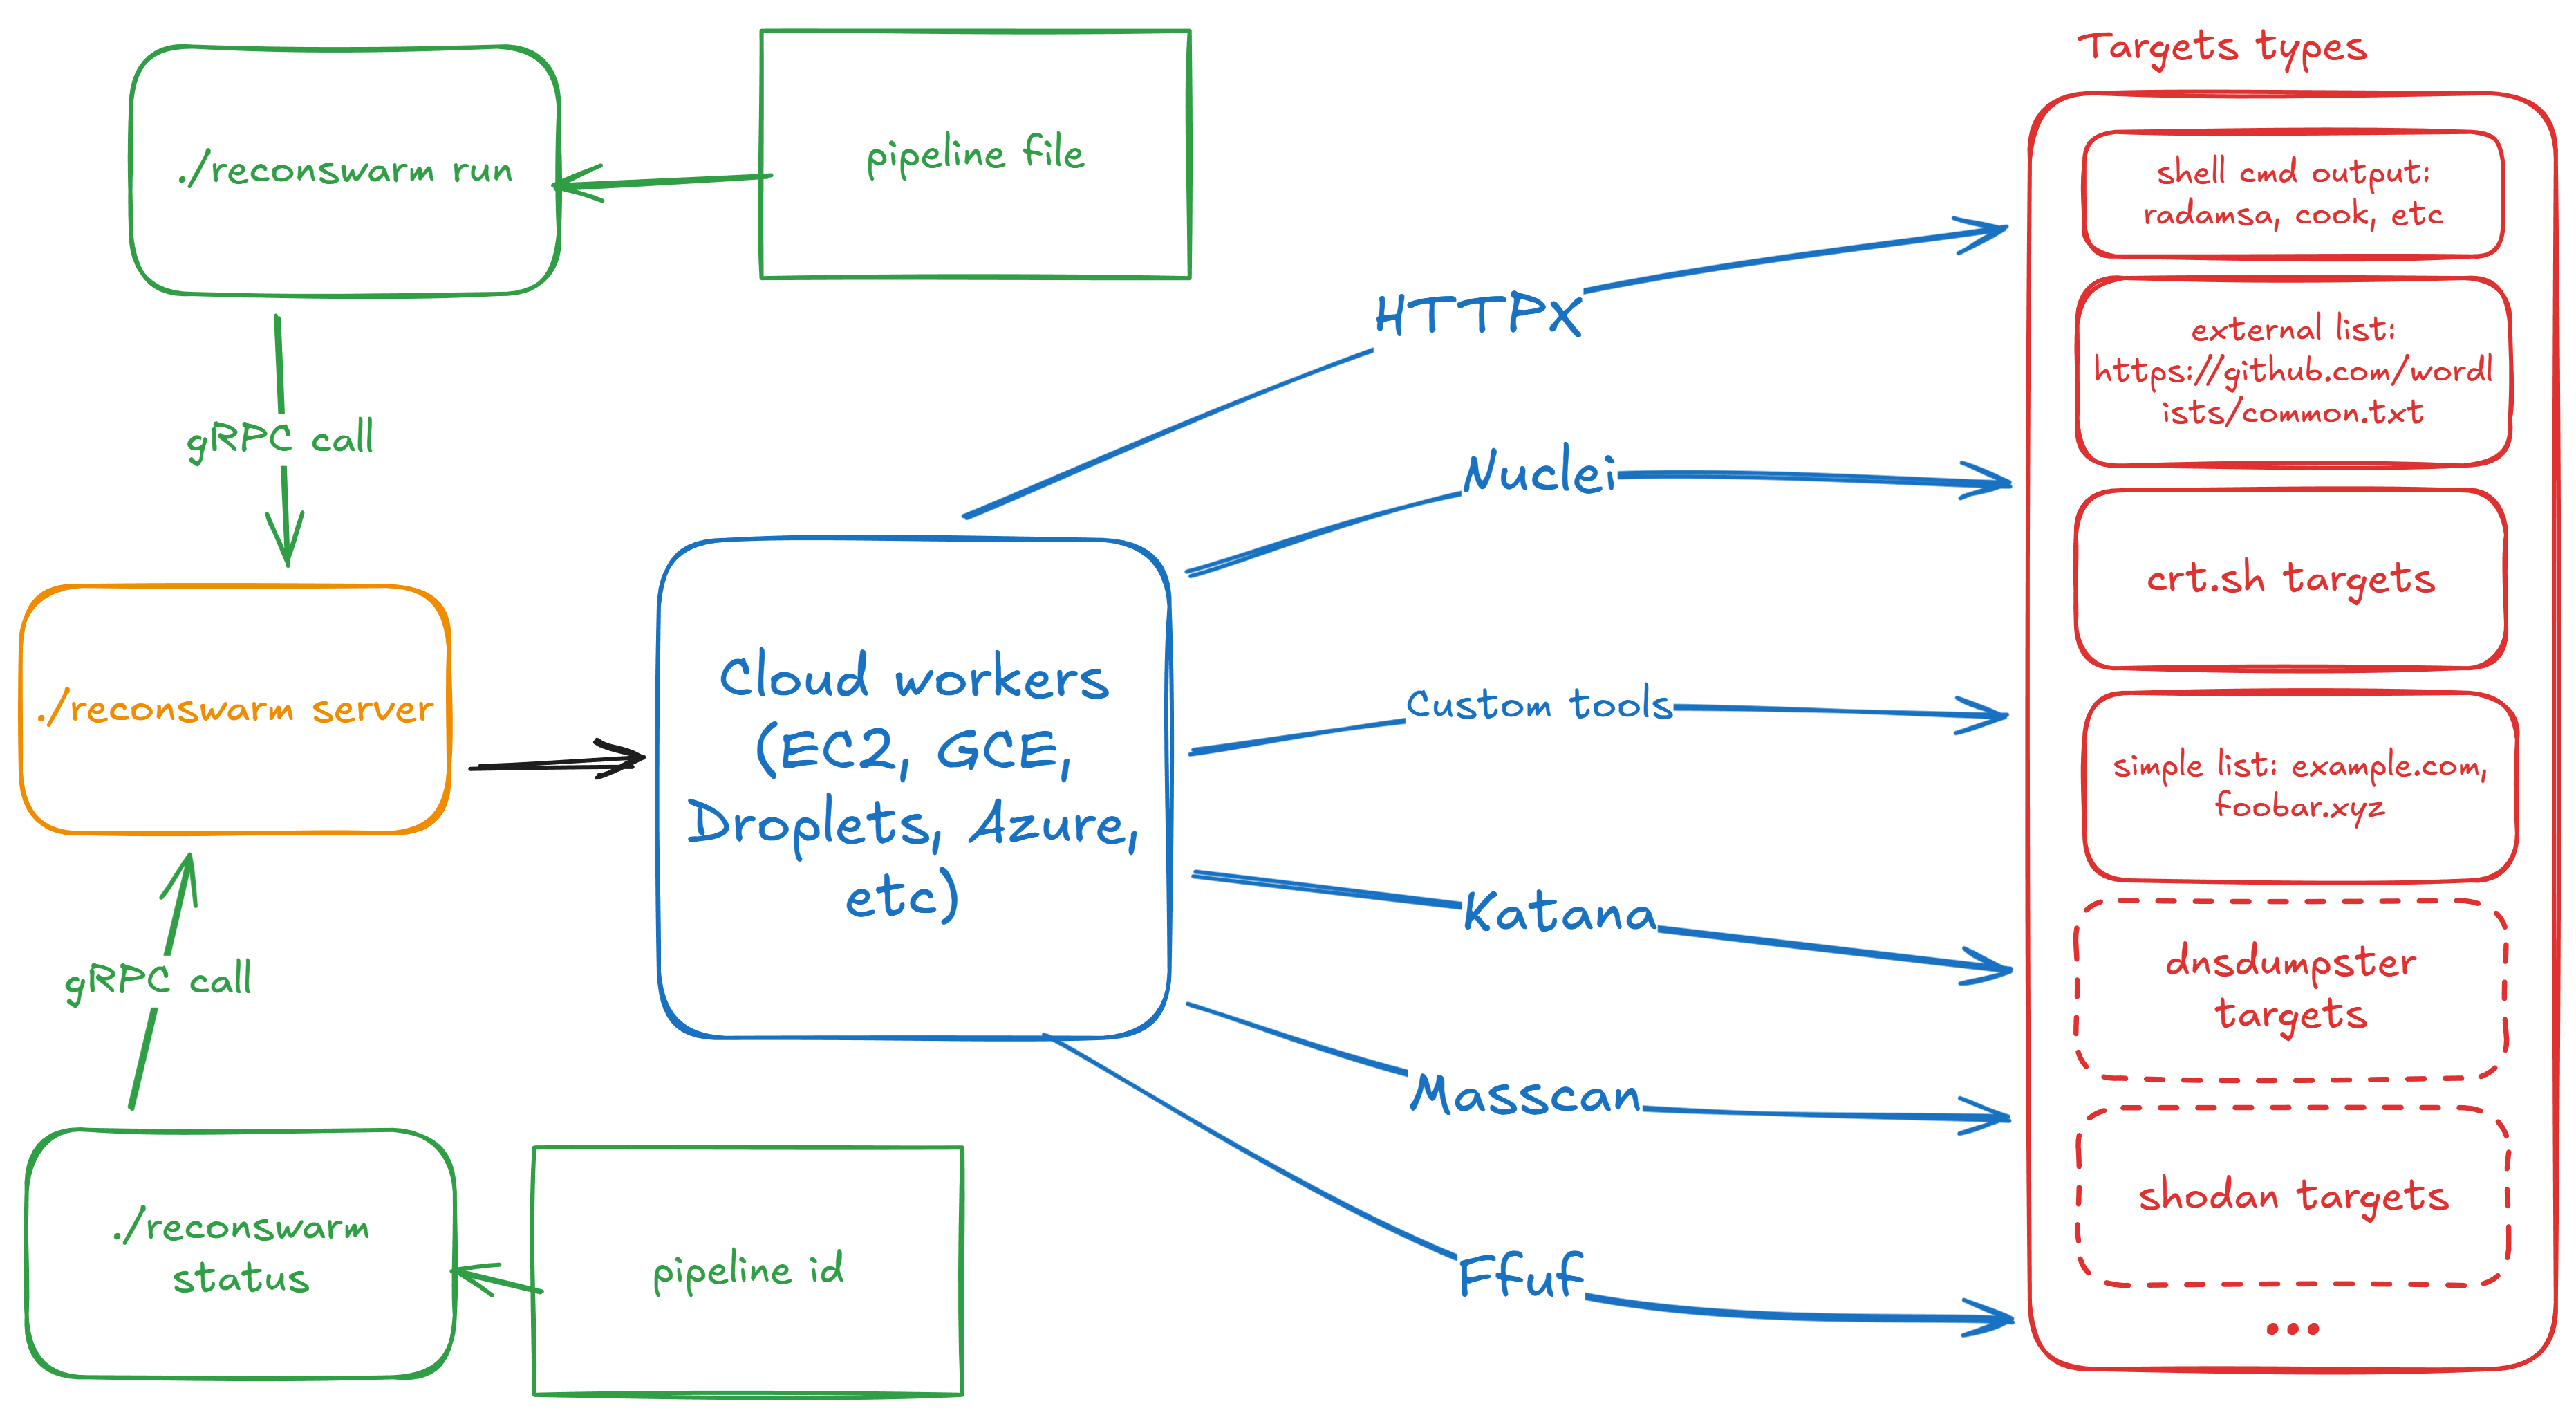 renatus-cartesius/reconswarm
Extend your recon with cloud power
 aquasecurity/trivy-plugin-attest
Publish SBOM attestation
 iulianvostrut/contexthound
Static analysis CLI that scans codebases for LLM prompt-injection, data-exfiltration, jailbreak, and unsafe agent/tool vulnerabilities. Runs fully…
 codesource/copyfail-check
Archived, moved to codesource/cve-check. Shell script to detect CVE-2026-31431 (Copy Fail) exposure and mitigations on Linux systems: kernel check,…
 nu0l/nginx-rift
CVE-2026-42945 NGINX 堆溢出漏洞扫描与验证工具
 xiaoqimikko/spring-cvss-check
Scans Java artifacts and source for Spring/Tomcat CVEs, compares vendor vs NVD CVSS scores, verifies exploitability conditions, and checks if fix…
 heroku/heroku-cve-2013-0269
Inspect all of your Heroku apps for vulnerable versions of the JSON gem

 leitwacht/leitwacht
Leitwacht control plane — runtime security for GitLab Runner CI/CD: policy authoring, multi-tenancy, audit, GitLab integration
 moderneinc/rewrite-cve-2026-22732
OpenRewrite recipe that detects and fixes Spring Security header suppression (CVE-2026-22732) by identifying Content-Length header misuse and…
 squid-protocol1/gitgalaxy
AST-free heuristic knowledge graph engine for deep repository intelligence and zero-trust security scanning. Integrates as a GitLab CI/CD component,…
 knqyf263/go-mal-pkgs
A security tool to detect malicious Go packages by verifying checksums in go.sum against the original source code
 g0dse11/detecttrace
Open-source detection engineering tool that traces security detections end to end and identifies the first failing stage.
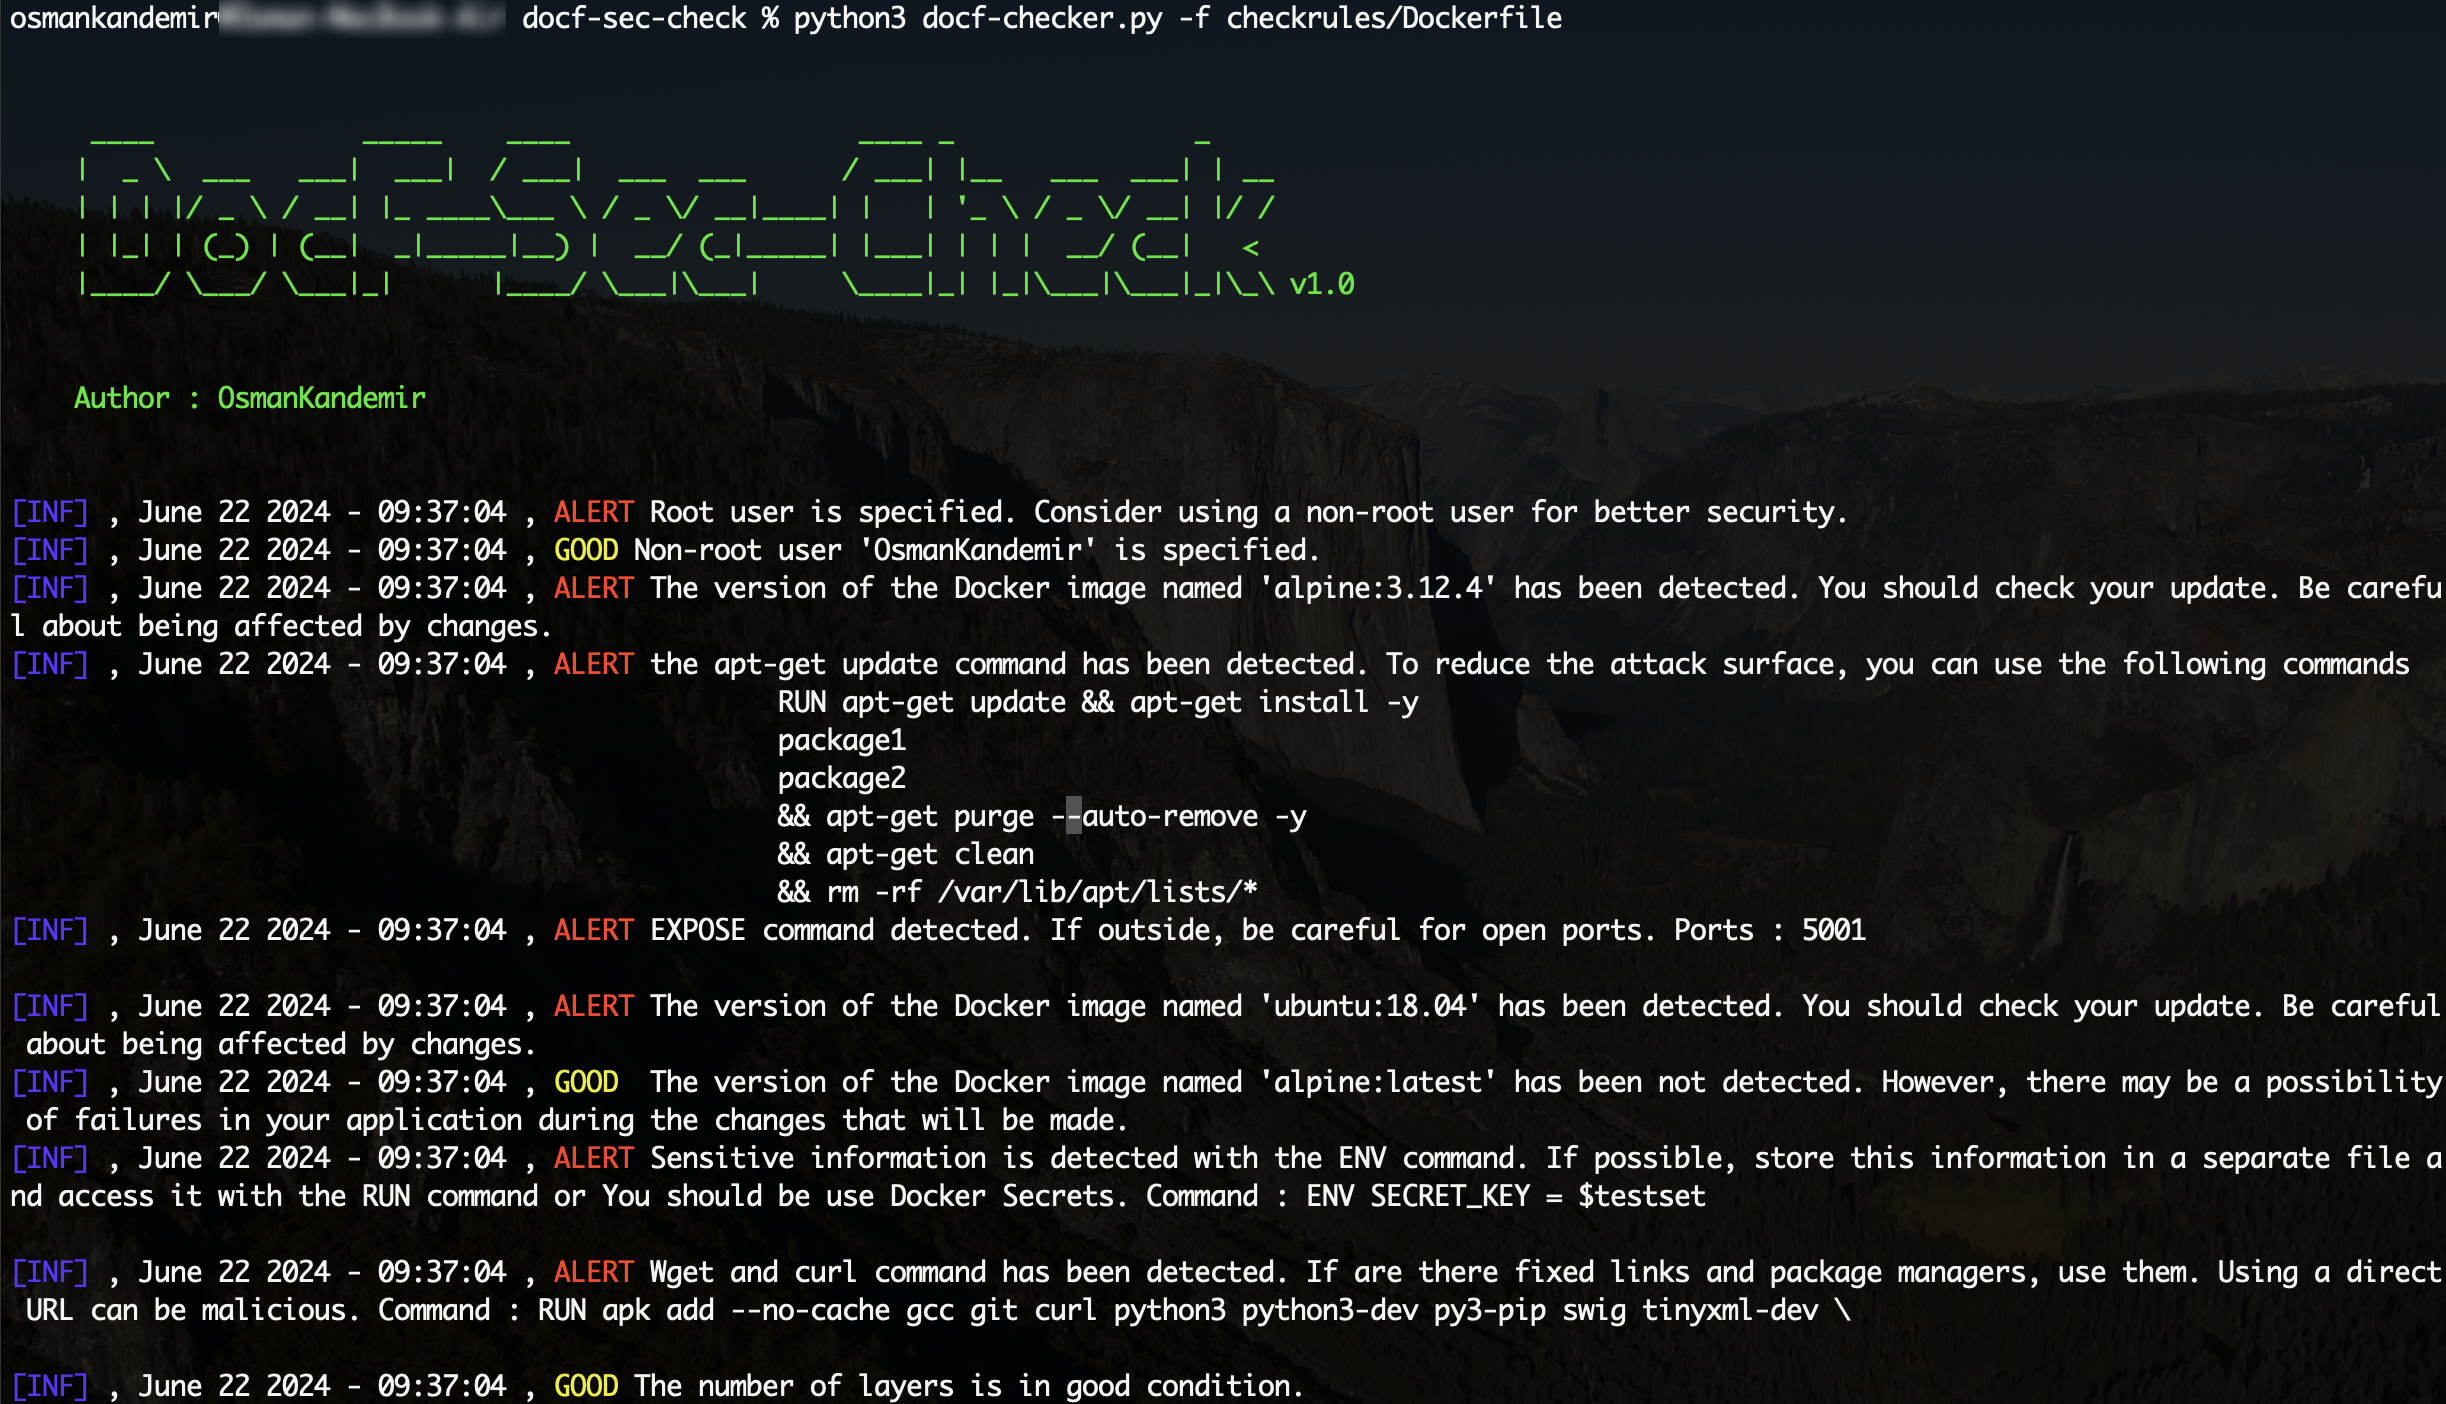 osmankandemir/docf-sec-check
Static analysis tool that scans Dockerfiles for insecure commands and configuration issues, providing actionable security notifications to harden…
 studiomeyer-io/mcp-stdio-shellguard
Defense-in-depth bundle for MCP stdio servers: drop-in guardExec/guardSpawn wrappers, AST audit CLI, reference MCP server. Closes the Ox-Security…
 aquasecurity/trivy-module-wordpress
Trivy example module for WordPress
 d0rb/shellscope
Defensive exposure auditor for Plex2Shell and php2shell — find your own before they find you.
 irgoncalves/f5-waf-quick-patch-cve-2021-44228
This tool creates a custom signature set on F5 WAF and apply to policies in blocking mode








