#1
Security integration in CI/CD pipelines, shift-left, and DevOps security automation tools.
Kitploit recommended
 mhaskar/bughound
Static code analysis tool based on Elasticsearch
 aaaguirrep/offensive-docker-vps
Create a VPS on Google Cloud Platform or Digital Ocean easily with Offensive Docker included to launch assessment to the targets.
 purpleteam-labs/purpleteam-app-scanner
Application scanning component of purpleteam
 shanika04/apache_skywalking
CVE-2020-9483 OR CVE-2020-13921
 shanika04/cloudfoundry_uaa
CVE-2016-4468
 rauc/rauc-1.5-integration
integration examples for the CVE-2020-25860 fix
 purpleteam-labs/purpleteam-tls-checker
TLS checking component of purpleteam
 purpleteam-labs/purpleteam-server-scanner
Server scanning component of purpleteam
 purpleteam-labs/purpleteam-s2-containers
Stage two containers
 purpleteam-labs/purpleteam-orchestrator
Orchestration component of purpleteam
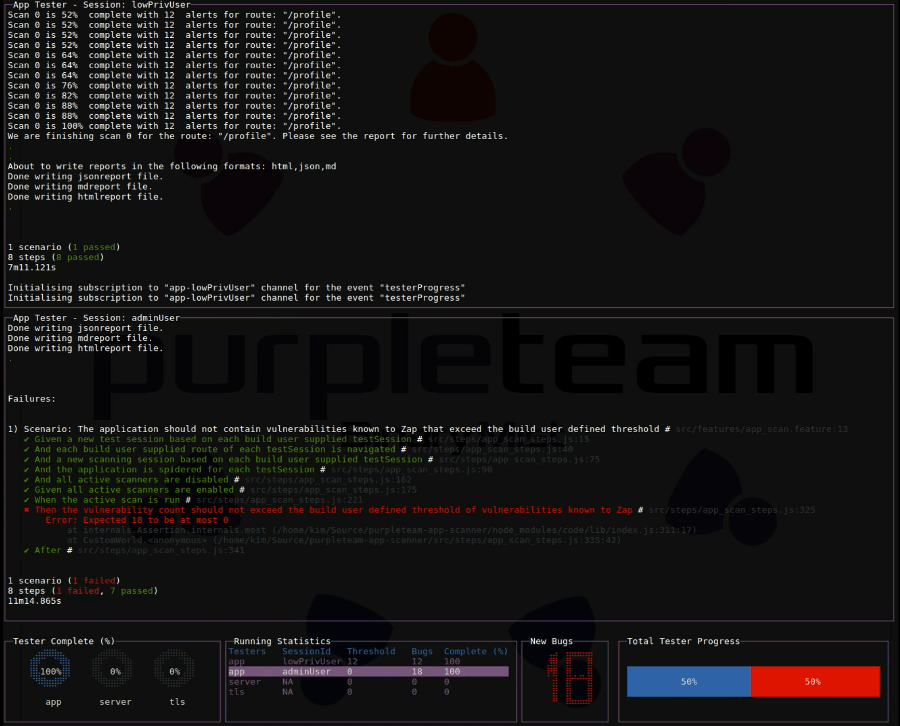 purpleteam-labs/purpleteam
CLI component of purpleteam
 threatspec/threatspec
threatspec - continuous threat modeling, through code
 flyniu666/ingress-nginx-0.21-1.19.5
based on nginx 1.19.5 to fix for CVE-2018-16843, CVE-2018-16844, CVE-2019-9511, CVE-2019-9513, and CVE-2019-9516
 resery/cve-2019-17041
Proof-of-concept exploit for CVE-2019-17041, a buffer overflow in rsyslog's parser, demonstrating remote code execution.
 dev-sec/ansible-ssh-hardening
This Ansible role provides numerous security-related ssh configurations, providing all-round base protection.
 guettli/fix-cve-2020-15228
Python script that automatically patches GitHub Actions workflow files to replace deprecated and insecure ::set-env and ::add-path commands with the…
 michenriksen/drawio-threatmodeling
Draw.io libraries for threat modeling diagrams