

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
DevSecOps — Page 28 | Kitploit
Categories

DevSecOps

Security integration in CI/CD pipelines, shift-left, and DevOps security automation tools.

Kitploit recommended

Top tools

10 selected
trivy preview#1

trivy

GitHubaquasecurity/trivy
37.4k16h 13m ago
semgrep preview#2

semgrep

GitHubsemgrep/semgrep
16.2k3 days ago
gitleaks preview#3

gitleaks

GitHubgitleaks/gitleaks
28.6k27 days ago
trufflehog preview#4

trufflehog

GitHubtrufflesecurity/trufflehog
27.4k1 day ago
checkov preview#5

checkov

GitHubbridgecrewio/checkov
8.9k16h 51m ago
grype preview#6

grype

GitHubanchore/grype
12.7k1 day ago
syft preview#7

syft

GitHubanchore/syft
9.9k3 days ago
dependency-track preview#8

dependency-track

GitHubdependencytrack/dependency-track
4.1k1 day ago
DependencyCheck preview#9

DependencyCheck

GitHubdependency-check/dependencycheck
7.8k4 days ago
osv-scanner preview#10

osv-scanner

GitHubgoogle/osv-scanner
10.8k1 day ago
NewestRelevanceMost popularRecently updated
1100 results
MCPwner preview

MCPwner

GitHubpigyon/mcpwner

Model Context Protocol server for autonomous vulnerability discovery

penetration-testing-frameworksreconnaissancestatic-analysis+6
533 months ago
Log4ShellAuditor preview

Log4ShellAuditor

GitHubc00ln3t/log4shellauditor

An autonomous reflective Go agent for full-cycle security auditing, WAF evasion, OOB LDAP verification, self-remediation (auto-patching), and…
vulnerability-scannerspayload-generationport-scanning+6
13 months ago
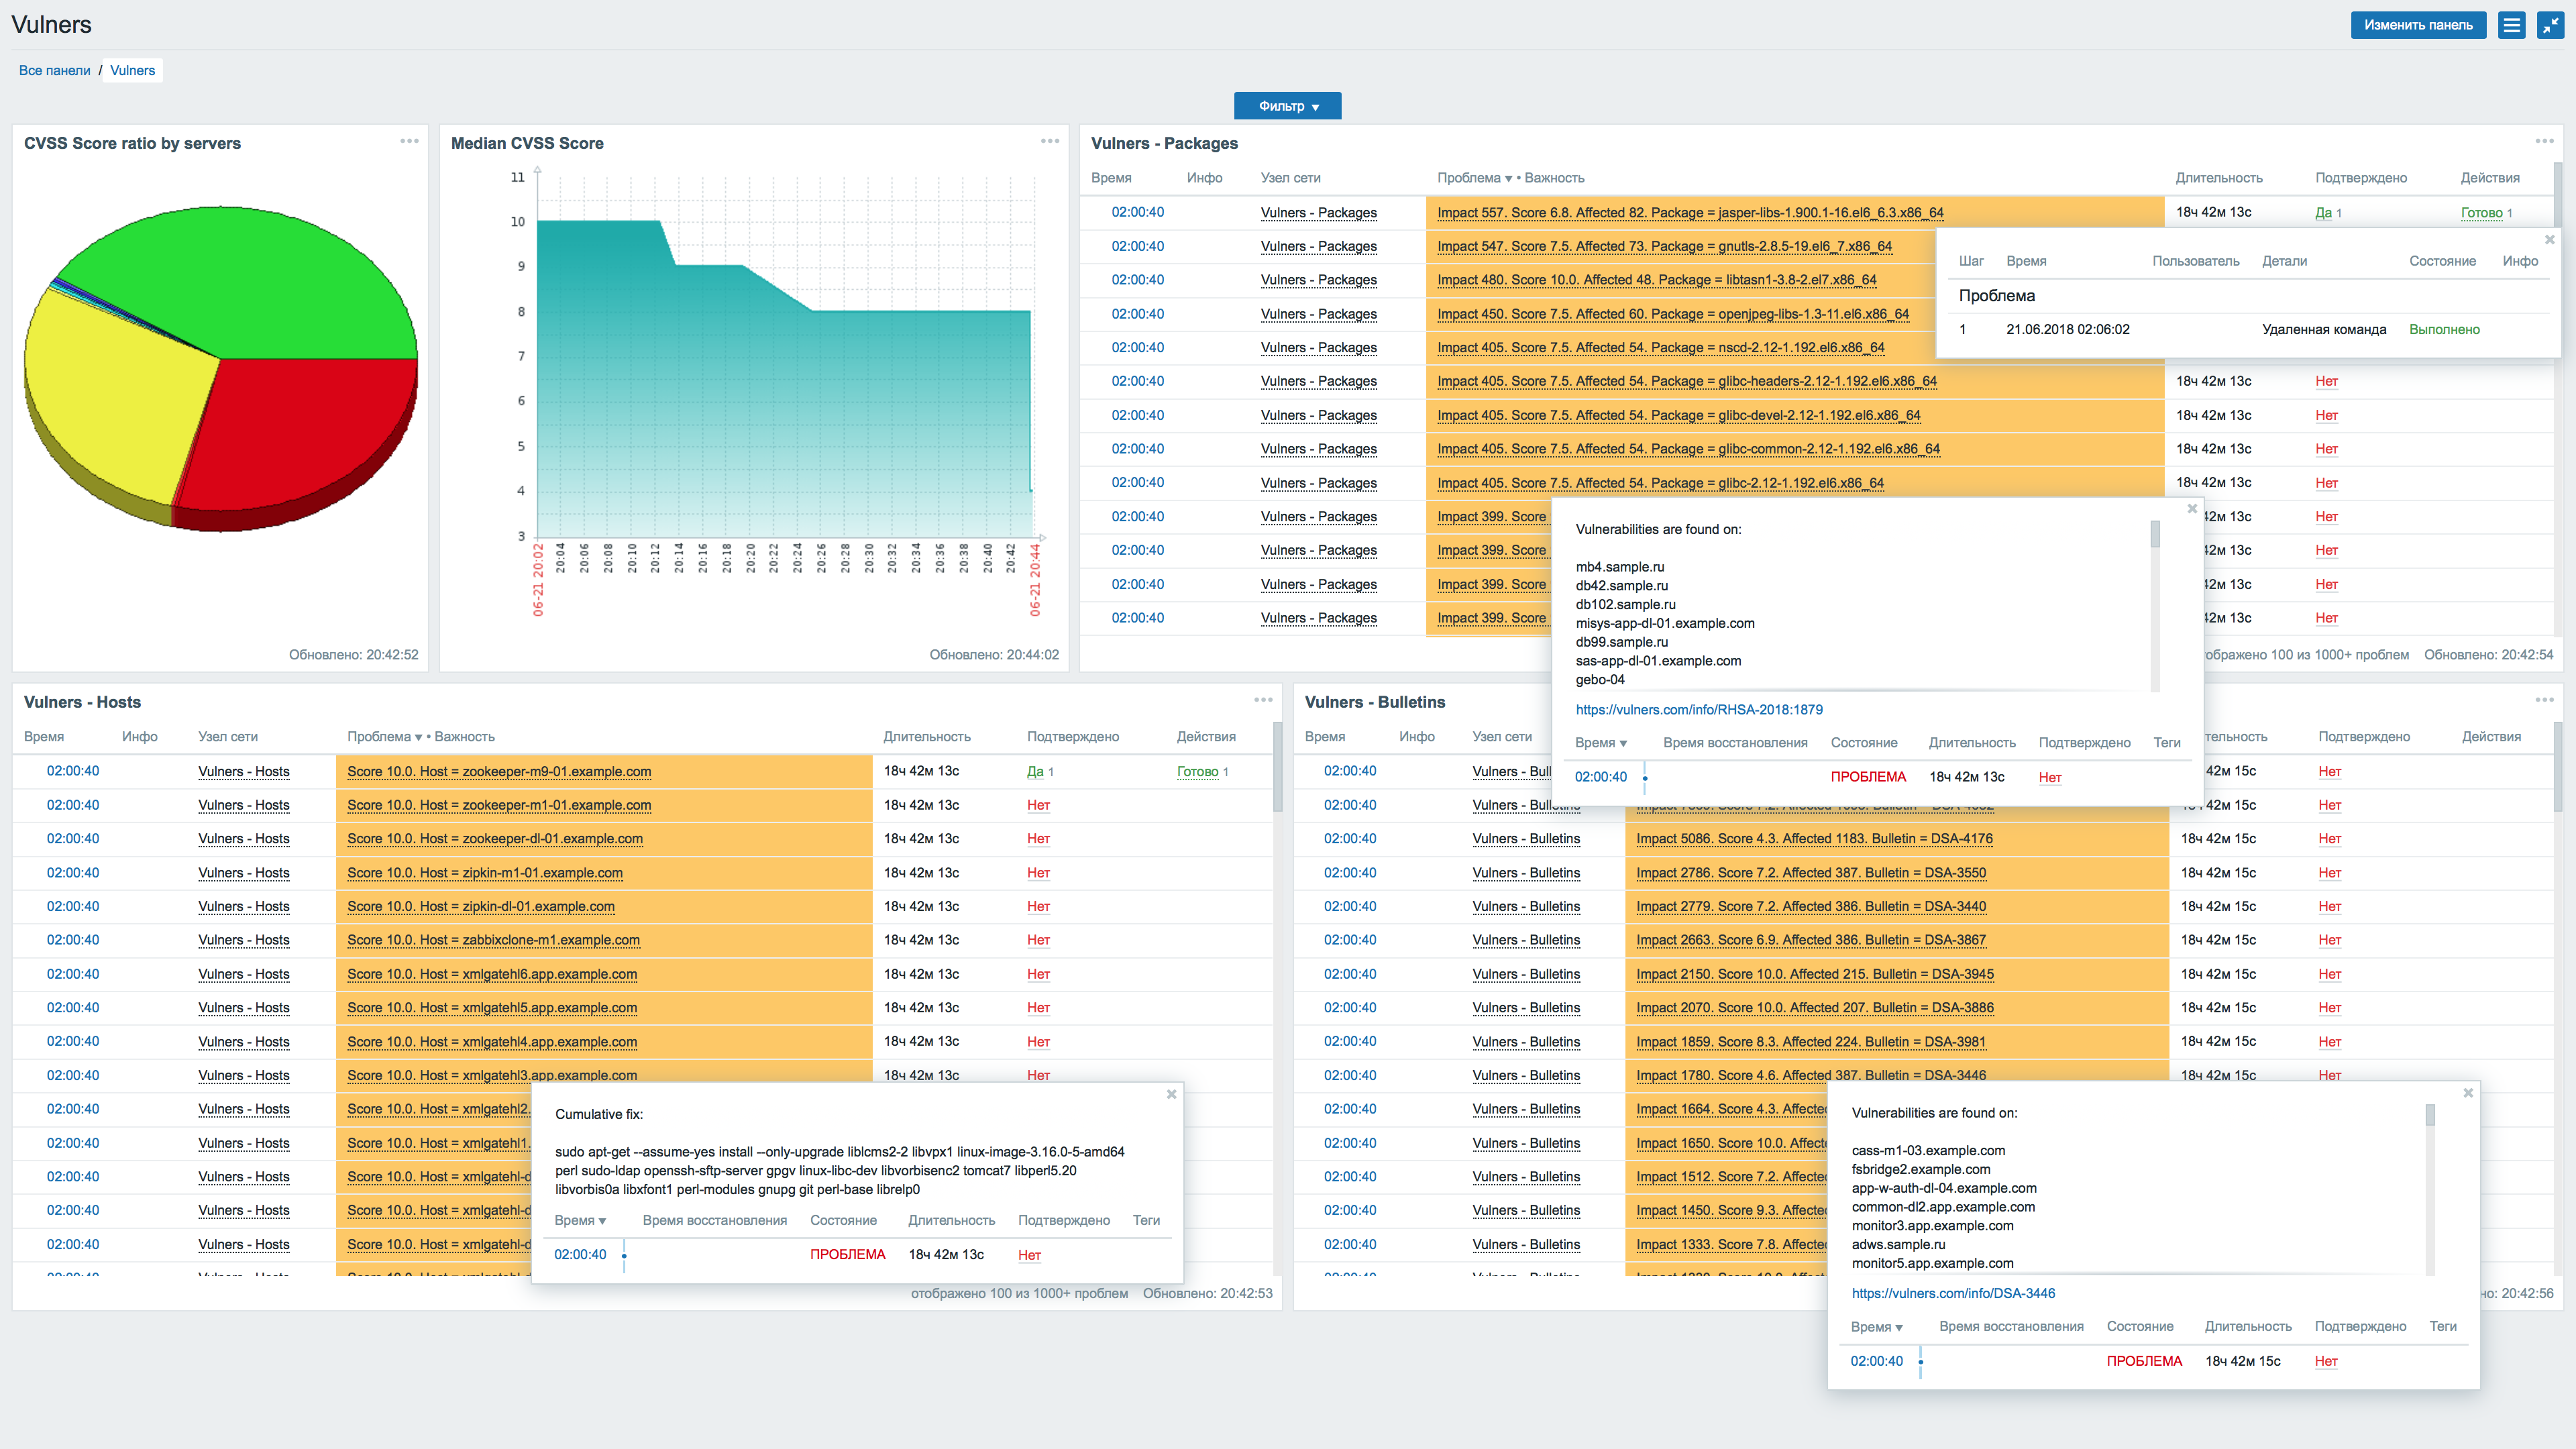
zabbix-threat-control preview

zabbix-threat-control

GitHubvulnerscom/zabbix-threat-control

Zabbix vulnerability assessment plugin

vulnerability-scannersvulnerability-analysisconfiguration-auditing+1
2223 months ago
clawk preview

clawk

GitHubclawkwork/clawk

Give coding agents a disposable Linux VM, not your laptop

container-securitydynamic-analysis-sandboxingsecurity-virtualization+3
7583 months ago
azure-sentinel-detection-engineering preview

azure-sentinel-detection-engineering

GitHubibondarenko1/azure-sentinel-detection-engineering

9 MITRE ATT&CK-mapped KQL detections on a live Microsoft Sentinel + Defender XDR environment (control-plane, endpoint, identity), with a PR-gated…

vulnerability-scannersconfiguration-auditingcloud-security+4
53 months ago
defending-code-reference-harness preview

defending-code-reference-harness

GitHubanthropics/defending-code-reference-harness

Skills for threat modeling, scanning, triage, patching, plus an autonomous scanning harness you can /customize

static-analysisvulnerability-scannersdynamic-analysis-sandboxing+6
7.0k3 months ago
Vulnhalla preview

Vulnhalla

GitHubcyberark/vulnhalla

Automated security analysis pipeline that runs CodeQL queries on GitHub repositories and uses LLMs to classify and filter true vulnerabilities from…

static-analysisvulnerability-analysiscode-analysis+4
2013 months ago
flar preview

flar

GitHubswelljoe/flar

Lightweight CLI tool that runs AI coding agents inside isolated Bubblewrap sandboxes with strict filesystem, network, and credential isolation to…

privilege-escalationcontainer-securityids-ips-evasion+5
513 months ago
CVE-2026-22018-Jenkins-Pipeline-Shared-Library-Code-Execution-via-Grab- preview

CVE-2026-22018-Jenkins-Pipeline-Shared-Library-Code-Execution-via-Grab-

GitHubgeorge0papasotiriou/cve-2026-22018-jenkins-pipeline-shared-library-code-execution-via-grab-

PoC for CVE-2026-22018, a critical Jenkins Pipeline Shared Library RCE via Groovy @Grab, demonstrating supply-chain code injection and mitigation…

vulnerability-analysisexploitationweb-application-exploitation+2
13 months ago
teamcity-cve-2026-63077-remediation preview

teamcity-cve-2026-63077-remediation

GitHubbakos-sandor-nx/teamcity-cve-2026-63077-remediation

JetBrains TeamCity On-Premises CVE-2026-63077 Emergency Hardening & Patch Runbook Package

cloud-infrastructure-securityconfiguration-auditingnetwork-security+6
3 months ago
Veritensor preview

Veritensor

GitHubarsbr/veritensor

The Anti-Virus for AI Artifacts & RAG Firewall. A static analysis tool scanning Models and Notebooks for RCE, Datasets and RAG docs for Data…
static-analysisvulnerability-scannersencryption-decryption-tools+8
853 months ago
CVE-2026-11120-Command-Injection-via-Git-URL-in-CI-CD-Pipeline preview

CVE-2026-11120-Command-Injection-via-Git-URL-in-CI-CD-Pipeline

GitHubgeorge0papasotiriou/cve-2026-11120-command-injection-via-git-url-in-ci-cd-pipeline

Demonstrates command injection via unsanitized Git URLs in CI/CD pipelines, including a vulnerable build script and exploit example for a critical…
vulnerability-analysisexploitationdevsecops+1
3 months ago
rusty-hog preview

rusty-hog

GitHubnewrelic/rusty-hog

Multi-source secret scanner detecting API keys, passwords, and PII across Git repos, S3 buckets, filesystems, Confluence, JIRA, Slack, and Google…

code-analysiscloud-securitydevsecops+1
5553 months ago
mcp-server preview

mcp-server

GitHuboffensive360/mcp-server

MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…

static-code-analysisvulnerability-analysiscode-analysis+3
3 months ago
sast-scan-action preview

sast-scan-action

GitHuboffensive360/sast-scan-action

GitHub Action for Offensive360 SAST: scan a repository and upload SARIF results to GitHub code scanning. Free for eligible open-source projects.

vulnerability-scannersstatic-code-analysiscode-analysis+4
3 months ago
SharkTooth preview

SharkTooth

GitHubznakar/sharktooth

Port Scanner with Docker & Prometheus + Grafana integration. A tool for network auditing with multithreading support and real-time monitoring.

container-securitynetwork-mappingport-scanning+2
43 months ago
semgrep-rules preview

semgrep-rules

GitHubelttam/semgrep-rules

Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…

cloud-infrastructure-securitystatic-analysiscontainer-security+6
2463 months ago
azure-security-auditor preview

azure-security-auditor

GitHubneelkotnis/azure-security-auditor

CLI tool to audit Azure security posture, RBAC, NSGs, storage, identity, and encryption

cloud-infrastructure-securitydefensive-toolsconfiguration-auditing+5
13 months ago
Previous1…272829…62Next








