
 #1
Security integration in CI/CD pipelines, shift-left, and DevOps security automation tools.
Kitploit recommended

 americanhanko/windows-security-cve-2017-8543
InSpec profile to verify a node is patched and compliant for CVE-2017-8543
 aquasecurity/vex-repo-spec
VEX Repository Specification
 imlzw/kubernetes-1.12.3-all-auto-install
个人整理的Centos7.x + Kubernetes-1.12.3 + Dashboard-1.8.3 无 CVE-2018-1002105 漏洞的master节点全自动快速一键安装部署文件,适用于测试环境,生产环境的快速安装部署
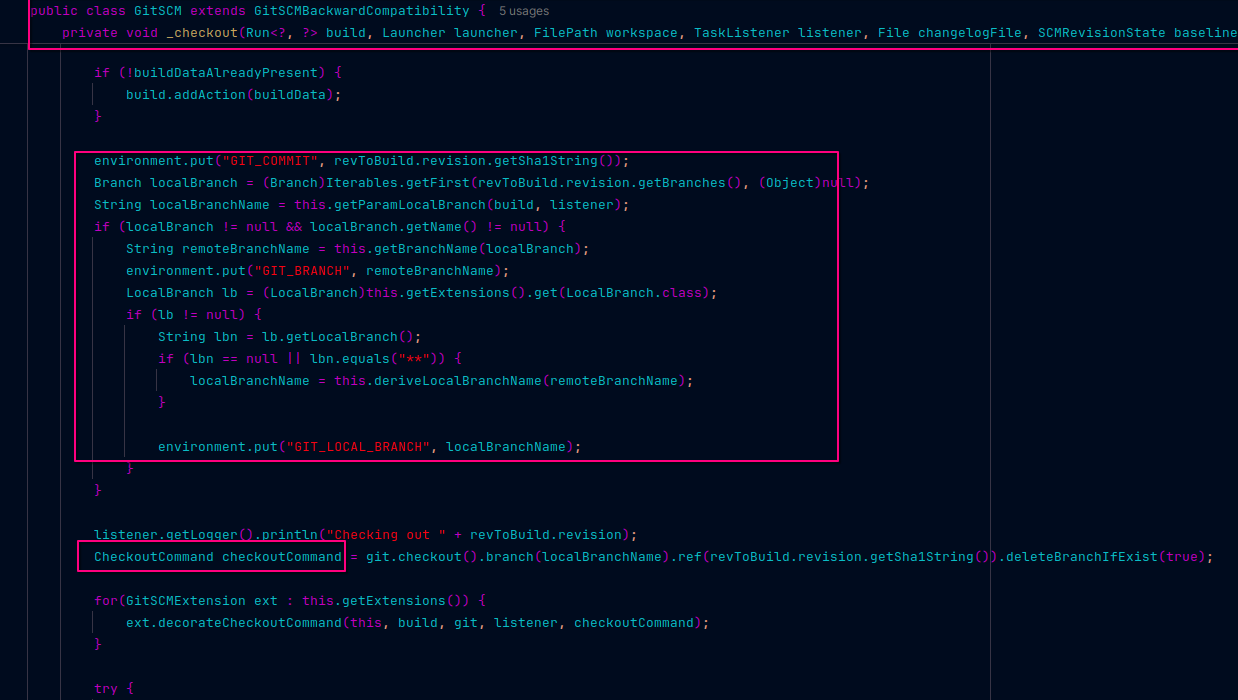 pl4tyz/cve-2025-53652-jenkins-git-parameter-analysis
CVE-2025-53652: Jenkins Git Parameter Analysis
 gonsarrabia/minimus-junior-backend-exercise
Junior Backend Candidate Exercise: Packaging the dasel CLI (v3.3.1) with Melange, fixing CVE-2026-33320, and building a minimal container image using…
 gina-alaska/bash-cve-2014-7169-cookbook
Chef cookbook to detect and patch the Shellshock (CVE-2014-7169) bash vulnerability across servers using automated configuration management.
 dannyendortest/invokeai
Synthetic demo target for CVE-2024-10821 vulnerability detection and automated fix via compensating control. Demonstrates one-click PR-based…
 isecuritytw/seal-security-nuget-demo-net7
.NET 7 fork of seal-security-nuget-demo: same CVE-2024-21907 exploit story, retargeted for customers locked to .NET SDK 7.
 claranet/ansible-role-log4shell
Ansible role to detect Log4Shell (CVE-2021-44228) by scanning filesystem and open files for vulnerable JAR/WAR files, reporting version and…
 contrast-security-oss/cve-2021-44228
Professional Service scripts to aid in the identification of affected Java applications in TeamServer
 shoucheng3/cov-int
XWiki Commons CVE-2023-31126 v14.10.3 for Coverity analysis
 shoucheng3/apache__incubator-dubbo_cve-2021-30181_2-6-8
High-performance Java RPC and microservices framework with service discovery, traffic management, observability, and built-in security for building…
 shoucheng3/apache__dolphinscheduler_cve-2023-51770_3_2_1_fixed
Exploit for CVE-2023-51770 targeting Apache DolphinScheduler versions 3.2.1 and earlier, enabling remote code execution via crafted workflow…
 dannyendortest/node-vulnerable
Synthetic demo target for EXPOSURE — CVE-2018-21268 (traceroute) + CVE-2018-3757 (pdf-image)
 zanex360/cdt-samba-deploy
CDT Ansible playbook for deploying CVE-2017-7494 aka "SambaCry" to an Ubuntu box
 aaaguirrep/offensive-docker-vps
Create a VPS on Google Cloud Platform or Digital Ocean easily with Offensive Docker included to launch assessment to the targets.
 xiaoqimikko/fastjson-check
Zero-dependency, offline CLI scanner that finds fastjson inside JARs and Spring Boot fat-JARs, flags CVE-2026-16723 exposure, and detects shaded…
 axisops/cve-2021-44228
log4j mitigation work








