
 #1
Security integration in CI/CD pipelines, shift-left, and DevOps security automation tools.
Kitploit recommended
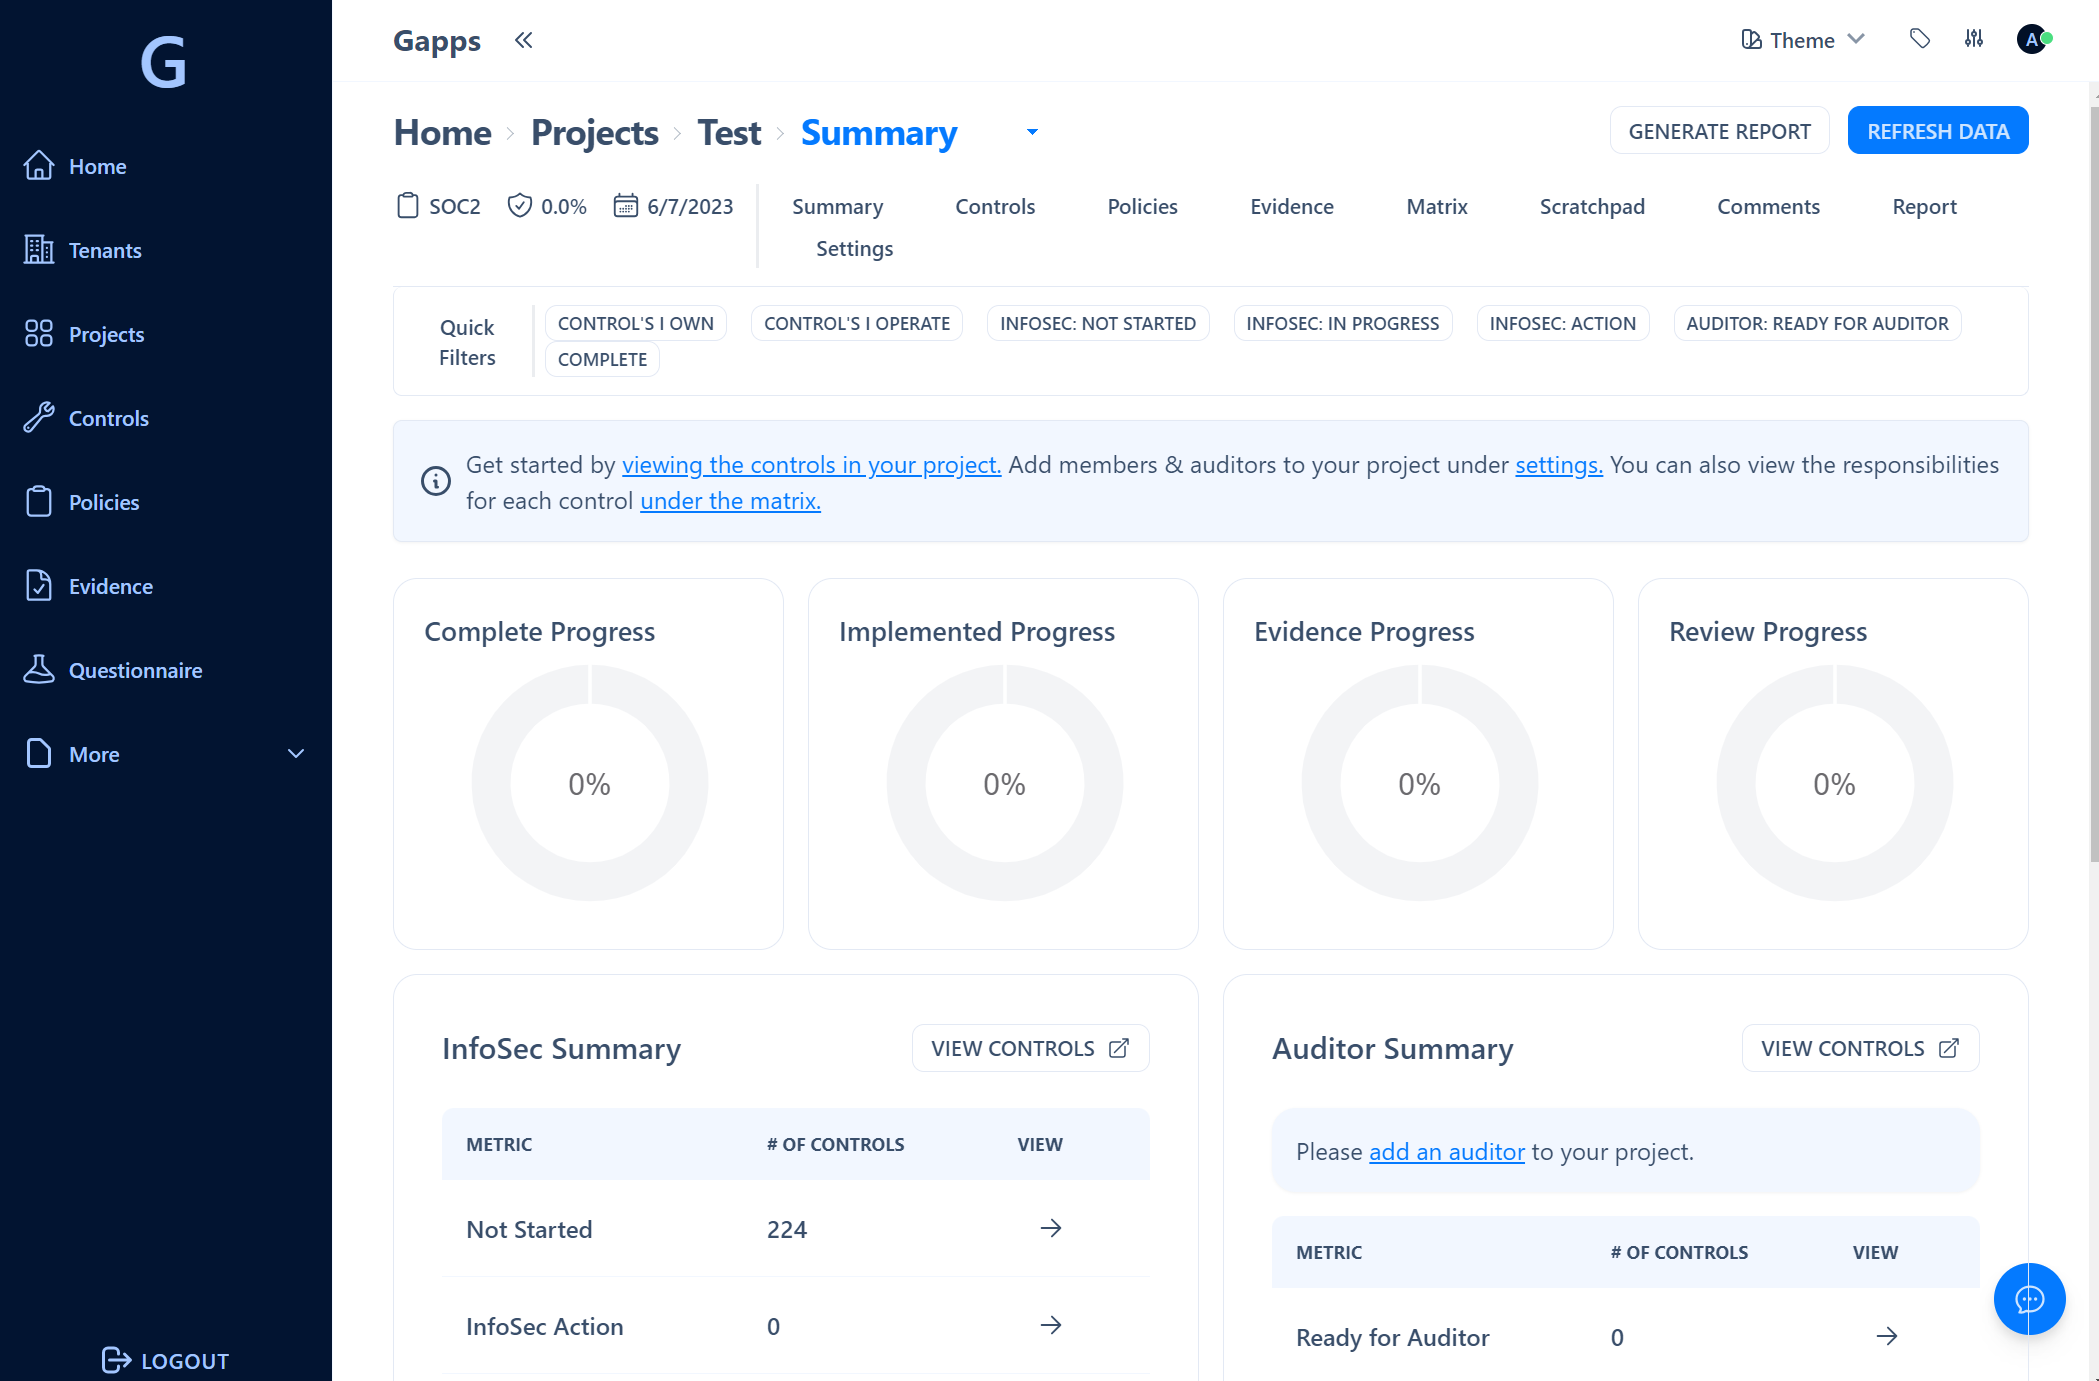
 bmarsh9/gapps
Security compliance platform - SOC2, CMMC, ASVS, ISO27001, HIPAA, NIST CSF, NIST 800-53, CSC CIS 18, PCI DSS, SSF tracking
 securityrat/securityrat
OWASP SecurityRAT (version 1.x) - Tool for handling security requirements in development
 ory/talos
Scalable API key server for issuing, verifying, and revoking credentials with token derivation for fine-grained capability tokens. Supports…
 apiiro/combobulator
Modular framework to detect and prevent dependency confusion attacks by analyzing package manifests across multiple sources and package management…
 speytech/c-sentinel
Semantic Observability for UNIX Systems - A lightweight C-based system prober with AI-powered analysis
 tejasprasad2008-afk/tracetree
Runtime behavioral analysis tool that sandboxes suspicious packages in Docker, traces syscalls with strace, maps process cascades into directed…
 owasp/application-security-curriculum
Structured curriculum for learning application security, covering secure coding, threat modeling, and DevSecOps practices. Designed for self-paced…
 pgedge/pgedge-anonymizer
An anonymizer tool for replacing PII and similar data in dev/test databases copied from production
 owasp/open-sammy
Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.
 kamalsrini/sentinel-cve
CLI tool that explains CVEs in plain English and scans repos for impact. Powered by Claude.
 corelight/corelight-ansible-roles
Corelight-Ansible-Roles are a collection of Ansible Roles and playbooks that install, configure, run and manage a variety of Corelight, Suricata and…
 rgielen/struts1filter
A request parameter filter solution for Struts 1 CVE-2014-0114 based on the work of Alvaro Munoz and the HP Fortify team
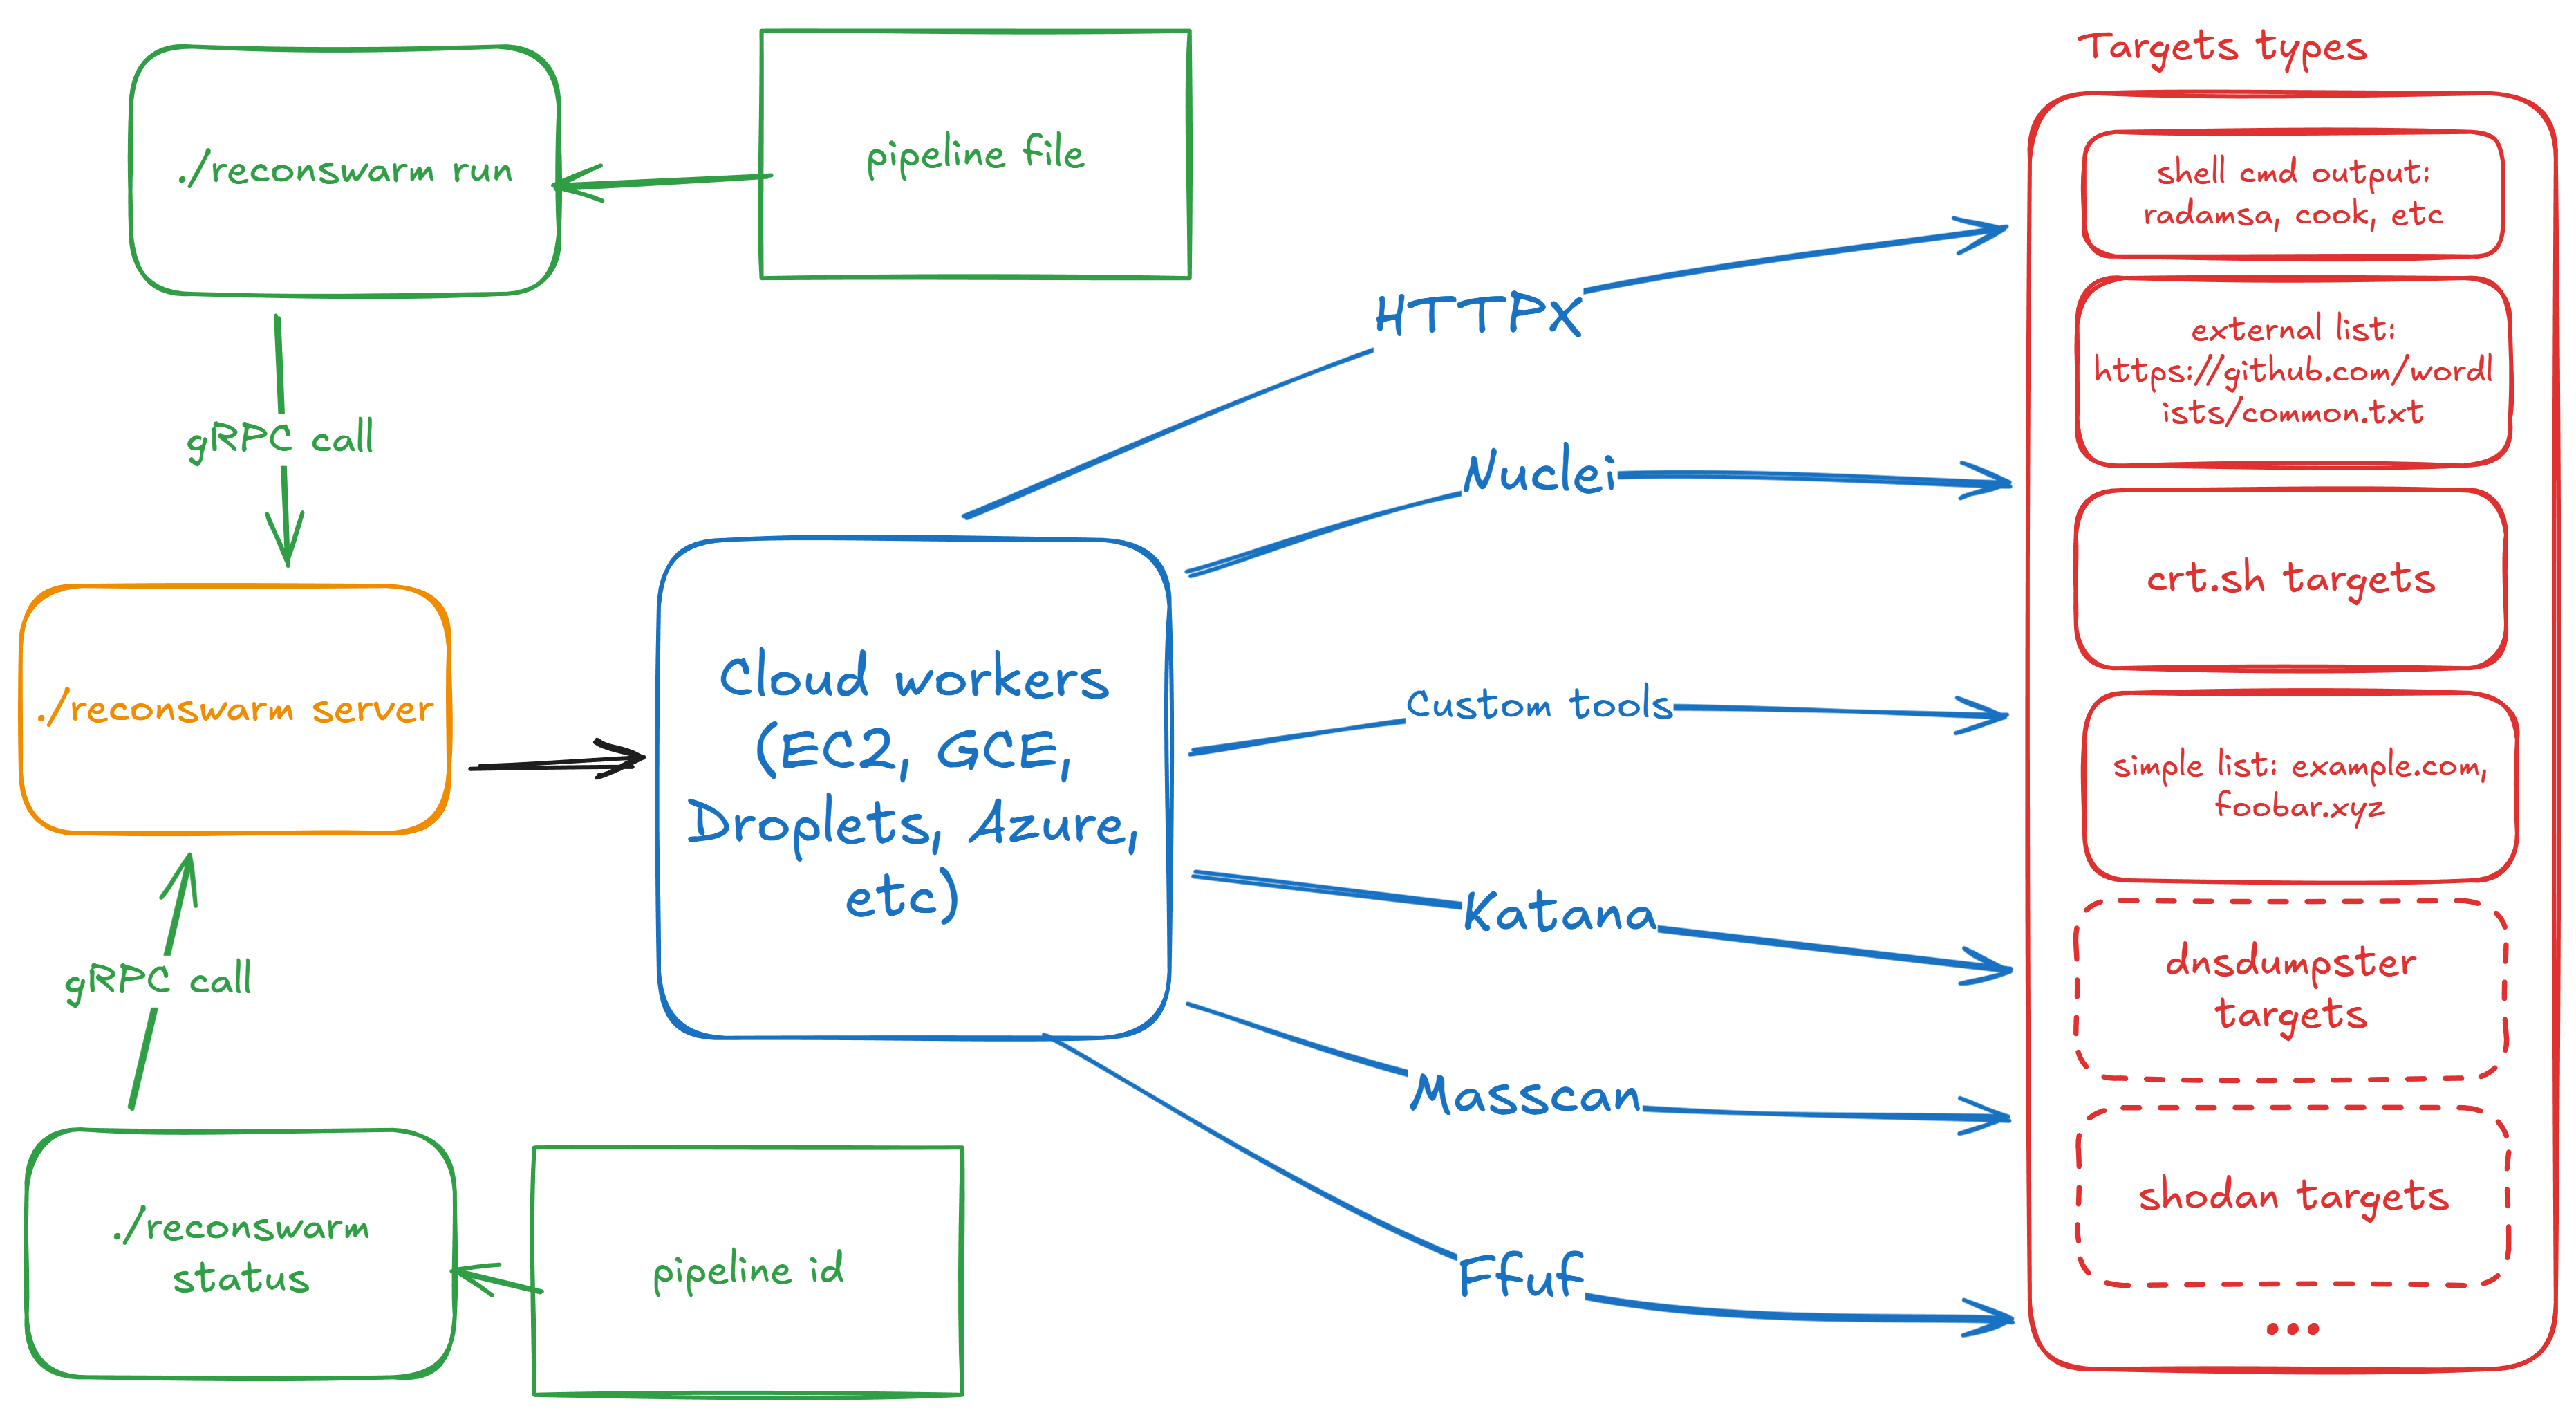 renatus-cartesius/reconswarm
Extend your recon with cloud power
 aquasecurity/trivy-plugin-attest
Publish SBOM attestation
 irgoncalves/f5-waf-enforce-sig-cve-2021-44228
This enforces signatures for CVE-2021-44228 across all policies on a BIG-IP ASM device
 chef-cft/salt-vulnerabilities
Checks for CVE-2020-11651 and CVE-2020-11652
 chef-boneyard/bash-shellshock
DEPRECATED: Chef cookbook to audit & remediate "Shellshock" (BASH-CVE-2014-7169)
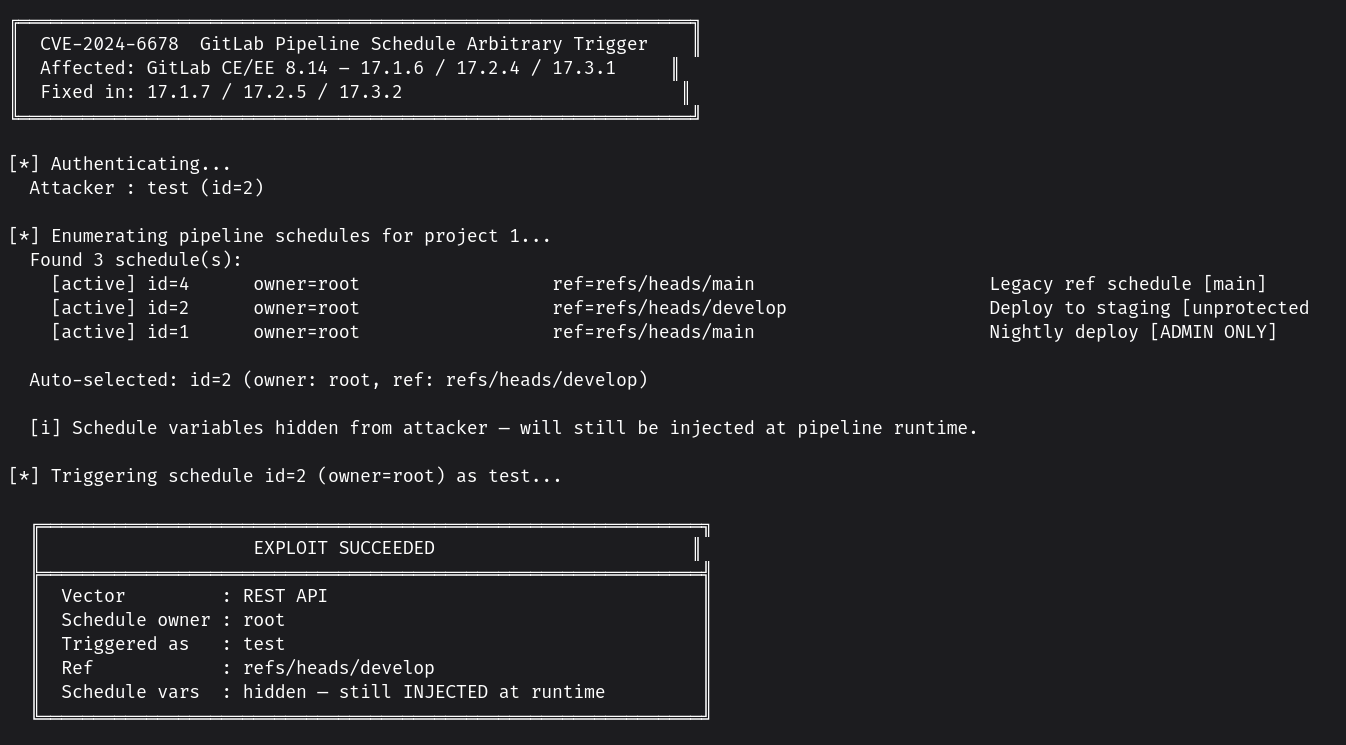 fallenskill1/cve-2024-6678
PoC for CVE-2024-6678








