
 #1

 pompelmi/pompelmi
ClamAV antivirus scanning for Node.js — scan file uploads with a single function call. Zero dependencies. Typed Symbol verdicts. Local or…
 hawkeyesec/scanner-cli
A project security/vulnerability/risk scanning tool
 check-spelling/check-spelling
Spelling checker action to check spelling in repositories / pull requests / commits
 jagracey/regex-dos
:cop: :punch: RegEx Denial of Service (ReDos) Scanner
 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
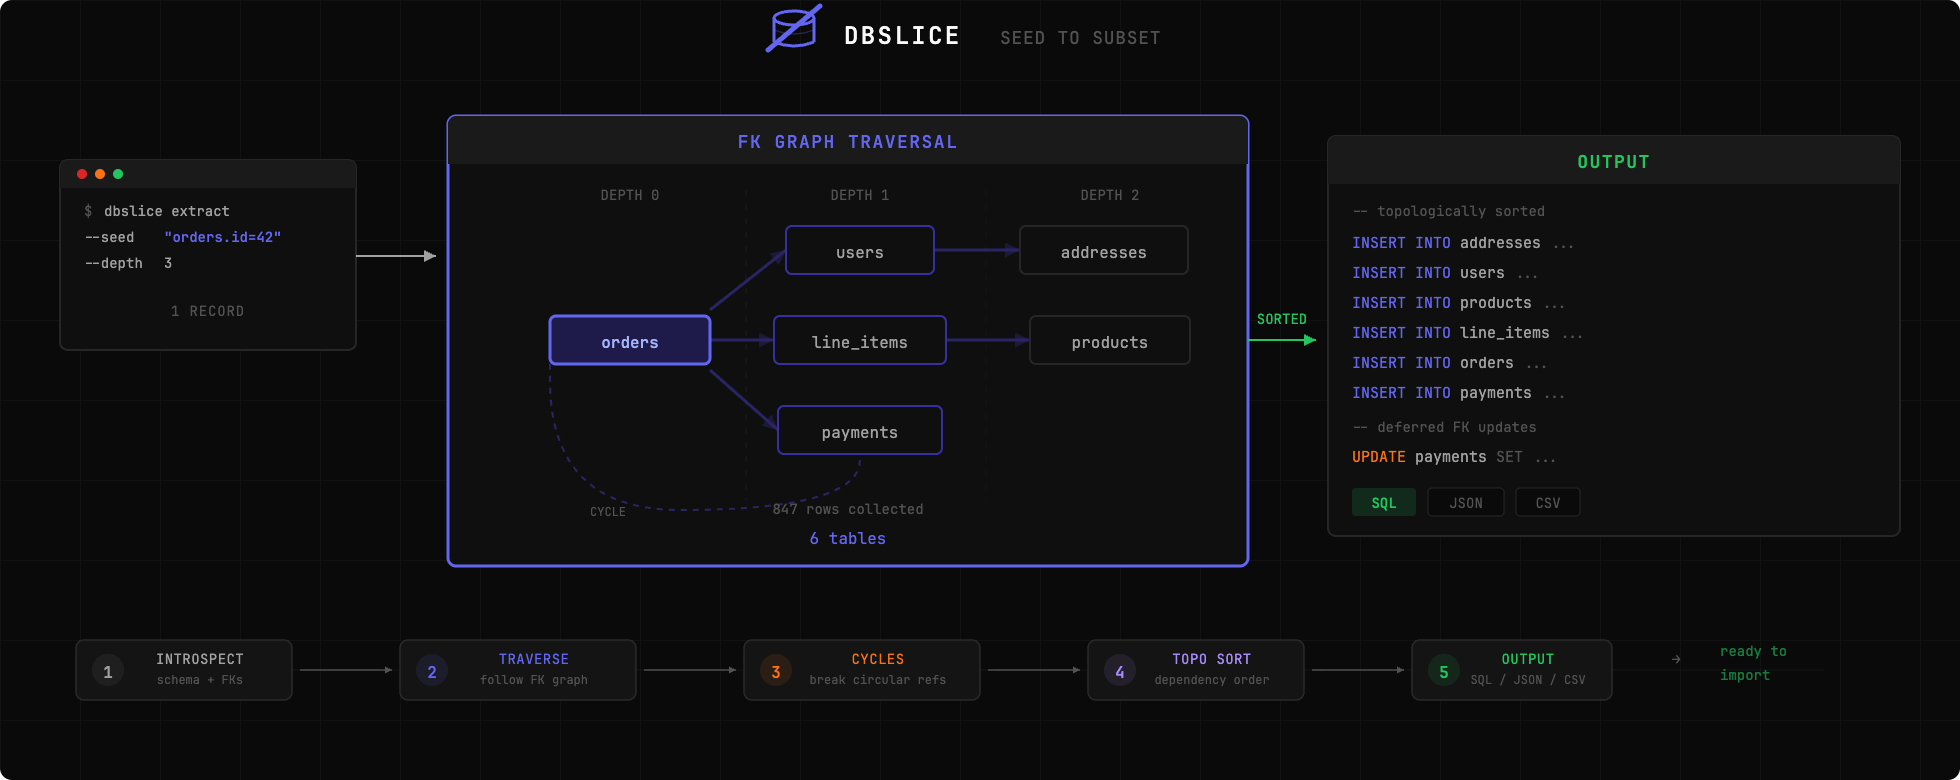 nabroleonx/dbslice
Extract a slice of your production database to reproduce bugs locally. Point dbslice at a record, it follows foreign keys and gives you a complete,…
 ariesq/gh-safe-repo
Python CLI that creates GitHub repos with safe defaults — branch protection, Dependabot, secret scanning, and pre-flight security scanning — applied…
 afine-com/glassworm-hunter
Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…
 backbay-labs/hush
Portable security rules for the action boundary of AI agents
 projectdiscovery/naabu-action
A fast port scanner written in go with a focus on reliability and simplicity.
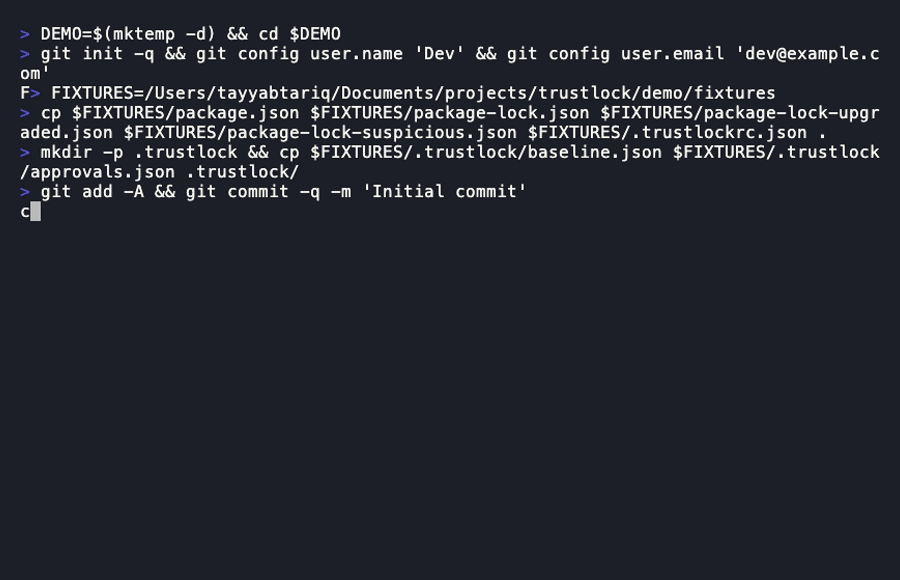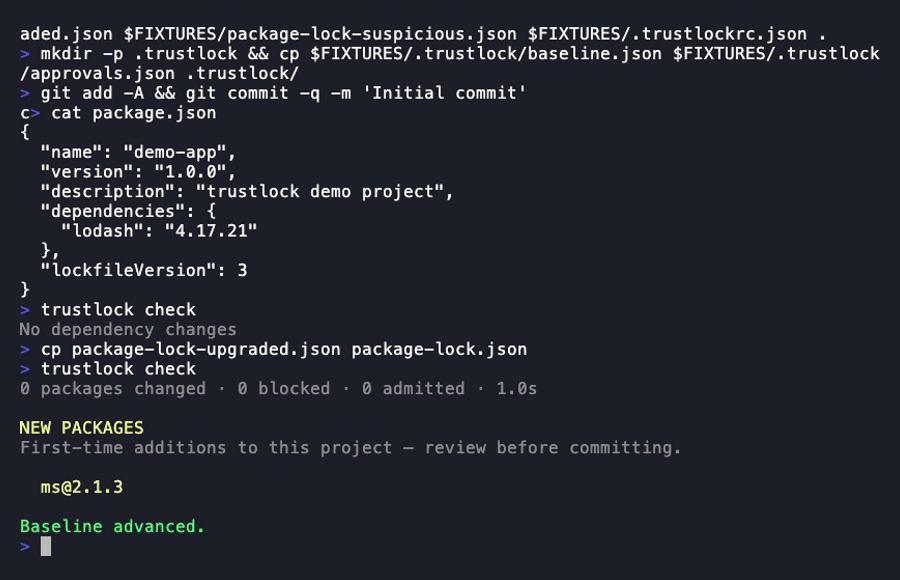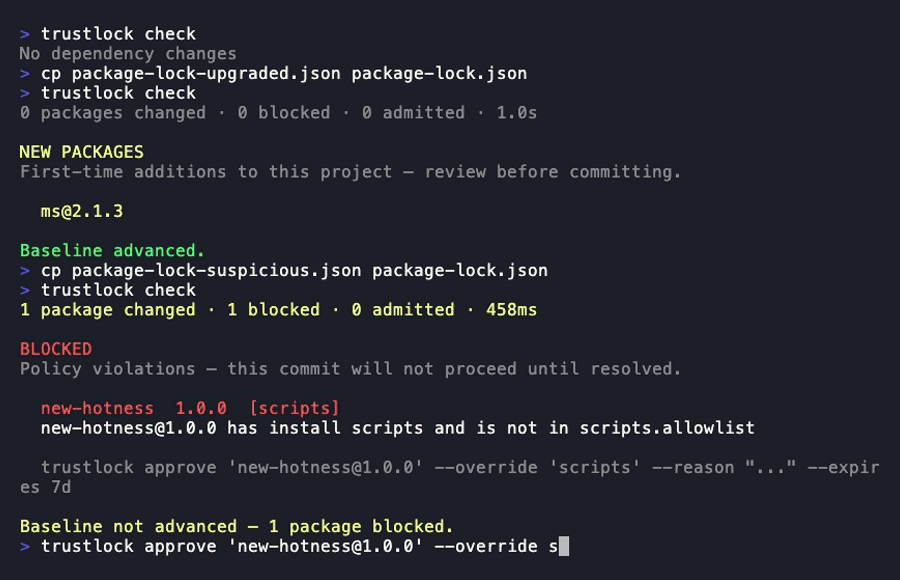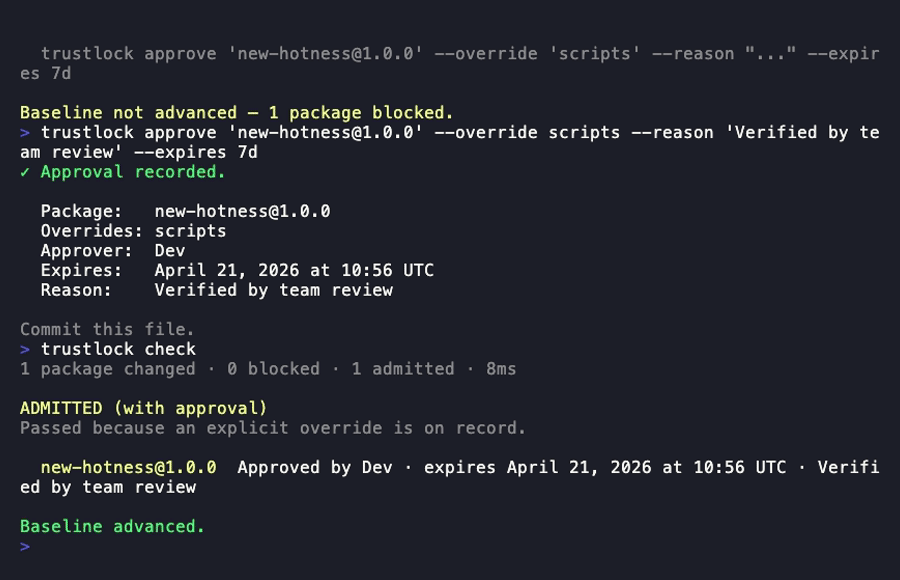 tayyabt/trustlock
A Git-native dependency admission controller. Evaluates trust signals on every dependency change and blocks commits or builds when packages fail your…
 thirukguru/aws-perimeter
A terminal-based AWS Security Scanner with 102+ security checks across VPC, IAM, S3, CloudTrail, containers (ECS/EKS), and AI attack detection.…
 kemal-arslan/reposherlock
Analyze any GitHub repo (URL or local path) → architecture map, verified run commands, risks, and actionable issues - in minutes.
 p3dr16k/log4j-1.2.15-mod
log4j version 1 with a patch for CVE-2021-44228 vulnerability
 meersjo/ansible-mysql-cve-2016-6662
Simple ansible playbook to patch mysql servers against CVE-2016-6662
 purpleteam-labs/purpleteam-orchestrator
Orchestration component of purpleteam
 george0papasotiriou/cve-2026-22018-jenkins-pipeline-shared-library-code-execution-via-grab-
PoC for CVE-2026-22018, a critical Jenkins Pipeline Shared Library RCE via Groovy @Grab, demonstrating supply-chain code injection and mitigation…









