
 #1
Security integration in CI/CD pipelines, shift-left, and DevOps security automation tools.
Kitploit recommended

 3pplus/loguccino
Scan and patch tool for CVE-2021-44228 and related log4j concerns.

 warhorse/warhorse
Infrastructure Automation
 awslabs/threat-modeling-mcp-server
MCP server for structured STRIDE-based threat modeling with automatic code validation, business context analysis, and comprehensive report generation…
 sshwarts/skillscript
Skillscript — a small declarative language for authoring agent workflows. Runtime, compiler, and CLI.
 infobyte/faraday_agent_dispatcher
Faraday Agent Dispatcher launches any security tools and send results to Faradaysec Platform.
 rohansx/wardn
credential isolation for AI agents. Agents never see real API keys - structural guarantee, not policy.
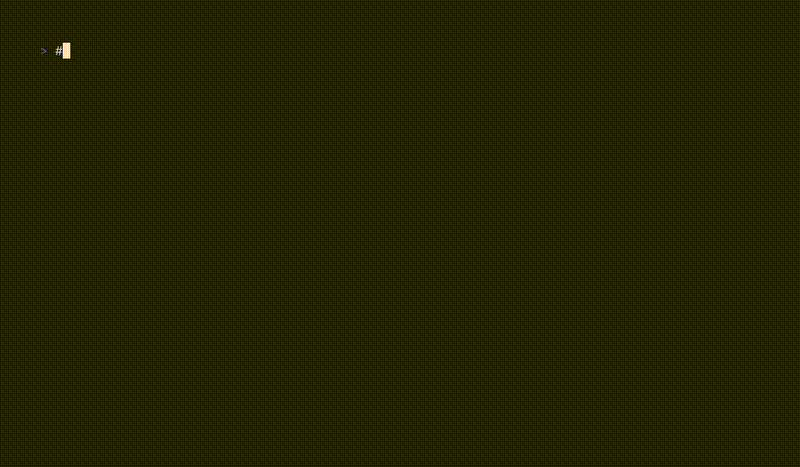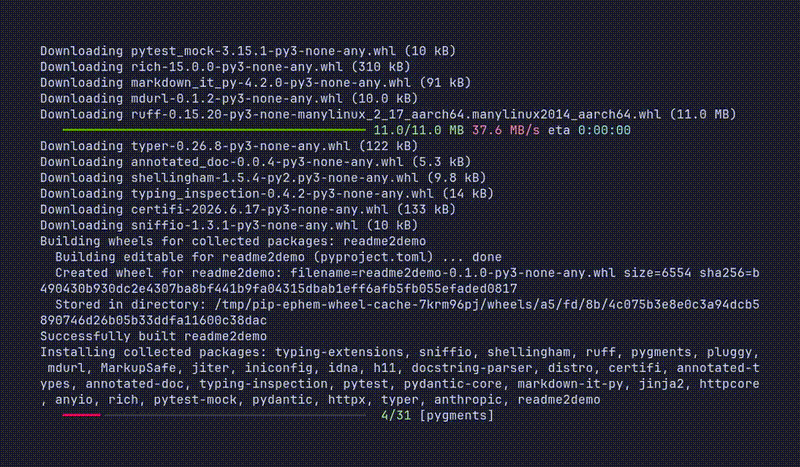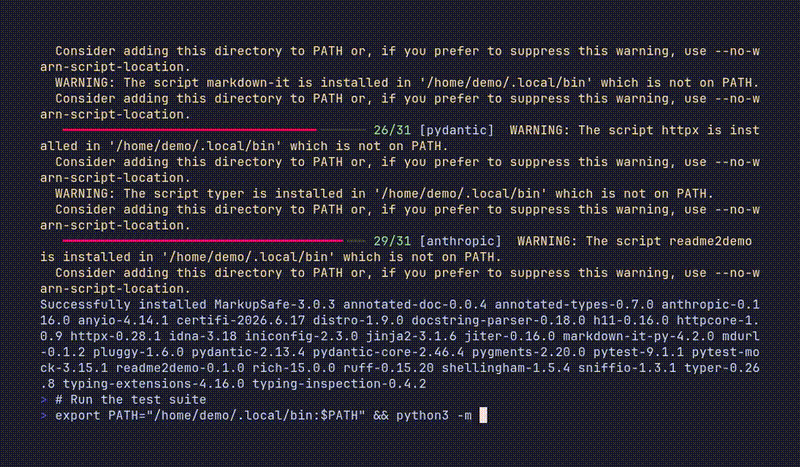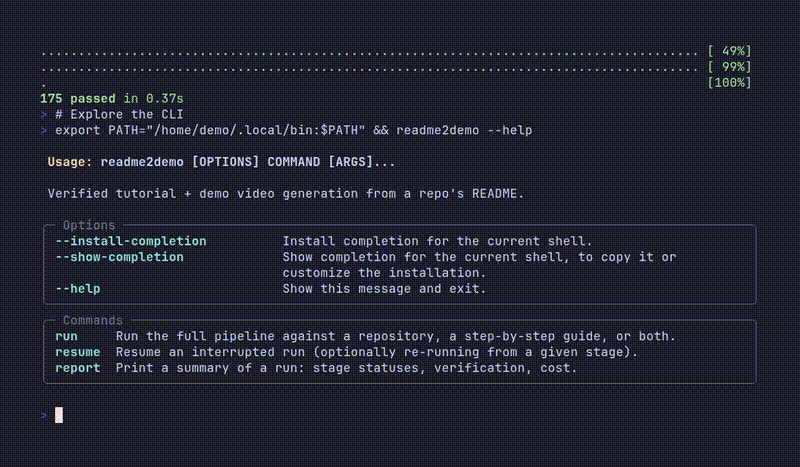 alphacrack/readme2demo
Verified tutorials and demo videos from your README. An AI agent runs it in a hardened Docker sandbox and replays it in a fresh container before…
 shivang0/guardmodel
GitHub Action that scans ML model files for malicious code and security vulnerabilities
 purpleteam-labs/purpleteam
CLI component of purpleteam
 purpleteam-labs/purpleteam-s2-containers
Stage two containers
 nedlir/dasel-hardened-container
Hardened dasel v3.3.1 package and image built via Melange and apko. Patching CVE-2026-33320.
 leitwacht/leitwacht
Leitwacht control plane — runtime security for GitLab Runner CI/CD: policy authoring, multi-tenancy, audit, GitLab integration
 moderneinc/rewrite-cve-2026-22732
OpenRewrite recipe that detects and fixes Spring Security header suppression (CVE-2026-22732) by identifying Content-Length header misuse and…
 mukul975/cve-mcp-server
Production-grade MCP server giving Claude 27 security intelligence tools across 21 APIs — CVE lookup, EPSS scoring, CISA KEV, MITRE ATT&CK, Shodan,…
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 michelin/chopchop
YAML-driven CLI scanner that detects exposed services, files, and folders on web endpoints. Designed for developers to integrate security checks into…
 robocoder/rips-scanner
RIPS - A static source code analyser for vulnerabilities in PHP scripts








