
 #1
Security integration in CI/CD pipelines, shift-left, and DevOps security automation tools.
Kitploit recommended

 dev-sec/chef-mysql-hardening
This chef cookbook provides security configuration for mysql.
 adarsh14734/aegis-releases
Sandbox and MCP proxy that blocks AI coding agents from reading SSH keys, AWS credentials, and .env files, with deny-by-default policy and…
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST: scan a repository and upload SARIF results to GitHub code scanning. Free for eligible open-source projects.
 wi3memake/react2shell-scanner
Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…
 mebibite/log4jhound
Created after the disclosure of CVE-2021-44228. Bash script that detects Log4j occurrences in your projects and systems, allowing you to get insight…
 digitalocean/nginxconfig.io
⚙️ NGINX config generator on steroids 💉
 docker/docker-bench-security
The Docker Bench for Security is a script that checks for dozens of common best-practices around deploying Docker containers in production.
 praetorian-inc/gokart
A static analysis tool for securing Go code
 netflix/repokid
AWS Least Privilege for Distributed, High-Velocity Deployment
 francescostabile/numasec
AI security agent that runs in your terminal, orchestrating local tools, runbooks, and agents for authorized AppSec, pentest, OSINT, and CTF…
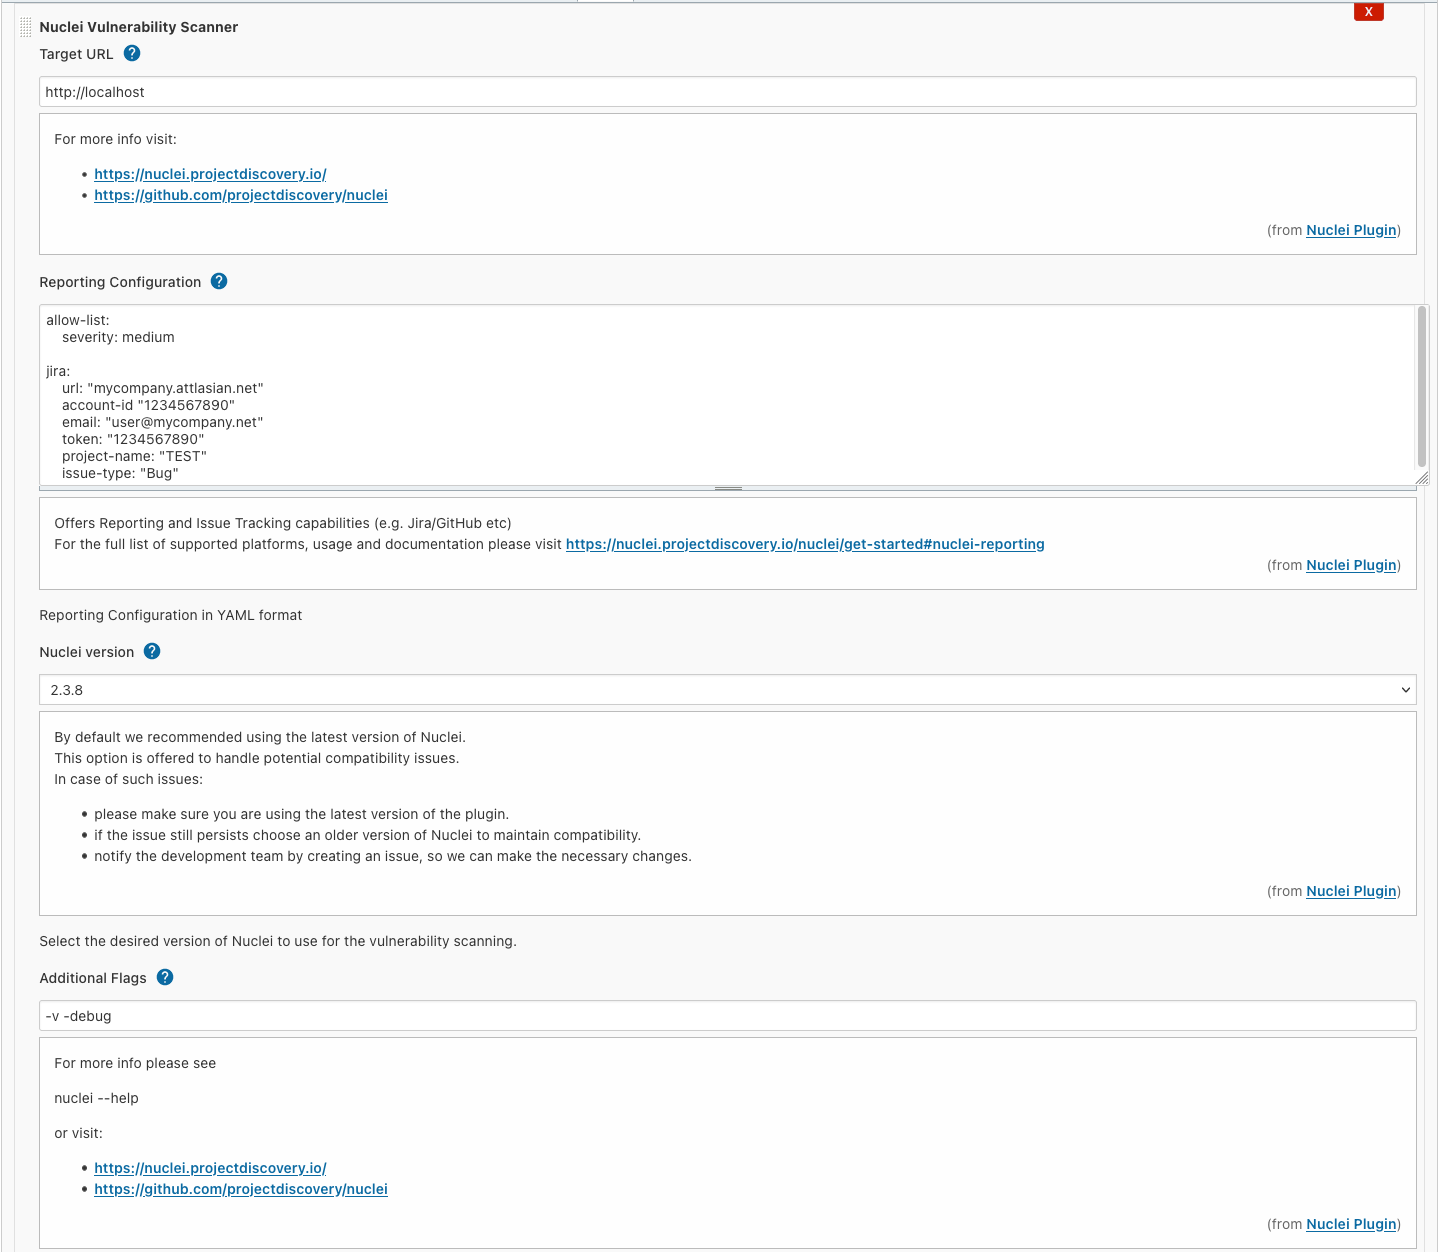 jenkinsci/nuclei-plugin
Nuclei is a fast tool for configurable targeted vulnerability scanning based on templates offering massive extensibility and ease of use.
 dnszlsk/muad-dib
Real-time npm/PyPI supply-chain threat detection. Behavioral chain analysis, AST scanning, IOC feeds, and compound scoring engine.
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …

 oseguera12/cowrie-honeypot-digitalocean
Medium-interaction SSH/Telnet honeypot built with Cowrie, Loki, Promtail, and Grafana - provisioned on DigitalOcean via Terraform with a GitLab CI…
 shoucheng3/testng-team__testng_cve-2022-4065_7-5
Java testing framework for unit, integration, and end-to-end tests with annotations, data-driven testing, and parallel execution support.
 xiaoqimikko/thymeleaf-check
Offline checker for Thymeleaf CVE-2026-40477 / CVE-2026-41901 — tells you which of the two CVSS 9.0 SSTI flaws you are exposed to, and whether your…
 mrarianet/cpanel-fix
One security-remediation.sh for CVE-2026-41940 (cPanel), CVE-2026-31431 (kernel "Copy Fail"), CSF, optional domain/proxy cleanup, and optional…
 liamromanis101/cve-2026-31431-copy-fail---vulnerability-detection-script
Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…








