
 #1
Security integration in CI/CD pipelines, shift-left, and DevOps security automation tools.
Kitploit recommended

 dev-sec/ansible-collection-hardening
This Ansible collection provides battle tested hardening for Linux, SSH, nginx, MySQL
 projectdiscovery/pdtm
ProjectDiscovery's Open Source Tool Manager
 clawkwork/clawk
Give coding agents a disposable Linux VM, not your laptop
 synacktiv/shh
Systemd Hardening Helper - Mirror of https://github.com/desbma/shh
 owasp/user-security-stories
Repo to hold mapping of user-security-stories
 stacscan/stacs
Static Token And Credential Scanner
 wantasticapp/wantasticcore
AIO Cloud Managment Server
 adamsjack711-ux/pkgxray
Pre-install security for AI agents, npm packages, and MCP servers. Zero-dep local static analysis; normal scans never execute package code.
 aquasecurity/secfixes-tracker
Forked from https://gitlab.alpinelinux.org/kaniini/secfixes-tracker

 leitwacht/leitwacht-agent
eBPF + nftables + DNS proxy egress enforcement for GitLab Runner CI/CD job containers — community edition data plane https://leitwacht.eu/
 squid-protocol1/gitgalaxy
AST-free heuristic knowledge graph engine for deep repository intelligence and zero-trust security scanning. Integrates as a GitLab CI/CD component,…
 masriyan/fufufafa
Framework for Unified Flaw & Fault Auditing The ultimate AWS Cloud Security Audit Framework that makes security auditing so easy, you can do it even…
 abhishek2512mishra/claude-code-security-audit
Security scanner auditing Claude Code environments for CVE-2026-21852 pre-trust execution, hook hijacking, and eBPF lockdown.
 devstuff/harden-docker-seccomp
Docker mitigation for CVE-2026-31431 ('Copy Fail'). Includes Kubernetes templates as well.
 42crunch/api-security-audit-action
Automates static API security auditing of OpenAPI contracts in CI/CD, running 300+ checks for authentication, authorization, and data constraints,…
 archerysec/archerysec
ASOC, ASPM, DevSecOps, Vulnerability Management Using ArcherySec.
 poshbotio/poshbot
Powershell-based bot framework
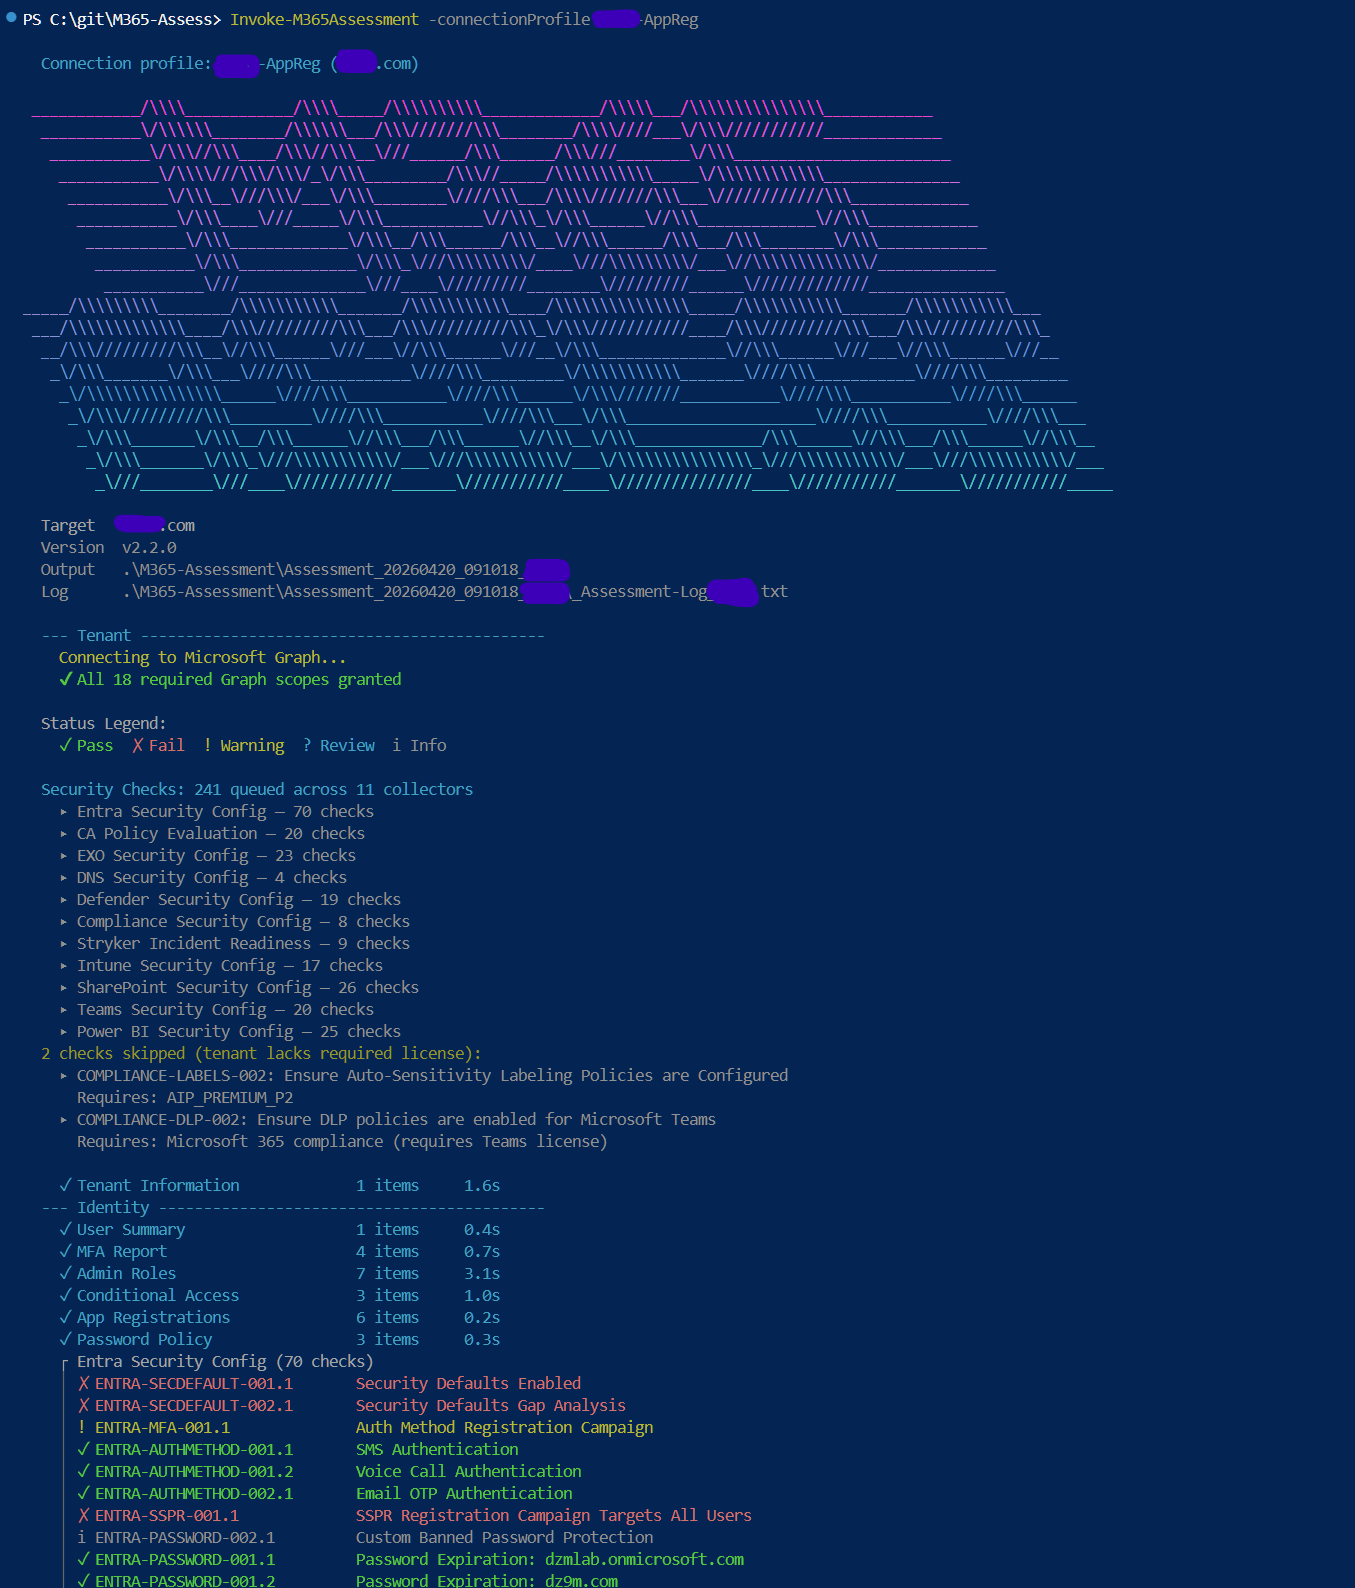 galvnyz/m365-assess
290+ Automated checks across 14 compliance frameworks, interactive HTML report, no data leaves your machine.








