#1
Tools for blue team, defensive security, and threat protection.
Kitploit recommended
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
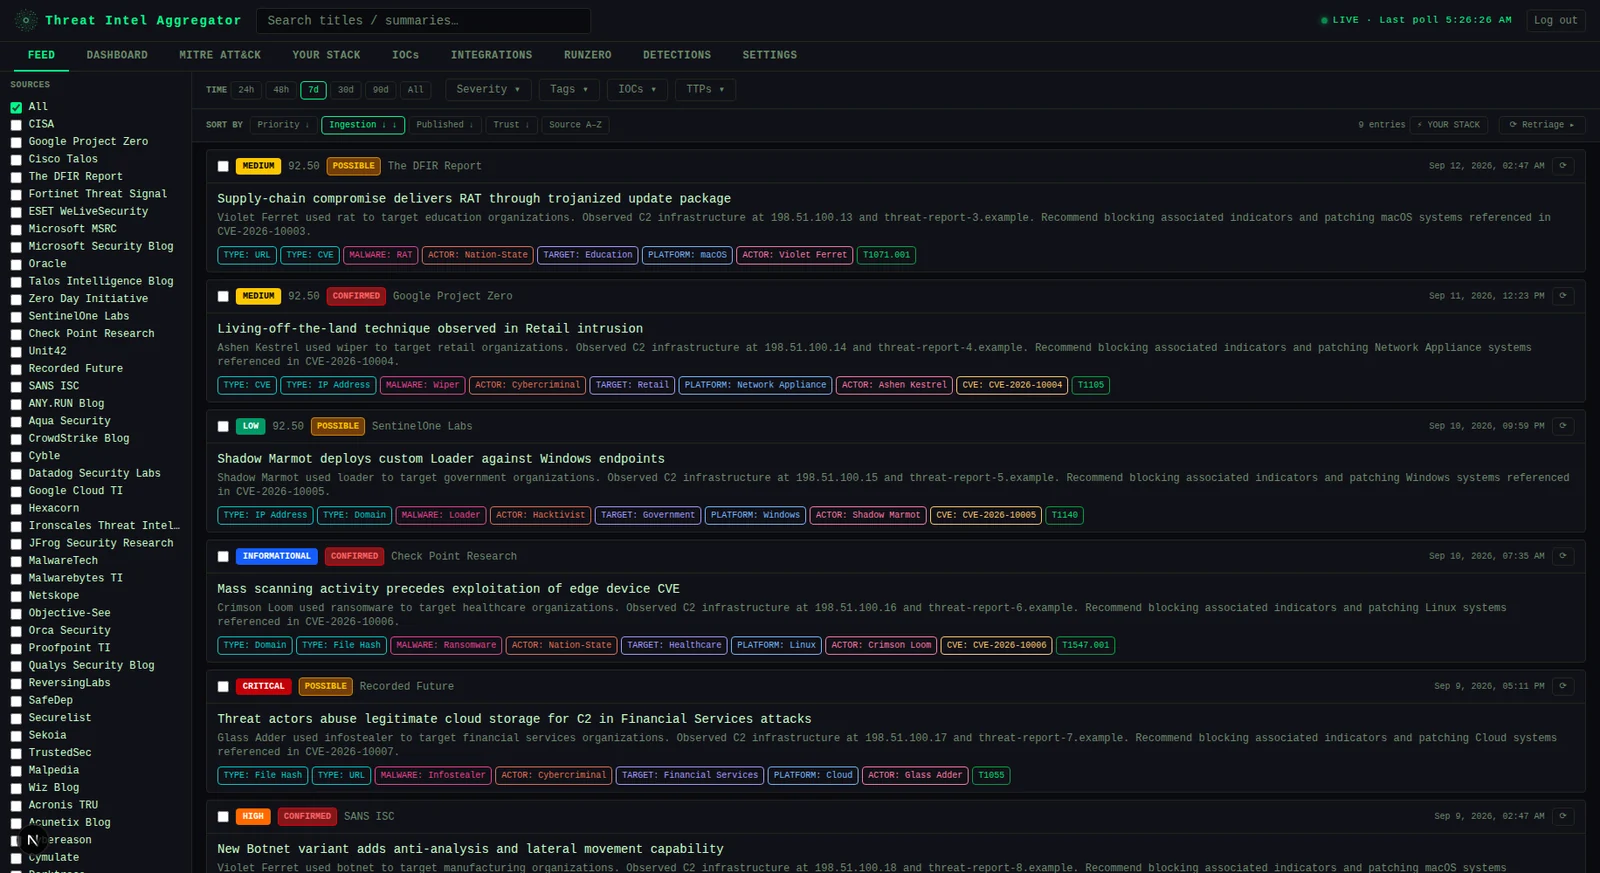 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
 binzhwang/actguard
Pre-execution action-auditing defense that detects and masks indirect prompt injection in tool-using LLM agents using embedding retrieval and…
 gmh5225/dse-patcher
Windows tool that disables Driver Signature Enforcement by patching kernel variables, allowing unsigned drivers to load for testing and research.
 gmh5225/dsark64
BYOVD proof-of-concept abusing the WHQL-signed DsArk64.sys driver for ring-0 process termination and kernel read/write via encrypted IOCTLs and…
 philippeabraxas-jpg/responsible-alliance-protocol
Safety cannot be a prompt instruction. TBP provides an external execution-layer boundary for autonomous agents, enforcing hard F/I/W invariants via…
 pbxqdown/portclue
Explain why a Linux TCP port may or may not be reachable
 xiaoqimikko/netty-resolver-dns-check
Offline static checker that inspects packaged Java jars for vulnerable netty-resolver-dns versions and detects whether Spring WebClient actually uses…
 snyk/leaky-vessels-dynamic-detector
eBPF-based runtime detector for container breakout vulnerabilities in runc and Docker, monitoring syscalls and Docker daemon calls to detect…
 evdenis/lsm_bpf_check_argc0
LSM BPF module to block pwnkit (CVE-2021-4034) like exploits
 protectai/rebuff
Multi-layered prompt injection detector for AI applications using heuristics, LLM-based analysis, vectorDB attack signatures, and canary token leak…
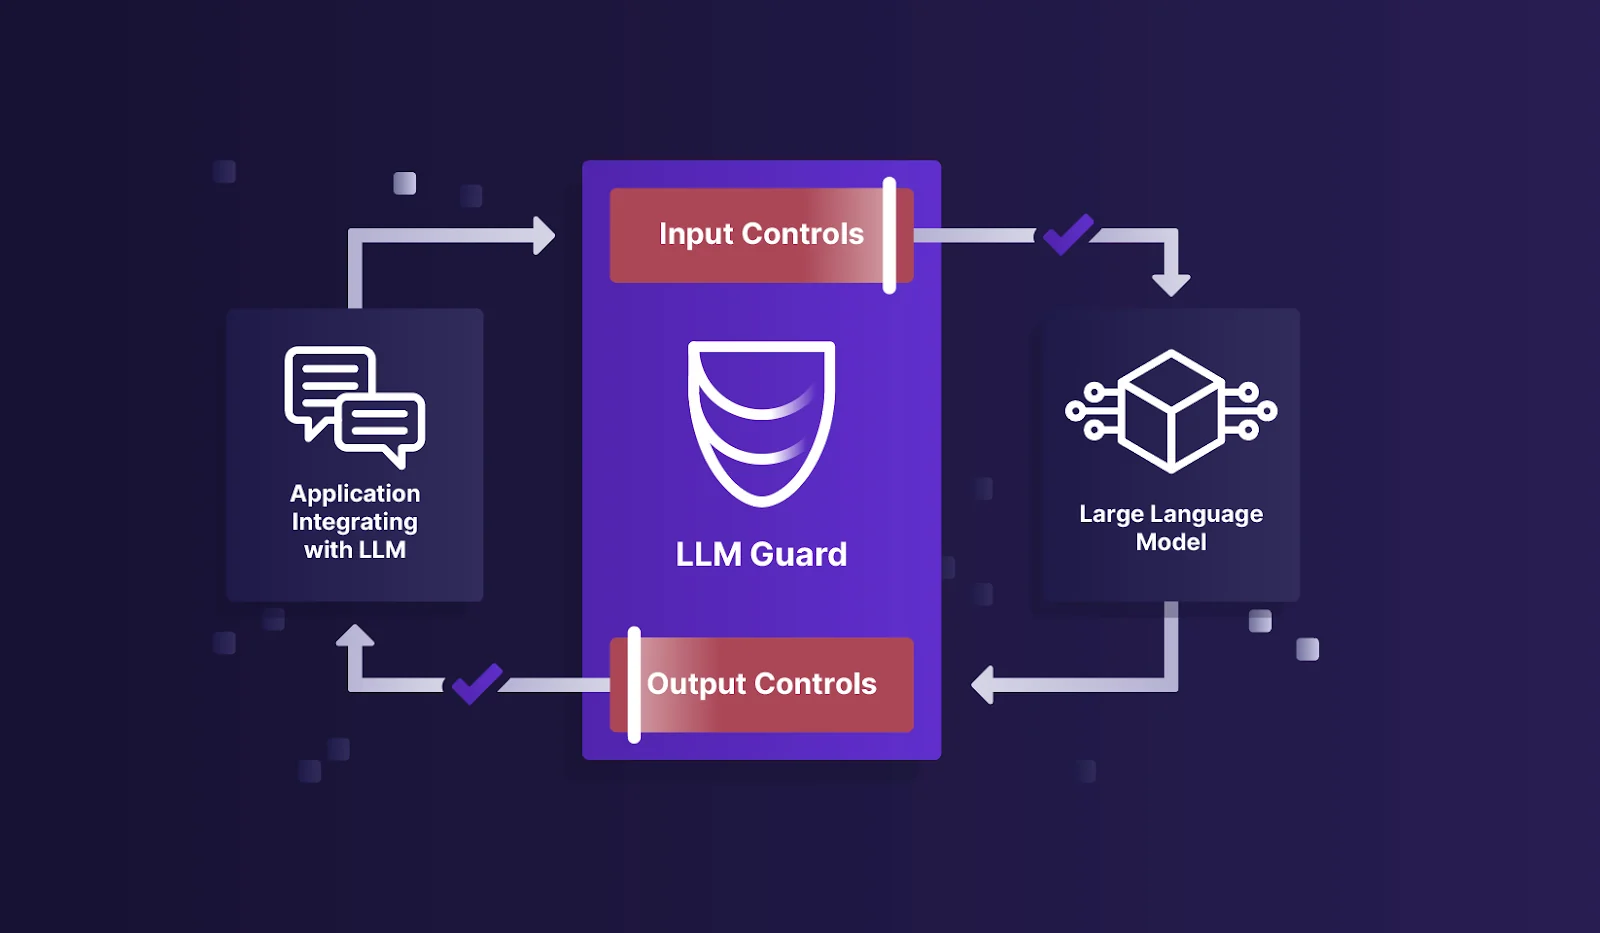 protectai/llm-guard
The Security Toolkit for LLM Interactions
 yanchenyu360/cve-2026-41940-security-patch
针对CVE-2026-41940漏洞的临时缓解措施
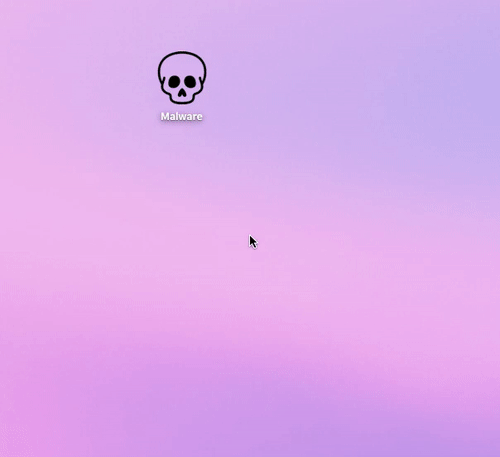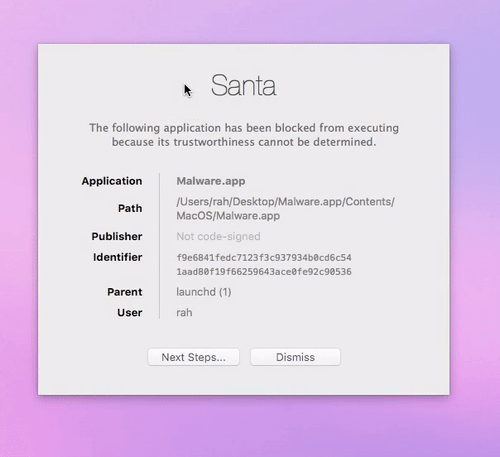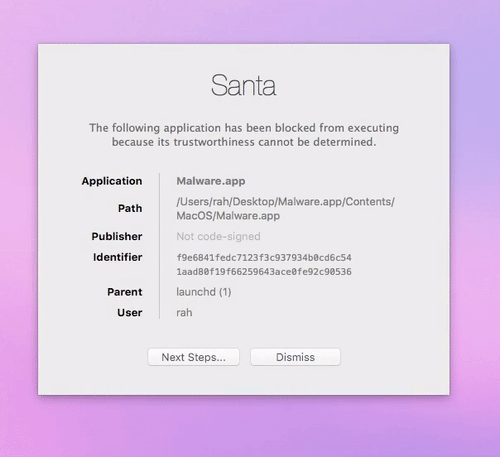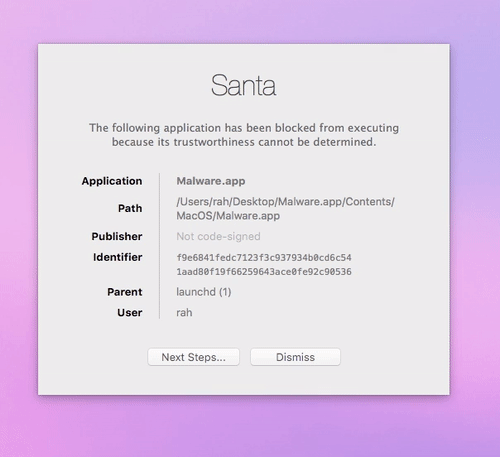 google/santa
A binary authorization and monitoring system for macOS
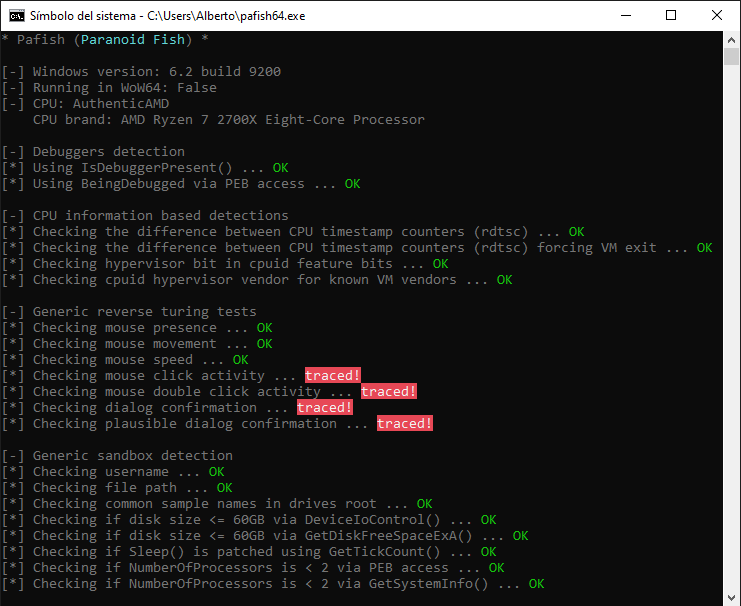 a0rtega/pafish
Pafish is a testing tool that uses different techniques to detect virtual machines and malware analysis environments in the same way that malware…
 efforg/https-everywhere
A browser extension that encrypts your communications with many websites that offer HTTPS but still allow unencrypted connections.