#1
Tools for blue team, defensive security, and threat protection.
Kitploit recommended

 spiderlabs/owasp-modsecurity-crs
OWASP ModSecurity Core Rule Set (CRS) Project (Official Repository)
 mozilla/mozdef
DEPRECATED - MozDef: Mozilla Enterprise Defense Platform
 optiv/mangle
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
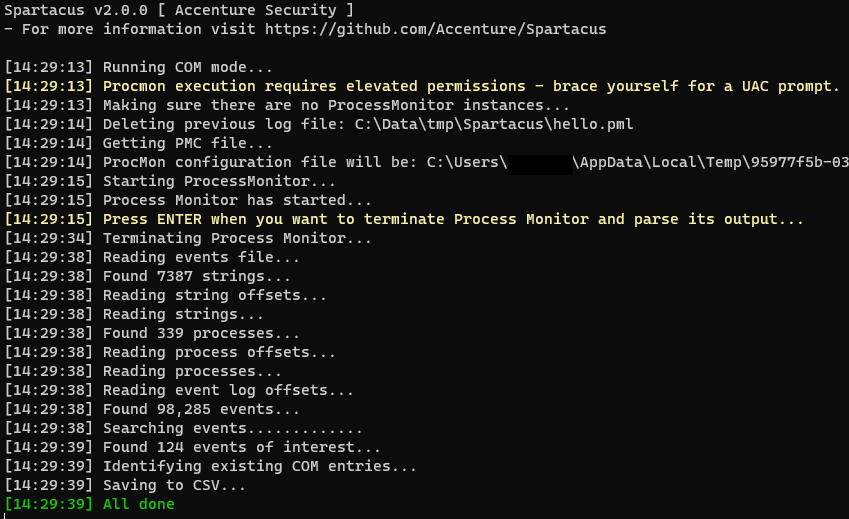 accenture/spartacus
Spartacus DLL/COM Hijacking Toolkit
 kiexitdispatcher/godefender
Anti Virtulization, Anti Debugging, AntiVM, Anti Virtual Machine, Anti Debug, Anti Sandboxie, Anti Sandbox, VM Detect package. Windows ONLY.
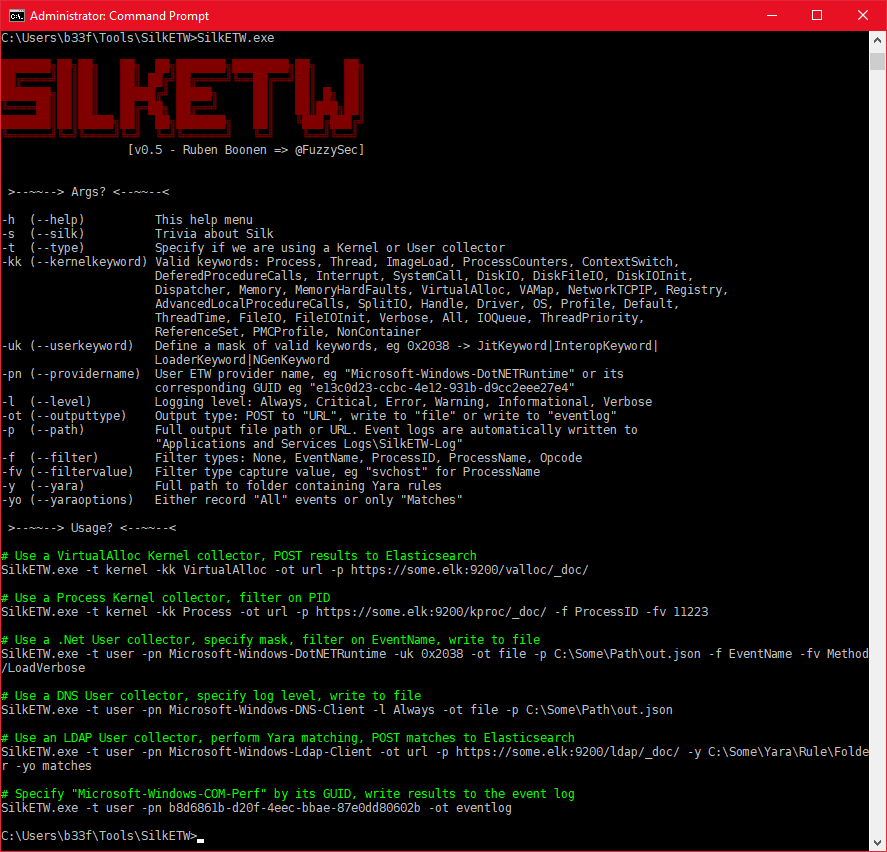 mandiant/silketw
C# wrapper for ETW that serializes kernel and user-mode event data to JSON for threat hunting, malware analysis, and incident response, with Yara…

 cloudflare/mitmengine
A MITM (monster-in-the-middle) detection tool. Used to build MALCOLM:
 idov31/functionstomping
Shellcode injection technique. Given as C++ header, standalone Rust program or library.
 chryzsh/darthsidious
Building an Active Directory domain and hacking it
 chronicle/gcti
Detection signature repository providing YARA rules and threat-hunting content for identifying malware and malicious activity across enterprise…
 hlldz/reflexxion
RefleXXion is a utility designed to aid in bypassing user-mode hooks utilised by AV/EPP/EDR etc. In order to bypass the user-mode hooks, it first…
 blackhillsinfosec/eventlogging
Automation scripts to deploy Windows Event Forwarding, Sysmon, and custom audit policies in an Active Directory environment.
 foospidy/honeypy
A low to medium interaction honeypot.
 azuread/azure-ad-incident-response-powershell-module
The Azure Active Directory Incident Response PowerShell module provides a number of tools, developed by the Azure Active Directory Product Group in…
 didi/kemon
An Open-Source Pre and Post Callback-Based Framework for macOS Kernel Monitoring.