
 #1
Debugging tools specifically for analyzing malware execution flow and identifying vulnerabilities.
Kitploit recommended
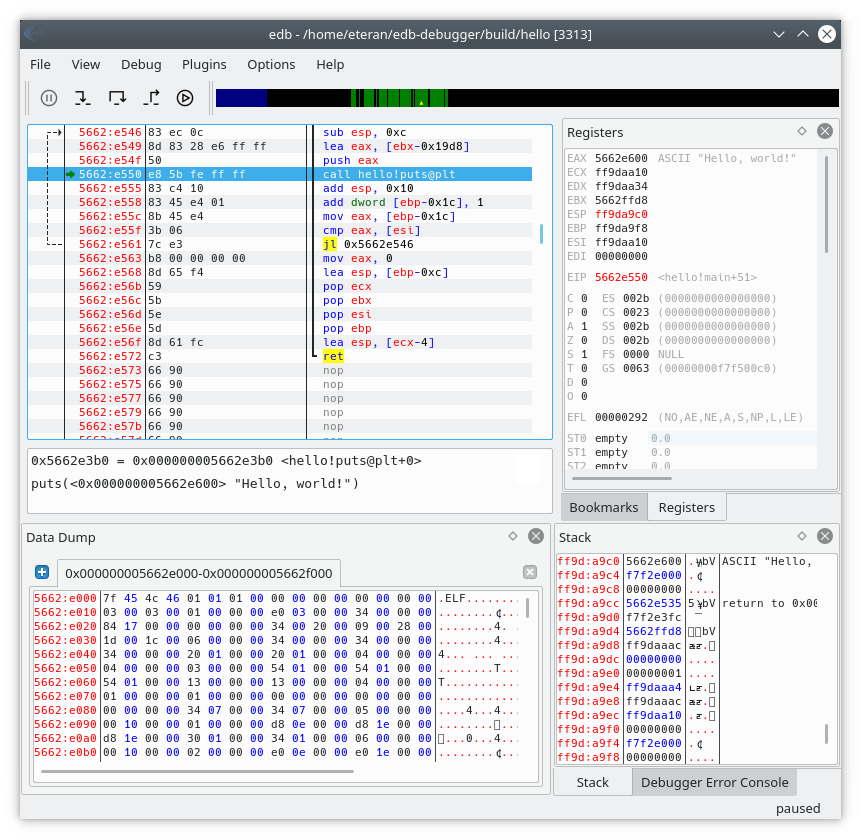
 eteran/edb-debugger
edb is a cross-platform AArch32/x86/x86-64 debugger.
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 ricardoquesada/regenerator2000
An interactive disassembler for the CPU 6502, focused on Commodore 8-bit computers. Features a TUI with modern features like x-ref, undo/redo, flow…
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 gallopsled/pwntools
CTF framework and exploit development library
 grammatech/ddisasm
Datalog-based disassembler producing reassemblable assembly from ELF/PE binaries, with GTIRB intermediate representation for binary analysis and…
 geo-tp/esp32-bit-pirate
A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
 zhuyansen/awesome-ai-reverse-engineering
Open-source AI reverse engineering tools for coding agents: Ghidra MCP, IDA Pro MCP, jadx, Frida, skills and REA. 122 repos, each read and…
 frida/frida-gum
Cross-platform instrumentation and introspection library written in C
 hyperdbg/hyperdbg
State-of-the-art native debugging tools
 angr/angr
A powerful and user-friendly binary analysis platform!
 riscv-software-src/riscv-isa-sim
Functional RISC-V ISA simulator supporting multiple extensions (RV32/64, V, cryptography) with interactive debug mode, GDB integration, and…
 vmoranv/jshookmcp
A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 jeanextreme002/pymemoryeditor
A pure-Python library, app and MCP that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
 lmacken/pyrasite
Inject code into running Python processes
 go-delve/delve
Source-level debugger for Go with CLI, API, and headless modes; supports breakpoints, variable inspection, and execution tracing for efficient…
 sunghoojung/reverse-engineering-browser
Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…






