#1
Capture The Flag platforms, challenge creation, solving tools, and competitive cybersecurity frameworks.
Kitploit recommended
 abdelhakimgafernetworksec/enigm-writeup
Comprehensive penetration testing write-up and exploit details for Hack The Box - Enigma machine, covering local enumeration, OliveTin CVE-2026-27626…
 recurse-labs/recurse
Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
 donofly/cve-2025-22457-vulnserver-lab
Hands-on lab reproducing CVE-2025-22457: sets up Docker attacker/victim containers, finds stack addresses with GDB, and delivers a msfvenom reverse…
 danreis20/pentest-lab-metasploitable2
Laboratório de pentest em rede isolada: enumeração com nmap/nikto e exploração manual do Metasploitable2 (backdoor vsFTPd CVE-2011-2523, bindshell)…
 w4r10ck423/envvisualizer
Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…
 iapetus12/hackcar-writeup
Writeup: Hackcar - DockerLabs (Node.js Inspector RCE + CVE-2025-55182 React2Shell)
 iapetus12/cohort-htb
HTB Cohort - SSRF, Marimo pre-auth RCE (CVE-2026-39987) y PackageKit privesc (CVE-2026-41651)
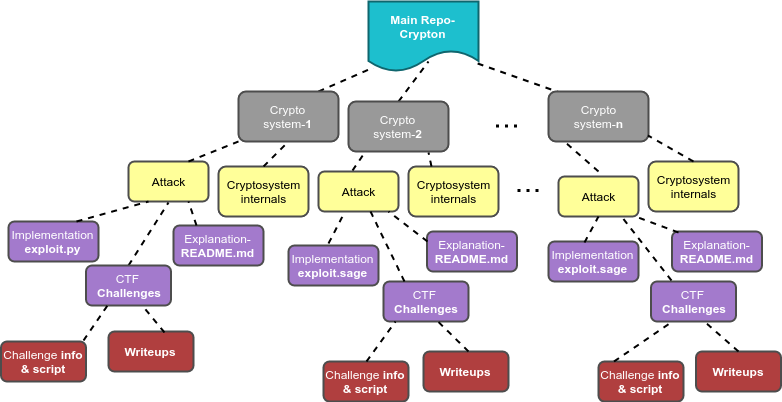 ashutosh1206/crypton
Library consisting of explanation and implementation of all the existing attacks on various Encryption Systems, Digital Signatures, Key Exchange,…
 screetsec/brutesploit
BruteSploit is a collection of method for automated Generate, Bruteforce and Manipulation wordlist with interactive shell. That can be used during a…
 b3nac/injuredandroid
A vulnerable Android application that shows simple examples of vulnerabilities in a ctf style.
 paradoxis/stegcracker
Steganography brute-force utility to uncover hidden data inside files
 p1kachu/v0lt
Security CTF Toolkit (Not maintained anymore)
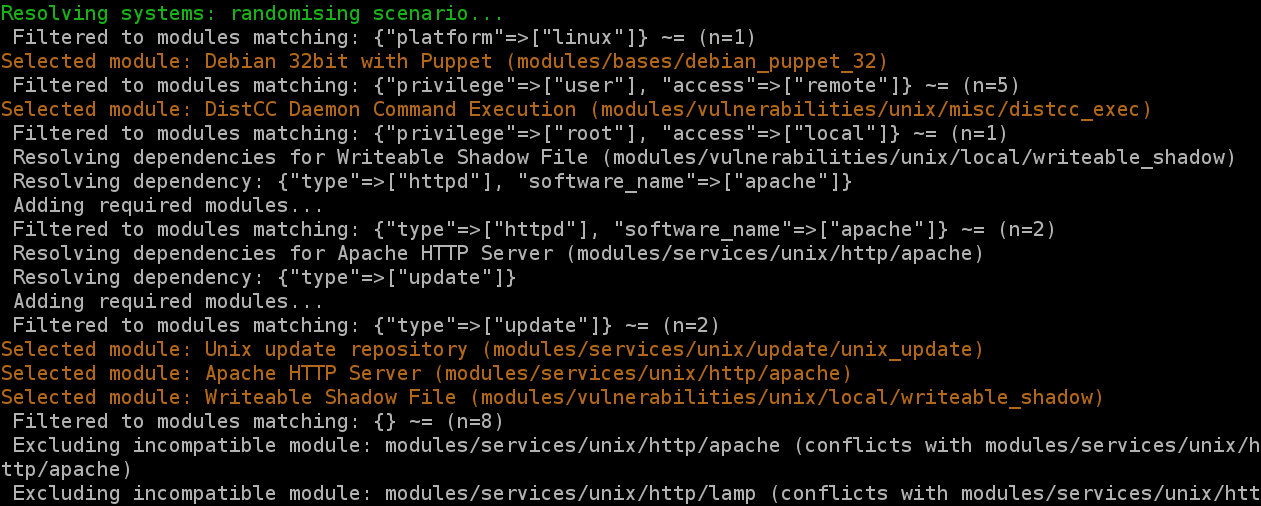 secgen/secgen
Generate vulnerable virtual machines on the fly (current team development is taking place in the cliffe/SecGen fork)

 orange-cyberdefense/ctf-party
🎏 A library to enhance and speed up script/exploit writing for CTF players
 zephrfish/cve-2021-28480_honeypoc3
DO NOT RUN THIS.
 octetsplicer/lazypariah
A tool for generating reverse shell payloads on the fly.