#1
Capture The Flag platforms, challenge creation, solving tools, and competitive cybersecurity frameworks.
Kitploit recommended

 thanhthuy2908/athdh_cve_2022_24644
Bai cuoi ky CVE-2022-24644
 m0d0ri205/wargame-turkey_in_2
CTF wargame platform featuring Unicode bypass exploitation (CVE-2015-9238), flag file segmentation, brute force delay, and password hashing for…
 synacktiv/bfs_challenge_2019
Solution for BFS Ekoparty challenge 2019
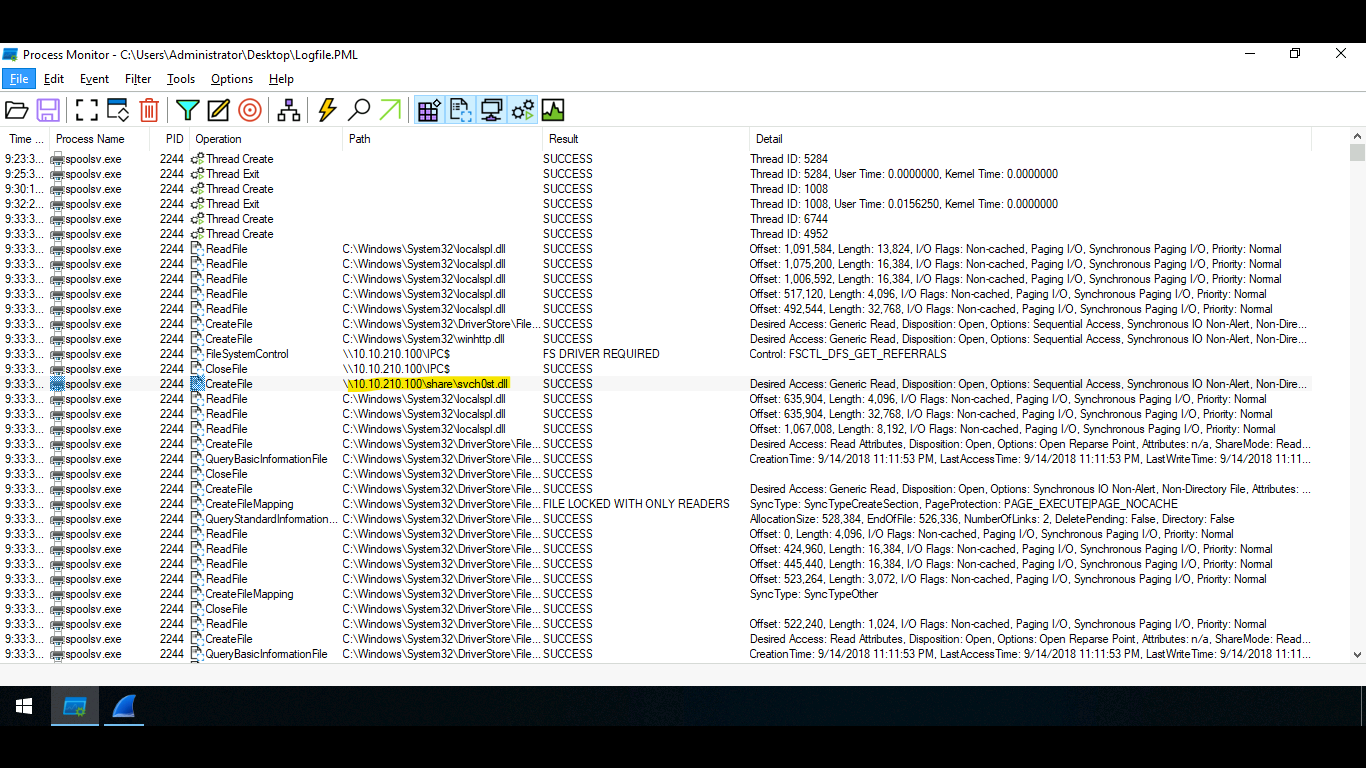 r1skkam/printnightmare
Learn about the vulnerability known as PrintNightmare (CVE-2021-1675) and (CVE-2021-34527)
 m0d0ri205/wargame-tarpioka
YISF 2024 CTF-Web (Directory Traversal via ".tar" file, CVE-2007-4559), easy
 bka/magento-cve-2024-34102-exploit-cosmicstring
Educational slides and demo material explaining the CosmicSting XXE vulnerability (CVE-2024-34102) in Adobe Commerce and Magento, including exploit…
 shayz614/cve-2022-22963
CVE to CTF FP
 adindrabkin/llama_facts
Web application vulnerable to Python3 Flask SSTI (CVE-2019-8341)
 abdibimantara/cve-2022-30190-analysis-with-letsdefends-lab
this is my simple article about CVE 2022-30190 (Follina) analysis. I use the lab from Letsdefend.
 natteesetobol/cve-2018-15133-lavel-expliot
"Lavel Exploit CVE-2018-15133 is a powerful exploit that allows attackers to gain unauthorized access to vulnerable systems. This exploit was…
 rishabh-kumar-cyber-sec/cve-2023-27163-ssrf-to-port-scanning
It is a simple script to automate internal port scanning dueto SSRF in requests-baskets v 1.2.1. this script can also assisst in solving 'SAU'…
 henry861010/network_security_nycu
CVE-2021-21300 exploit implementation for network security coursework at NYCU. Includes shell scripts for vulnerability demonstration and penetration…
 ch4n3-yoon/cve-2024-21520-demo
Educational repository demonstrating XSS vulnerabilities in Django Rest Framework applications. Contains intentionally vulnerable code to teach…
 ahmedmansour93/event-id-268-rule-name-soc292-possible-php-injection-detected-cve-2024-4577-
🚨 New Incident Report Completed! 🚨 Just wrapped up "Event ID 268: SOC292 - Possible PHP Injection Detected (CVE-2024-4577)" on LetsDefend.io. This…
 wwwiesel/infosec-black-friday
All the deals for InfoSec related software/tools this Black Friday
 cure53/xsschallengewiki
Community-maintained wiki cataloging XSS challenges and solutions, providing curated hands-on exercises for learning cross-site scripting…
 mitsu-bis/security-portfolio
Security portfolio of original responsible-disclosure findings, CTF and lab write-ups, methodology notes, and purpose-built pentest tooling covering…
 1833ravikumar-max/cve-2021-41773-apache-path-traversal-lab
Docker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.