
 #1
Capture The Flag platforms, challenge creation, solving tools, and competitive cybersecurity frameworks.
Kitploit recommended
 kybr-git/dc30-badge-challenge-writeup
Writeup for the DEF CON 30 badge challenge
 xib3rr4dar/wannarace
WebApp intentionally made vulnerable to Race Condition for practicing Race Condition
 jeanpeyremesmots/osx-password-dumper
A tool to dump users's .plist on a Mac OS system and to convert them into a crackable hash
 hasherezade/flareon2024
Solutions and write-ups for Flare-On 11 CTF challenges, showcasing reverse engineering, binary analysis, and malware analysis techniques with…
 r3tr074/exploits
Personal collection of exploits including n-days, 0-days, CTFs, kernel and browser vulnerabilities for security research and penetration testing.
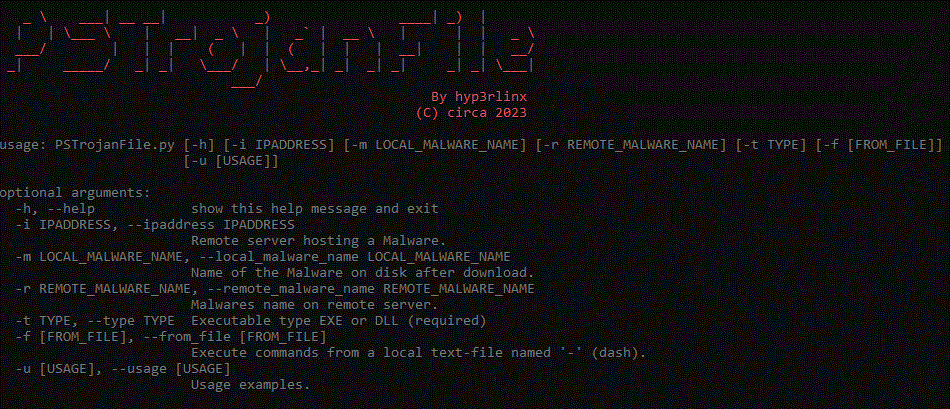 hyp3rlinx/pstrojanfile
Unfixed Windows PowerShell Filename Code Execution POC
 owasp/vulnerable-container-hub
VULCONHUB provides access to files to build your own hands-on vulnerable container image to learn and practice security
 zinja-coder/damn-vulnerable-android-components
An intentionally vulnerable Android Application to demonstrate various vulnerabilities that airses in Android Components.
 psycostea/pi-zero-2w-bad-usb
Configure your Pi Zero 2W to be a BadUSB
 anvbis/browser_ctf
A collection of web browser CTF challenges and solutions.
 ameetsaahu/kernel-exploitation
Linux kernel exploit development notes and scripts for CTF challenges, covering initramfs extraction, msg_msg/ldt_struct abuse, and practical…
 owasp/ai-vulnerabilities-playground
Hands-on AI security lab platform with 50+ scenarios across prompt injection, agentic system exploitation, model manipulation, and MCP trust boundary…
 thecybergeek/cve-2026-4480-poc
Proof-of-concept exploit for CVE-2026-4480, an unauthenticated remote command execution in Samba's print subsystem via %J injection. Includes reverse…
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
 jazho76/page_table_walk
Walk x86-64 page tables by hand in qemu and gdb. Decompose a virtual address, follow cr3 through all levels of physical memory, and extract a flag…
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
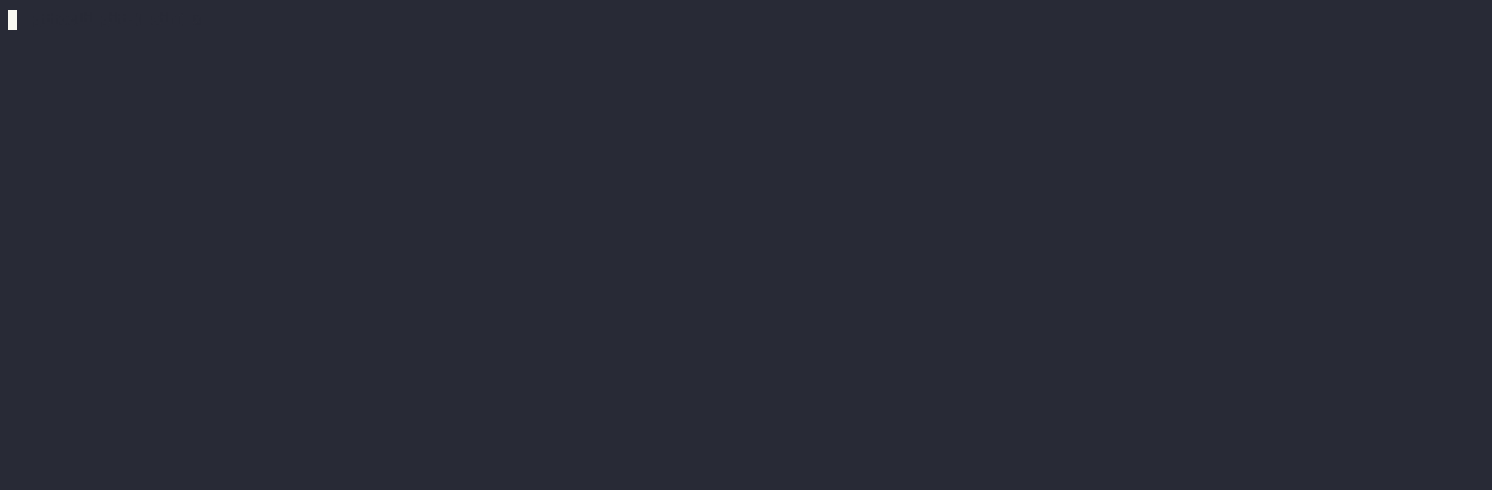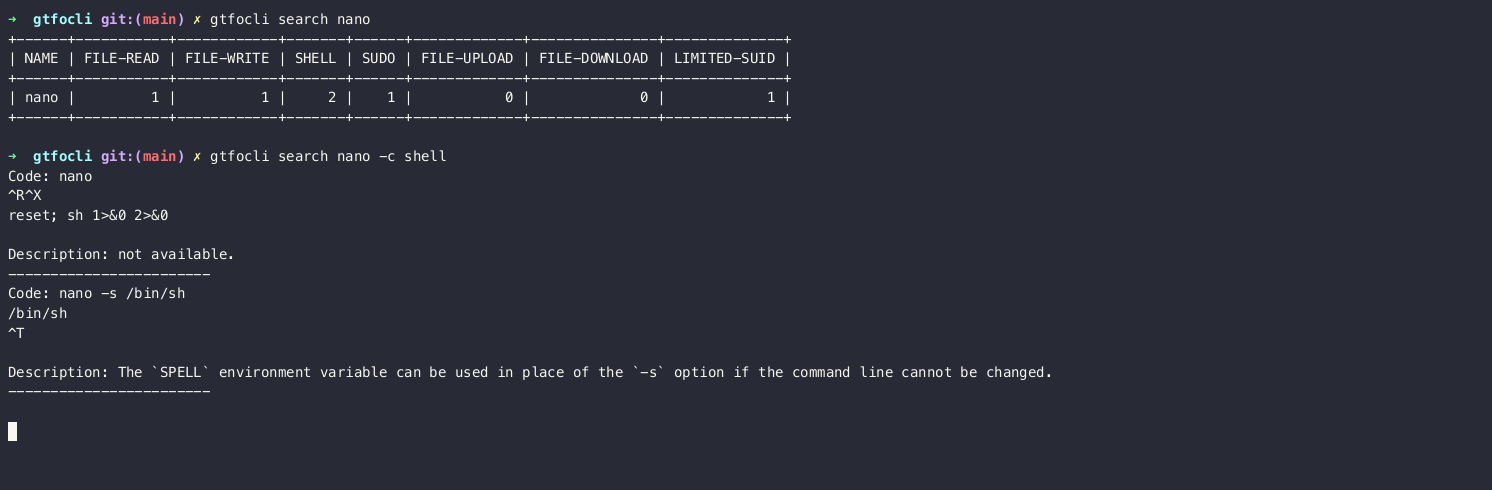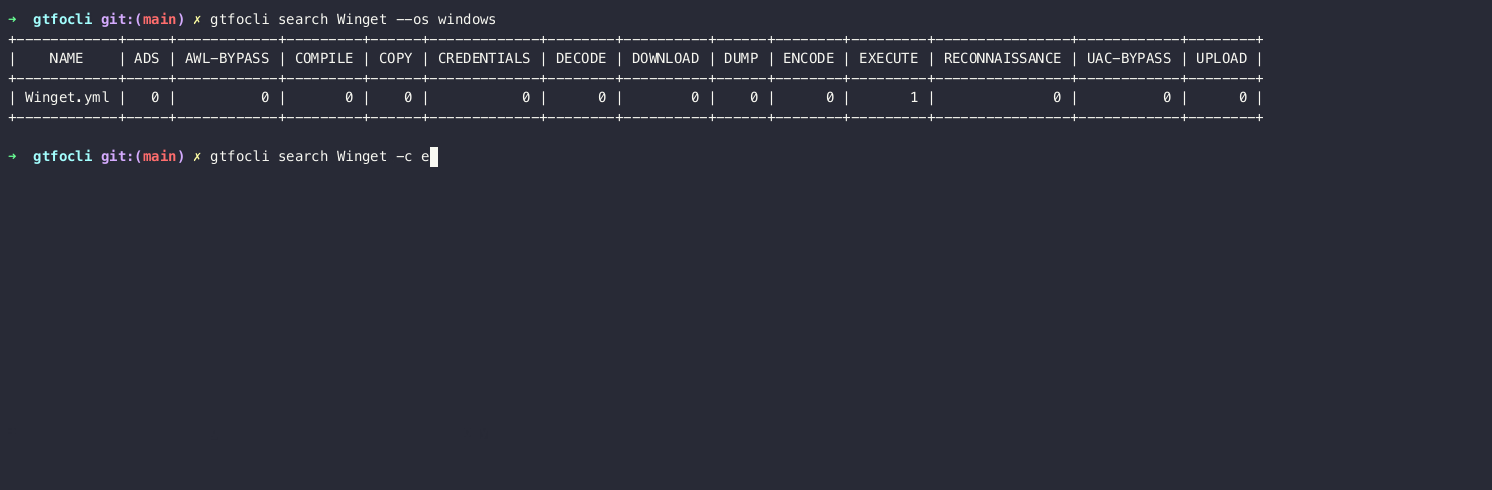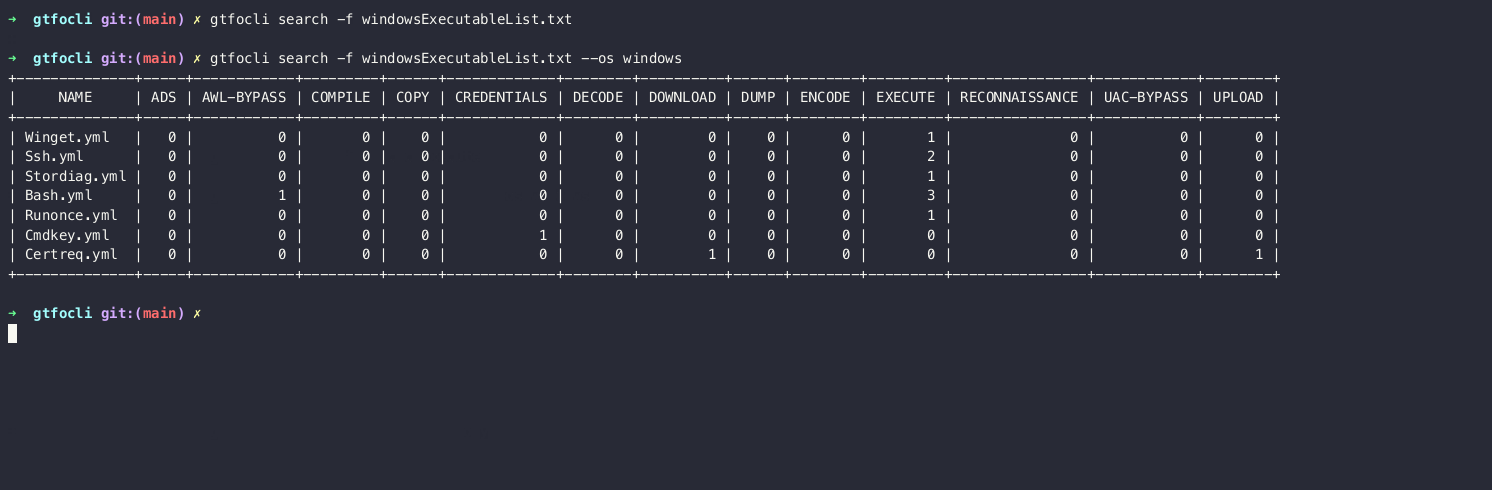 cmd-tools/gtfocli
GTFO Command Line Interface for easy binaries search commands that can be used to bypass local security restrictions in misconfigured systems.








