
 #1
Container breakout techniques, privilege escalation, and sandbox escape testing tools.
Kitploit recommended
 4qu4r1um/tugtainer-1.30.2-cve-2026-55494-and-cve-2026-62308-to-rce
A combination of CVE-2026-55494 and CVE-2026-62308 to get root privilege RCE in tugtainer
 wuzuowei/copy-fail-cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn vulnerability enabling local privilege escalation to root and container escape via AF_ALG and…
 recofu/cve-2026-31431-copy-fail
Local privilege escalation exploit for CVE-2026-31431 in the Linux kernel crypto subsystem, providing root access and container breakout with a…
 medaz-sploit/cve-2025-9074-docker-desktop-api-escape-poc
Proof-of-concept exploit for CVE-2025-9074 enabling Docker Desktop API escape via raw HTTP requests. Provides an emulated interactive shell inside a…
 pucagit/cve-2025-9074
PoC exploit for CVE-2025-9074 demonstrating a full Docker Desktop container escape on Windows and macOS via an unauthenticated internal Docker Engine…
 hulnothutu/cve-2026-31431
对 CVE-2026-31431 的复现分析、C 改编的 exp。
 gouldnicholas/cve-2026-5817-poc
Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…
 c0gnit00/cve-2025-9074
PHP poc, exploit for CVE-2025-9074
 kubernetesbachelor/cve-2024-21626
POC
 1neptune/dirtyfrag
Add go CVE-2026-43284 / CVE-2026-43500 (dirtyfrag) local privilege escalation exploit
 fulucky0-yuri/cve-2026-31431-pocc
C implementation of a proof-of-concept for CVE-2026-31431, a Linux kernel AF_ALG page cache poisoning vulnerability that enables local privilege…
 scherepiuk/container-escape-ebpf
POCs and Tetragon Rules for CVE-2024-21626 and CVE-2025-31133
 gr-1m/cve-2026-31431
Golang rewrite of the Copy Fail (CVE-2026-31431) local privilege escalation exploit, corrupting page cache to gain root on Linux systems.
 mishl-dev/cve_2026_31431
Exploit for CVE-2026-31431, a Linux kernel page-cache write primitive enabling local privilege escalation and container escape via AF_ALG and…
 rat5ak/cve-2026-31413-bpf-container-escape
CVE-2026-31413: BPF verifier soundness bug - container escape
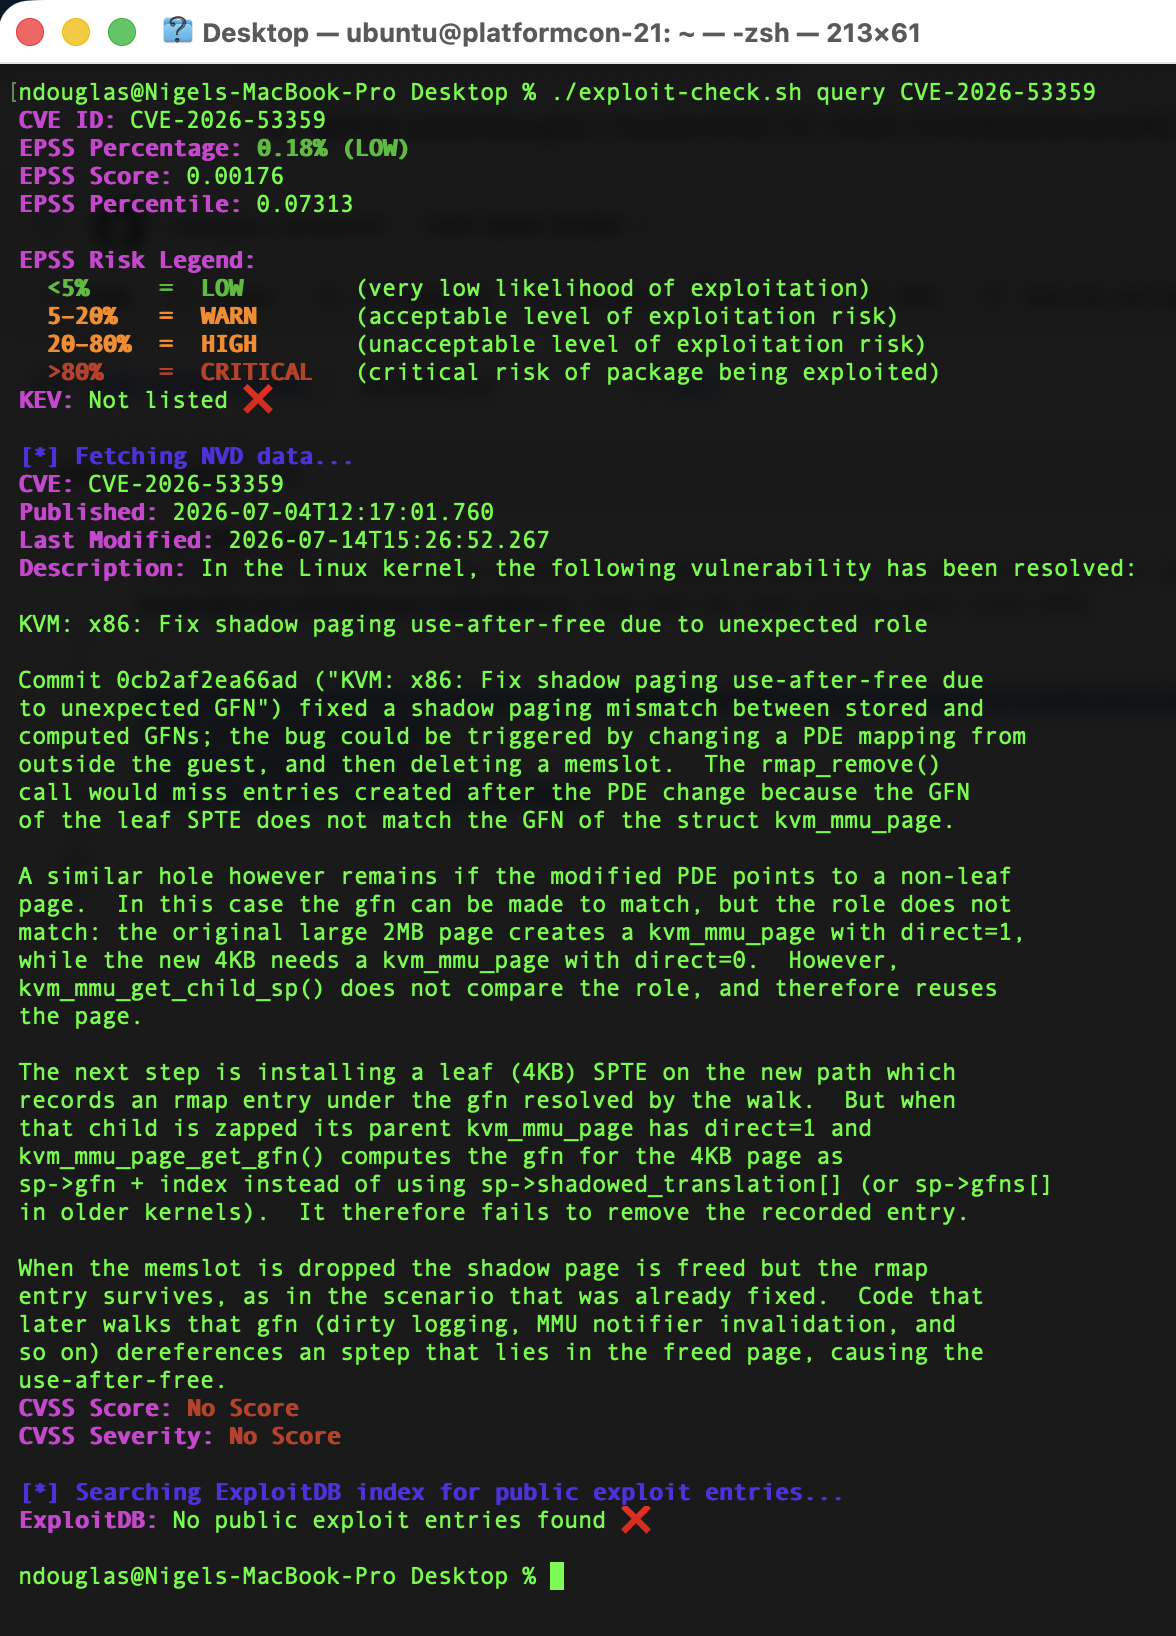 ndouglas-cloudsmith/cve-2026-53359
A 16-year-old bug in the Linux kernel lets a rented VM break out and attack the host it runs on. Intel and AMD alike. Januscape is a use-after-free…
 r0binak/cve-2025-23266
CVE-2025-23266 – Fully Weaponized NVIDIA Container Toolkit Exploit
 flojboj/cve-2024-21626
Working exploit for CVE-2024-21626, a runC/Docker container escape via working directory symlink attack, enabling host filesystem access.








