

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
ActiveMQ-cve-2026-42588-scanner-gui — GUI-based scanner and exploit tool for CVE-2026-42588 (ActiveMQ RCE). Supports VPS payload delivery and DNSLog-based vulnerability verification with automated XML injection. | Kitploit
Tools/GitHubGitHub/strivepan/activemq-cve-2026-42588-scanner-gui
Vulnerability ScannersPayload GenerationExploitationWeb Application ExploitationCommand and ControlRemote Access Tool
GitHubstrivepan/activemq-cve-2026-42588-scanner-gui

ActiveMQ-cve-2026-42588-scanner-gui

GUI-based scanner and exploit tool for CVE-2026-42588 (ActiveMQ RCE). Supports VPS payload delivery and DNSLog-based vulnerability verification with automated XML injection.

View Repository
10315 months agoNot yet reviewed
Share

ActiveMQ-cve-2026-42588-scanner-gui

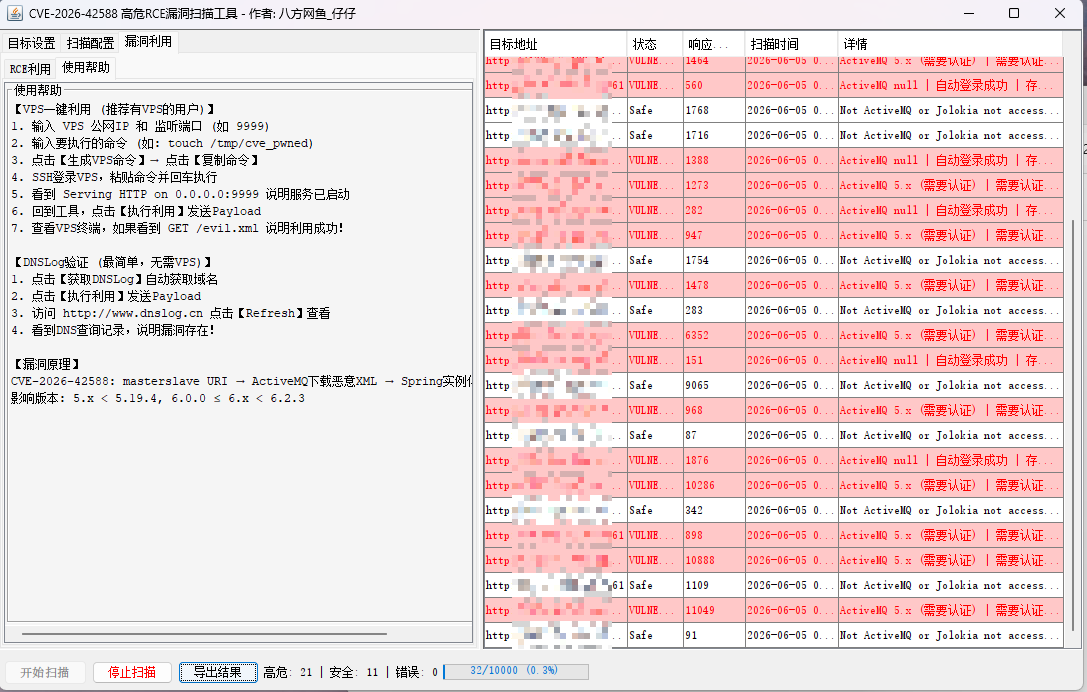
【One-click VPS Exploitation (Recommended for users with a VPS)】

  1. Enter the VPS public IP and listening port (e.g., 9999)
  2. Enter the command to execute (e.g., touch /tmp/cve_pwned)
  3. Click [Generate VPS Command] → Click [Copy Command]
  4. SSH into the VPS, paste the command, and press Enter
  5. See Serving HTTP on 0.0.0.0:9999 indicating the service has started
  6. Return to the tool, click [Execute Exploit] to send the Payload
  7. Check the VPS terminal; if you see GET /evil.xml, the exploit was successful!

【DNSLog Verification (Simplest, no VPS required)】

  1. Click [Get DNSLog] to automatically obtain a domain
  2. Click [Execute Exploit] to send the Payload
  3. Visit http://www.dnslog.cn and click [Refresh] to check
  4. If you see a DNS query record, the vulnerability exists!

【Vulnerability Principle】 CVE-2026-42588: masterslave URI → ActiveMQ downloads malicious XML → Spring instantiates Bean → RCE Affected versions: 5.x < 5.19.4, 6.0.0 ≤ 6.x < 6.2.3
ActiveMQ ActiveMQ_RCE
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    524
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    478
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    357
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    317
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    305
  • 6

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    275

Explore all tools

Browse our collection of tools

View all tools →






