
 #1
C2 frameworks, redirectors, listeners, and command infrastructure tools.
Kitploit recommended

 roostercoopllc/flipper-mcp
AI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
 oyesanyf/oshoosiclaw
Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…
 iss4cf0ng/openshell
Lightweight Go-based reverse shell management server with a web GUI for interactive shell sessions, session management, and multi-tab terminal…
 st3rven/fronthunter
FrontHunter is a tool for testing large lists of domains to identify candidates for domain fronting.
 r00k5a58/pyc2
simple c2 written in python to demonstrate security concepts
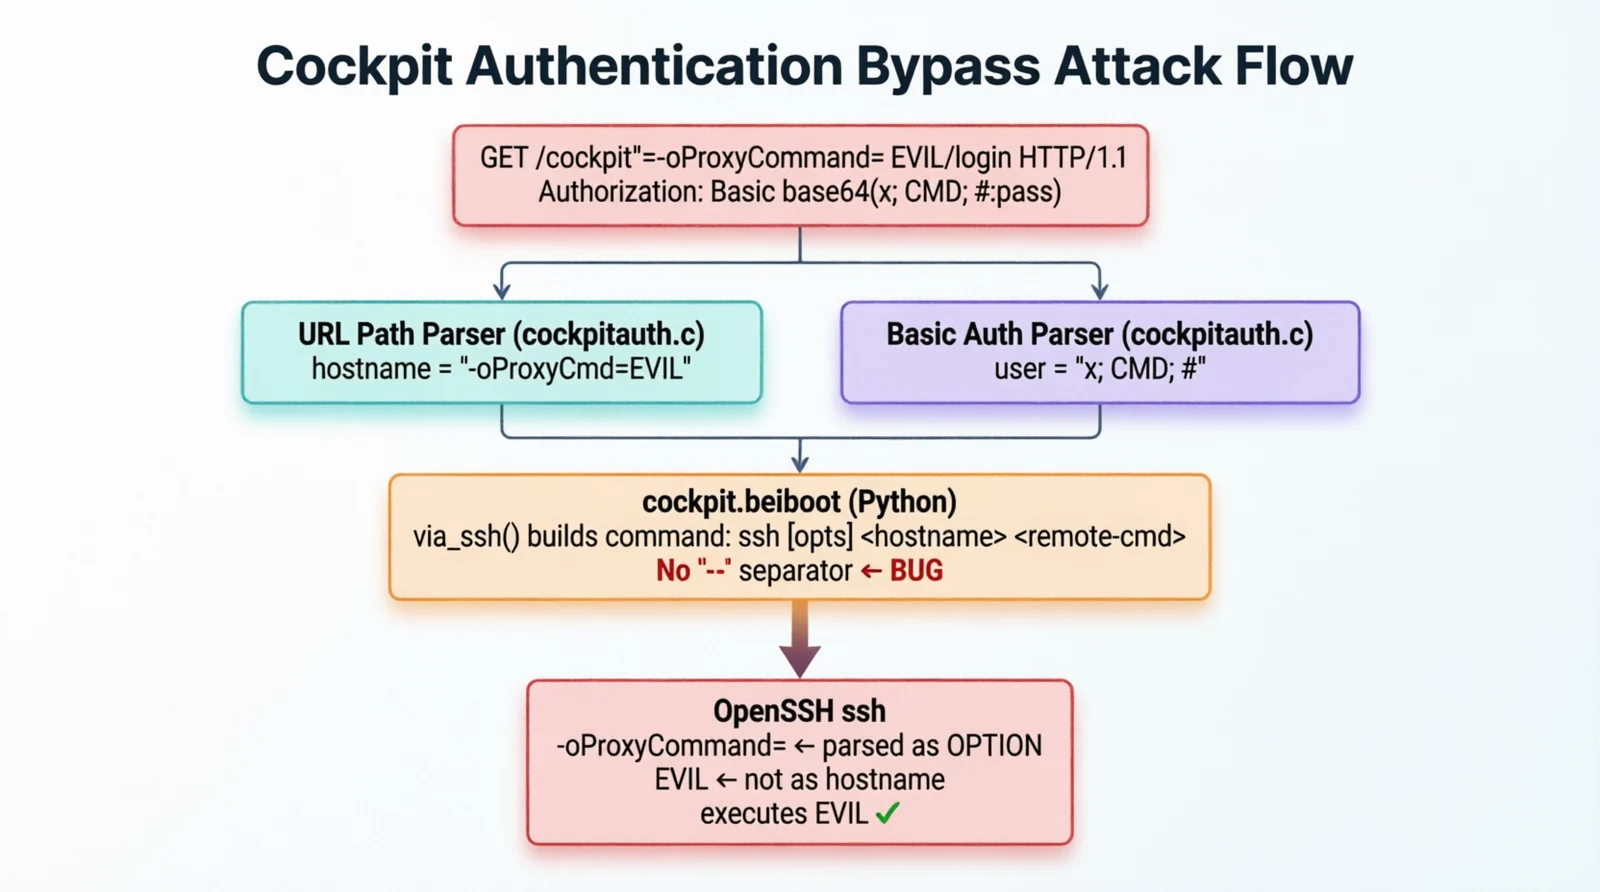 cyberheartmi9/cve-2026-4631-cockpit-rce
Cockpit: Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection
 tas9er/cve-2021-22986
Code By:Tas9er / F5 BIG-IP 远程命令执行漏洞
 rabbitsafe/cve-2021-36260
CVE-2021-36260
 henry4e36/cve-2022-30525
Zyxel 防火墙远程命令注入漏洞(CVE-2022-30525)
 padsalatushal/cve-2011-2523
Python exploit for vsftpd 2.3.4 - Backdoor Command Execution
 tc4dy/cve-2026-15409-15410-framework
Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…
 tc4dy/cve-2026-41940-poc-exploit
PoC exploit for CVE-2026-41940 targeting cPanel/WHM authentication bypass via CRLF injection. Supports session hijacking, RCE, reverse shell, mass…
 moch3n/cve-2022-22947-spring-cloud-gateway-spelrce
Spring Cloud Gateway远程代码执行漏洞POC,基于命令执行的基础上,增加了反弹shell操作
 user696/mrrat
:mouse: This is a cross-platform Python 2.x Remote Access Trojan (RAT)
 aminetitrofine/cve-2022-30190
Follina (CVE-2022-30190) is a Microsoft Office zero-day vulnerability that has recently been discovered. It’s a high-severity vulnerability that…
 horizon3ai/cve-2024-8190
Proof-of-concept exploit for CVE-2024-8190, an authenticated command injection vulnerability in Ivanti Cloud Service Appliance, enabling remote…
 leviticus-triage/chromsploit-framework
Advanced AI-Powered Exploitation Framework | CVE-2025-4664 & CVE-2025-2783 & CVE-2025-2857 & CVE-2025-30397 |
 arlyone/apache-struts-0day-exploit
Critical Remote Code Execution Vulnerability (CVE-2018-11776) Found in Apache Struts.








