
 #1
C2 frameworks, redirectors, listeners, and command infrastructure tools.
Kitploit recommended

 rmikehodges/hidensneak
a CLI for ephemeral penetration testing
 p0dalirius/cve-2018-16763-fuelcms-1.4.1-rce
Exploit to trigger RCE for CVE-2018-16763 on FuelCMS <= 1.4.1 and interactive shell.
 0x20c/cve-2024-23692-exp
CVE-2024-23692 Exploit
 catatonicprime/tospovirus
A WiFi Pineapple infecting worm.
 cr4at0r/next.js-rce-scanner-burpsuite-extension-
使用burp自动检测CVE-2025-55182 Next.js RCE 漏洞
 rev-code/androidclient
Android remote administration client
 xyplex3/redteamcoin
Red Team Coin for crypto-mining operations.
 watchtowrlabs/watchtowr-vs-fortisiem-cve-2025-25256
Detection artifact generator for FortiSIEM CVE-2025-25256 unauthenticated remote command execution vulnerability. Sends crafted packets to verify…
 n1et/cve-2026-46529
Evince/xreader/Atril RCE exploit to CVE-2026-46529
 darksh3llru/dark-doh
Covert file-transfer tool using DNS-over-HTTPS: encodes payload chunks in TXT records, applies XOR obfuscation, and can execute shellcode for…
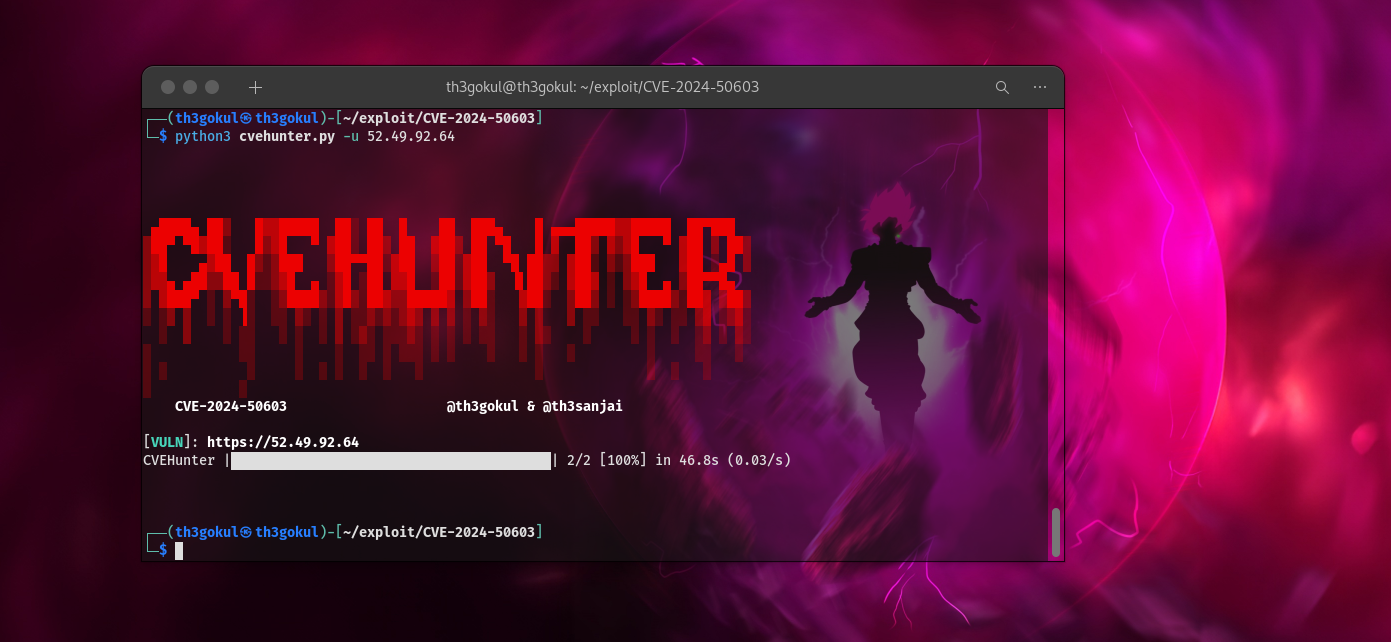 th3gokul/cve-2024-50603
CVE-2024-50603: Aviatrix Controller Unauthenticated Command Injection
 lorddemon/drupalgeddon2
Remote code execution exploit for Drupal CVE-2018-7600 (Drupalgeddon2) with command injection via HTTP requests.
 cfielding-r7/poc-cve-2023-2868
Ruby-based proof-of-concept exploit for CVE-2023-2868 command injection in Barracuda ESG, delivering a reverse shell for targeted penetration testing.
 blue0x1/rosemary
Rosemary: Cross-platform kernel-level pivoting over QUIC. No TUN/TAP. No proxychains. No proxy settings.
 elizarfish/cve-2023-21823
CVE-2023-21823 PoC
 mackleadmire/cve-2018-3191-rce-exploit
Exploit for CVE-2018-3191 targeting Oracle WebLogic servers. Generates a malicious payload via RMI, deploys reverse shell classes on an HTTP server,…
 jax7sec/cve-2022-22954
提供批量扫描URL以及执行命令功能。Workspace ONE Access 模板注入漏洞,可执行任意代码
 iveresk/cve-2022-26134
Just simple PoC for the Atlassian Jira exploit. Provides code execution for unauthorised user on a server.








