
 #1
C2 frameworks, redirectors, listeners, and command infrastructure tools.
Kitploit recommended

 tevora-threat/rt_redirectors
Ansible role to configure redirectors for red team C2
 benjaminhays/cve-2022-36804-poc-exploit
Somewhat Reliable PoC Exploit for CVE-2022-36804 (BitBucket Critical Command Injection)
 k8gege/cve-2021-40444
Exploit toolkit for CVE-2021-40444 MSHTML remote code execution, featuring DLL payload generation, Office document crafting, and lateral movement…
 gryfman/dlpwn
Red Team tool for covert file exfiltration via Bluetooth audio transmission, encoding binary data into FLAC signals to bypass EDR, XDR, and DLP…
 whispergate/lldp
C2 profile for Mythic tunneling encrypted peer-to-peer agent traffic through IEEE 802.1AB LLDP Organizationally Specific TLVs for covert Layer 2…
 haxrob/bpfdoor-controller-source
Source code for a BPFDoor backdoor controller supporting TCP, UDP, ICMP, and HTTPS covert communication channels with magic packet activation,…
 mr-wolf-gb/d-rat_vb.net_mysql_php
D-RAT [VB.NET]+[MySQL]+[PHP]
 ill-deed/cve-2025-34085-multi-target
Multi-target unauthenticated RCE scanner for CVE-2025-34085 affecting WordPress Simple File List plugin. Uploads, renames, and triggers PHP webshells…
 octoberfest7/aggressor_snippets
A collection of random small Aggressor snippets that don't warrant their own repo
 90n45-d3v/bluebunny
BLE-based C2 server for Hak5 Bash Bunny enabling wireless command injection, payload delivery, and remote control over Bluetooth Low Energy.
 shellkraft/ledger
An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…
 s1xhcl/f5_rce_poc
cve-2021-22986 f5 rce 漏洞批量检测 poc
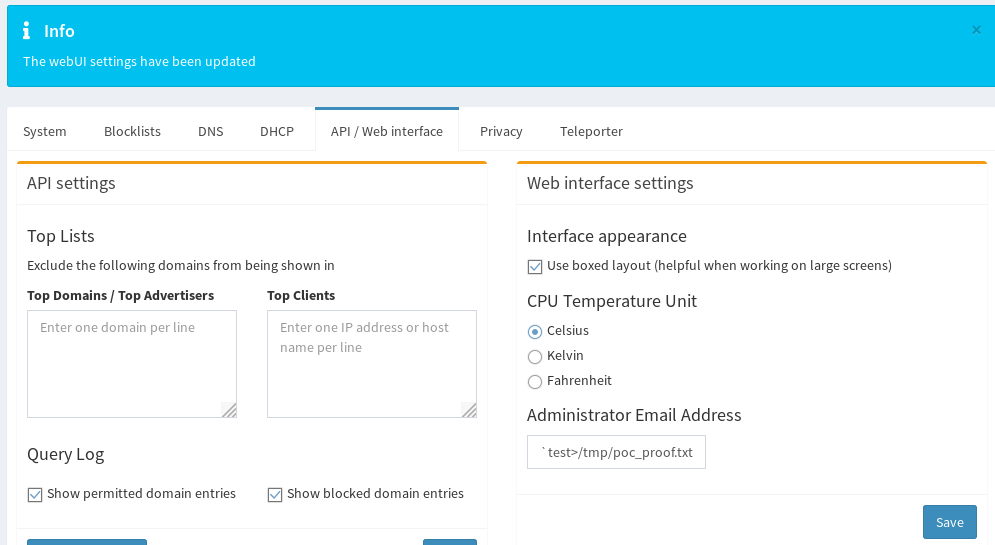 pr0tean/cve-2019-13051
Proof-of-concept exploit for Pi-Hole AdminLTE command injection (CVE-2019-13051) enabling remote root access via email field injection and cron-based…
 ap0dexme0/cve-2023-34960
Perform with Massive Command Injection (Chamilo)
 watchtowrlabs/palo-alto-panos-cve-2024-0012
Exploit for CVE-2024-0012 and CVE-2024-9474 targeting authentication bypass and authenticated command injection in Palo Alto PAN-OS management web…
 tas9er/springcloudgatewayrce
SpringCloudGatewayRCE - CVE-2022-22947 / Code By:Tas9er
 jbaines-r7/overkill
QNAP N-Day (Probably not CVE-2020-2509)
 mbadanoiu/cve-2025-31644
CVE-2025-31644: Command Injection in Appliance mode in F5 BIG-IP








