
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended
 pcmkuit/cve-2021-44228---log4shell-analysis
Technical deep dive into Apache Log4j2 JNDI injection vulnerability. Features static code analysis, patch comparison, attack vectors (LDAP/RMI/DNS),…
 gonaumov/cve-2025-55182-checker
A portable Bash script to detect vulnerable versions of React Server DOM and Next.js packages affected by [CVE-2025-55182]
 trerb/ai-ide-config-guard
Scan a repo for AI-IDE config files that can trigger RCE via Claude Code hooks, Cursor rules, MCP auto-registration. Detects CVE-2025-59536,…
 jaytarr-geo/nextjs-lodash-cve-2025-13465-repro
Reproduction environment for CVE-2025-13465, demonstrating a vulnerability in Next.js applications using Lodash. Provides a minimal setup to test and…
 changgun-lee/next.js-rsc-rce-scanner-cve-2025-66478
CLI scanner that detects whether a target website runs a vulnerable Next.js version affected by CVE-2025-66478 RCE in React Server Components.
 ankitpandey383/roundcube-cve-2025-49113-lab
Hands-on exploitation lab for Roundcube Webmail CVE-2025-49113 (authenticated PHP object deserialization → RCE) to read /secret.txt.
 sudo-wp/sudowp-crowdsignal-forms
A security-hardened fork of Crowdsignal Forms. Patches CVE-2025-69015 (Broken Access Control), modernizes for PHP 8.2+, and enforces strict…
 premdanav/react2shelldemo
This repo contains the scripts you can execute to simulate the (CVE-2025-55182) along with next.js server
 tnot123/cve-2017-9822
In-depth technical analysis and proof-of-concept for CVE-2017-9822, an insecure deserialization vulnerability in DotNetNuke leading to remote code…
 ubaydev/cve-2026-11551-poc
Proof-of-concept exploit for CVE-2026-11551, an unauthenticated privilege escalation vulnerability in the Branda White Label plugin for WordPress,…
 degenwithheart/react2shell-vulnerability-verification-script
Standalone Python script to verify if a project is affected by CVE-2025-55182 (React2Shell). Checks package.json dependencies and performs optional…
 lukasz-rybak/cve-2026-23498
CVE-2026-23498 - Shopware Has Improper Control of Generation of Code in Twig rendered views
 ragatzino/test-cve-2016-1000027
validation de l'exploitabilité d'une CVE
 nunpa/cve-2025-64459
check if vulnerable python-django version to CVE-2025-64459 bug
 lycis/cawdog
CAWODOG is a proof-of-concept project demonstrating how to protect Python-based AI models deployed on offline industrial machines. Across three…
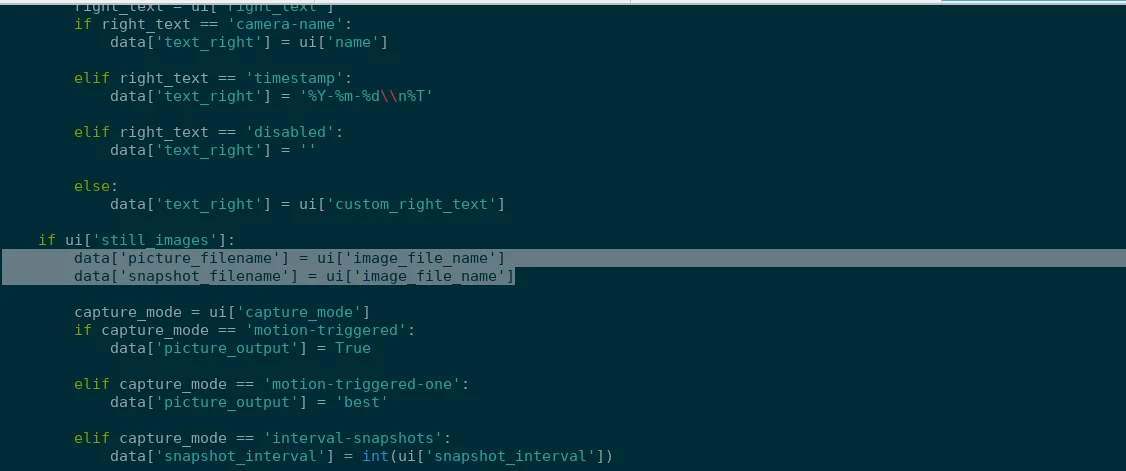 prabhatverma47/cve-2025-60787
Proof-of-concept for CVE-2025-60787, demonstrating remote code execution in MotionEye <= 0.43.1b4 via client-side validation bypass and command…
 syfi/cve-2023-46818
Metasploit Modules
 d0n601/cve-2025-6220
Ultimate Addons for Contact Form 7 <= 3.5.12 - Authenticated (Administrator+) Arbitrary File Upload via 'save_options'








