#1
 darrocarocatest-sys/pv2-victim
authz research - CVE-2026-3306 fix coverage
 jsecx88/cve-2025-29009-poc
Medical Prescription Attachment Plugin for WooCommerce <= 1.2.3 - Unauthenticated Arbitrary File Upload.
 rvermeulen/codeql-cve-2022-35737
A CodeQL query to find CVE 2022-35737
 oguri-souhei/cve-2025-55182
CVE-2025-55182 の検証用
 jithinodattu/cve-2007-4559-lab
Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…
 mooseloveti/vitepos-cve-report
Disclosure for CVE-2025-13156
 aecelen/ktor-xxe-poc
PoC for CVE-2023-45612
 thegenetic/cve-2026-2964-lab
Educational lab demonstrating CVE-2026-2964, a prototype pollution vulnerability in web-audio-recorder-js leading to RCE. Includes vulnerable and…
 vladjrfhfg/react-site-cve-2025-55182
Intentionally vulnerable Next.js corporate landing page demonstrating CVE-2025-55182, a JSON injection leading to RCE/SSRF via unsafe deserialization…
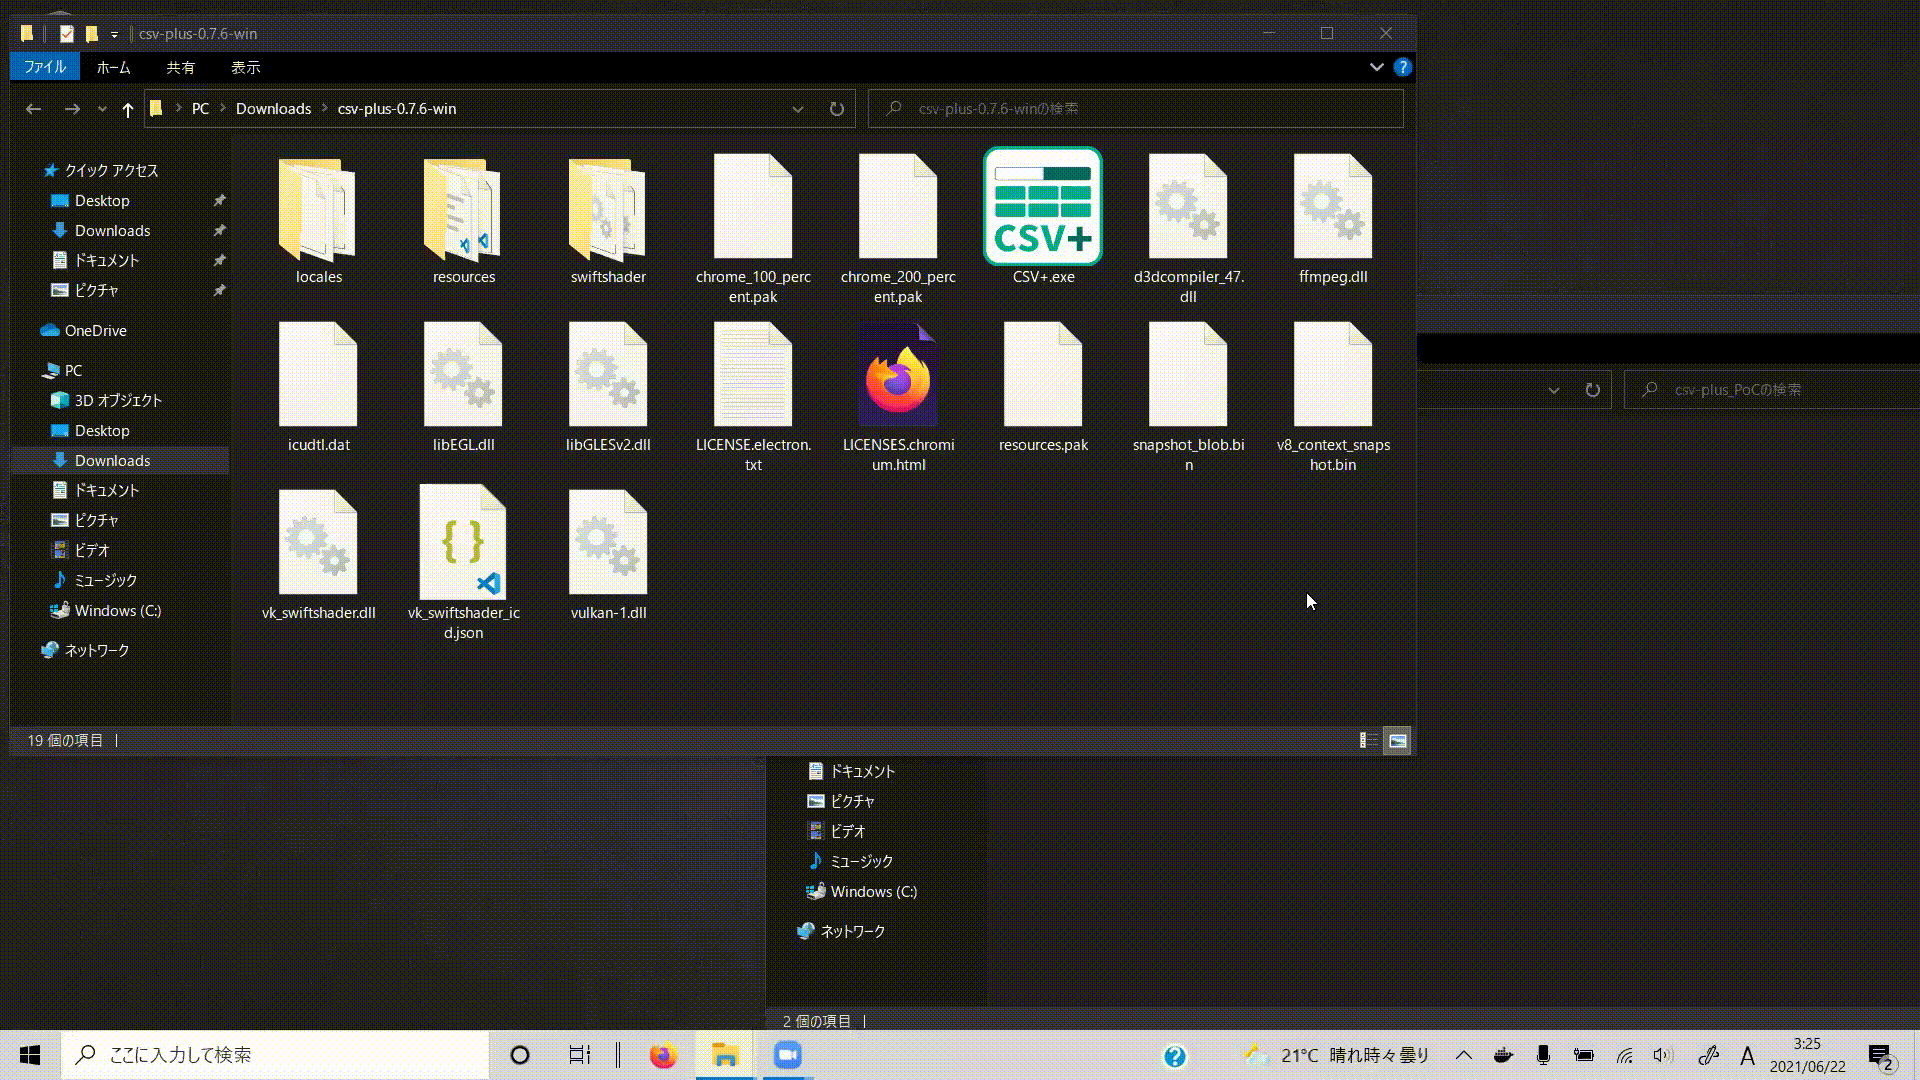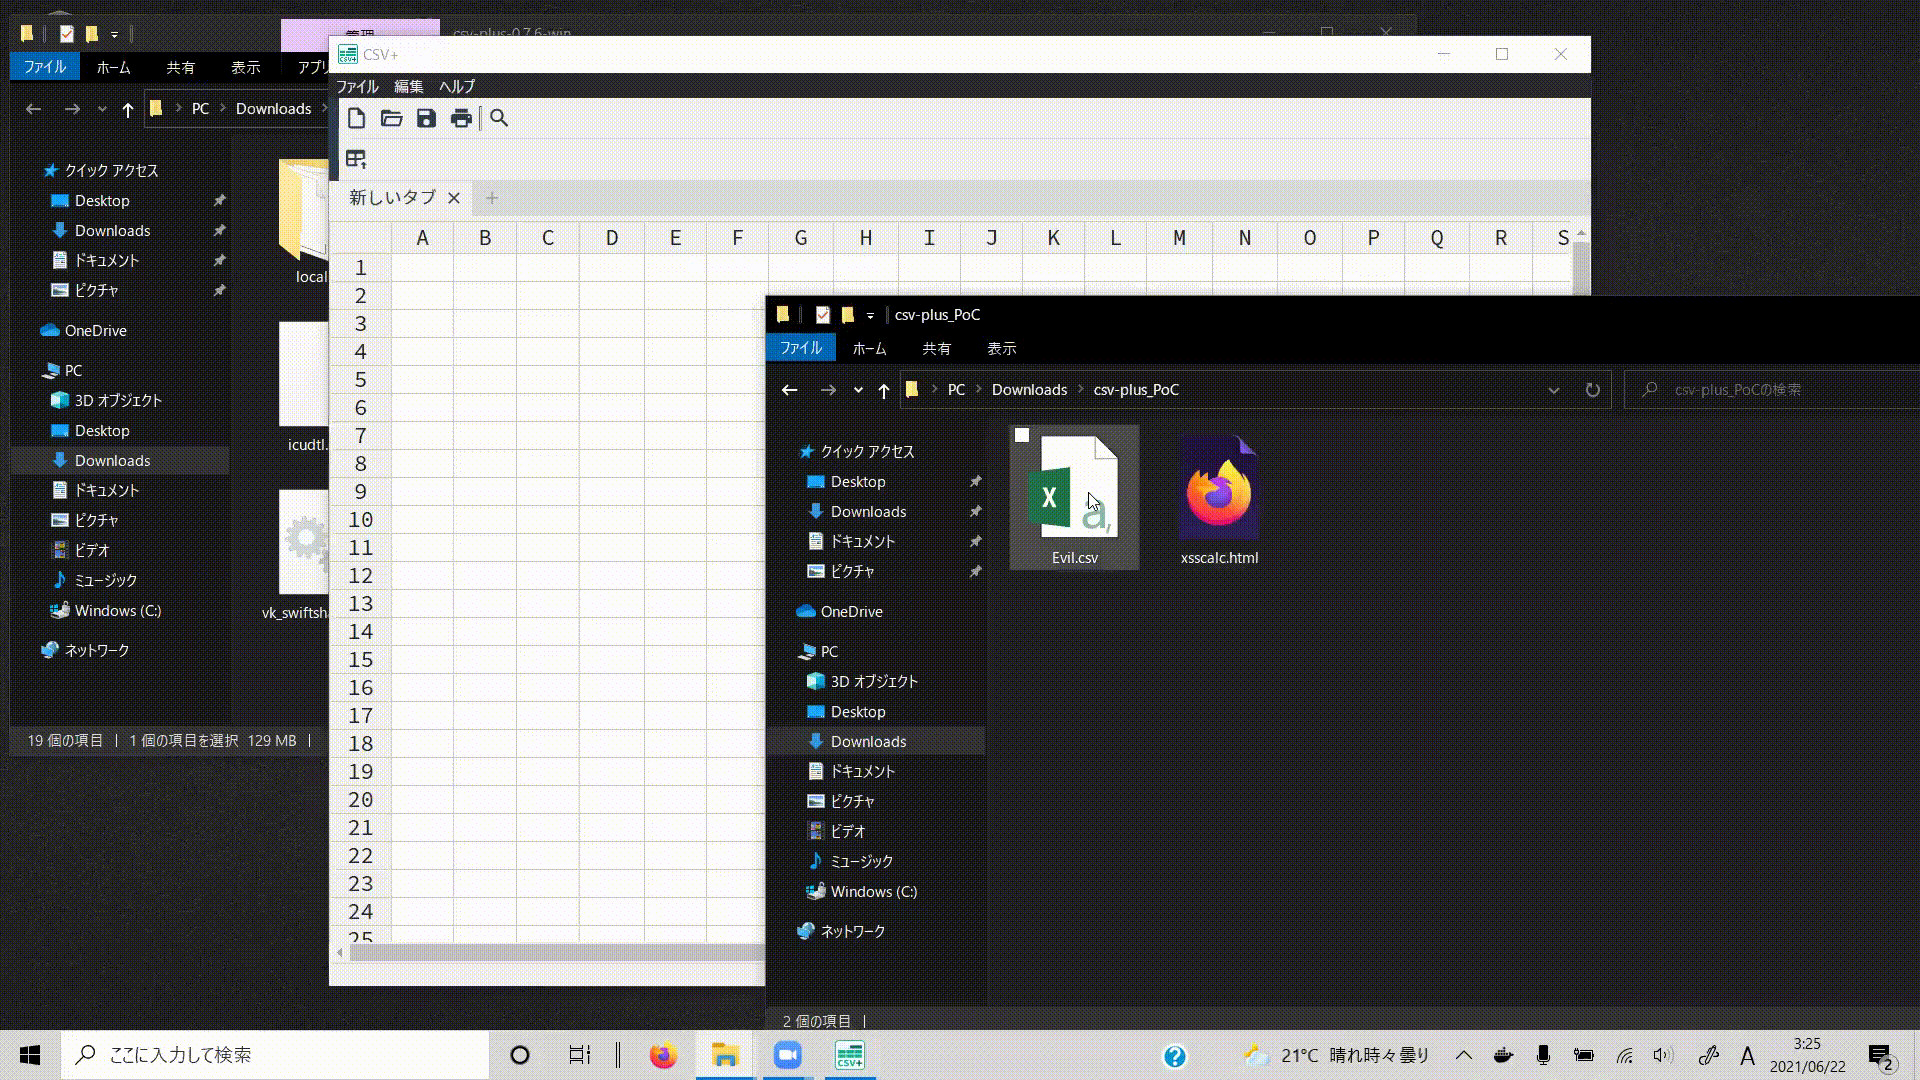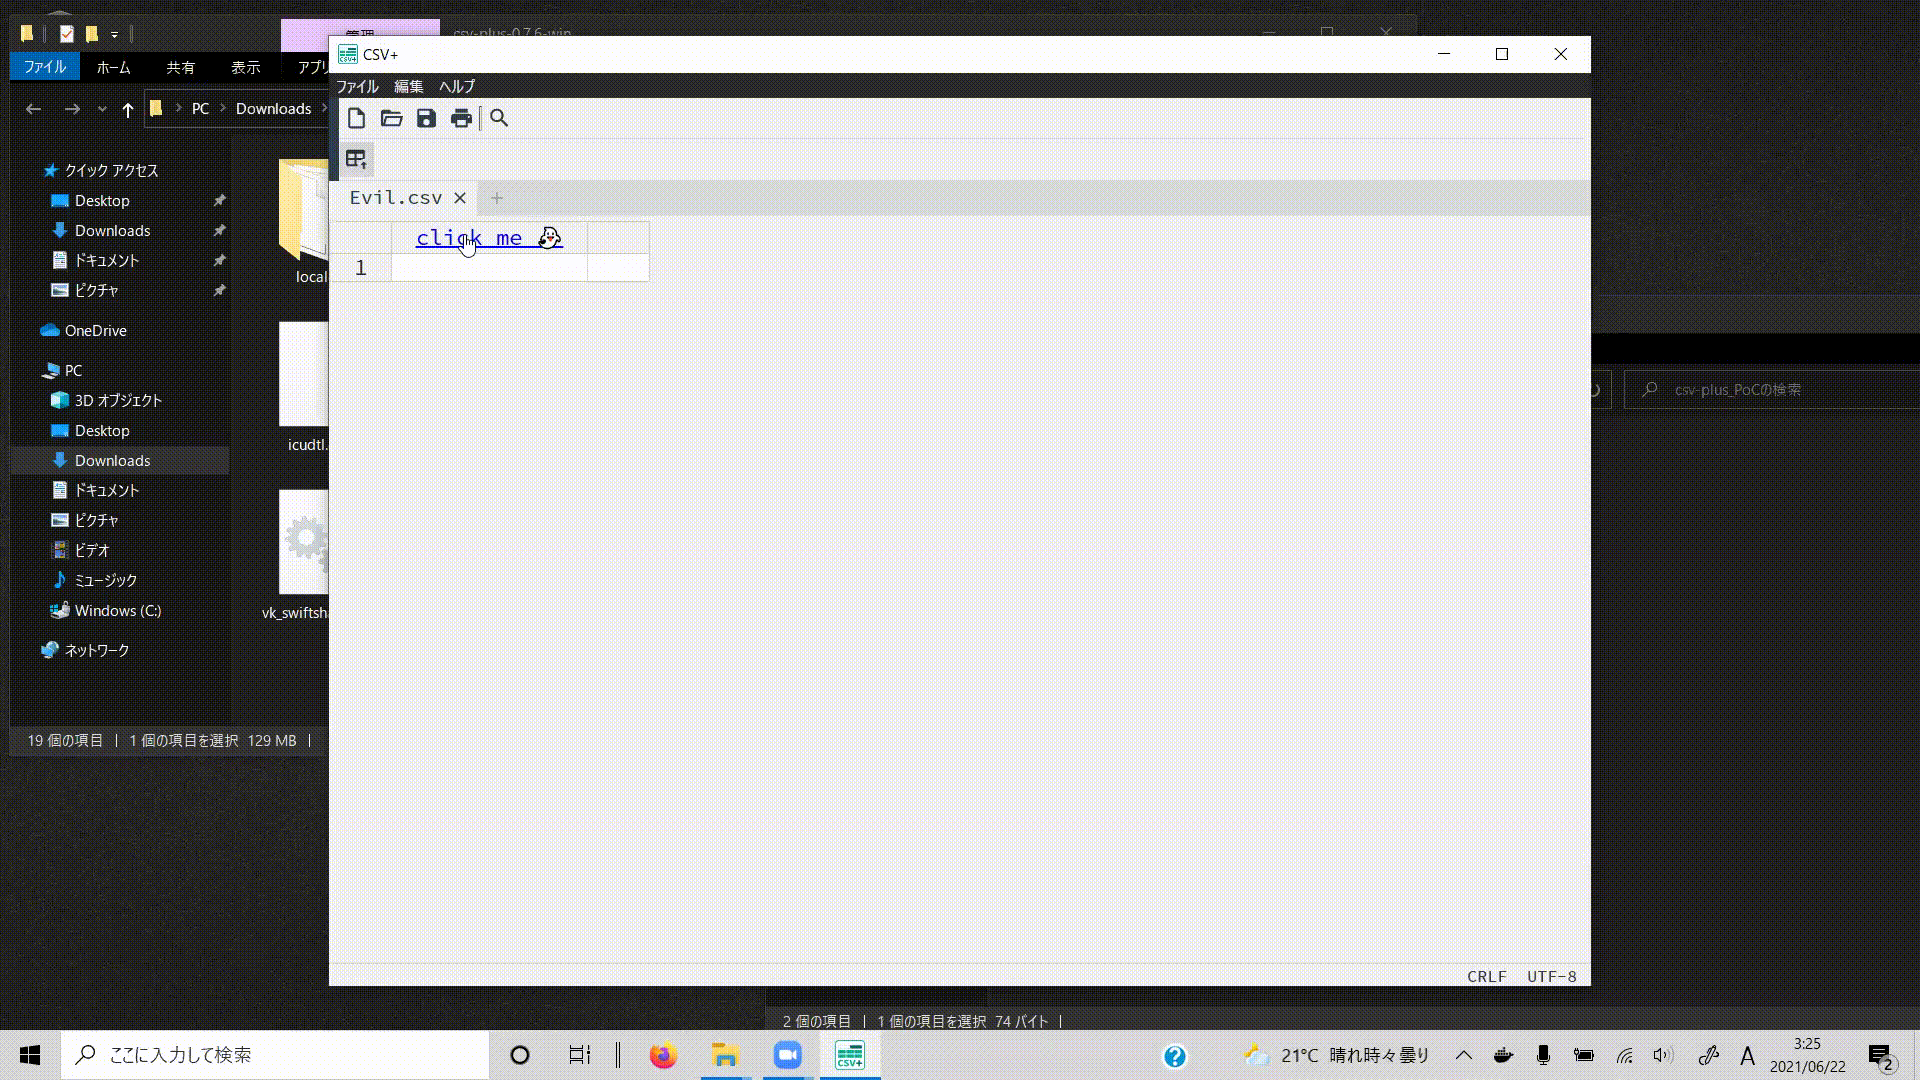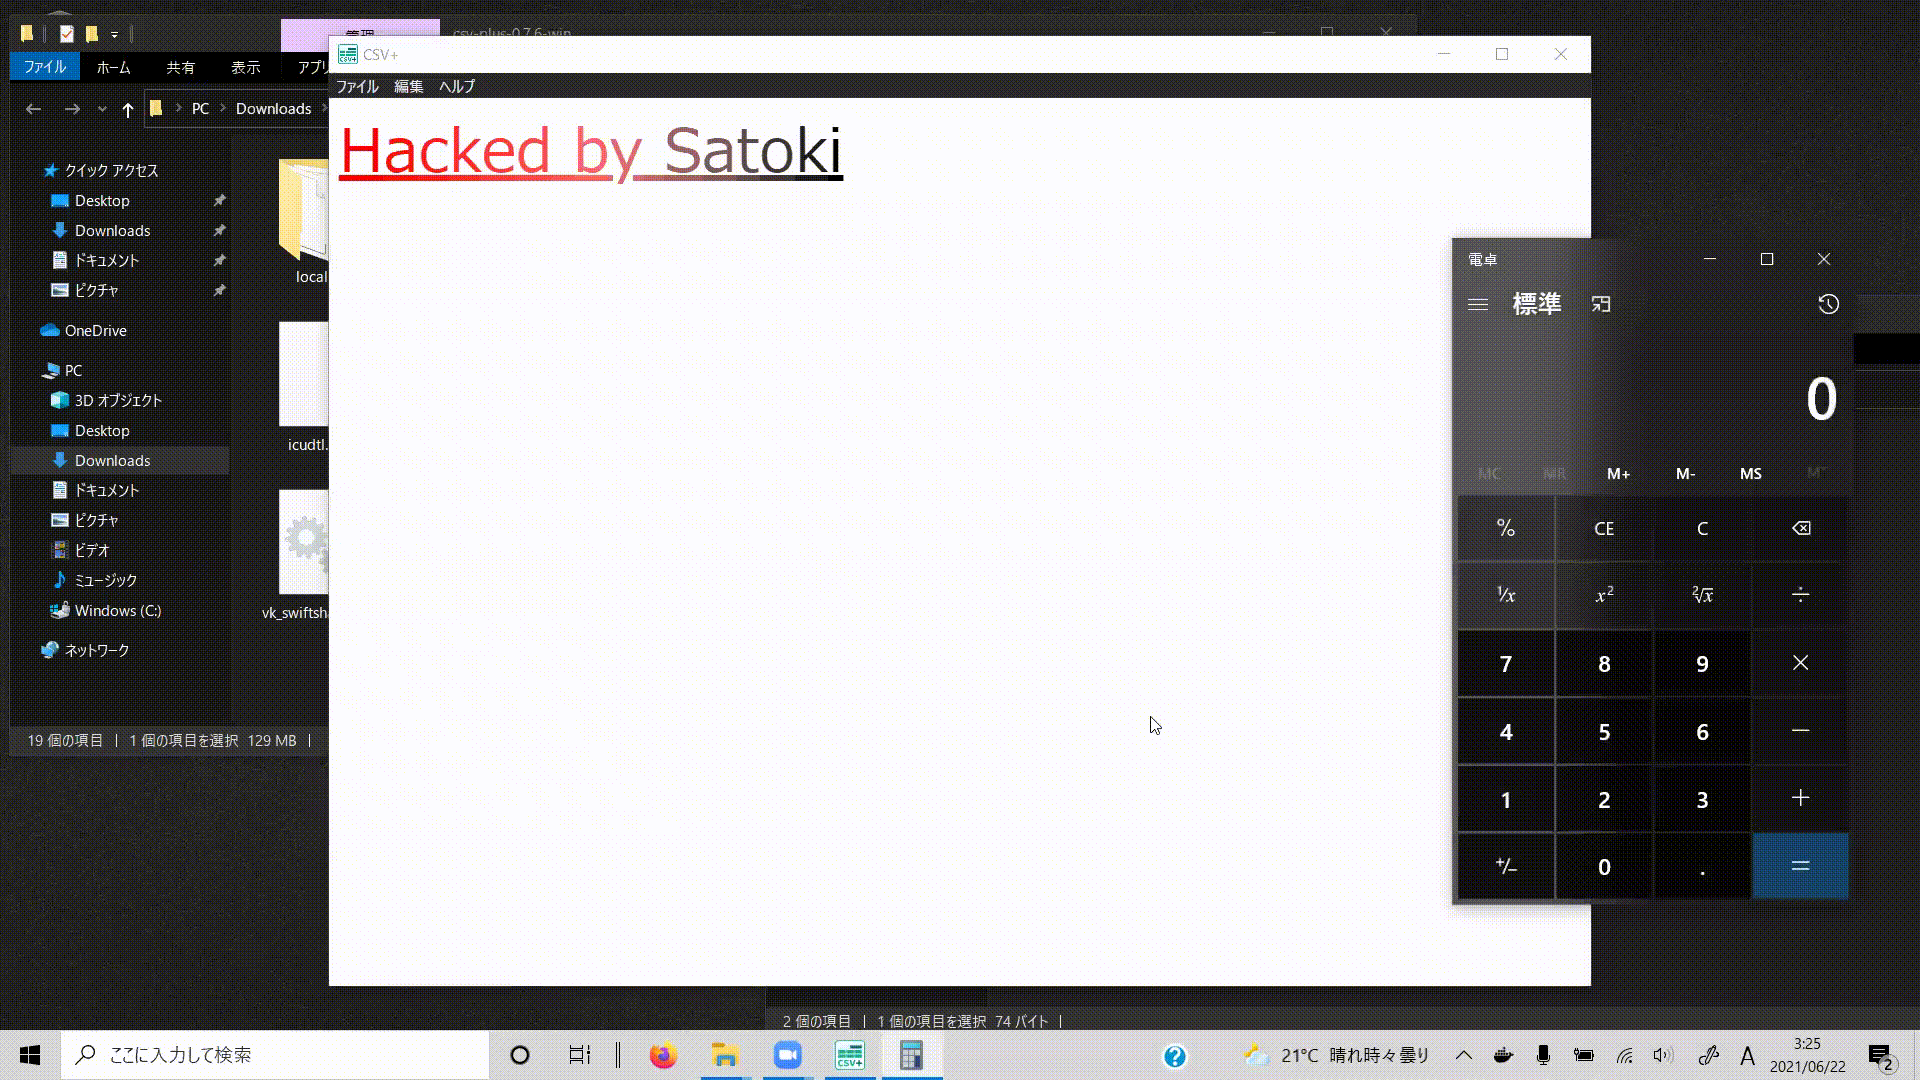 nanaao/csv-plus_vulnerability
👻 [PoC] CSV+ 0.8.0 - Arbitrary Code Execution (CVE-2022-21241)
 kai-one001/react-router-cve-2025-61686-
Detailed analysis of CVE-2025-61686, a path traversal vulnerability in React Router's file session storage, including root cause, attack scenarios,…
 rickidevs/cve-2026-26717
Technical write-up of CVE-2026-26717, an HMAC timing attack in OpenFUN Richie LMS webhook authentication, including vulnerable code, impact, and fix…
 jibaru/cve-2025-66478-github-patcher
Go-based automation tool that scans GitHub repositories for vulnerable Next.js versions (CVE-2025-66478) and automatically creates pull requests with…
 renio-wow/cve-2026-51416
Analyzes a specific CVE in WeChat OAuth handler, identifying unbounded HTTP response reads leading to denial of service, with remediation guidance.
 open-flaw/cve-2022-33171
CVE-2022-33171: TypeORM SQL Injection Vulnerability
 clemfavre/cve-2023-45612_exploit
Reproduction of a high severty security problem that allows XXE (XML eXternal Entity) attacks on Ktor's XML serialization.
 amir-malek/react-cve-2025-55182
Detects and fixes CVE-2025-55182 (React2Shell) in React Server Components and Next.js apps. Scans package versions, suggests safe upgrades, and…