
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended
 geraldoalcantara/cve-2023-50071
Multiple SQL injection vulnerabilities in /customer_support/ajax.php?action=save_department in Customer Support System 1.0 allow authenticated…
 shakun8/cve-2017-9805
CVE-2017-9805 POC
 al1ex/cve-2020-14195
This is a simple test for FasterXML jackson-databind
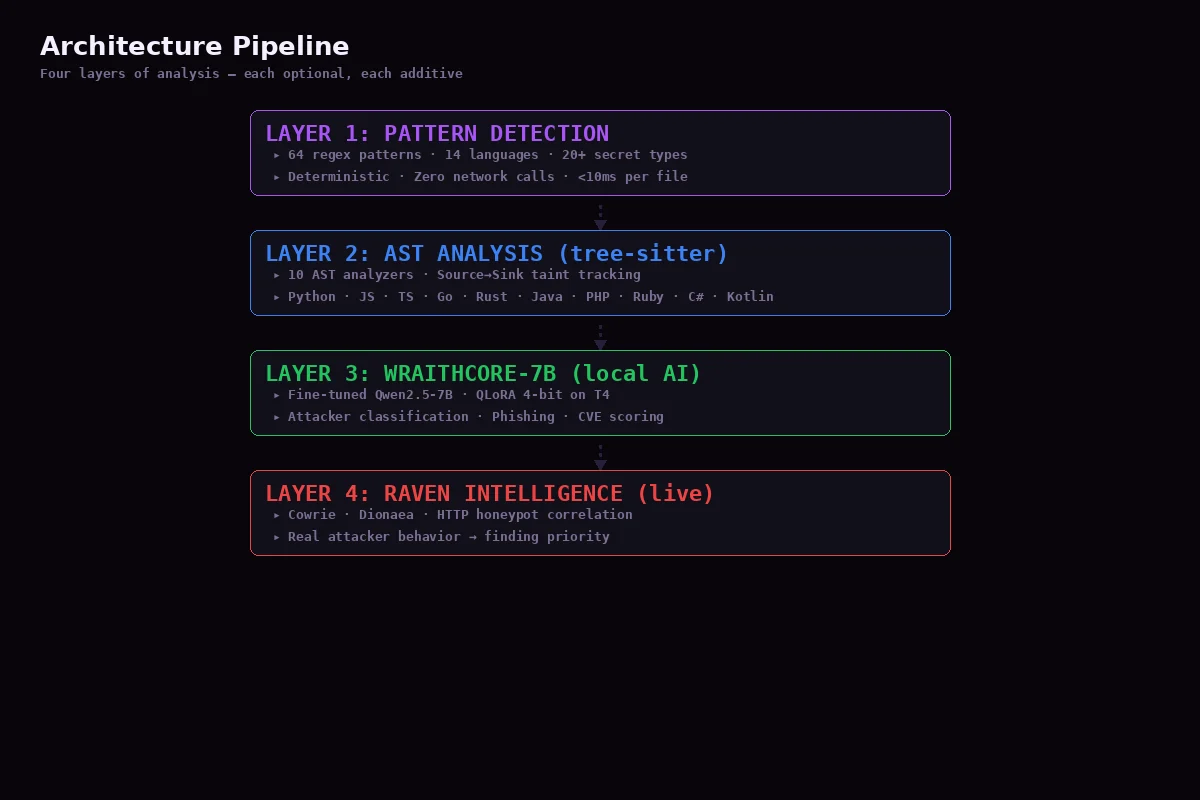 niffyhunt/codeguard-copilot
AI-powered security co-pilot that catches vulnerabilities as you code. Real-time security scanning, educational explanations, and auto fixes for…
 rh-rahulshetty/log4shell-cve-2021-44228
Deliberately vulnerable Java/Maven fixture for testing Log4Shell (CVE-2021-44228) detection, code-impact classification, and remediation guidance in…
 ridhinva/npm-tar-path-traversal-scanner
Scanner: CVE-2026-31802 npm tar path traversal — Python checker for arbitrary file write via npm pack
 josh-blythe/bordair-detector
Two-stage prompt-injection and jailbreak detector: regex gates plus a quantised DeBERTa-v3 ONNX classifier, with image, document, and audio support.…
 secoba/djvul_stringagg
Django StringAgg SQL Injection (CVE-2020-7471)
 gduma-phdata/patch-cve-2026-10520
Patch for Apache Struts OGNL injection vulnerability (CVE-2026-10520), currently in review and deployed to production.
 artwiderobo/cve-2026-13934
Structured vulnerability research repo for a Chrome Dawn WebGPU CWE-20 flaw: root cause, patch diff, static verification, severity review, and…
 theopaid/cve-2026-66753-http-header-injection-via-unvalidated-cr-and-lf-in-header-values-tiny_http-
Security Advisory: HTTP Header Injection via Unvalidated CR and LF in Header Values (tiny_http)
 csinexus/mcpshield
Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)
 fevar54/cve-2026-72530-trueconf-sandbox-escape-
Este repositorio contiene una demostración educativa de la mitigación y detección para **CVE-2026-72530**, una vulnerabilidad crítica de **Code…
 theopaid/cve-2026-66751-insufficient-access-controls-allow-for-unauthorized-room-deletion-let-s-chat-
Security Advisory: Insufficient Access Controls Allow for Unauthorized Room Deletion (Let's Chat)
 theopaid/cve-2026-66749-unchecked-room-lookup-leads-to-server-crash-let-s-chat-
Security Advisory: Unchecked Room Lookup Leads to Server Crash (Let's Chat)
 horkimhab/cve-2022-31626-cve-2024-2961-cve-2019-6977
CVE-2022-31626, CVE-2024-2961, CVE-2019-6977, PHP security research
 theopaid/cve-2026-66746-http-response-splitting-via-unvalidated-response-header-values-rouille-
Security Advisory: HTTP Response Splitting via Unvalidated Response Header Values (rouille)
 jenkinsci-cert/security-3430
Java agent that transforms a vulnerable class to block exploitation of CVE-2024-43044 in Jenkins controllers, with optional forced shutdown on…








