
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended

 dbzoo/log4j_scanner
Filesystem scanner for Log4Shell (CVE-2021-44228) and related CVEs. Detects vulnerable JAR files via hash matching and class presence. Runs…
 inettgmbh/checkmk-log4j-scanner
Checkmk extension that scans JAR, WAR, EAR, and AAR files for Log4j versions vulnerable to CVE-2021-44228 by inspecting META-INF pom.properties…
 gmh5225/antidbg-unabomber
VMP improved idea (old AmogusPlugin)
 nth347/cve-2020-28032_poc
PoC for CVE-2020-28032 (It's just a POP chain in WordPress < 5.5.2 for exploiting PHP Object Injection)
 liyuxuan504-byte/cve-2026-14266
7-Zip XZ Decoder Heap Buffer Overflow - Full analysis, root cause, PoC, and RCE exploitation roadmap
 0x-nope/cve-2019-12180
Advisory and proof of concept for CVE-2019-12180, demonstrating arbitrary Groovy code execution in SoapUI and ReadyAPI via malicious project files.
 gh-ost00/cve-2024-0195-spiderflow
CVE-2024-0195 Improper Control of Generation of Code ('Code Injection')
 aelmosalamy/cve-2024-53924
A PoC of CVE-2024-53924
 ming1700/cve-2026-38192
pluck-CMS-4.7.20-code-injection-vulnerability
 alikarimi999/cve-2021-21315
Proof-of-concept exploit for CVE-2021-21315, a command injection vulnerability in Node.js, demonstrating remote code execution.
 surajhacx/helakuruv.1.1-dllhijack
Helakuru Version 1.1 DLL Hijack - CVE-2024-48605
 rndhouse/vcamper
PoC: identify silent security patches before CVE
 hoangkien1020/cve-2021-21014
Magento versions 2.4.1 (and earlier), 2.4.0-p1 (and earlier) and 2.3.6 (and earlier) are vulnerable to a file upload restriction bypass. Successful…
 jzheaux/cve-2023-34035-mitigations
Demonstrates CVE-2023-34035 vulnerability in Spring Security with vulnerable and mitigated sample applications, teaching proper servlet mapping and…
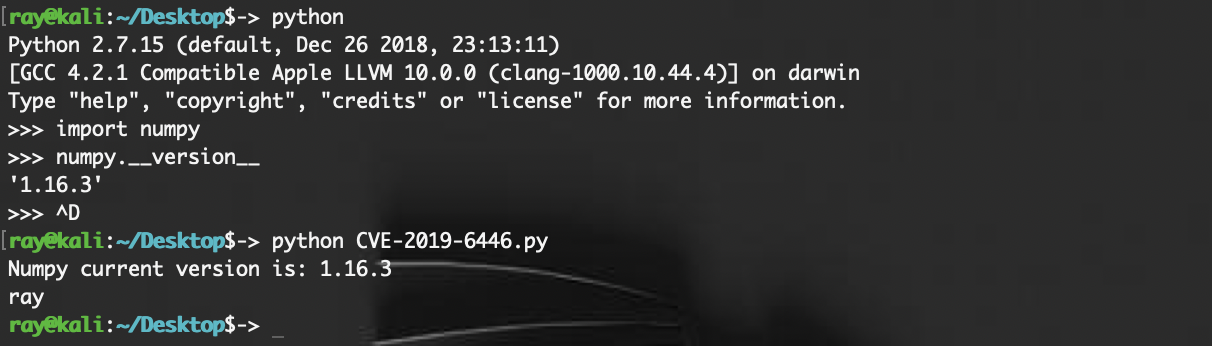 rayscri/cve-2019-6446
Numpy deserialization command execution
 viszsec/cve-2024-23897
Jenkins POC of Arbitrary file read vulnerability through the CLI can lead to RCE
 yuriisanin/cve-2022-45771
[PoC] Privilege escalation & code execution via LFI in PwnDoC
 p33d/cve-2024-9441
Exploit for CVE-2024-9441: Remote Code Execution via improper input sanitization in PHP forgot-password functionality. Uploads a malicious script and…








