
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended

 pycqa/bandit
Bandit is a tool designed to find common security issues in Python code.
 presidentbeef/brakeman
A static analysis security vulnerability scanner for Ruby on Rails applications
 crytic/slither
Static Analyzer for Solidity and Vyper
 lintsinghua/deepaudit
DeepAudit:人人拥有的 AI 黑客战队,让漏洞挖掘触手可及。国内首个开源的代码漏洞挖掘多智能体系统。小白一键部署运行,自主协作审计 + 自动化沙箱 PoC 验证。支持 Ollama 私有部署 ,一键生成报告。支持中转站。让安全不再昂贵,让审计不再复杂。

 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 pmd/pmd
An extensible multilanguage static code analyzer.
 pydantic/monty
A secure Python sandbox, written in Rust, for code written by AI.
 ossf/scorecard
OpenSSF Scorecard - Security health metrics for Open Source
 snyk/cli
Snyk CLI scans and monitors your projects for security vulnerabilities.
 awslabs/git-secrets
Prevents you from committing secrets and credentials into git repositories
 lirantal/awesome-nodejs-security
Curated directory of Node.js security tools, static analyzers, vulnerability scanners, and educational resources covering OWASP Top 10, supply chain…
 owasp/asvs
Application Security Verification Standard
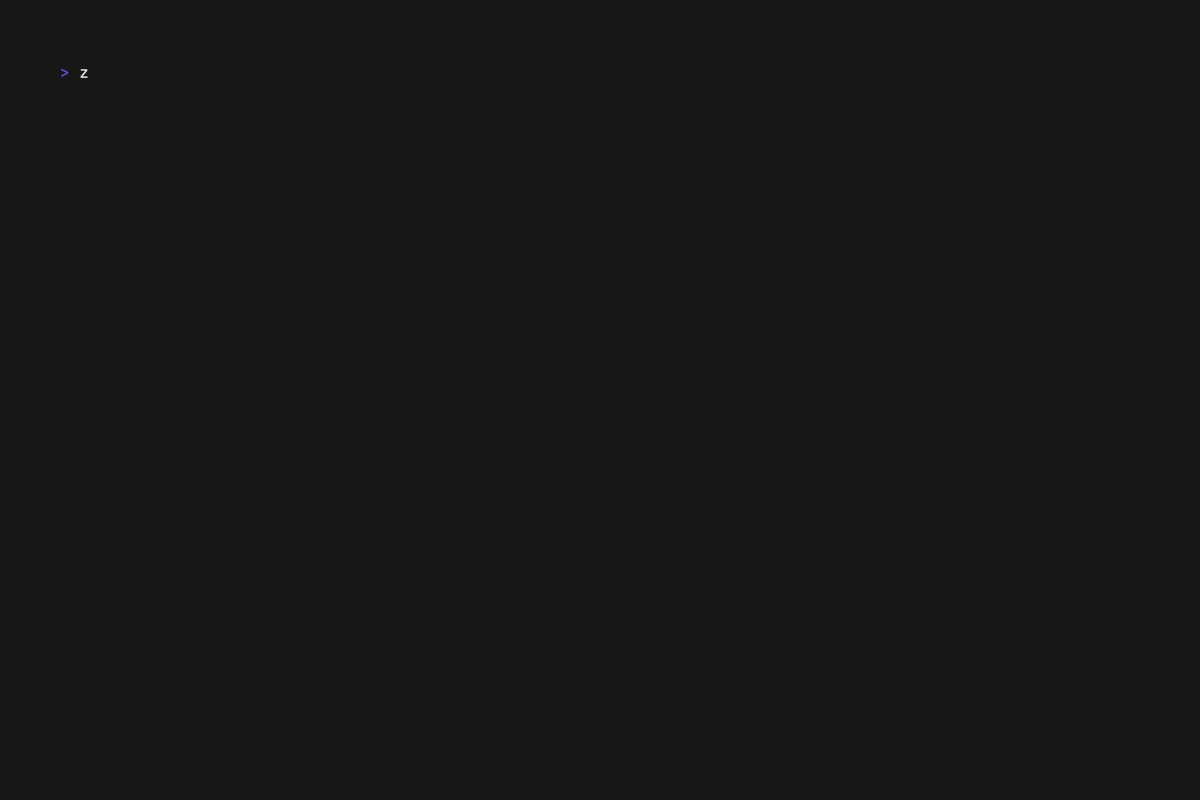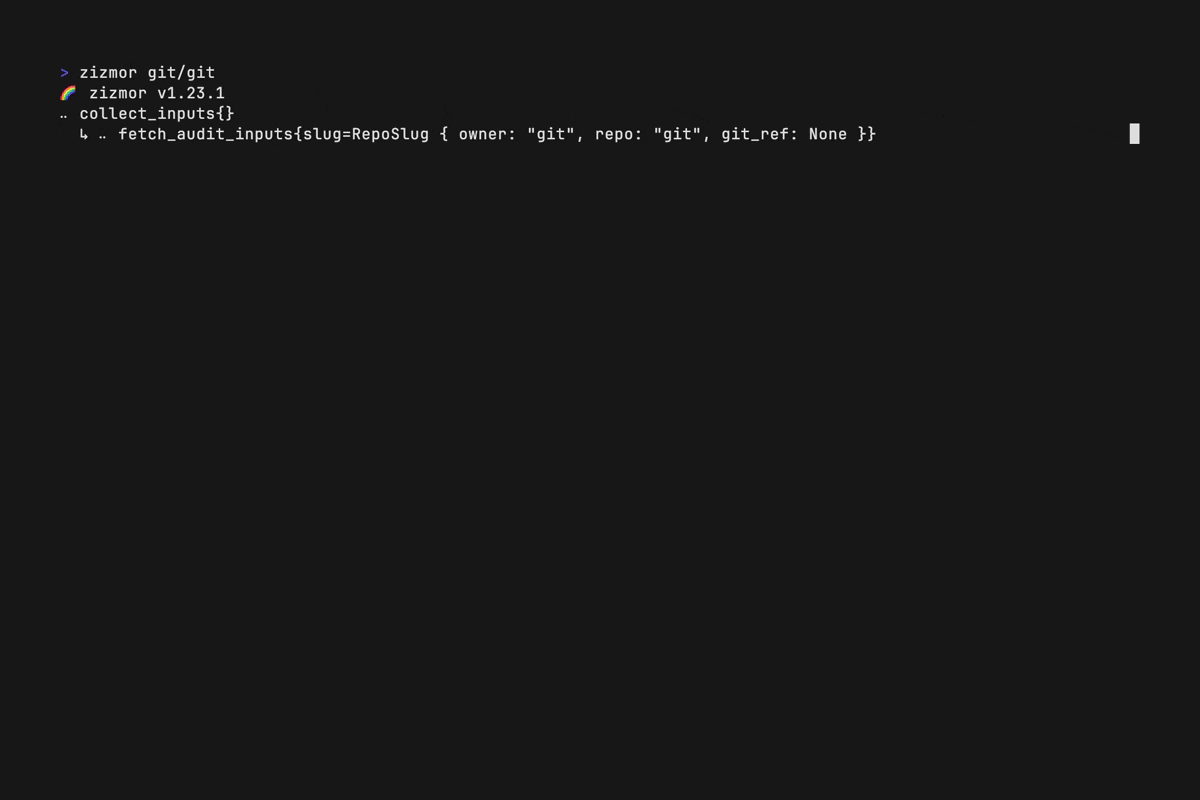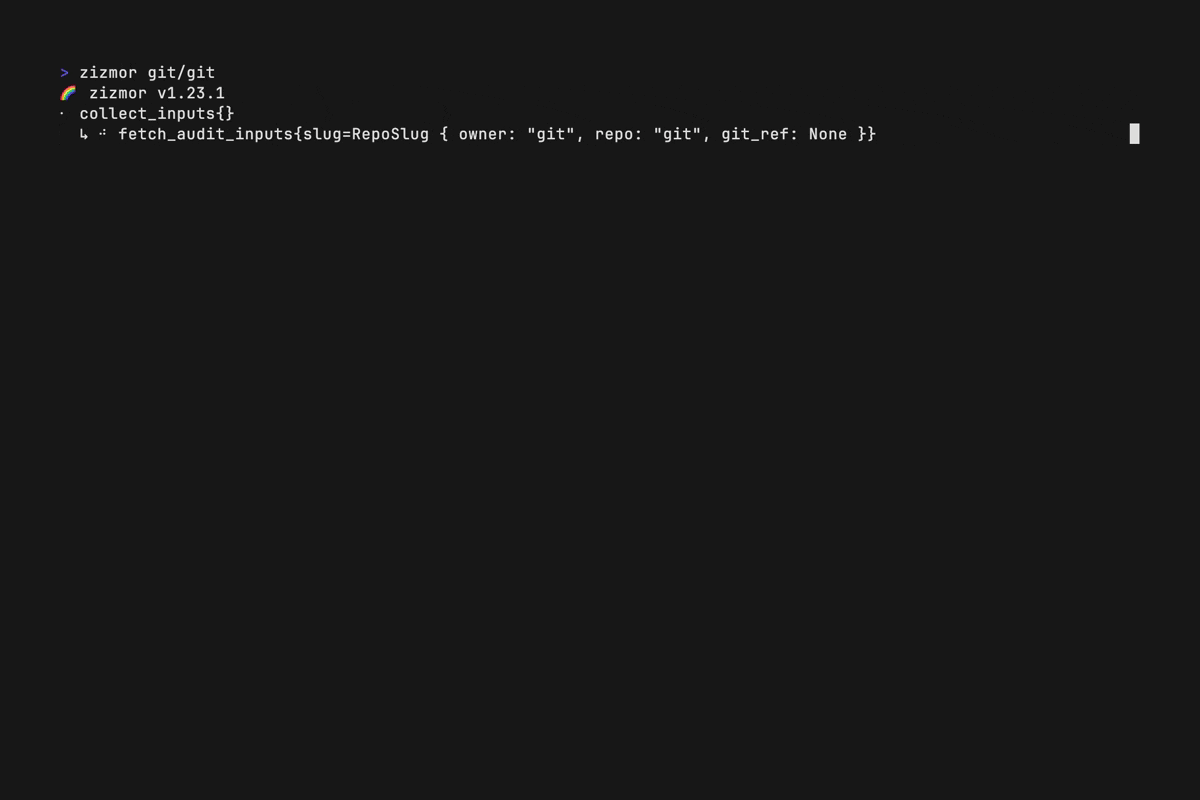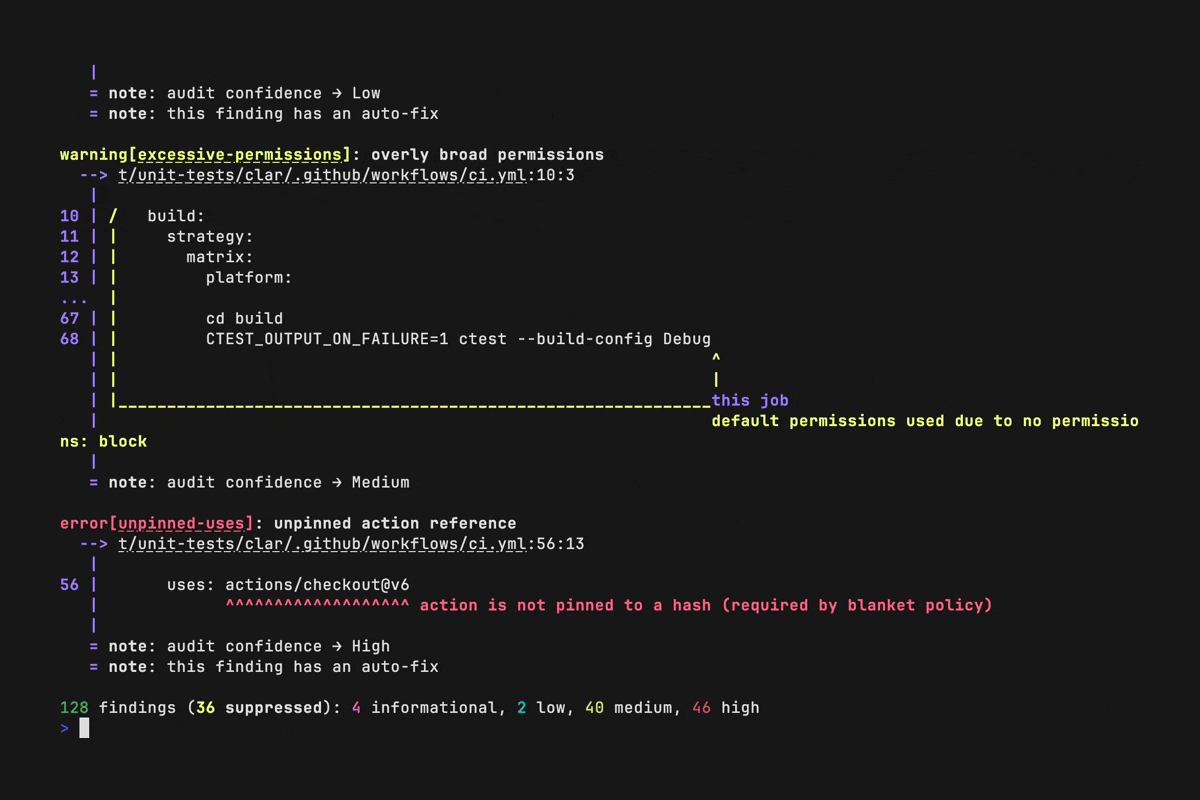 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
 burrowers/garble
Obfuscates Go builds by wrapping the Go toolchain, replacing identifiers, package paths, and position data with hashes and stripping debug and build…
 anthropics/oss-scanner
Service that builds enrolled open-source repositories in isolated offline VMs and scans them for security vulnerabilities, emailing findings with…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…





