
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended

 joernio/joern
Open-source code analysis platform for C/C++/Java/Binary/Javascript/Python/Kotlin based on code property graphs. Discord https://discord.gg/vv4MH284Hc
 nolabs-ai/nono
agent runtime security - zero trust, zero setup, zero latency agent sandboxing
 semgrep/semgrep-rules
Static analysis rule pack for detecting security vulnerabilities, dangerous code patterns, and configuration issues across many languages; integrates…
 ezyang/htmlpurifier
Standards compliant HTML filter written in PHP
 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…
 c2sp/wycheproof
Project Wycheproof tests crypto libraries against known attacks.
 revng/revng
Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
 snyk/agent-scan
Security scanner for AI agents, MCP servers and agent skills.
 aquasecurity/tfsec
Tfsec is now part of Trivy
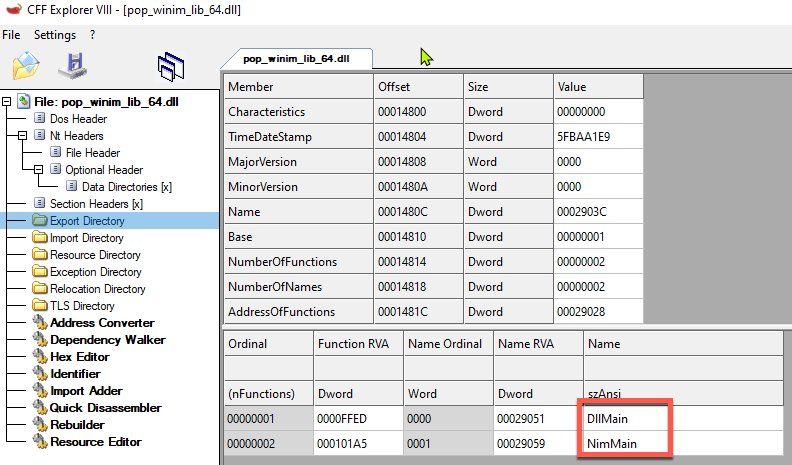 byt3bl33d3r/offensivenim
My experiments in weaponizing Nim (https://nim-lang.org/)
 patriksimek/vm2
Isolated JavaScript sandbox for Node.js that runs untrusted code with restricted access to built-in modules and host resources via Proxy-based…
 dman95/sasm
SASM - simple crossplatform IDE for NASM, MASM, GAS and FASM assembly languages
 huhusmang/awesome-llms-for-vulnerability-detection
The community's most comprehensive, continuously-updated index of research on Large Language Models for software vulnerability detection — papers…
 yelp/detect-secrets
An enterprise friendly way of detecting and preventing secrets in code.
 zinja-coder/jadx-ai-mcp
Plugin for JADX to integrate MCP server
 cisco-ai-defense/skill-scanner
Security Scanner for Agent Skills








