
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended

 githubsecuritylab/seclab-taskflows-fuzzing
An LLM-driven fuzzing pipeline powered by the GitHub Security Lab Taskflow Agent
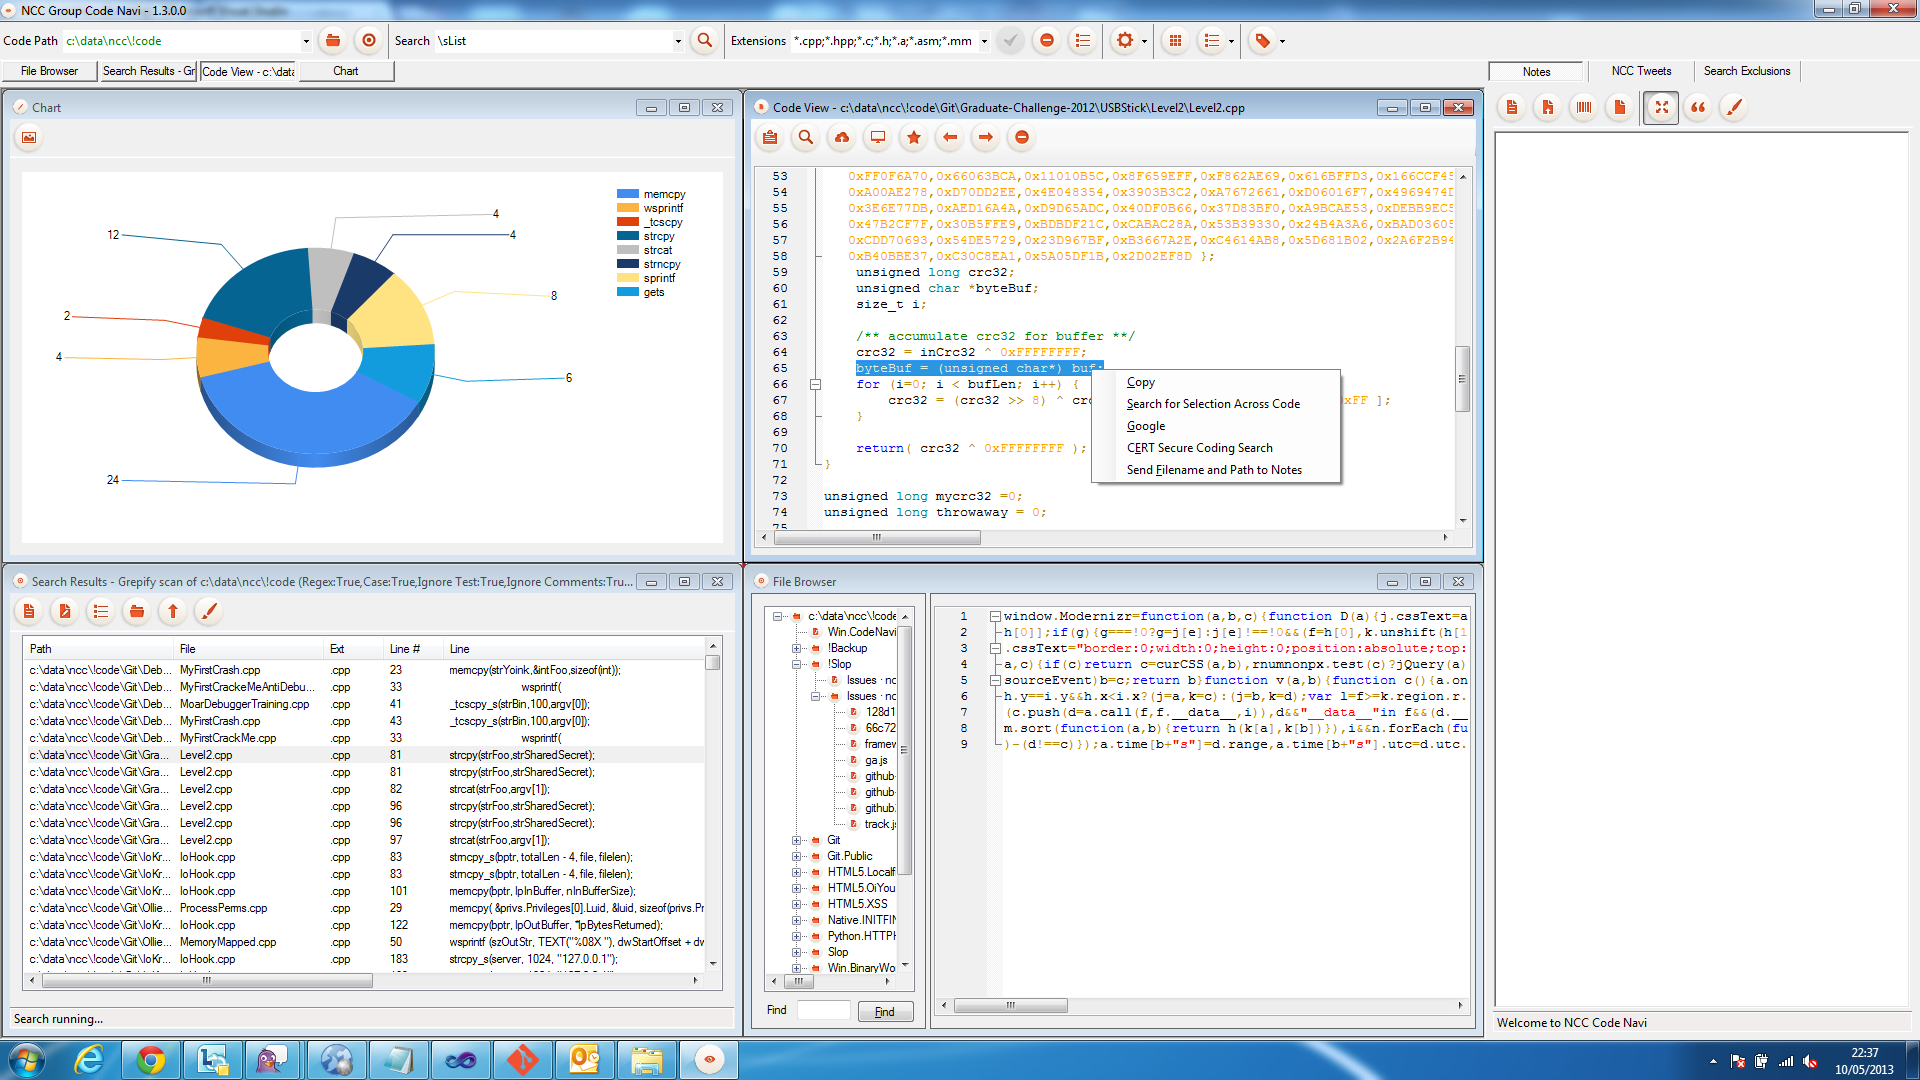 nccgroup/ncccodenavi
NCC Code Navigator
 atmoner/githubfind3r
Command-line tool for fast searching of GitHub repositories, users, and commits to gather open-source intelligence and code-related information.
 blackvectorops/semantic_firewall
Generate deterministic semantic fingerprints for Go functions. Detect xz-style backdoors and verify semantic equivalence using Static Single…
 zydak/leetobfuscator
Obfuscates C/C++ through LLVM passes: string encryption, control-flow flattening, MBA rewriting, and anti-analysis to defeat reverse engineering.
 jra89/cve-2019-19634
This is a filter bypass exploit that results in arbitrary file upload and remote code execution in class.upload.php <= 2.0.4
 neuralprogram/qlcoder
Agentic Framework for Synthesizing CodeQL Queries
 yaklang/javajive
Pure-Go Java Decompiler and Serialization Operator
 vigiloss/vigil
AI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…
 runreveal/sigmalite
Go library for parsing and executing Sigma detection rules against log entries, supporting field modifiers, CIDR matching, and custom field resolvers…
 nccgroup/icpin
An Integrity-Check Monitoring Pintool
 brianwrf/cve-2018-11788
Apache Karaf XXE Vulnerability (CVE-2018-11788)
 owasp/secure-coding-practices-quick-reference-guide
The Secure Coding Practices Quick-reference Guide from OWASP
 n7on/dllspy
Discover input surfaces and security issues in compiled .NET assemblies — without running them.
 hazcod/claudleak
Hunt for AI coding artifacts containing secrets.
 mustafabilgici/sucoshscanny
"Sucosh" is an automated Source Code vulnerability scanner and assessment framework for Python(Flask-Django) & NodeJs capable of performing code…
 zypherion-technologies/unconfuserex
A ConfuserEx2 deobfuscator with support for anti tamper, compressor, constants, control flow, and resource recovery.
 ga1ois/blackhat-europe-2022
Select Bugs From Binary Where Pattern Like CVE-1337-Days








