
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended
 preflightsh/preflight
Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…
 arsbr/veritensor
The Anti-Virus for AI Artifacts & RAG Firewall. A static analysis tool scanning Models and Notebooks for RCE, Datasets and RAG docs for Data…
 nccgroup/cq
Fast code security scanner designed for manual security code review by experts. Outputs line-referenced findings to text files for easy filtering and…
 binsec/xyntia
Xyntia, the black-box deobfuscator
 llvmparty/striga
Experimental x86-64 to LLVM IR lifter in Python that translates machine code into analyzable IR for reverse engineering, optimization, and VM handler…
 owasp/agent-security-regression-harness
Executable security regression testing for agentic applications and MCP-integrated systems.
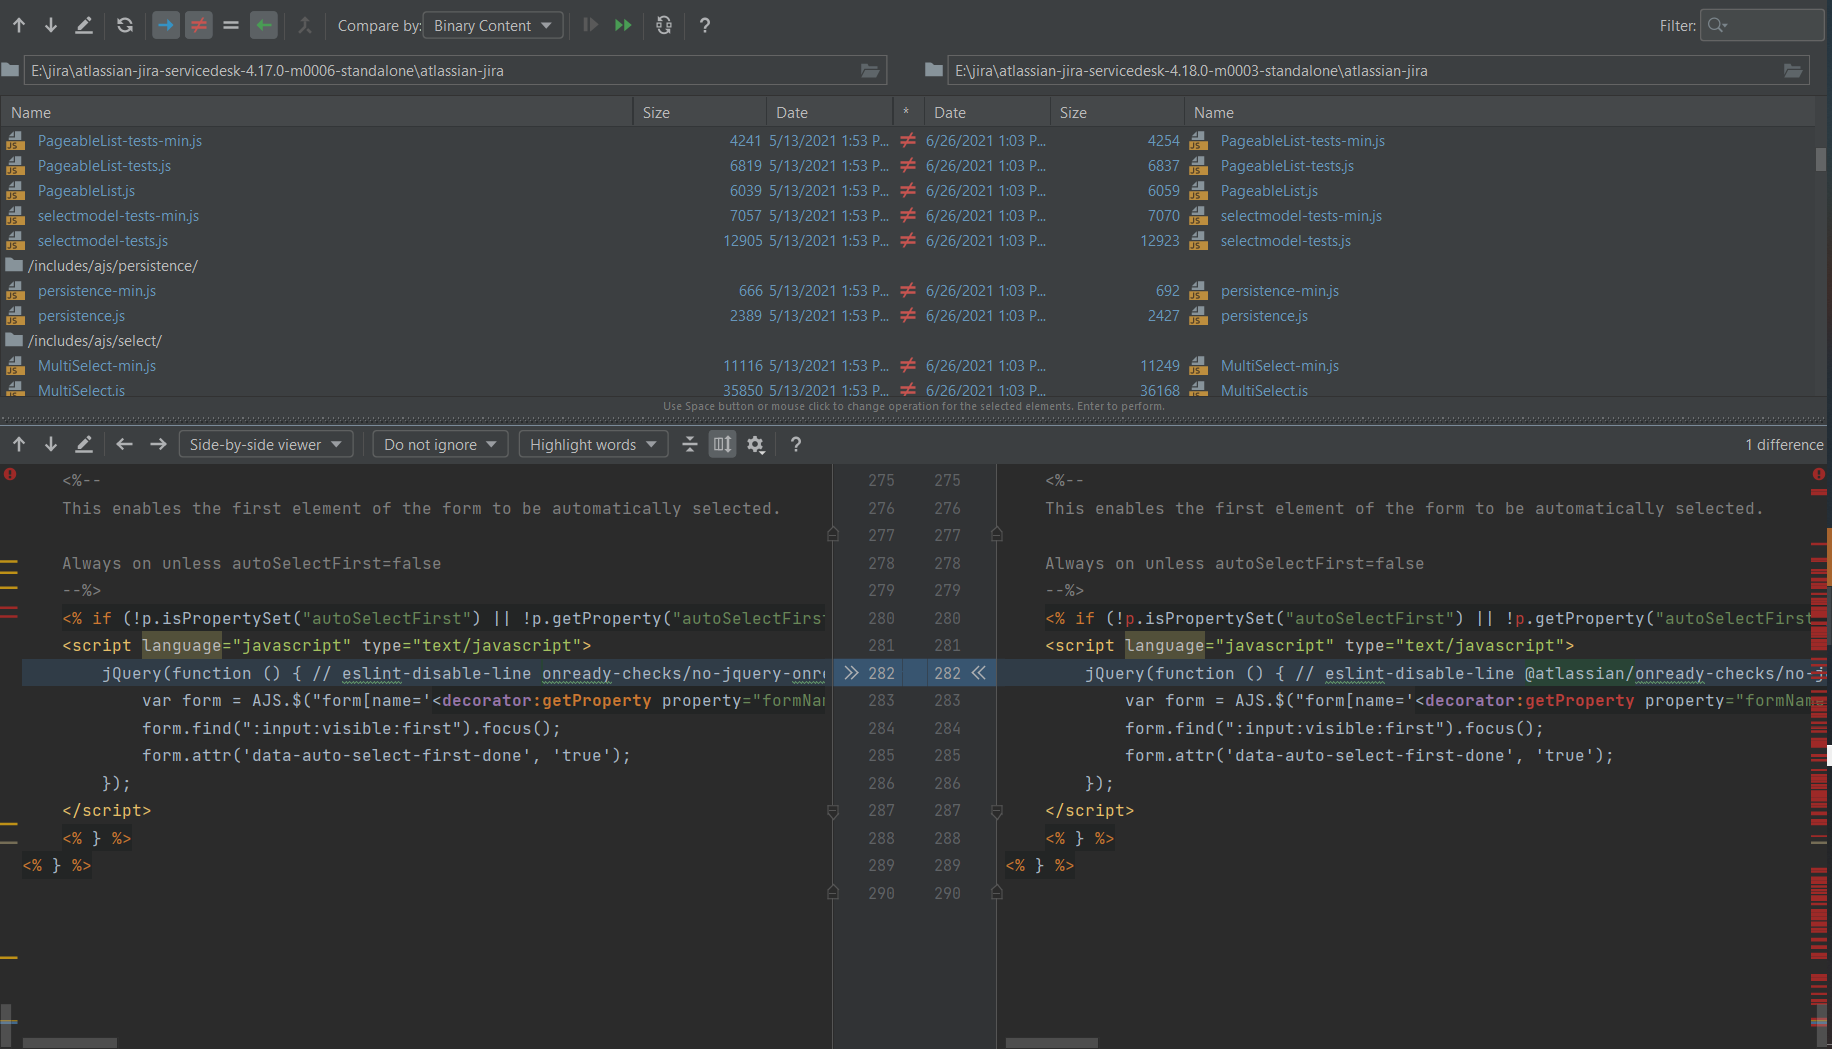 petrusviet/cve-2021-39115
Template Injection in Email Templates leads to code execution on Jira Service Management Server
 momenbasel/vulnhawk
AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.
 jas502n/jackson-cve-2020-8840
FasterXML/jackson-databind 远程代码执行漏洞
 brianwrf/wordpress_4.9.8_rce_poc
A simple PoC for WordPress RCE (author priviledge), refer to CVE-2019-8942 and CVE-2019-8943.
 owasp/cwe-tool
A command line CWE discovery tool based on OWASP / CAPSEC database of Common Weakness Enumeration.
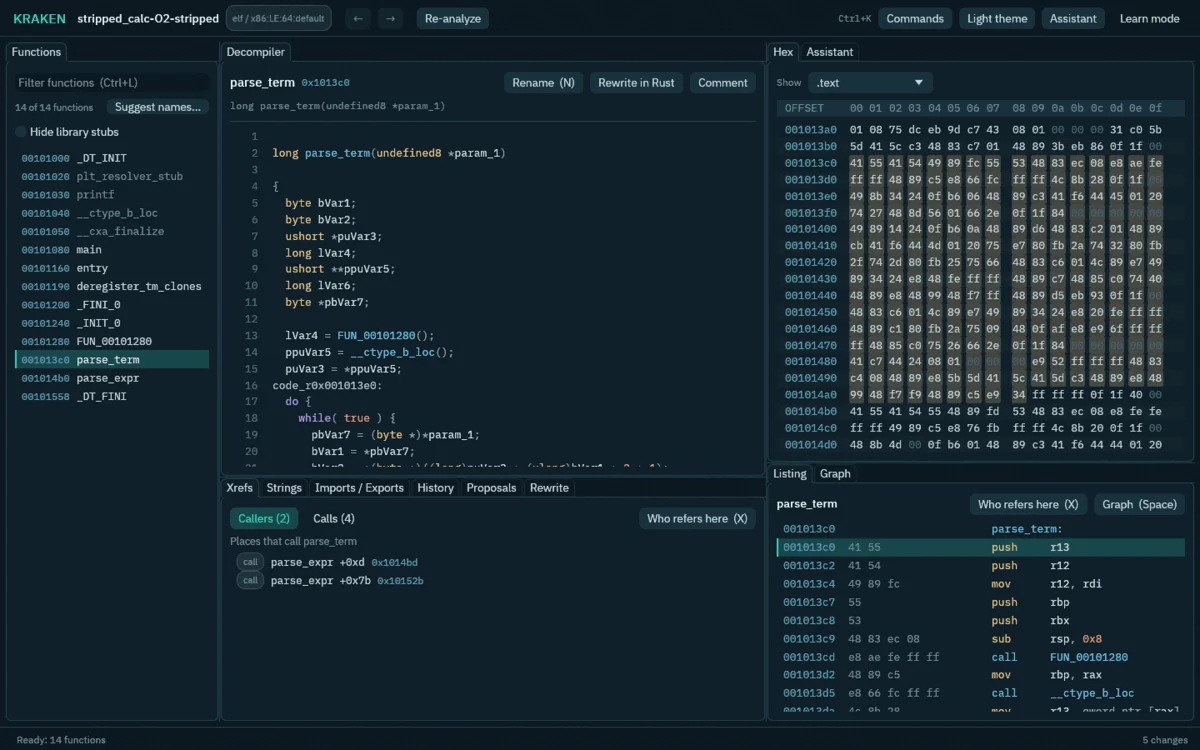 adam-atlassoftware/kraken
Reverse-engineering workbench built on Ghidra's decompiler with a native Java-free engine, AI-assisted function analysis, byte patching, sandboxed…
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
 marven11/cve-2024-28397-js2py-sandbox-escape
CVE-2024-28397: js2py sandbox escape, bypass pyimport restriction.
 pelock/jobfuscator
Obfuscates Java source code to protect against reverse engineering, decompilation, and IP theft. Renames variables/methods, encrypts strings, and…
 nightwatchcybersecurity/gitbleed_tools
Shell scripts to clone and mirror Git repositories, compute deltas, and run gitleaks to detect secrets hidden in deleted or reset commits.
 y4sec-team/cve-2023-21939
JDK CVE-2023-21939
 sqlsure/sqlsure
Semantic inspector for SQL — catches fan-out double-counting, additivity violations, wrong join keys, and policy breaches before the query runs.…








