#1
 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 trailofbits/testing-handbook
Trail of Bits Testing Handbook - appsec.guide
 kudelskisecurity/chainoffools
Proof-of-concept exploit for CVE-2020-0601 Windows CryptoAPI spoofing vulnerability, demonstrating rogue CA certificate generation using elliptic…
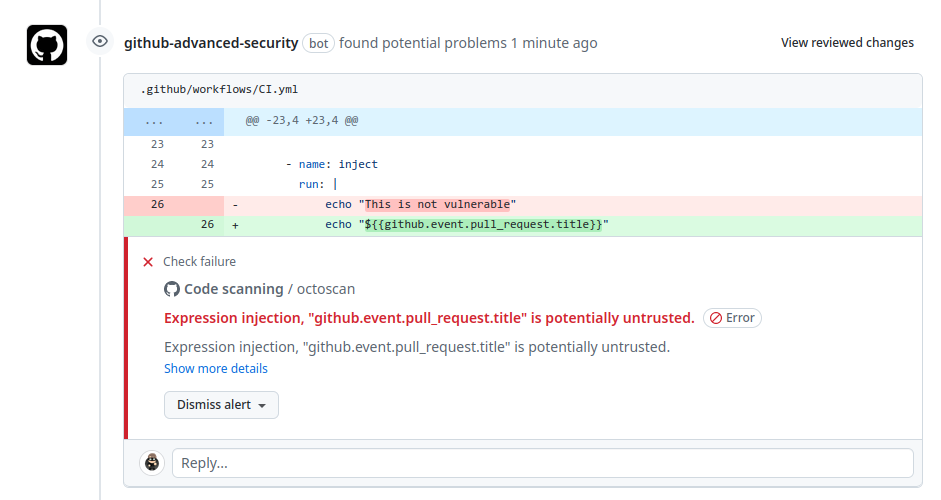 synacktiv/octoscan
Octoscan is a static vulnerability scanner for GitHub action workflows.
 sslmate/go-pkcs12
Go library for encoding and decoding PKCS#12 files
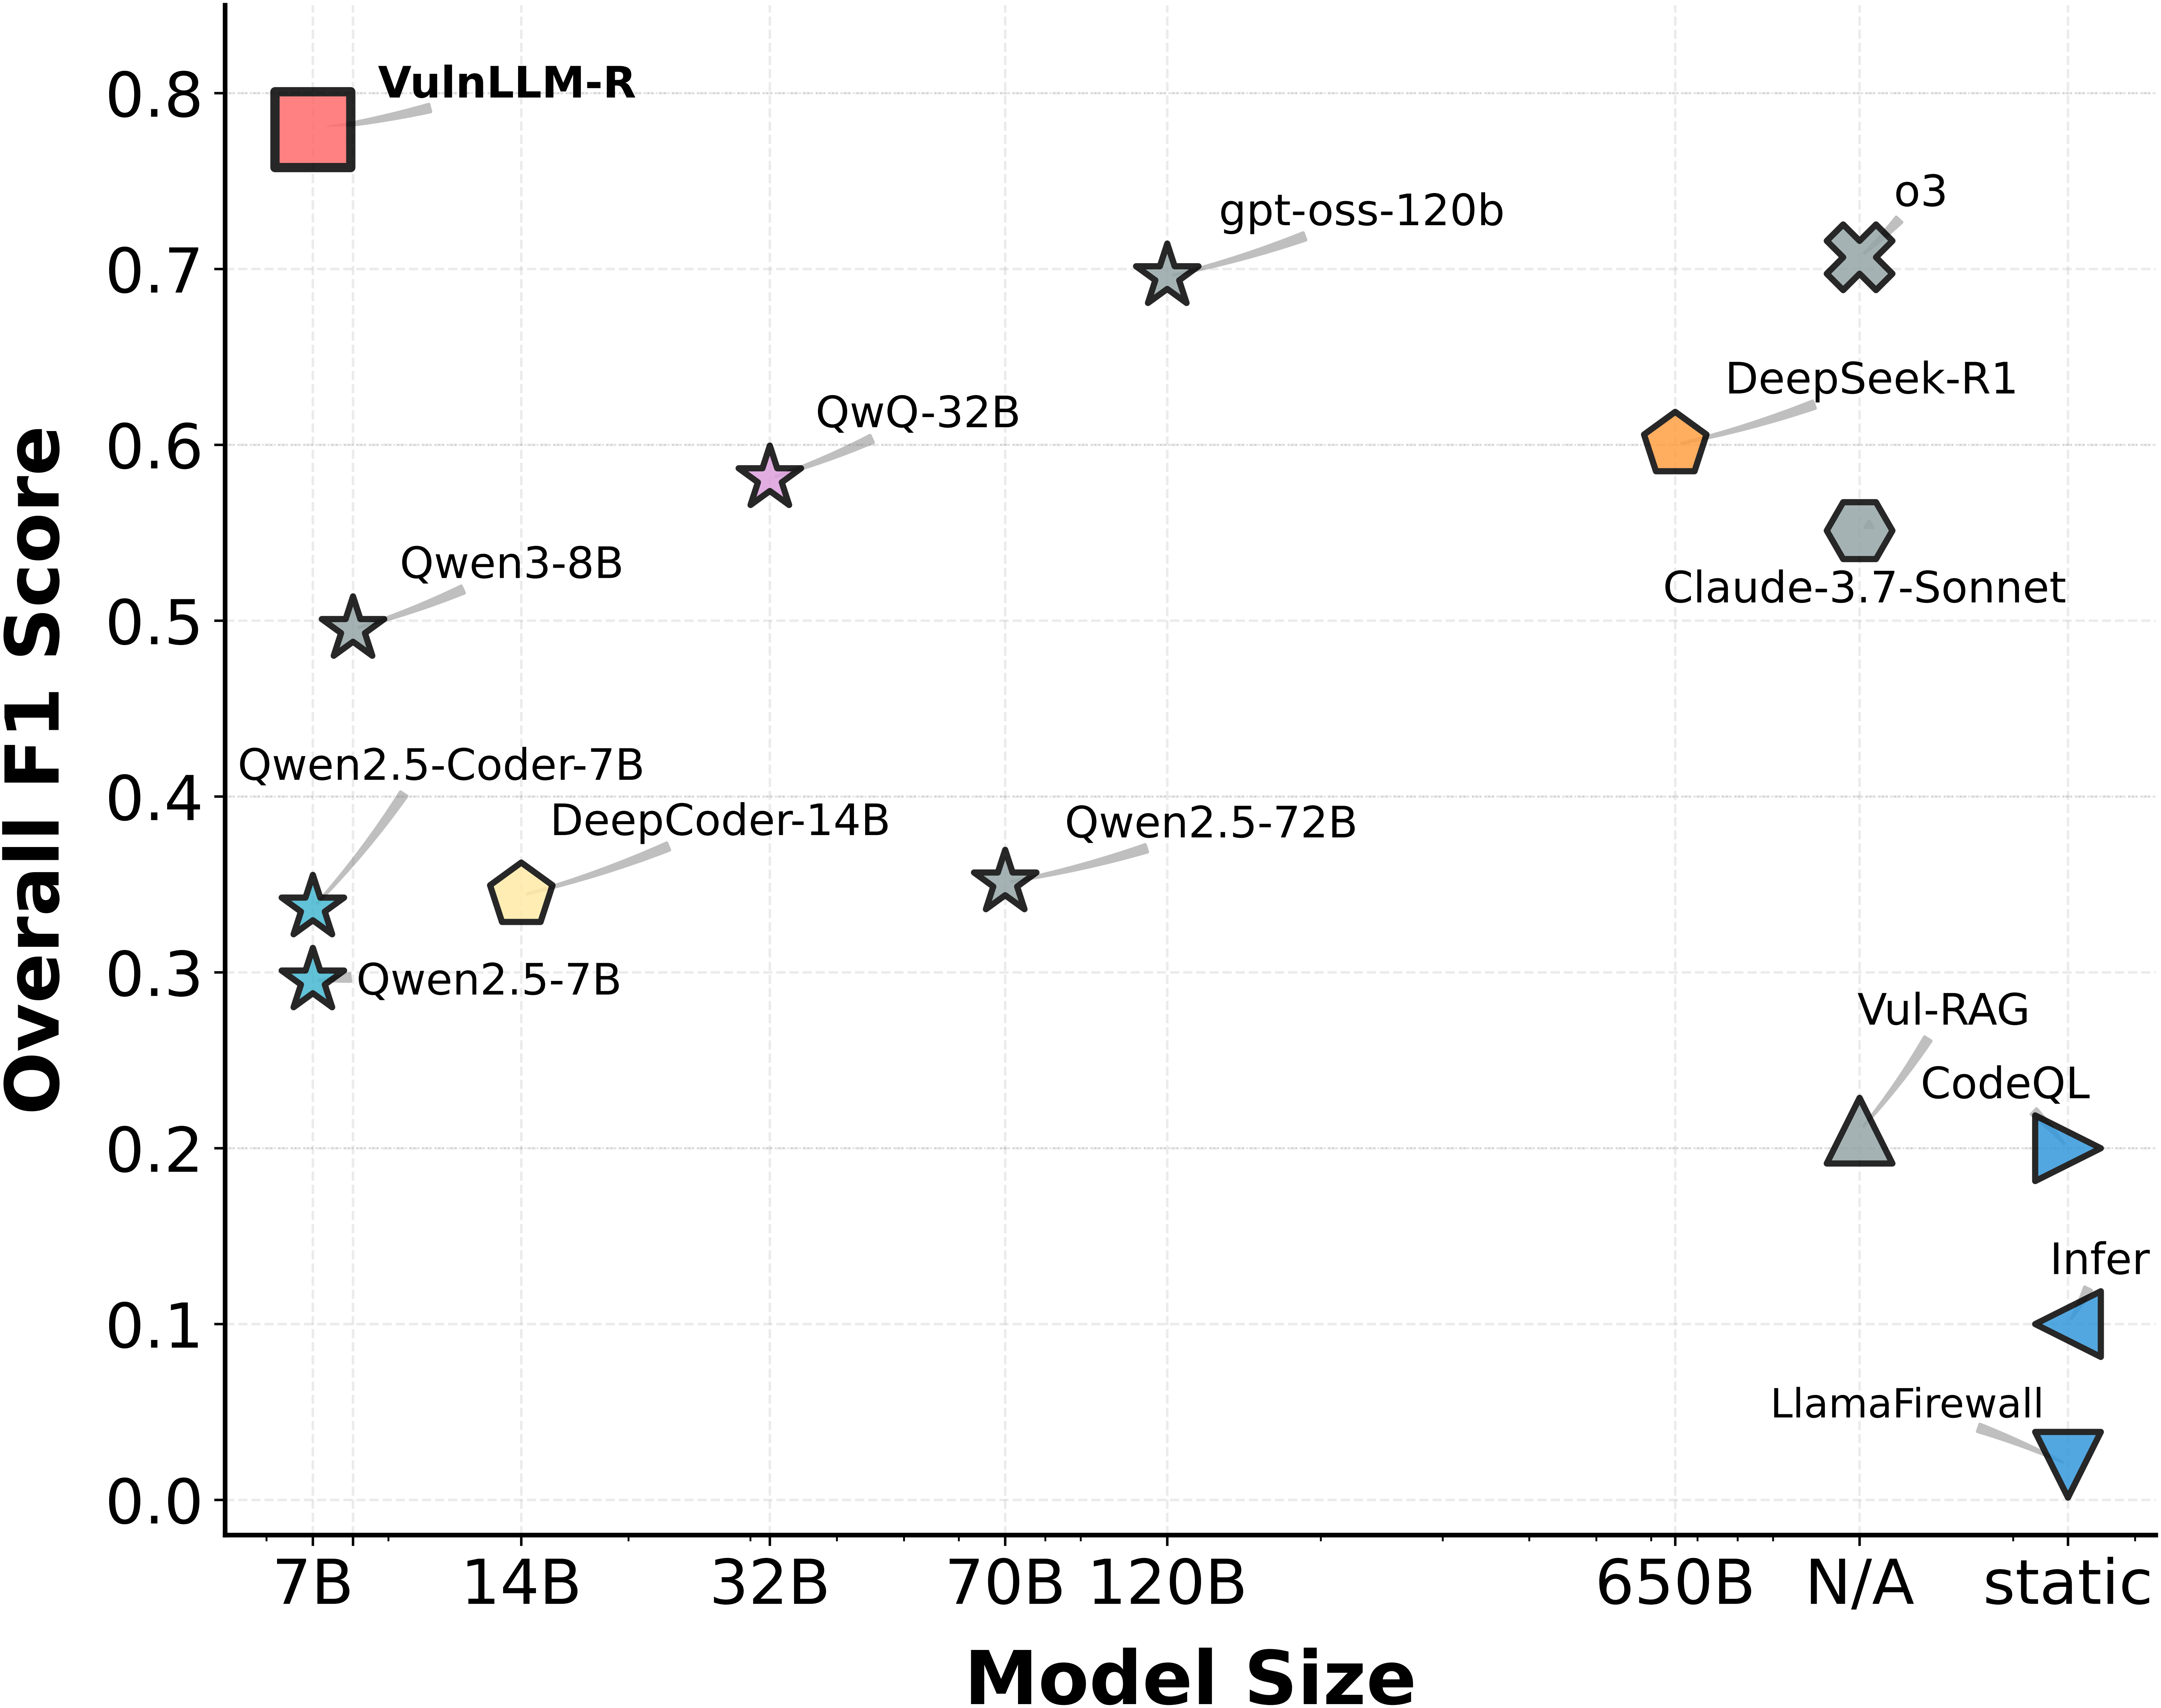 ucsb-mlsec/vulnllm-r
Specialized reasoning LLM for source-code vulnerability detection in C/C++ and Python, with dataset construction, SFT/DPO training, and…
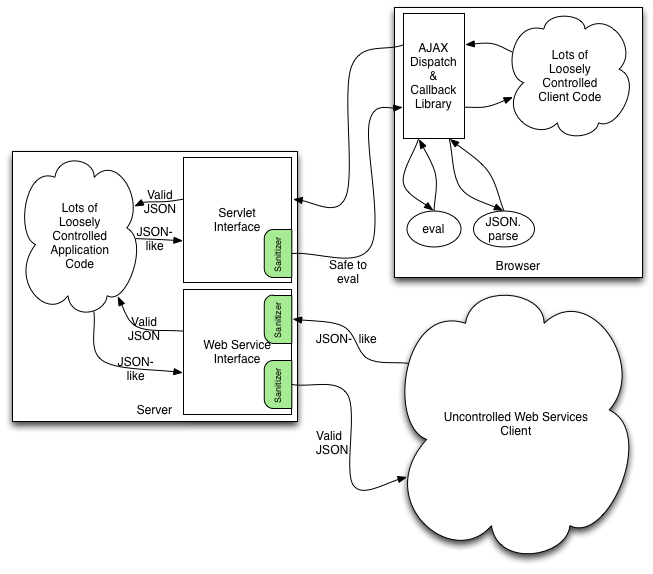 owasp/json-sanitizer
Given JSON-like content, The JSON Sanitizer converts it to valid JSON.
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
 jjyg/metasm
This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby
 corgea/sighthound
Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…
 fox-it/log4j-finder
Find vulnerable Log4j2 versions on disk and also inside Java Archive Files (Log4Shell CVE-2021-44228, CVE-2021-45046, CVE-2021-45105)
 check-spelling/check-spelling
Spelling checker action to check spelling in repositories / pull requests / commits
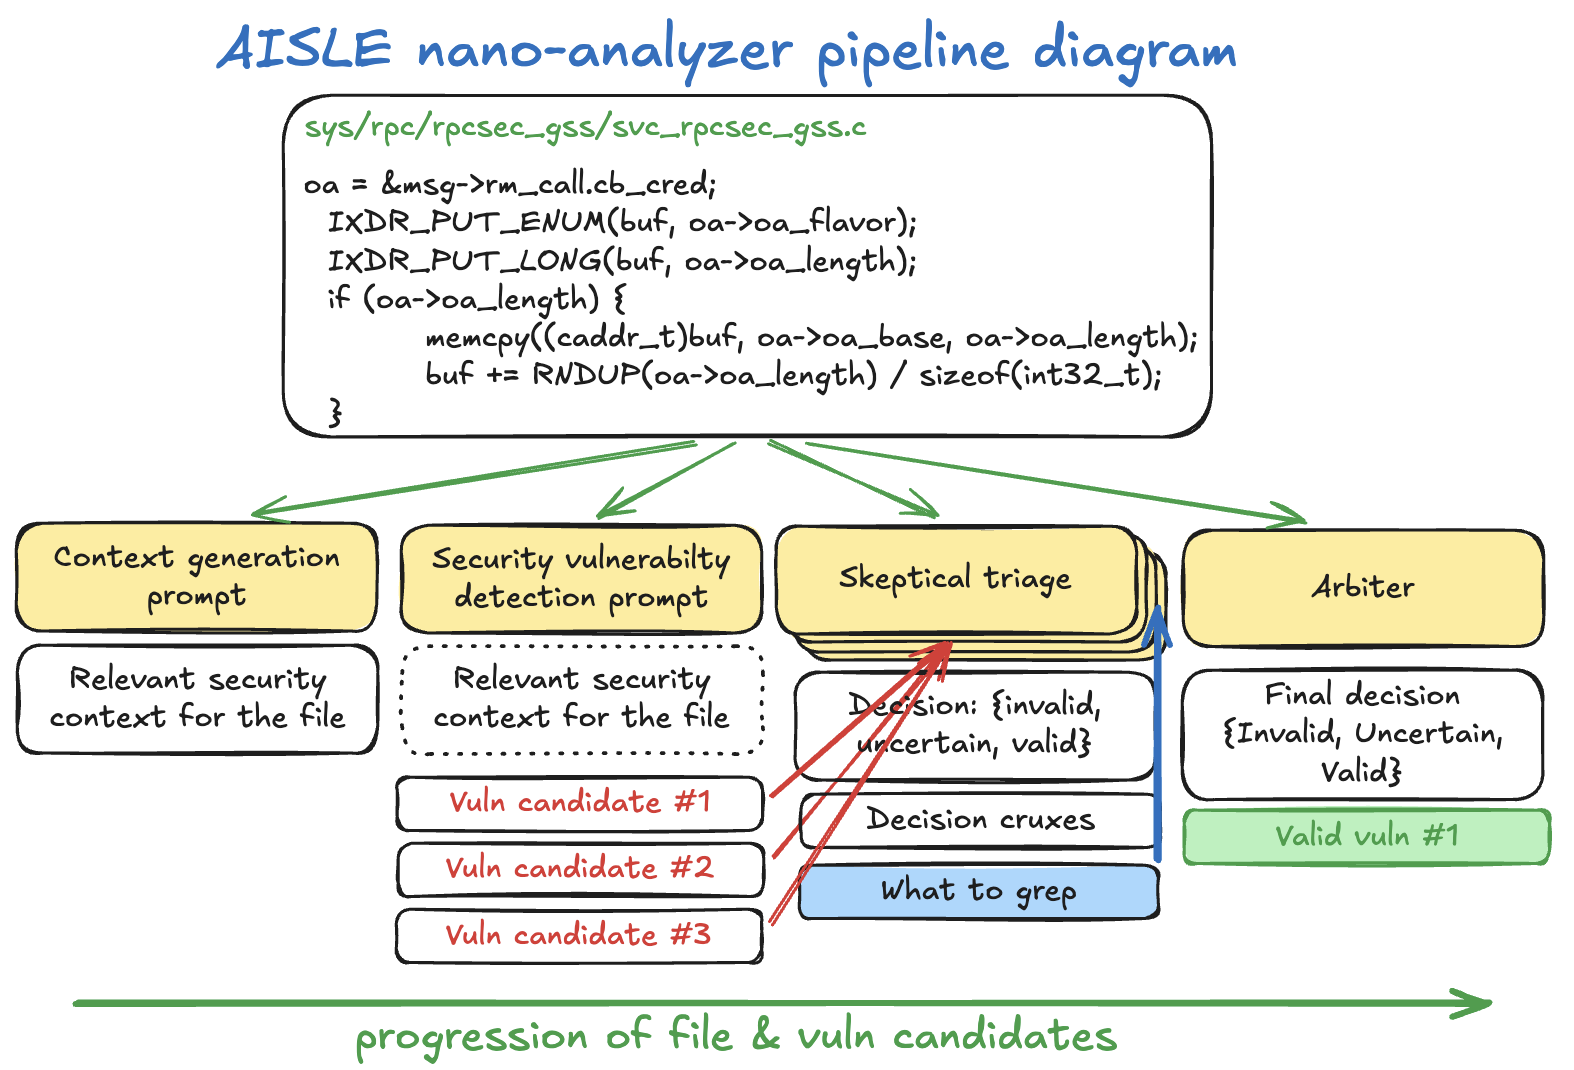 weareaisle/nano-analyzer
A minimal LLM-powered zero-day vulnerability scanner by AISLE.
 adamyordan/cve-2019-1003000-jenkins-rce-poc
Jenkins RCE Proof-of-Concept: SECURITY-1266 / CVE-2019-1003000 (Script Security), CVE-2019-1003001 (Pipeline: Groovy), CVE-2019-1003002 (Pipeline:…
 radicle-dev/heartwood
Peer-to-peer code collaboration and publishing stack with a secure, decentralized protocol, CLI tool, and network daemon for sovereign code forges.
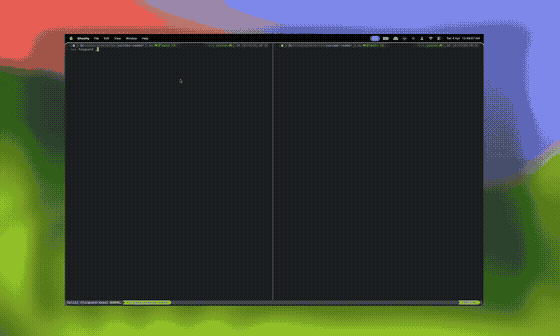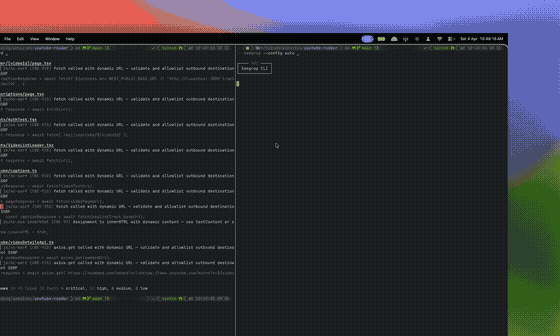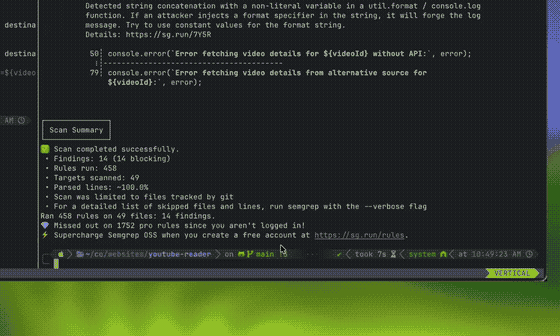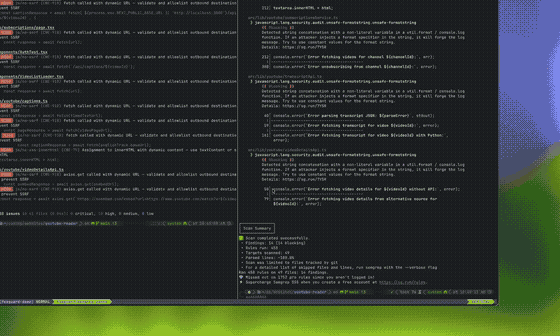 0sec-labs/foxguard
A fast universal code security scanner, written in Rust. Batteries included: supports 14 languages, TUI for triage, secrets, post-quantum audits,…
 makenowjust-labs/recheck
Static analysis tool for detecting ReDoS (Regular Expression Denial of Service) vulnerabilities in JavaScript and Scala codebases, providing…