
 #1
Tools for assessing, testing, and securing cloud environments (AWS, Azure, GCP) and their services.
Kitploit recommended

 greatscott/enject
enject: Hide .env secrets from prAIng eyes: secrets live in local encrypted stores (per project) and are injected directly into apps at runtime,…
 kstenerud/yoloai
Your agent is a security risk, so treat it like one. yoloAI does AI agent sandboxing right.
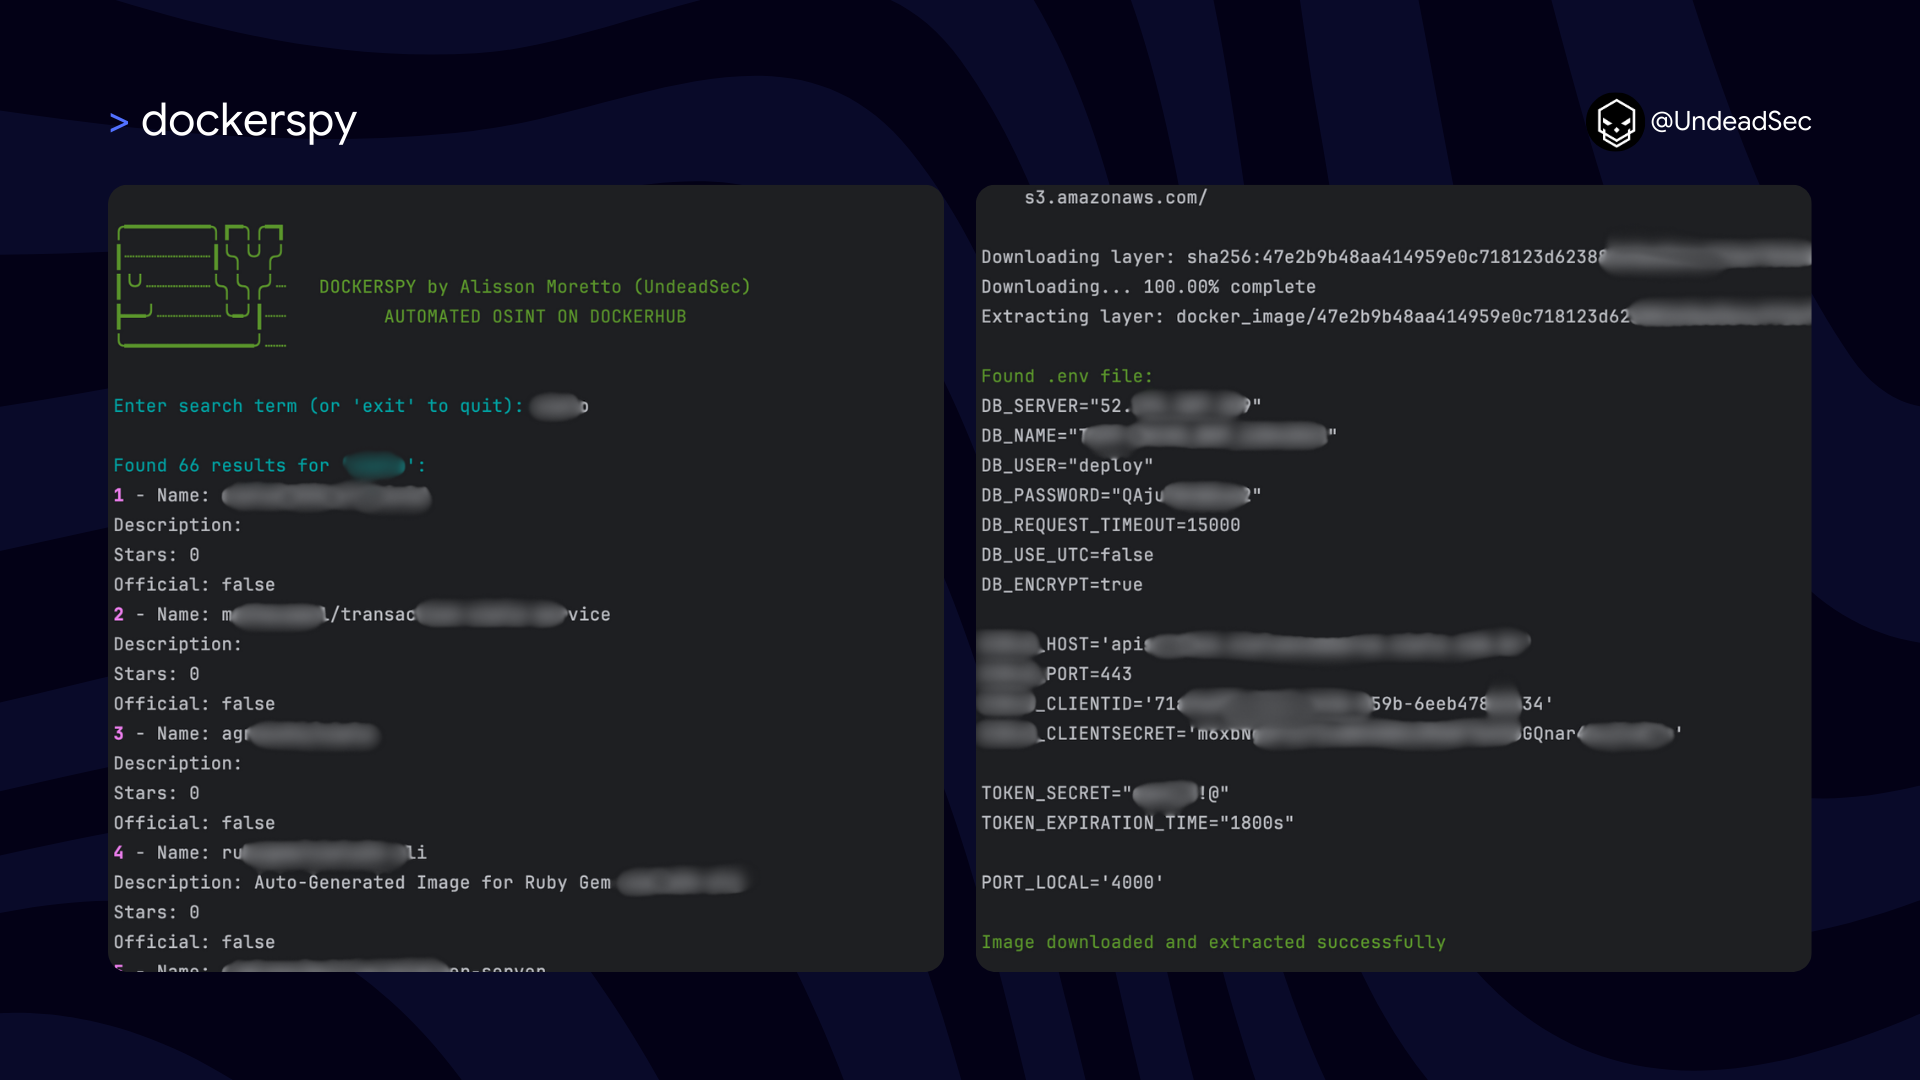 undeadsec/dockerspy
Scans Docker Hub images using regex patterns to extract exposed secrets, private keys, and authentication tokens for security auditing and incident…
 h4wkst3r/adokit
Modular attack toolkit exploiting Azure DevOps REST API for reconnaissance, privilege escalation, and persistence using stolen cookies or PATs.
 wiz-sec-public/cloud-middleware-dataset
Curated dataset of cloud middleware agents installed by AWS, Azure, and GCP, documenting past vulnerabilities, privileges, and attack-surface risks…
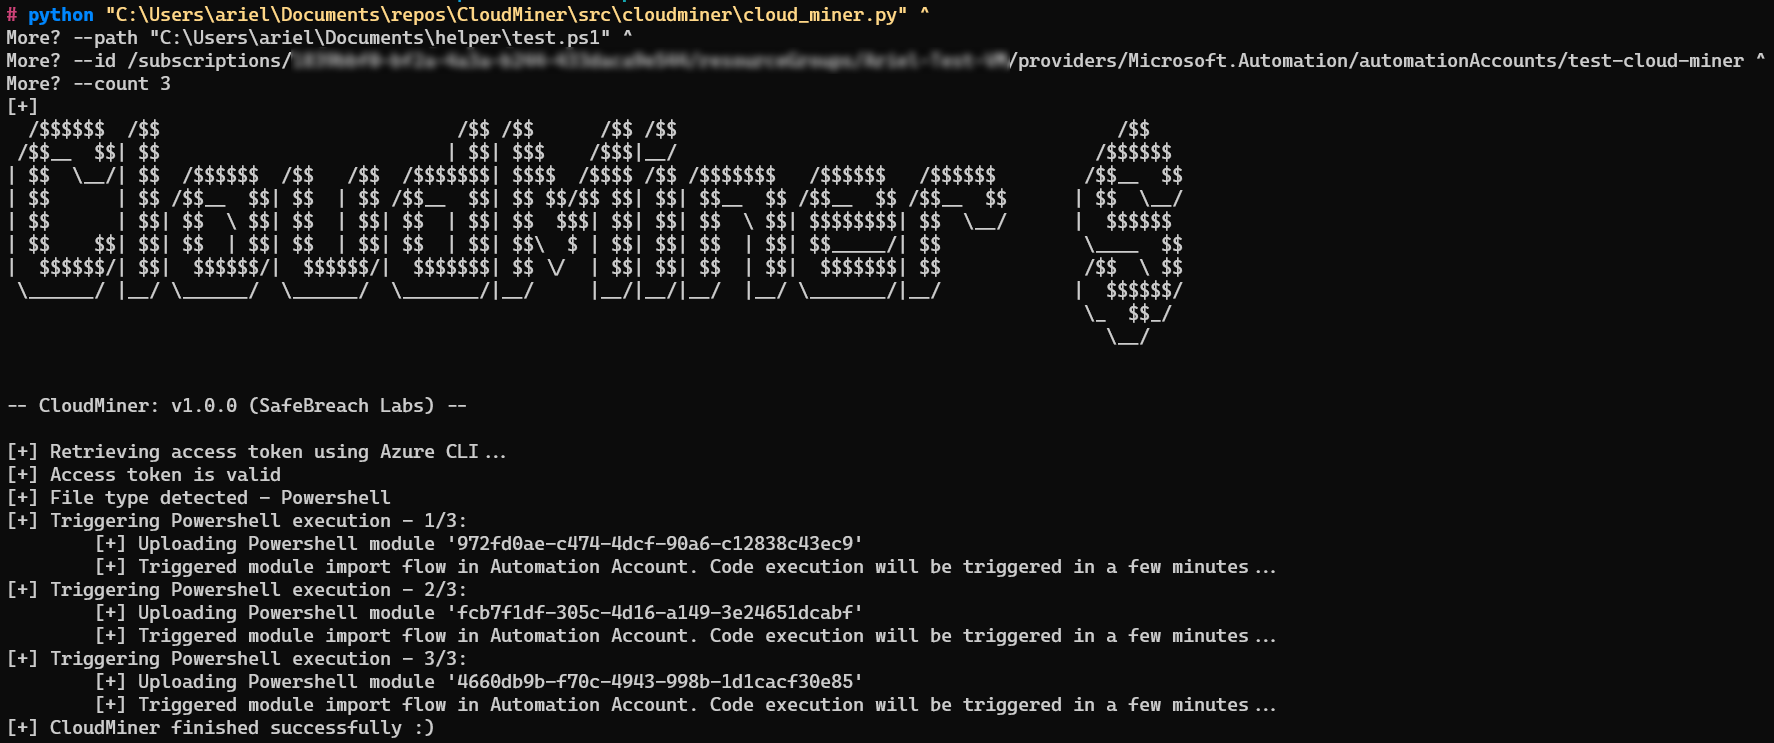 safebreach-labs/cloudminer
Execute code using Azure Automation service without getting charged
 tenable/cnappgoat
CNAPPgoat is an open source project designed to modularly provision vulnerable-by-design components in cloud environments.
 megamansec/gixy-next
Gixy-Next: NGINX Configuration Security Scanner & Performance Checker
 chithi-dev/chithi
The next generation encrypted file sharing project
 spacesiren/spacesiren
A honey token manager and alert system for AWS.
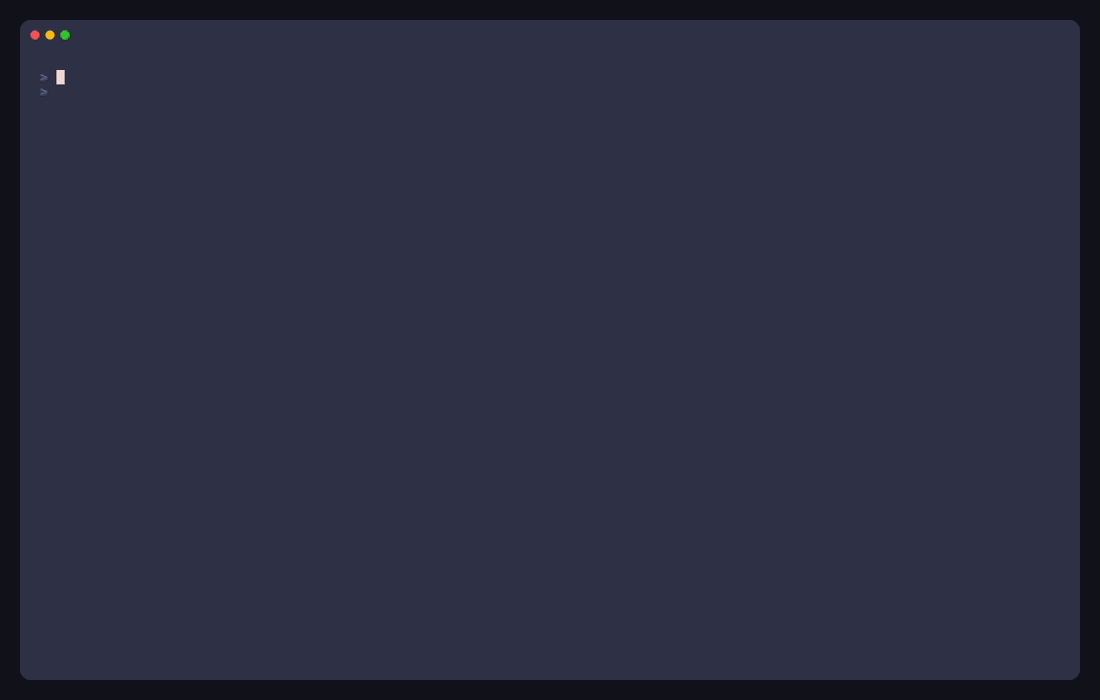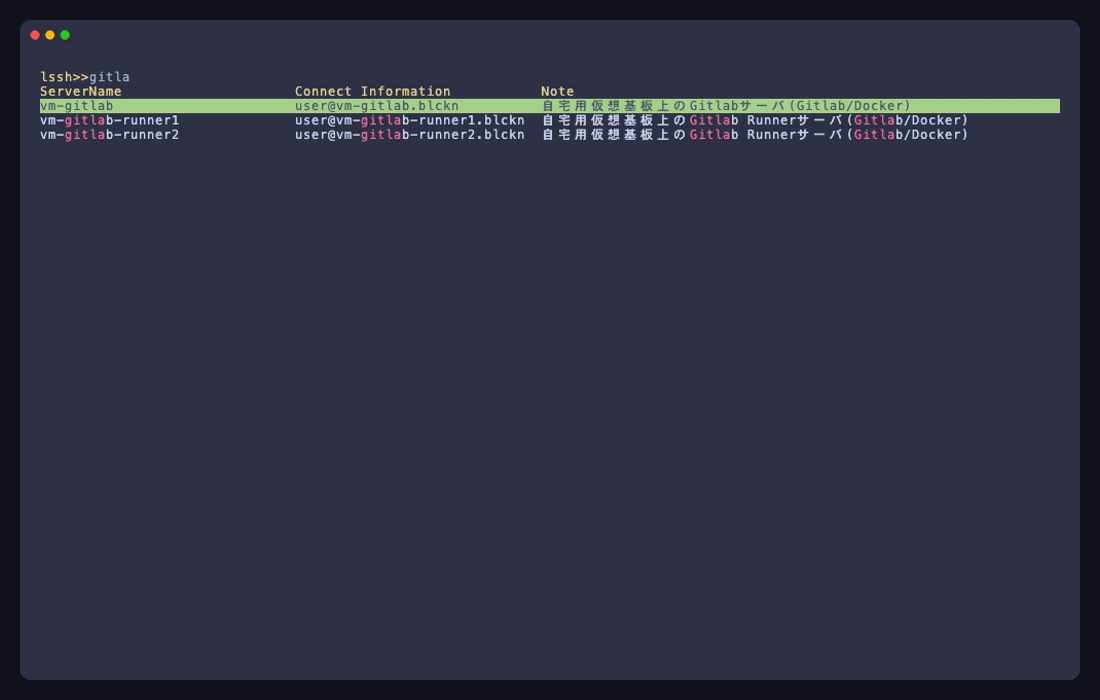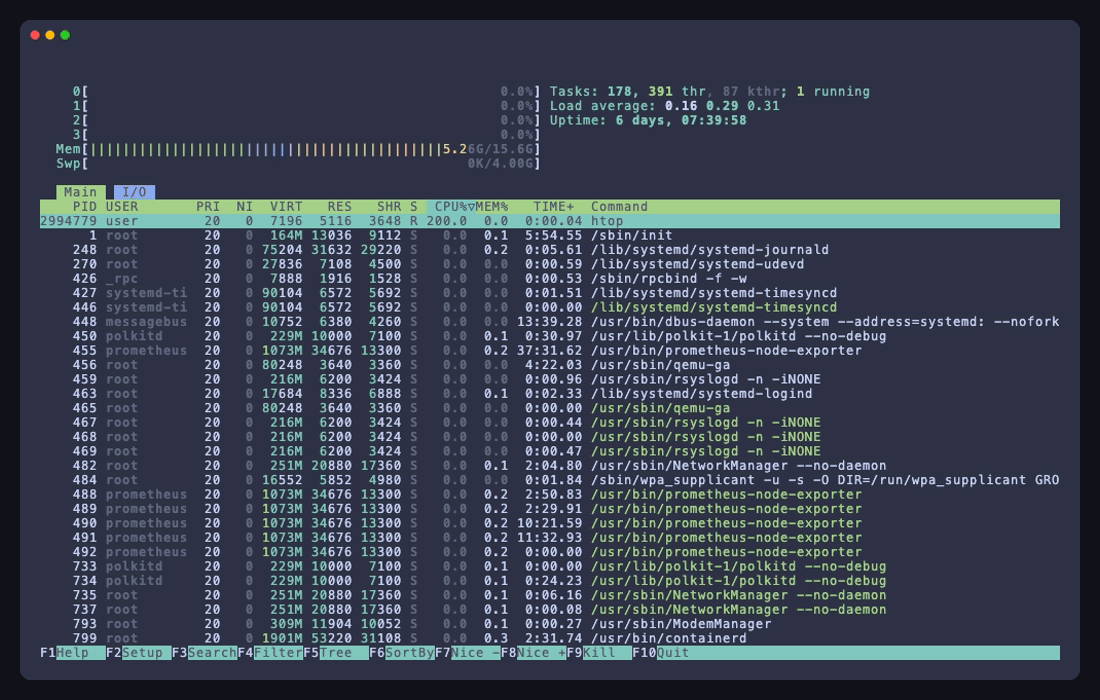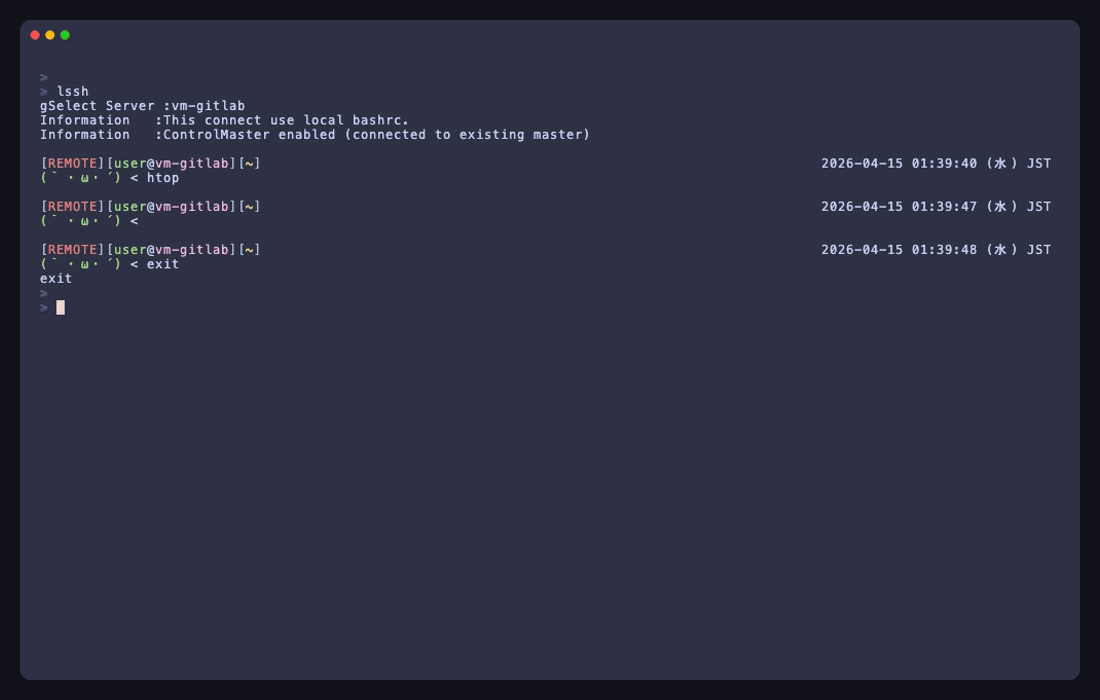 blacknon/lssh
A terminal-native remote access suite for SSH, cloud inventories, provider-backed connectors, parallel commands, mux workspaces, file transfer, and…
 owasp/iot-security-verification-standard-isvs
OWASP IoT Security Verification Standard (ISVS)
 luemmelsec/apex
Azure Post Exploitation Framework
 eqtylab/cupcake
A native policy enforcement layer for AI coding agents. Built on OPA/Rego.
 linnix-os/linnix
eBPF-powered Linux observability with AI incident detection. AGPL-3.0 licensed.
 aniket2912/all-cehv13-module-wise-pdf-reports
Practical labs, notes, and reports for CEH v13 modules — covering web hacking, network pentesting, malware analysis, social engineering, and security…
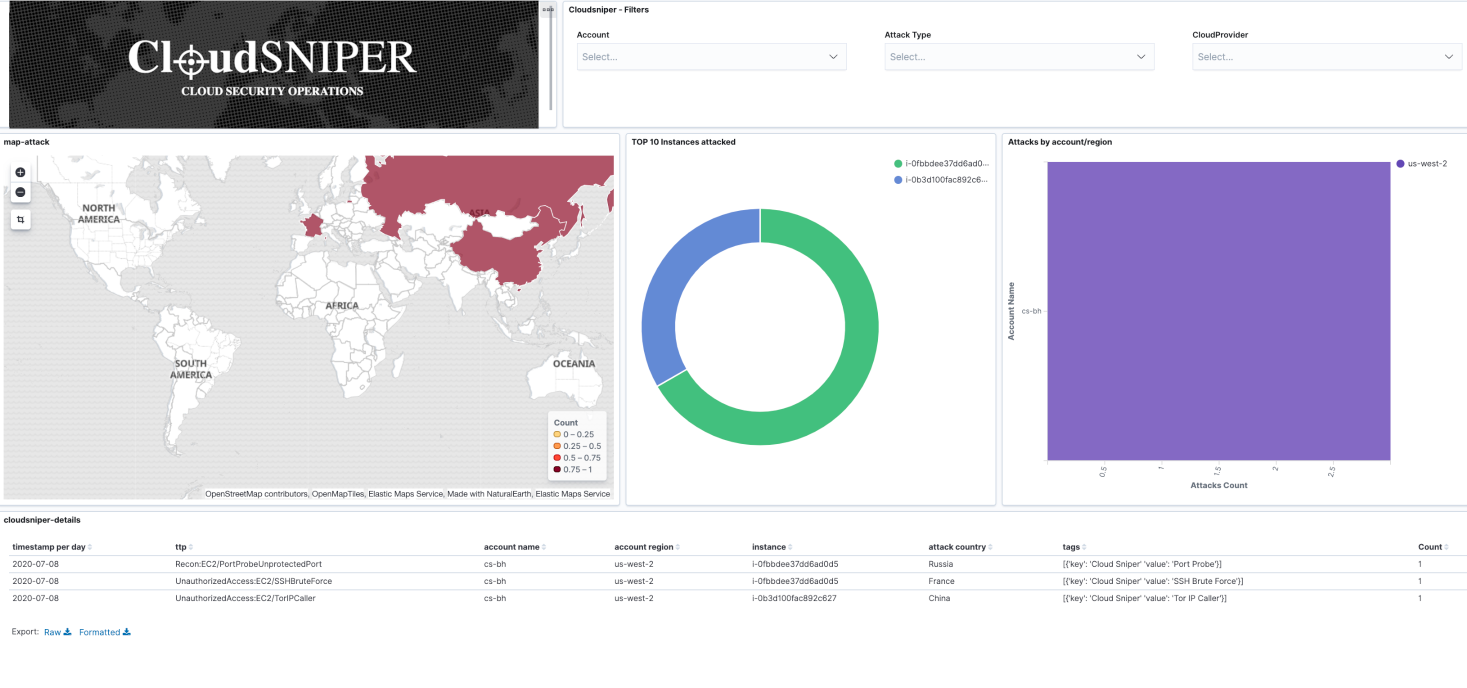 cloud-sniper/cloud-sniper
Detection-as-code platform that automates cloud security incident response by correlating artifacts, analyzing IOCs, and orchestrating…
 owasp/openshield
Open source CSPM for Azure - scan for misconfigurations and quantum-unsafe cryptography, map findings to CIS/NIST/ISO27001/SOC2, and fix them with…








