
 #1
Tools for assessing, testing, and securing cloud environments (AWS, Azure, GCP) and their services.
Kitploit recommended
 milesrichardson/docker-onion-nmap
Scan .onion hidden services with nmap using Tor, proxychains and dnsmasq in a minimal alpine Docker container.
 rhinosecuritylabs/gcpbucketbrute
A script to enumerate Google Storage buckets, determine what access you have to them, and determine if they can be privilege escalated.
 azuread/azureadassessment
Tooling for assessing an Azure AD tenant state and configuration
 bishopfox/cloudfoxable
Create your own vulnerable by design AWS penetration testing playground
 beetlechunks/spoolsploit
A collection of Windows print spooler exploits containerized with other utilities for practical exploitation.
 scille/parsec-cloud
Open source Dropbox-like file sharing with full client encryption !
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
 pensarai/apex
AI-powered offensive security testing using autonomous agents, directly in your terminal.
 legit-labs/legitify
Detect and remediate misconfigurations and security risks across all your GitHub and GitLab assets
 eilonh/s3crets_scanner
Automated scanner that hunts for secrets (API keys, credentials) accidentally uploaded to public S3 buckets, using truffleHog3 for detection and…
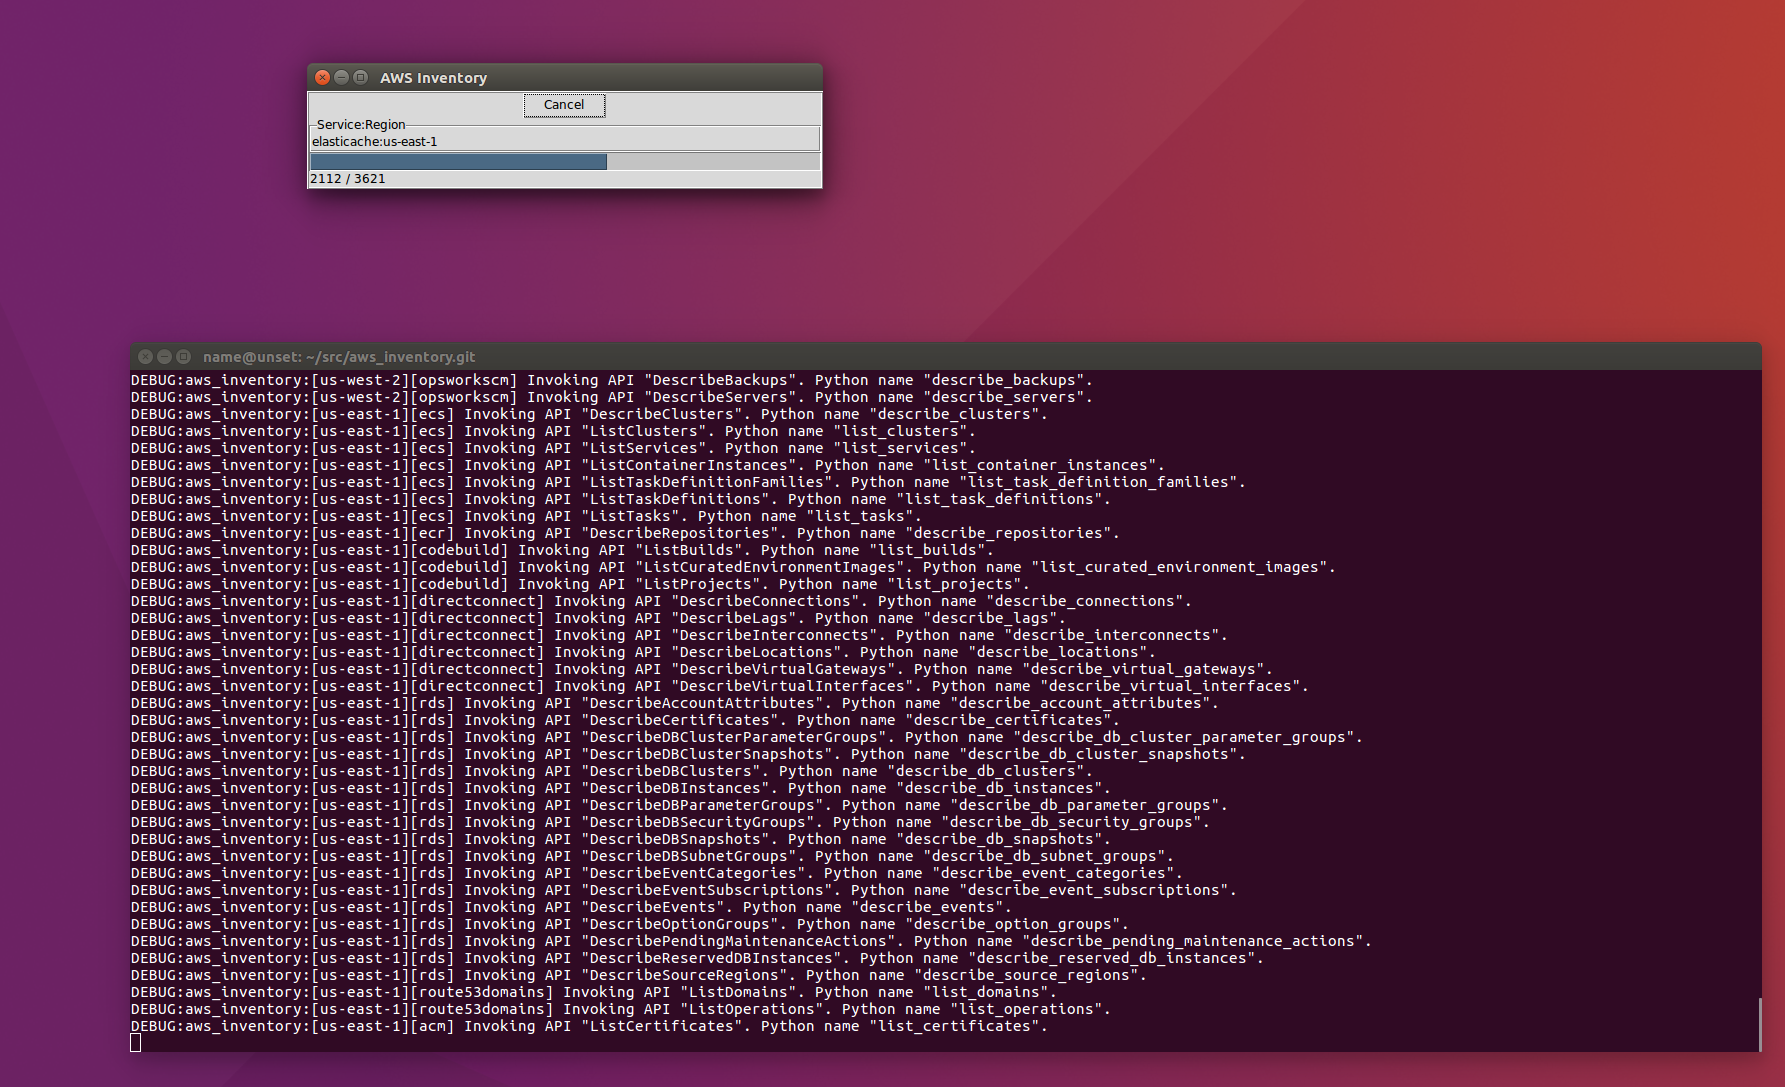 nccgroup/aws-inventory
Discover resources created in an AWS account.
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
 natlas/natlas
Attack Surface Management since before Attack Surface Management was a thing
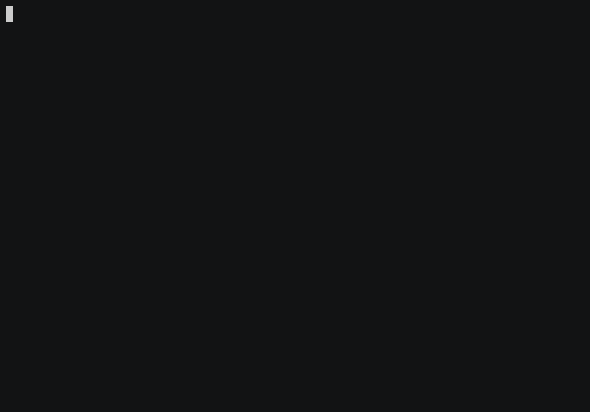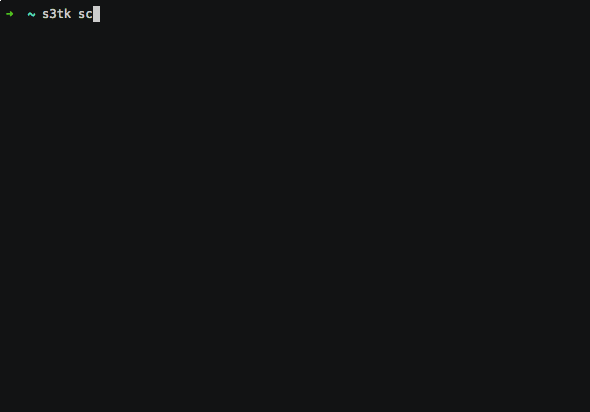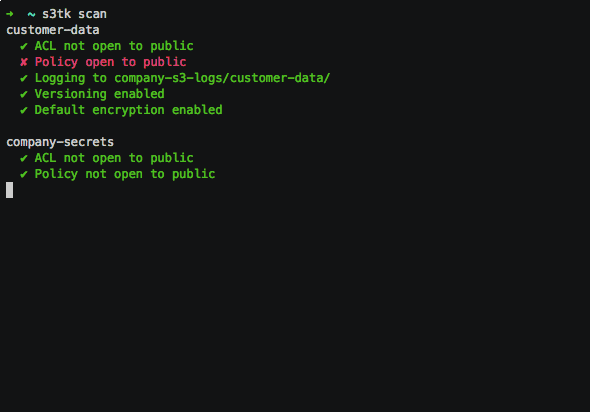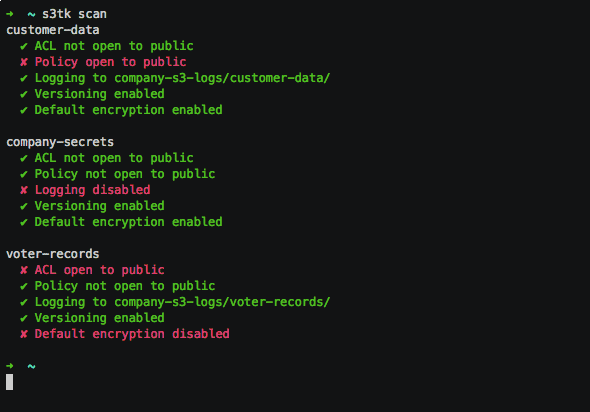 ankane/s3tk
A security toolkit for Amazon S3
 0x4d31/honeylambda
honeyλ - a simple, serverless application designed to create and monitor fake HTTP endpoints (i.e. URL honeytokens) automatically, on top of AWS…
 ine-labs/gcpgoat
GCPGoat : A Damn Vulnerable GCP Infrastructure
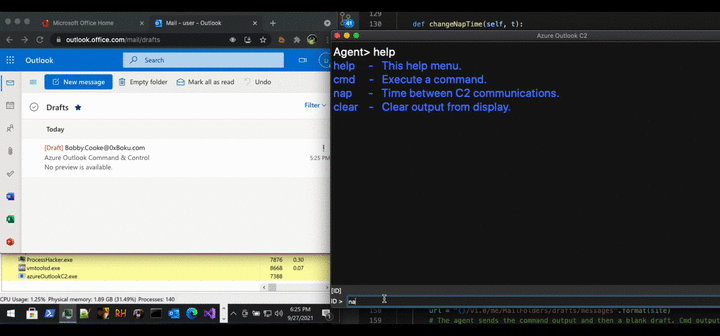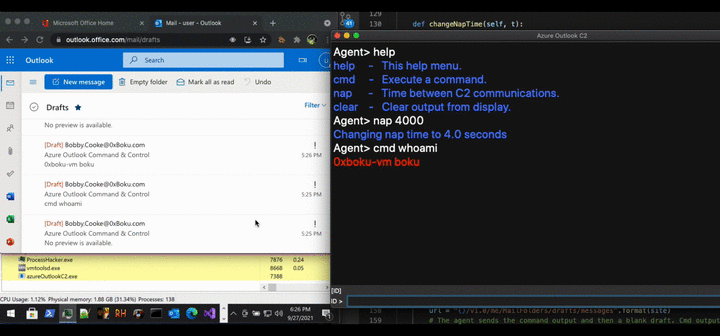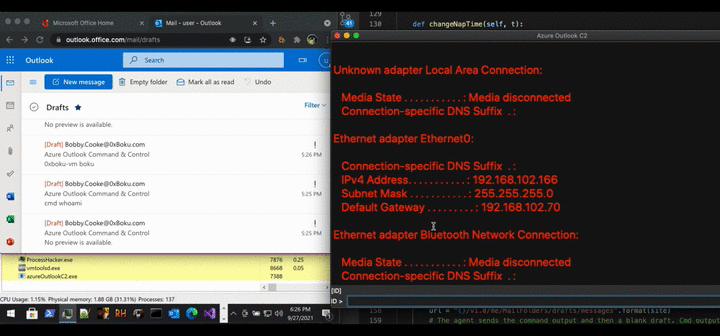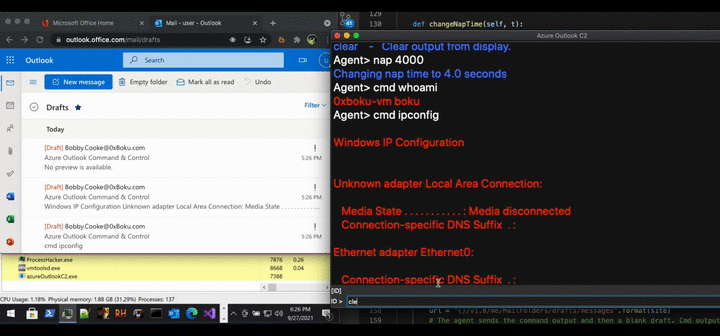 boku7/azureoutlookc2
Azure Outlook Command & Control (C2) - Remotely control a compromised Windows Device from your Outlook mailbox. Threat Emulation Tool for North…








