
 #1
Binary reverse engineering, disassembly, decompilation, and patching tools.
Kitploit recommended

 gmh5225/obs-graphics-hook32-hook
Demonstrates hooking OBS graphics-hook32.dll's D3D9 Present pointer to achieve stream-proof rendering that evades anti-cheat game capture detection.
 kaleth4/cve-2026-55200
Technical analysis and proof-of-concept for CVE-2026-55200, a critical heap-based buffer overflow in libssh2 allowing pre-authentication RCE.…
 idanshechter/cve-2017-13208-scanner
Python script using r2pipe to detect CVE-2017-13208 in Android libnetutils.so by checking for missing dhcp_size validation via static binary analysis.
 flamelu/cve-2020-17035-patch-analysis
Analysis of the patch for CVE-2020-17035, detailing the vulnerability and exploitation mechanism in the affected binary component.
 jianrongxiao-linksys/dnsmasq-cve-2026
Automated defect verification tool for 6 dnsmasq CVEs (CVE-2026-2291, 4890, 4891, 4892, 4893, 5172)
 rishvic/xpdf-docker
Docker images of Xpdf 4.04, vulnerable to CVE-2022-30524
 yan5ui/env-cve-2020-8036
Aritifacts of docker env of CVE-2020-8036
 nanopathi/external_libavc_aosp10_r33_cve-2021-0325
C-based vulnerability analysis and exploitation toolkit targeting AOSP libavc heap overflow (CVE-2021-0325) with static code analysis capabilities.
 muhammedhussein17/libheif-cve-2026-50142
CVE-2026-50142 — Heap allocation vulnerability in libheif HEIF sequence parser
 claesmnyberg/sdc
Self Decrypting Binary Generator
 jihwan77/linux-kernel-copy-fail-cve-2026-31431-
Analysis and mitigation of Linux kernel Copy Fail (CVE-2026-31431) vulnerability exploiting AF_ALG/splice page cache mutation, with PoC checker,…
 d7ead/cve-2026-38764
An issue in Unistal Systems Pvt. Ltd. Protegent 360 v2.0.0.4 allows a local attacker to escalate privileges via the kernel driver pgsecdl.sys
 eaea0001/servu-cve-2026-28318-poc
SolarWinds Serv-U CVE-2026-28318: unauthenticated Content-Encoding: deflate crash. Root-cause analysis (invalid free of an interior pointer -> heap…
 fzrsllasher/cve-2026-12166_cve-2026-12167_cve-2026-12168
Technical advisory detailing three local privilege escalation vulnerabilities (CVE-2026-12166/7/8) in the Little Orbit GFAC kernel driver, including…
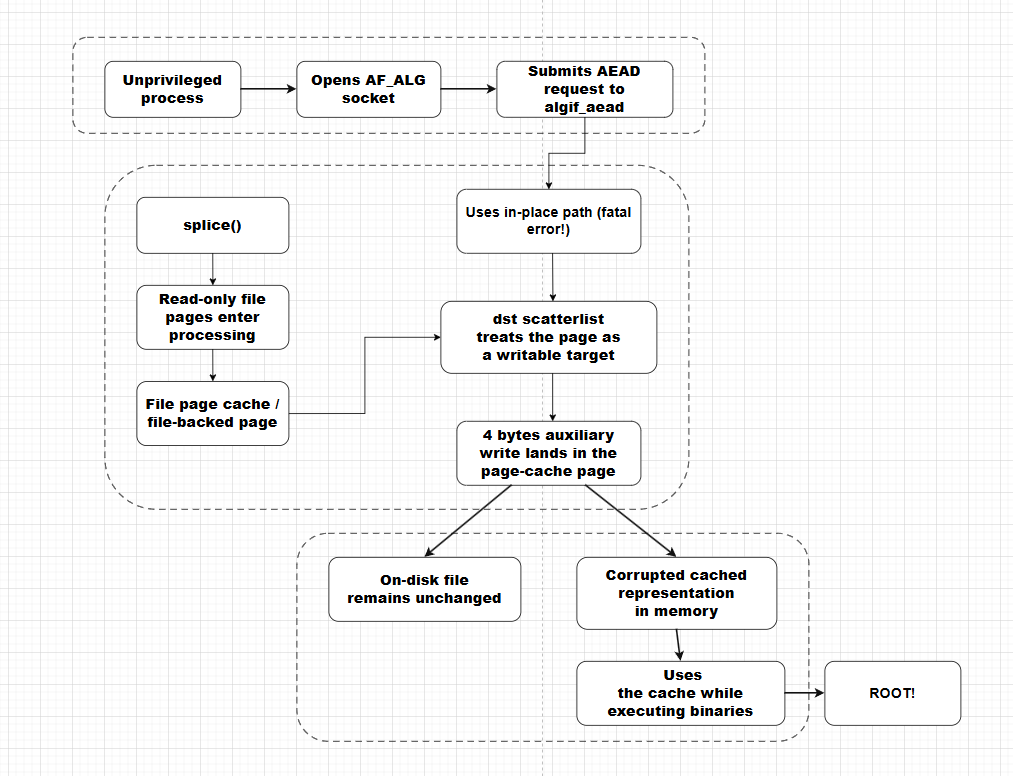 chernstepanov/copyfail-for-dummies
Research notes and proof-of-concept for Linux kernel CVE-2026-31431, documenting the AF_ALG splice() page cache corruption bug with source artifacts…
 halcy0nic/cve-2023-38434
Proof of Concept for CVE-2023-38434
 personnumber3377/dns_client_fuzzing
Fuzzing the Microsoft Windows DNS client library. Inspired by CVE-2026-41096.
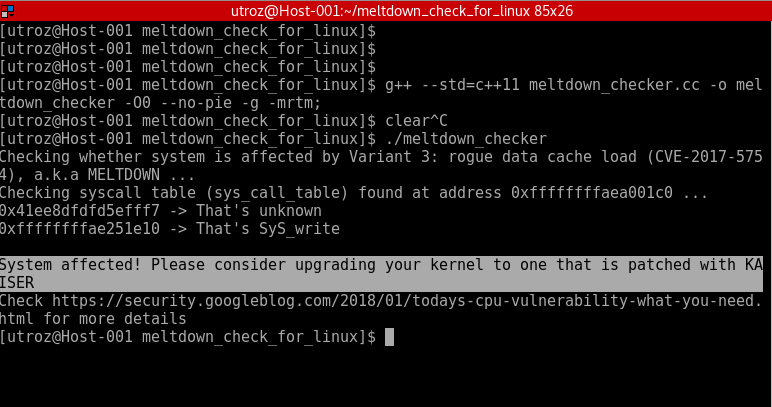 speecyy/am-i-affected-by-meltdown
Proof-of-concept / Exploit / checks whether system is affected by Variant 3: rogue data cache load (CVE-2017-5754), a.k.a








