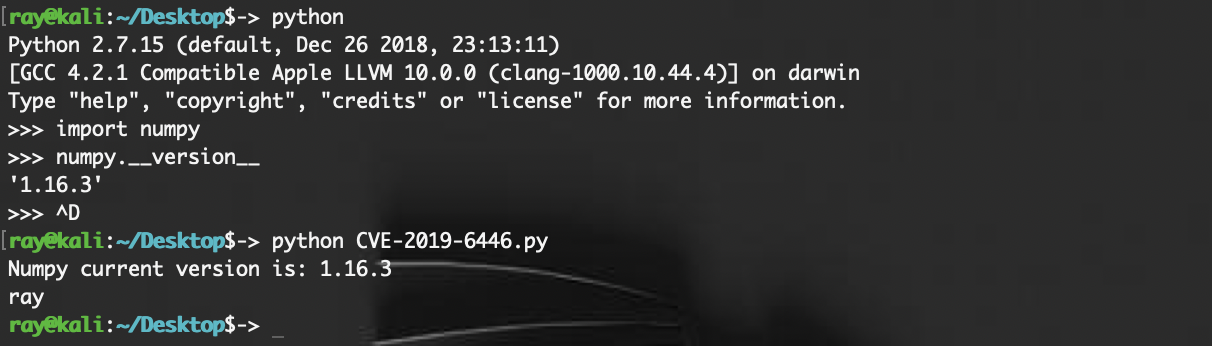
#1

 sangsheng2026/honor-90gt-mag-an00-root-research
Android kernel root research toolkit for Honor 90 GT: SELinux device probing, slab spray primitive validation, and AArch64 kernel Image disassembly…
 australeo/cve-2021-28476
Proof-of-concept for CVE-2021-28476, a Hyper-V vmswitch.sys arbitrary pointer dereference allowing guest-to-host denial-of-service and potential RCE.
 whatthefuzz/openssl-fuzz
Finding CVE-2022-3786 (openssl) with Mayhem
 norvethil/cve-2013-3900-powershell-poc
CVE PoC
 badnack/d_link_880_bug
CVE-2017-14948 for D-Link 880 Firmware
 dodo-sec/kpot-string-decrypter
IDA python scripts to decrypt strings from KPOT and set those as comments
 typeconfused/cve-2025-14174-analysis
Analysis and PoC for CVE-2025-14174 - ANGLE Metal OOB write (iOS Safari, macOS Chrome)
 jm00nj/hpe-aruba-aos8-vulnerabilities
ArubaOS 8.13.2.0 pre-auth attack surface research. XXE+SSRF, ICMP reflection, buffer over-read, hardcoded credentials — all submitted to HPE…
 bytehackr/unzip_poc
CVE-2022-0529 & CVE-2022-0530
 oxfemale/cve-2020-15999
CVE-2020-15999
 gtgalaxi/electronvulnerableversion
Find Electron Apps Vulnerable to CVE-2023-4863 / CVE-2023-5129
 kernelm0de/cve-2018-8090
DLL Hijacking in Quickheal Total Security/ Internet Security/ Antivirus Pro (Installers)
 umbertodellamonica/linksys-wrt54gl-exploitation
From Solder to Shell: Full Hardware Exploitation of the Linksys WRT54GL Router (CVE-2022-43973)

 lanph3re/cve-2019-1108
Proof-of-concept exploit for CVE-2019-1108, an RDP client information disclosure vulnerability that leaks memory contents via specially crafted…
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
 4onurdemir/tcl-androidtv-root-attempts
Documents reverse engineering of a TCL Android TV factory layer: 56 kHz IR protocol, tclfactoryos daemon, kernel IR driver, and evidence that…