
 #1
Binary reverse engineering, disassembly, decompilation, and patching tools.
Kitploit recommended
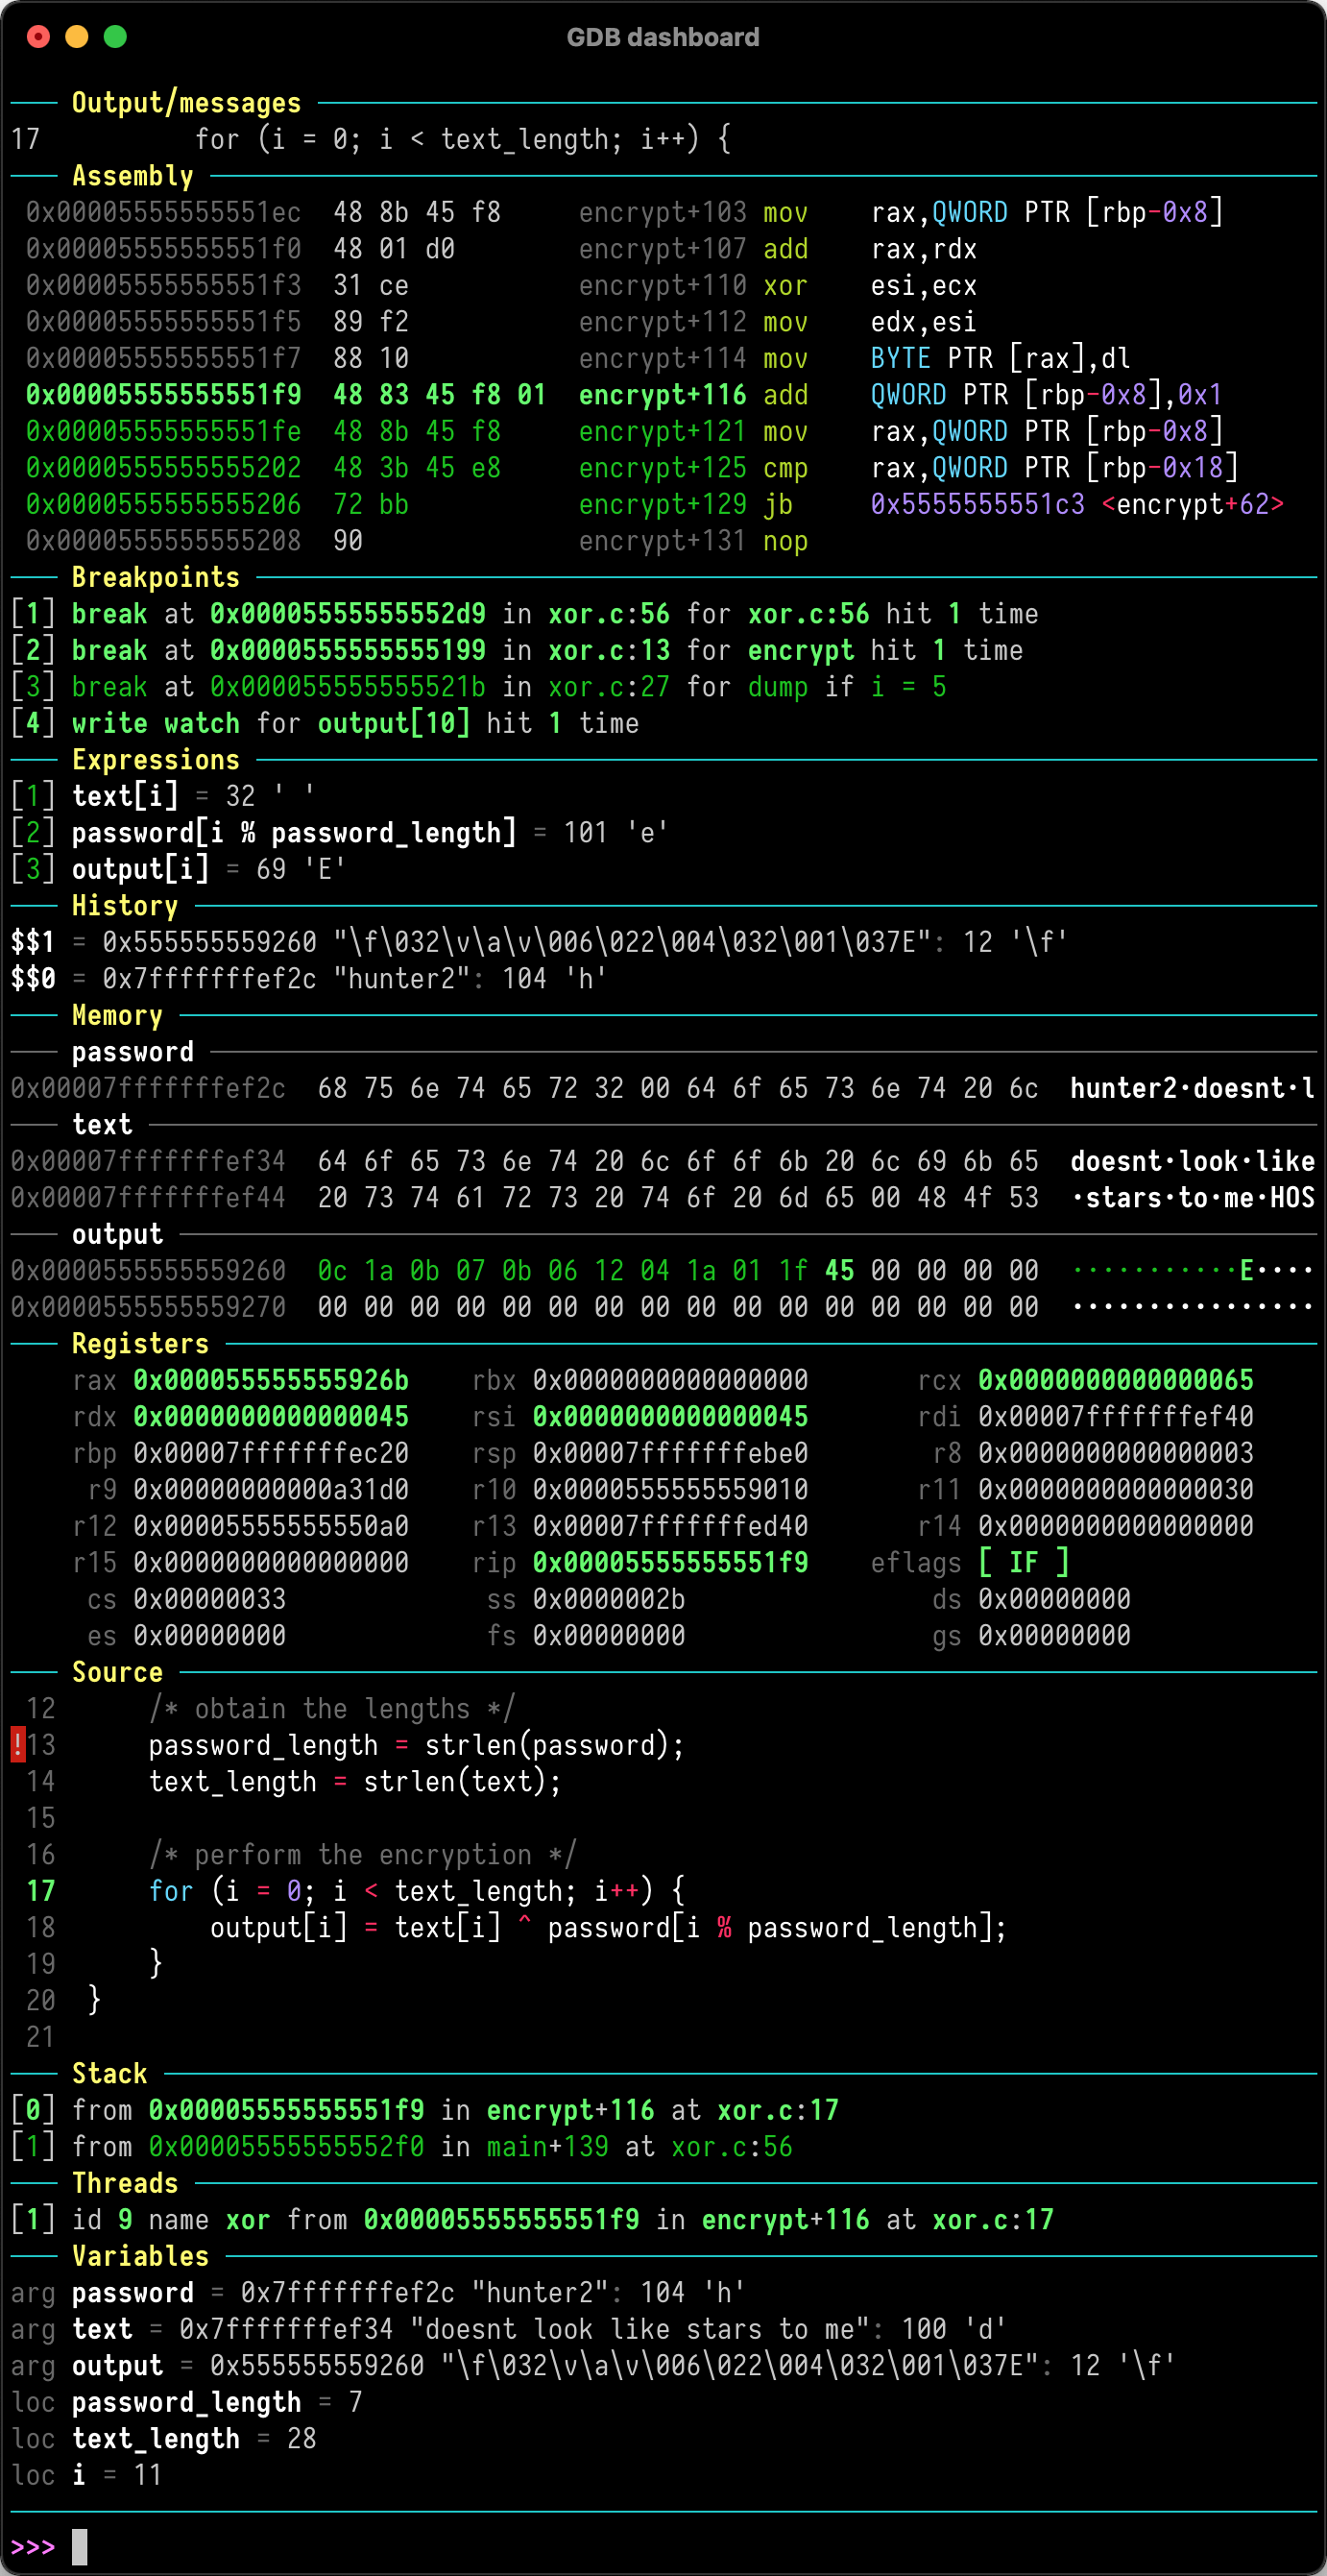
 cyrus-and/gdb-dashboard
Modular GDB interface providing a visual dashboard with customizable panels for inspecting registers, source code, assembly, and program state during…
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
 zrax/pycdc
C++ python bytecode disassembler and decompiler
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 mandiant/flare-floss
FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.
 burrowers/garble
Obfuscates Go builds by wrapping the Go toolchain, replacing identifiers, package paths, and position data with hashes and stripping debug and build…
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
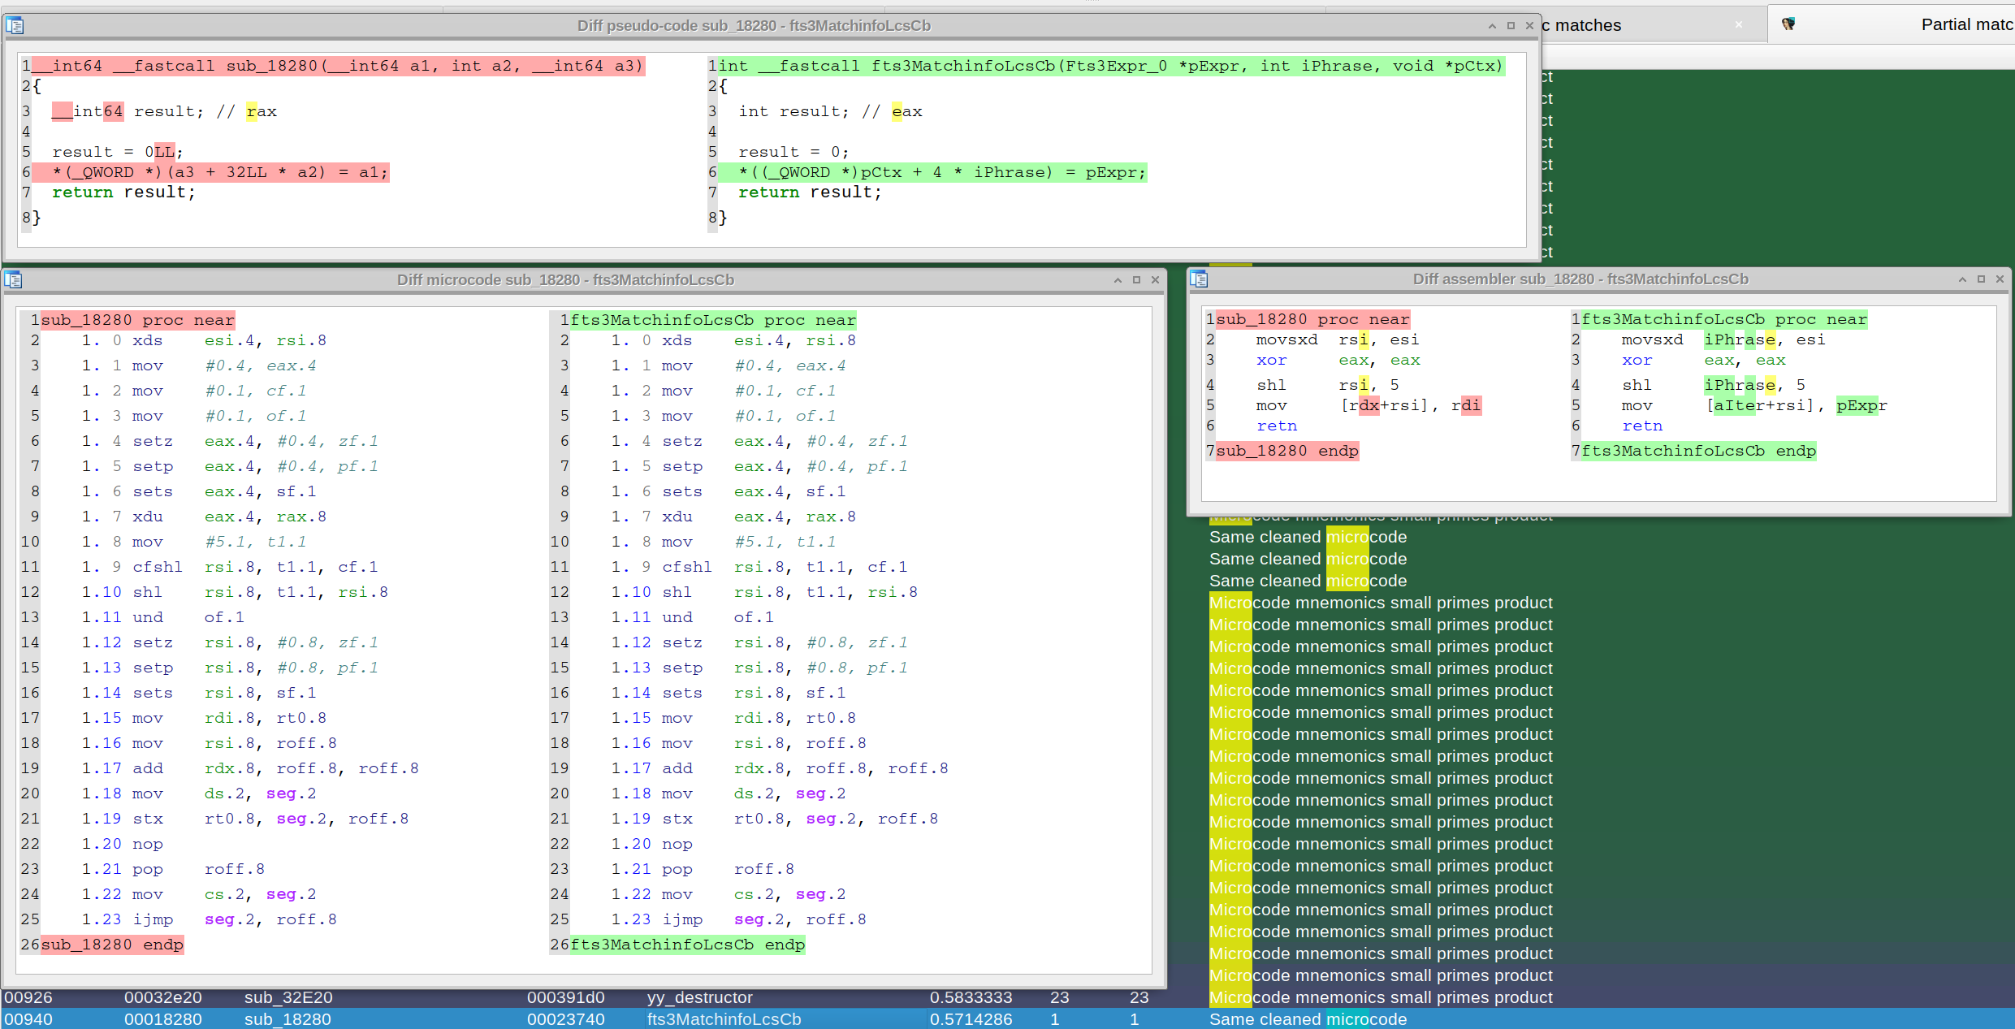 joxeankoret/diaphora
Diaphora, the most advanced Free and Open Source program diffing tool.
 rocky/python-uncompyle6
A cross-version Python bytecode decompiler
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 xoreaxeaxeax/sandsifter
The x86 processor fuzzer
 joernio/joern
Open-source code analysis platform for C/C++/Java/Binary/Javascript/Python/Kotlin based on code property graphs. Discord https://discord.gg/vv4MH284Hc
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 jetbrains/fernflower
Decompiler from Java bytecode to Java, used in IntelliJ IDEA.
 worawit/blutter
Flutter Mobile Application Reverse Engineering Tool
 trailofbits/publications
Publications from Trail of Bits
 cmu-sei/pharos
Automated static analysis tools for binary programs
 blacktop/ipsw
iOS/macOS Research Swiss Army Knife







